
How the Compensation Scheme of Last Resort must protect superannuation from scams
Your superannuation is a target for criminals and the Compensation Scheme of Last Resort (CSLR)is the only compensation mechanism currently available for those who lose a lifetime of savings from which they can never recover. This is Scam Victim Alliance’s submission to the Treasury Consultation on CSLR reforms.
Executive summary
Scam Victim Alliance supports fraud victims through the trauma that follows life-changing loss. We support groups who experience lead generator harms which switched them into fraudulent self-managed superannuation schemes that ‘collapsed’ and were most likely designed as fraudulent schemes.
The Scam Victim Alliance (SVA) is a not-for-profit organisation representing Australians harmed by scams, cyber-enabled fraud and financial crime. Our members have lived experience of complex victimisation that begins with a financial loss and ends in years of complex legal fights and battles that retraumatise people and exacerbate the initial financial harm. We welcome the opportunity to submit lived experience feedback to Treasury's consultation paper, Enhancing member protections in the superannuation system.
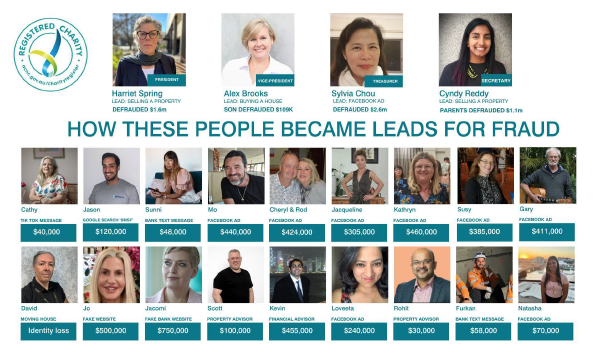
[Image: SVA committee and members, showing losses from bank transfers, super rollovers and investment transfers ranging from $30,000 to $2.6 million]
Superannuation savings are being raided by criminally fraudulent networks.
Scams involving superannuation are not simply financial losses. They are life-altering events that leave Australians facing long-term financial insecurity, emotional trauma, damaged relationships and, in many cases, permanent reductions in retirement dignity and quality of life. We see dangerous vulnerabilities in Australia's identity, superannuation and banking system, with mule accounts, money laundering and criminal networks constantly exploiting opportunities to steal superannuation, tax refunds and other savings Australians may have. This submission argues that protecting Australians' retirement savings must now be understood as both a consumer protection issue and a national financial crime priority.
Harriet Spring, President, Scam Victim Alliance
Executive summary
For Australians, superannuation is not simply an investment. It is legislated and a necessary retirement safety net at a time when the government-funded Age Pension does not keep up with living expenses [1] and Aged Care [2] and Home Care [3] requirements are becoming increasingly expensive.
Public discussion and policy responses still focus overwhelmingly on First Guardian and Shield [4] losses rather than the systemic weaknesses that Treasury and regulators have had oversight of. This problem not only robs victims today, but also steals from future taxpayers, who will increasingly be required to stump up for shortfalls to manage an ageing population who have had their superannuation savings stolen.
Regulatory and law enforcement weaknesses mean that organised syndicates [5], cyber-enabled fraud networks [6] and increasingly sophisticated social engineering tactics [7] are targeting superannuation savings at an industrial scale. These attacks are not confined to retirees but increasingly target working-age people, too.
Younger Australians are increasingly being manipulated into fraudulent investments and relationship frauds, duped into high-risk superannuation switching arrangements, or compromised through linked digital identity breaches. The devastating financial losses mean these victims' superannuation will not "go far" and will further deplete Australia's ability to collectively look after its defrauded population.
The rapid growth of artificial intelligence (AI), impersonation technology and automated scam infrastructure means this threat is likely to accelerate significantly in coming years. Criminal networks are evolving faster than Australia's current consumer protection, anti-scam and superannuation governance frameworks. Our organisation has seen three growing categories of harm.
Harm 1: Unauthorised access to superannuation accounts. In these cases, criminals compromise linked systems such as identity documents, email accounts, mobile phone services or myGov credentials before targeting superannuation balances. Once control of these systems is obtained, scammers can intercept security codes, reset passwords and initiate fraudulent transactions or account changes. Some members of our community have unwittingly had their identities stolen after moving house, experiencing a data breach or being the victim of a previous scam. These members commonly experience fraudulent tax refund lodgements, superannuation rollovers or withdrawals, and the nightmare of having to put credit freezes in place to protect themselves.
Harm 2: Scam-induced withdrawals or super rollovers. Here victims are manipulated into voluntarily withdrawing their superannuation and transferring funds into fraudulent investment schemes. This happened in the First Guardian and Shield situation (10,000–12,000 victims), and also in the Australian Fiduciaries Limited [8] collapse (600 victims), the Lion Property Group [9] collapse (600 victims) and other unscrupulous schemes [10]. Fraudulent investment schemes are now architected with multiple ASIC-registered entities, poor (and likely deceitful) auditing practices, and poorly managed investment schemes, some registered and some not. The harm scales through several channels:
low-cost digital ads placed on social media and in traditional media ad networks like Taboola and Outbrain
lead generation activity used to get around cold-calling sanctions
investment opportunities marketed as legitimate and sophisticated
Harm 3: Traditional organised scam compound activity. Sometimes known as "pig butchering", romance scams and investment scams are now morphing into highly engineered attacks on Australians. These scams can also involve threats and impersonation of our most trusted authorities: police, regulators, banks and government authorities like Medicare. Some of our community members are being victimised in relationship frauds and coached into claiming releases from their superannuation for medical reasons. The criminals then manipulate victims into paying their released superannuation money into the many mule accounts within Australia's banking system, where the money is laundered and victims have no redress.
Importantly, scam-related losses are not confined to retirees. Younger Australians increasingly hold significant superannuation balances and are being targeted through online investment fraud and identity compromise. This means superannuation fraud should not be viewed solely as a retirement issue, but as part of Australia's broader cybercrime and financial crime challenge.
SVA strongly supports:
stronger governance obligations for platform trustees, particularly those involved in the First Guardian and Shield debacle;
codified due diligence requirements, especially for banks, ASIC, auditors and the Australian Taxation Office;
waiting periods for certain super rollover and switching transactions;
stronger scrutiny of advice-fee deductions;
enhanced compensation and redress pathways for victims, particularly through the Australian Financial Complaints Authority (AFCA); and
tighter regulation of lead generation and investment promotion models.
1. Mandatory scam disruption for large super withdrawals and rollovers
Trustees, banks, superannuation funds and "custodians" who hold credit or financial services licences should be required to implement mandatory scam-risk checks where:
a member is transferring substantial balances to newly established SMSFs or super rollover products;
funds are being rolled into non-diversified investment products and managed investment schemes;
auditors are not from a respected Australian firm that does quality work;
unusual withdrawal or rollover behaviour is detected; or
known red-flag indicators are present, like rapid placement and layering of funds or rapid deposits and withdrawals.
This should include mandatory customer contact by licensed financial firms, cooling-off periods and independent verification requirements. It should also include strong reimbursement obligations when licensed firms and accounting professionals like auditors fail to get it right.
AUSTRAC's recent indicators of suspicious activity [11] for the superannuation sector are welcome. However, they remain too heavily focused on traditional fraud, identity misuse and post-event transaction behaviour, rather than the reality of organised cyber-enabled fraud and AI-driven social engineering.
We think these indicators should be strengthened to better detect three things: scam-induced superannuation switching, behavioural manipulation, and coordinated criminal infrastructure operating across banking, telecommunications, digital platforms and superannuation systems simultaneously. Current indicators focus largely on unusual transaction size, fraudulent documents or account compromise after harm has already occurred. They do not adequately capture the behavioural and contextual indicators that often precede catastrophic losses. They also do not tie corporations charged with looking after superannuation to reimbursement obligations when they fail.
Case study: Ms T, targeted by relationship fraud twice, super also stolen
Ms T has an acquired brain injury. She had a successful career as a project manager but fell into deep depression after experiencing catastrophic relationship fraud, during which she took out several unsecured credit facilities. She borrowed money from family but still ended up homeless, living in her car. She rebuilt her life until she was targeted by a second relationship fraud. This is a common experience, as scam crime organisations know that previous victims are vulnerable to retargeting with a fresh, new approach. This time she was targeted through Instagram by an "army doctor trapped in Syria" who needed her help to get out.
During the second relationship fraud, the criminal suggested Ms T take out unsecured loans through Citi, Zip Pay and Zip Plus. Her physical health spiralled due to a hip injury. Her scammers had gained knowledge of the Australian superannuation early release conditions, and they manipulated her into making medical release claims against her large Australian industry super fund. A $20,000 release from her superannuation was successful. But rather than the funds being used to treat her medical condition, the scammers directed payments through a multitude of Australian mule bank accounts, PayPal, Steam gift cards and other gift cards. More than a dozen transfers, ranging from about $1,500 to $6,000, went to personal accounts at Bankwest, Commonwealth Bank, ANZ, Great Southern Bank and Bank First.
Ms T's case reveals that scams are directly eroding Australians' retirement savings through coercive superannuation withdrawals and the proliferation of mule accounts on Australian banking platforms. This happened alongside Centrelink dependency, high-risk loans and repeated scam indicators that financial institutions failed to interrupt. When the trauma of discovering the whole scheme was a fraud unfolded, the mental health harms were immense, and suicidal ideation is a common experience for victims. At this point, victims often urgently require access to their superannuation but cannot get it because they have already sent it to scammers.
Cases like this demonstrate that superannuation losses are not limited to SMSF investment fraud or illegal early access schemes. Increasingly, organised criminal networks exploit and socially engineer emotionally vulnerable consumers, leveraging Australia's lax banking and money laundering system controls to drain retirement savings in real time.
Takeaway: Any proposed Treasury reforms should explicitly recognise scam-induced superannuation depletion as a major financial crime and consumer protection issue. That requires mandatory intervention and reimbursement obligations, enhanced transaction monitoring and clearer compensation pathways for victims.
2. Stronger digital identity and account security protections
Australia urgently requires stronger protections against identity compromise across the banking and superannuation systems.
Minimum protections should include:
secure government identities robust enough to thwart organised crime networks that create mule accounts at scale to defraud ATO tax returns and engineer superannuation rollovers;
stronger recovery protections where identity, email or mobile phone/SIM compromise is suspected;
mandatory telephone alerts for changes to Australian Taxation Office, Medicare or superannuation fund contact details or linked accounts; and
rapid freeze mechanisms where fraud is suspected, or automatic reimbursement when licensed financial corporation failures are identified.
Case study: A banker experienced a data breach and later discovered that four Military Bank mule accounts had been created in his name. He only found out after his accountant queried why he was amending past tax returns.
3. Regulation of investment advertising and lead generation
Many superannuation scam victims are initially targeted through social media advertising and lead generation funnels that appear legitimate. Lead generation activity connected to superannuation switching or investment promotion should face significantly higher scrutiny, licensing obligations and enforcement, as outlined in our submission to Treasury's other consultation. We see harm not only in investment or SMSF creation, but also in "scam recovery", "AI trading" and other false opportunities.
[Image: flowchart "How one ad click can lead to people losing all their super"]
How one ad click can lead to people losing all their super:
Ads are targeted to people looking to improve their superannuation.
The victim clicks on an ad and submits their email and phone number.
A lead generator calls the victim, who reveals more and more personal information.
The lead generator learns how much super the victim has, and the victim is on the hook.
A licensed Statement of Advice is issued.
The victim is conned into "switching" to an SMSF.
The underlying managed investment schemes "collapse". This is fraud: victims are robbed, but there is no investigation.
ASIC and APRA do not communicate with victims.
Some victims take action through AFCA and the CSLR.
Liquidators are slow to report, and victims are not a priority.
Victims are left with no recourse.
4. Royal Commission, mandatory reimbursement and simple compensation pathways
Consumers currently face fragmented and inconsistent recovery pathways after superannuation-related fraud. SVA supports reforms requiring trustees and platforms to compensate members where governance failures, inadequate controls or poor due diligence contributed to losses. The AFCA process is difficult, traumatic and unlikely to lead to any redress for victims, compounding the harm they experience.
Compensation frameworks should recognise scam-related harms where consumers were manipulated through sophisticated deception, not only traditional unauthorised access.
We believe regulators like ASIC should be notifying victims of investment and superannuation losses, so that victims know the pathways available to pursue recovery or reimbursement, such as applying to the Compensation Scheme of Last Resort (CSLR).
Because AFCA is so harmful and traumatic for victims, the discretionary Act of Grace payments [12] and the Scheme for Compensation for Detriment caused by Defective Administration (CDDA Scheme) [13] need to be made clear for victims seeking redress.
AFCA takes a quick box-ticking approach to resolving complaints through its external dispute resolution (EDR) process. It commonly adds to the trauma and distress that victims feel, particularly when their cases are mired in delays and AFCA's determination and membership fees are prioritised over payments to victims.
SVA submits that the evidence emerging from Shield, First Guardian, Prime Trust, Lion Property Group, Australian Fiduciaries and related matters demonstrates the need for a Royal Commission into financial crime, regulatory failure, superannuation switching misconduct and compensation system gaps across Australia's financial services sector.
The issues revealed by Treasury, ASIC and Department of Finance material are not isolated operational failures. They point to systemic structural weaknesses involving:
conflicted financial advice ecosystems;
inadequate platform trustee oversight;
weak inter-agency coordination;
inconsistent regulatory intervention;
unclear liability allocation; and
significant barriers to compensation and procedural fairness for victims.
Importantly, Treasury and ASIC correspondence released under Freedom of Information [14] concerning the CDDA Scheme raises serious questions. It suggests Australians may have been effectively denied meaningful access to compensation pathways that Parliament intended to exist for losses connected to defective regulatory administration.
The Treasury correspondence disclosed under FOI suggests a prolonged and unresolved jurisdictional vacuum in which:
ASIC's CDDA authorisation lapsed in 2015;
Treasury and ministers subsequently argued they could not determine claims involving ASIC because of ASIC independence concerns;
victims were redirected toward Act of Grace processes instead; and
substantial claims appear never to have been determined on their merits.
SVA is deeply concerned this may have created a practical denial of procedural fairness for victims of alleged regulatory failures and defective regulator administration. This is particularly concerning when victim-survivors of SMSF fraud continue to pay ongoing accounting and ASIC registration fees, and in some cases fines, that add to the harm.
We believe a Royal Commission should therefore examine:
whether current compensation and redress frameworks for fraud and scams are fit for purpose;
whether victims are being improperly excluded from Government compensation pathways and denied procedural fairness;
whether the CDDA, Act of Grace, AFCA and CSLR frameworks create structural barriers to fair compensation, particularly when victims are not notified in a timely way to apply for this limited redress;
whether regulatory agencies act promptly and effectively in response to known fraud and crime risks;
the role of lead generators, advisers, platforms, banks and SMSFs in enabling consumer harm;
whether current laws appropriately allocate liability for fraud and investment-related losses; and
whether Australia's financial crime response adequately reflects the scale of organised cyber-enabled fraud affecting consumers, and the potential harm it can cause to trust in governments.
SVA submits that without a comprehensive public inquiry, Australia risks repeating the same cycle observed after previous financial collapses and the 2018–19 Banking Royal Commission: widespread consumer harm, fragmented accountability, delayed reform and inadequate compensation outcomes.
Consumers should not be forced to navigate opaque jurisdictional disputes between agencies while suffering catastrophic losses connected to regulatory failures or systemic misconduct.
5. Recognition of fraud as a financial crime and productivity issue
Scams and cyber-enabled fraud are no longer isolated consumer issues. They represent organised transnational financial crime causing widespread economic and psychological harm to Australians. The risk of illicit capital flowing to offshore actors is real, and it causes grave trafficking harms in other countries around the globe.
Superannuation protections should therefore be designed not only as consumer safeguards, but as part of Australia's broader anti-money laundering, cybercrime and financial crime response. A cohesive national fraud strategy that treats these crimes as both a national security issue and a consumer protection issue is now urgent.
6. Artificial intelligence will increase scale and harm
SVA is concerned that artificial intelligence (AI) is rapidly increasing the scale and sophistication of financial crime targeting Australians, including superannuation members. The immediate threat is not speculative "superintelligent" AI systems. It is the industrialisation of existing scam techniques such as phishing, smishing, impersonation and fraudulent investment advertising on social media platforms.
The social engineering playbooks behind these scams already exist and are highly effective. AI removes the remaining operational bottleneck by allowing criminal networks to automate and scale deceptive communications, relationship grooming and fraudulent investment promotion at volumes previously impossible without large human workforces.
This creates a profound asymmetry between criminals and defenders, and between criminals and victims. Criminal actors are unconstrained by governance, ethics or compliance obligations. Financial institutions, trustees and technology providers, by contrast, remain bound by fragmented regulatory settings that often limit their ability to deploy effective detection systems. The increasing use of real-time payments and rapid superannuation switching mechanisms further reduces the opportunity to detect and disrupt fraudulent transactions before funds become unrecoverable.
Australia urgently requires a regulatory framework that supports responsible AI-enabled fraud detection, stronger behavioural monitoring capabilities and clearer guidance for institutions seeking to identify scam-related activity before catastrophic losses occur. Without urgent action, AI will dramatically accelerate the scale of financial harm experienced by Australian consumers and superannuation members.
AI systems are now "agentic": they can access databases, read documents, execute workflows and interact with external systems through basic OAuth sign-ins [15]. This dramatically expands the consequences of social engineering and prompt injection attacks. In practical terms, criminals may no longer need sophisticated malware or traditional hacking techniques to compromise systems if AI-enabled tools can be manipulated into performing unintended actions on their behalf.
SVA believes Australia urgently requires clearer national guidance on the responsible use of AI for scam and fraud prevention. This should include stronger frameworks for secure AI system design, behavioural anomaly detection, digital identity protection and real-time intervention capabilities. Without rapid regulatory and technical adaptation, AI-enabled fraud risks will increasingly undermine trust in banking, superannuation and digital financial systems, while exposing Australian consumers to catastrophic and large-scale financial harm.
SVA believes Australia has a structural and systemic problem of fraud inside our trusted financial systems. Lead generation, conflicted advice, fast SMSF establishment, weak switching friction, poor platform due diligence and inadequate redress are all symptoms of this structural problem. Treasury material has recognised that scammers exploit how easy SMSFs are to establish. This includes cases where people are persuaded to roll over balances from APRA-regulated funds into newly created SMSFs, after which funds may be stolen from an SMSF bank account controlled by scammers.
SVA contends that past frauds like Astarra Trio and Prime Trust reveal an endemic pattern of victims being left in a redress gap, where no agency accepts practical responsibility for deciding compensation claims on their merits.
Our conclusion
Australians should be able to trust that their retirement savings are protected from sophisticated criminal exploitation. When these protections fail, we believe the CSLR must be a quick and painless process by which to recover and start rebuilding superannuation assets.
Treasury's proposed reforms are an important step forward. However, stronger preventative safeguards, scam-specific intervention measures and clearer compensation pathways are essential to restoring public trust and protecting Australians from devastating financial harm.
The Scam Victim Alliance welcomes continued engagement with Treasury on these reforms.
References
"Retirement Standard." ASFA. Accessed 10 May 2026. https://www.superannuation.asn.au/consumers/retirement-standard/
Eagar, Kathy. "Best of 2025 – Government Is Planning Hardship for Older Australians Living at Home." Pearls and Irritations, 9 January 2026. https://johnmenadue.com/post/2026/01/best-of-2025-government-is-planning-hardship-for-older-australians-living-at-home/
SBS News. "'No Vacancies': Australia Is Getting Older — and We're Facing a 'Conundrum.'" 11 June 2026. https://www.sbs.com.au/news/article/will-federal-budget-keep-pace-with-ageing-australians/ltljydliy
ABC News. "Collapses Expose Deep Flaws in Australia's $4.3 Trillion Super System." 18 September 2025. https://www.abc.net.au/news/2025-09-19/first-guardian-shield-collapse-asic-and-superannuation-flaws/105783328
ASIC. "22-363MR Melbourne Woman Sentenced after Stealing Millions from Superannuation and Share Trading Accounts." Media release. Accessed 10 May 2026. https://asic.gov.au/
Taylor, Josh. "$500,000 Stolen in Australian Super Fund Data Breach." The Guardian, 4 April 2025. https://www.theguardian.com/australia-news/2025/apr/04/australian-super-funds-compromised-cybersecurity-data-breach-hack
Poptodorov, Kon (LexisNexis Risk Solutions). "Op-Ed: Protecting Superannuation Accounts from Rising Cyber Security Risks." Cyber Daily, 7 May 2025. https://www.cyberdaily.au/security/12061-op-ed-protecting-superannuation-accounts-from-rising-cyber-security-risks
ASIC. "Australian Fiduciaries Ltd." Accessed 22 May 2026. https://www.asic.gov.au/
ASIC. "Lion Property Group." Accessed 22 May 2026. https://www.asic.gov.au/
ASIC. "26-093MR ASIC Permanently Bans Queensland Property Developer Trent Giumelli from Financial Services." Media release. Accessed 22 May 2026. https://asic.gov.au/
AUSTRAC. "Indicators of Suspicious Activity for the Superannuation Sector." Accessed 10 May 2026. https://www.austrac.gov.au/industry-and-business/education-and-resources/publications-and-resources/indicators-suspicious-activity-superannuation-sector
Department of Finance. "Act of Grace Payments." Accessed 22 May 2026. https://www.finance.gov.au/individuals/act-grace-payments-waiver-debts-commonwealth-compensation-detriment-caused-defective-administration-cdda/act-grace-payments
Department of Finance. "Scheme for Compensation for Detriment Caused by Defective Administration (CDDA Scheme)." Accessed 22 May 2026. https://www.finance.gov.au/individuals/act-grace-payments-waiver-debts-commonwealth-compensation-detriment-caused-defective-administration-cdda/scheme-compensation-detriment-caused-defective-administration-cdda-scheme
Department of the Treasury. "FOI – Australian Securities and Investments Commission (ASIC)." 4 May 2026. https://treasury.gov.au/the-department/accountability-reporting/foi/3041
Obsidian Security. "OAuth Vulnerabilities Every Security Team Should Know." Accessed 11 May 2026. https://www.obsidiansecurity.com/blog/oauth-vulnerabilities-security-teams