
AFCA holds Australia's best scam data — let’s use it!
From March 2027, Australian banks must investigate scam intelligence within 28 days, but no one has to actually do it until late 2027. AFCA's scam complaints could fill that gap and Scam Victim Alliance is urging Governments, law enforcement and regulators to use the confidentiality rules to treat tham as actionable scam intelligence.
Banks treat each scam as a customer mistake. Put the cases side by side and the same mule accounts, money laundering methods and banks keep appearing. That is actionable scam intelligence, and it is being wasted sitting in complaints that take years to resolve.
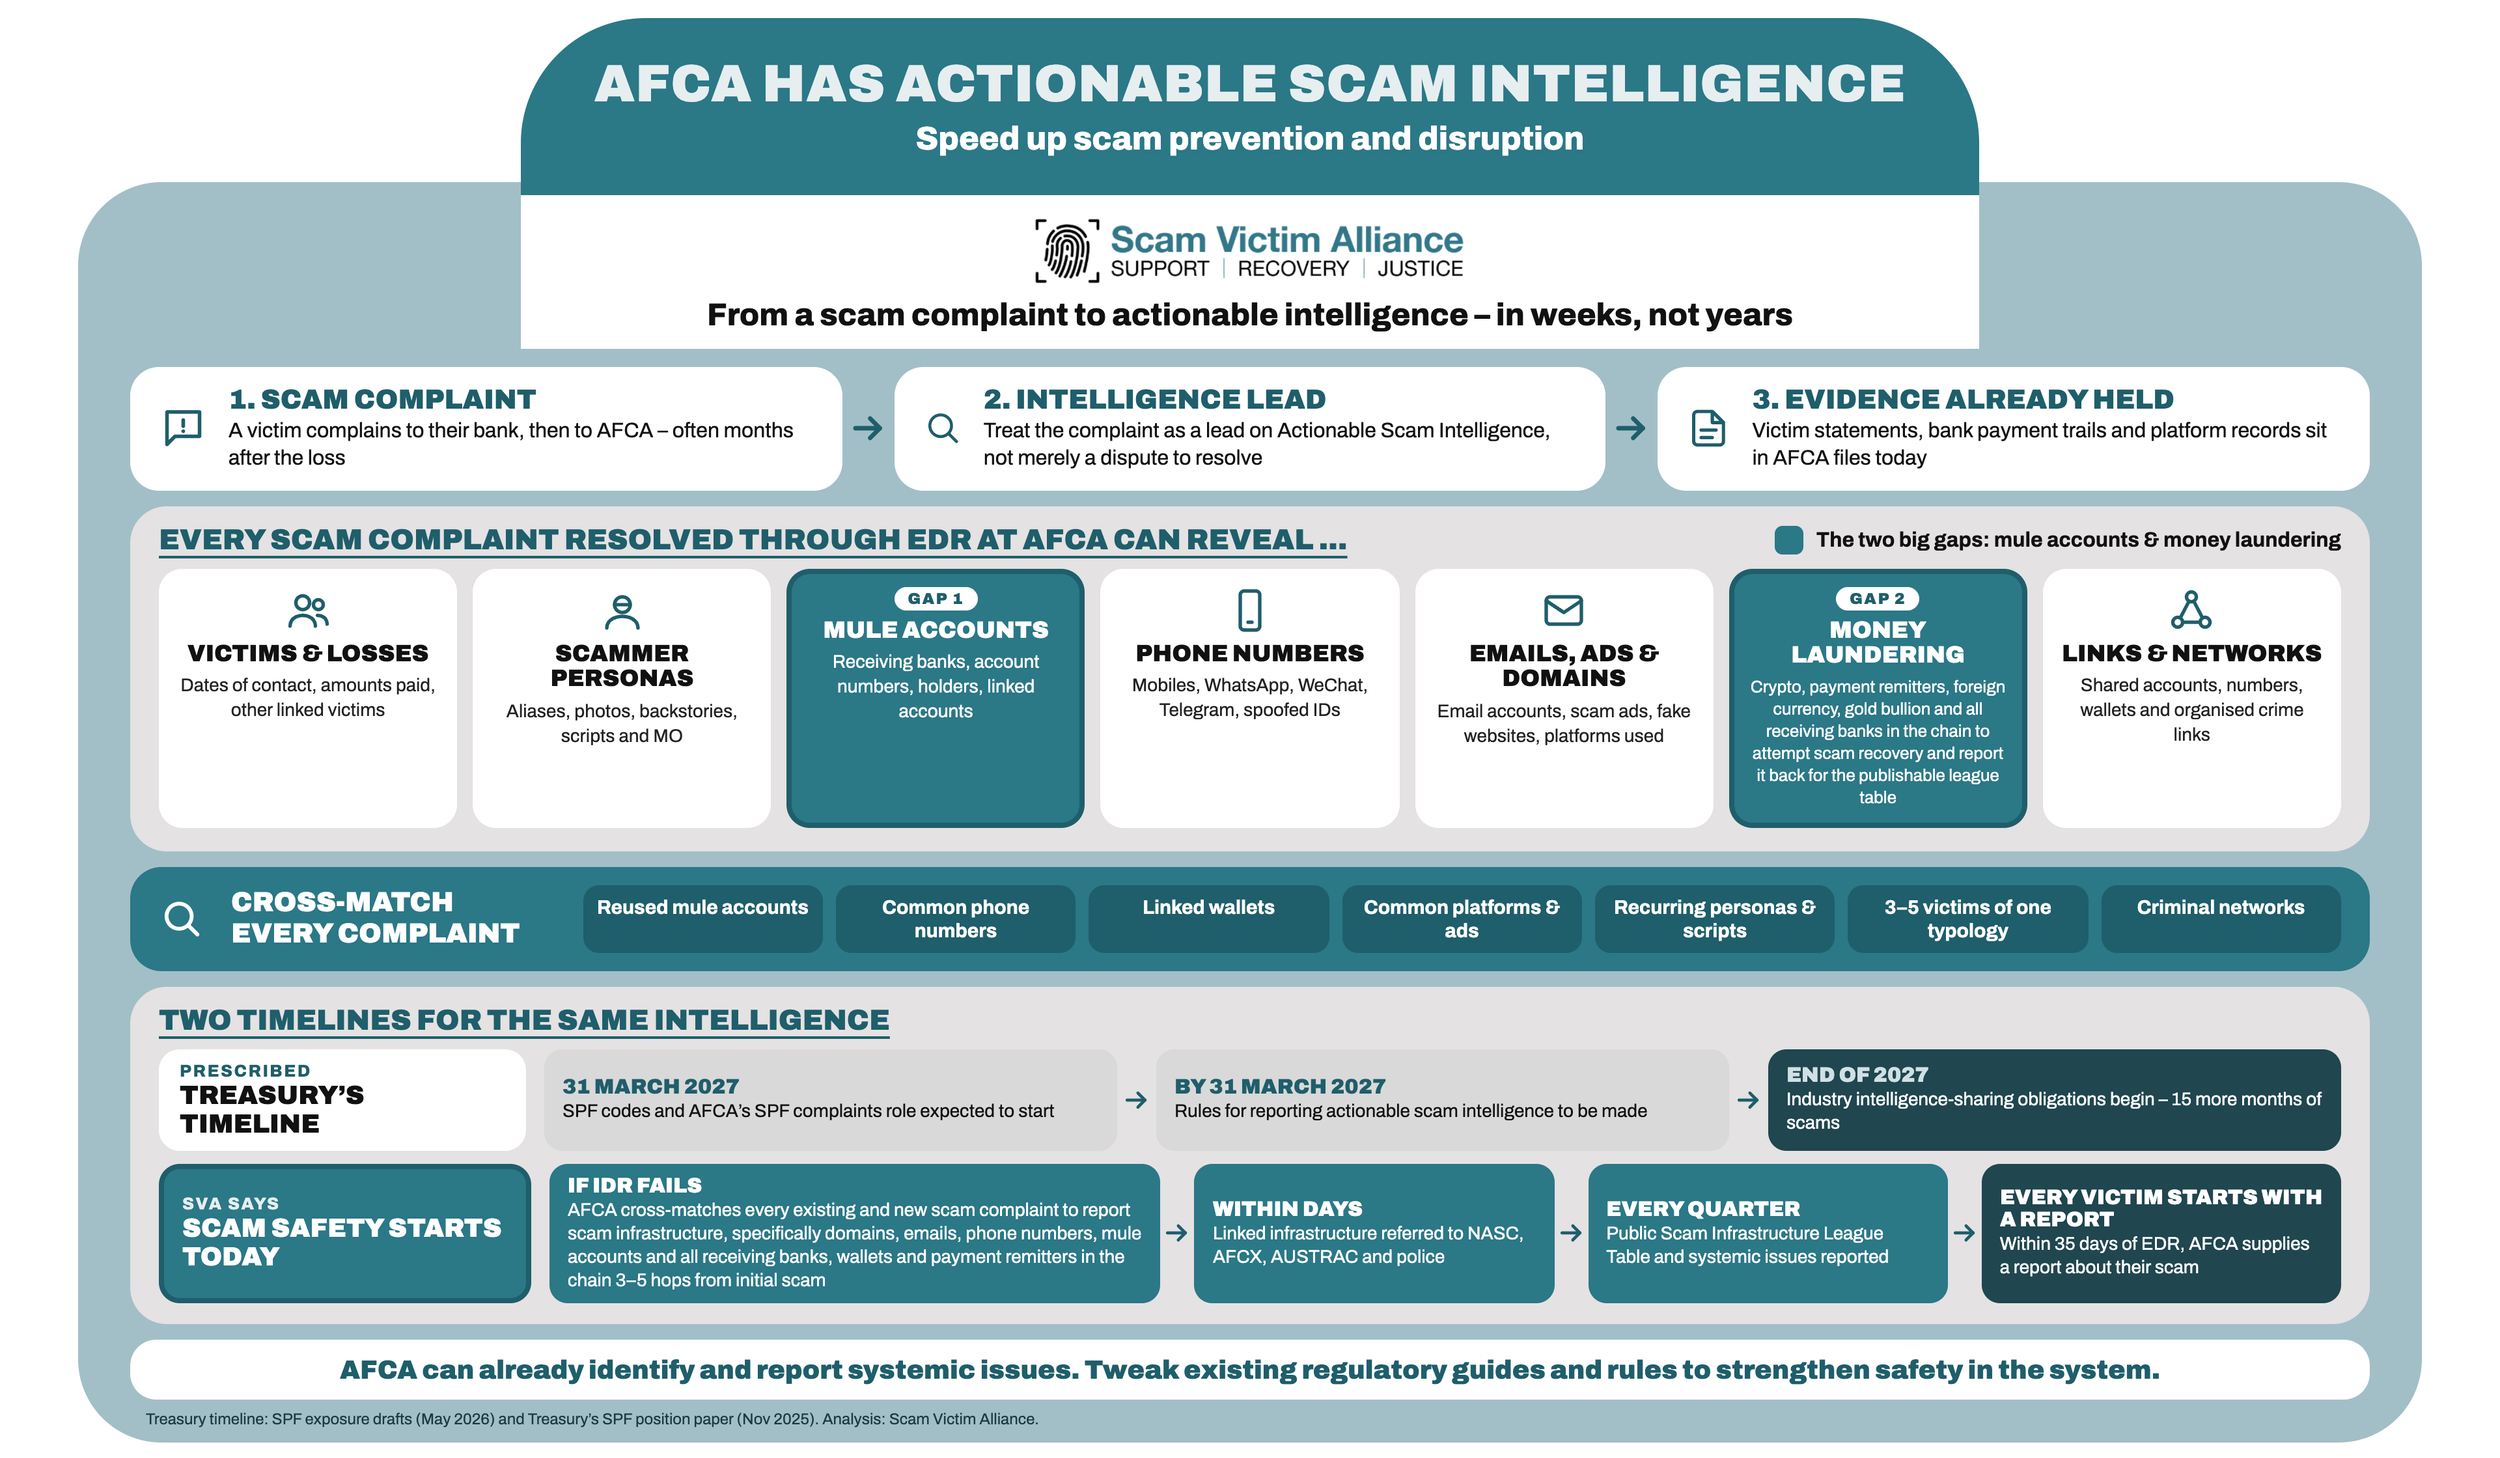
6 suggestions could change everything
Part 1 sets out cultural and procedural changes AFCA can make immediately, without any rule change.
Part 2 explains how the Scam Rules and Operational Guidelines should reverse the burden of proof, so the firms that hold the evidence must produce it.
Part 3 asks AFCA to share verified scam intelligence with regulators within 5 business days, so that each complaint helps stop the next fraud.
Part 4 draws lessons from three typologies our members have taken through AFCA, with a focus on property settlement misdirection fraud.
Part 5 maps what ASIC's regulatory guides and the SPF legislation already require.
Part 6 sets out our recommended rule changes and answers to AFCA's 19 questions
Our organisation sees firsthand how difficult AFCA's scam dispute process can be. Scams are engineered to make the victim look responsible. Criminals use deception and trusted bank infrastructure to induce a payment, then launder funds the victim appears to have "authorised" through a mule account. When the dispute reaches AFCA, the victim carries the burden of proving a crime they did not see, against a bank that holds the logs, KYC records and transaction trail.
AFCA also sits on some of the most valuable verified scam loss intelligence in Australia, and it is reaching regulators too slowly to stop the next victim. Banks face civil penalties if they fail to report actionable scam intelligence to the ACCC within prescribed periods under SPF laws. AFCA, which tests that same intelligence against evidence from both sides, should face deadlines sooner than 2027.
Our key recommendations TO IMPROVE SCAM VICTIM OUTCOMES AT AFCA
Fix the process and administrative burden harms now. Record and confirm every Agent Authority form within 2 business days and never ask for it again. Never close a scam complaint for "no response" without a phone call and a checked portal log. Issue evidence preservation notices to sending and receiving banks on the day a complaint is registered.
Reverse the burden of proof. A standard evidence package from every Regulated Entity in the funds chain within 21 days, with mandatory adverse inference, a payment to the victim, and referral to ASIC, AUSTRAC and APRA if it is not produced.
Share verified scam intelligence fast. A new Scam Rule requiring AFCA to refer verified scam identifiers to SPF regulators and the National Anti-Scam Centre (NASC) within 5 business days, with typology alerts shared with regulators after 3 matching complaints.
Hold the receiving bank chain accountable to prevent money laundering. Expressly include receiving and intermediary institutions in Rule 1.4.3(b), join every regulated entity in the funds chain by default, and treat KYC, AML and CTF failures as failures to take "reasonable steps".
No silencing settlements. Settlements must never stop victims reporting to regulators or police, consistent with RG 267.61.
Publish a scam league table. Annual public reporting of complaints, recoveries and reimbursements by firm, as the UK's Payment Systems Regulator does.
Part 1: Changes AFCA cOULD make tomorrow
The fastest way to reduce harm is to stop AFCA's own processes adding to it. None of the changes in this Part needs a rule amendment or ASIC approval. They are decisions about how AFCA staff work, what its systems record and what its letters say. AFCA's draft Rule 1.2.2 already says its Engagement Charter sets out the behaviour expected of AFCA employees as well as parties. These changes would give that commitment practical effect for scam victims.
1. Correct the administrative failures of losing agent nominations or automatically closing victim cases
Many scam victims rely on a family member, community advocate or SVA volunteer to deal with AFCA, because they are traumatised, unwell, elderly or not confident in English. That relationship depends on AFCA's Agent Authority Form. Our members report forms lodged and then requested again, authorities not linked to a second complaint about the same scam, and representatives told they cannot be spoken to while the victim waits.
In case 12-26-406829, SVA asked AFCA to consider six victims across four disputes as a group, because they had lost money to a similar type of scam. AFCA closed the file because it held no signed Agent Authority Form for each person and does not consider "group complaints" for unrelated complainants. The letter records that AFCA held no information about the six victims; rather than contacting them to ask whether they wanted to proceed, it left each to start again alone.
Do now: Log every authority form on receipt and confirm it to the victim and representative in writing within 2 business days. Attach it to every current and future complaint by that victim about the same scam, and never request it again unless it is revoked. Accept consent given by the victim over the phone and recorded by AFCA. Before closing or excluding any complaint because authority is unclear, including under proposed Rule 2.2.2(j), phone the victim directly.
2. No scam complaint closed by automatic notice
Proposed Rule 1.9.6(b) allows AFCA to refuse to continue considering a complaint if the complainant fails to comply with a requirement within a specified timeframe. In practice, our members have received closure notices wrongly stating they failed to respond, after they had responded through the portal, by email, or by phone to their case manager. Portal outages and broken information exchange templates make this more likely. For a victim with trauma-related cognitive load, a closure notice can end their pursuit of redress entirely.
Do now: No scam complaint should close for non-response unless AFCA has (a) tried to reach the victim on two channels, including a phone call; (b) checked portal, email and call logs for anything received; and (c) sent a final notice giving at least 10 business days. A victim who shows they did respond should have the file reopened automatically, with no new lodgement and no loss of place. AFCA should publish how many scam complaints close for non-response each quarter.
Do now: Stop sending substantive outcomes from "do not reply" addresses. Every scam complainant should have one named case manager and a direct phone number.
3. Investigate first, process second
Scam data is perishable and highly changeable, yet AFCA's process runs as a sequence of delays that let the value of this data as actionable intelligence perish: registration, refer-back to the firm for another 30 days, then information requests, then conciliation. Where more than one entity is involved, refer-backs can run one after the other. By the time AFCA asks for evidence, it may be gone.
The cost is visible in our members' cases. In case 12-24-120119, the victim asked for CCTV of his branch visit, which police had also sought. The bank told AFCA the footage showed only the foyer, the victim had been taken to a private room, and releasing the footage would breach other customers' privacy. In an HSBC matter (Ms Q), IP and login logs requested in April 2025 were never produced. In the Supercheap Security matter, it took an AFCA information request in January 2025 before CBA confirmed it had been notified about the recipient account at 6:53pm on 17 June 2022 and had only blocked future payments.
Do now: On the day a scam complaint is registered, send every Regulated Entity in the funds chain a preservation notice covering transaction and session logs, device and IP data, call recordings, branch file notes, CCTV, Confirmation of Payee results, account-opening and KYC records, and recall and recovery messages. Run refer-backs in parallel, not in sequence. Triage every new scam complaint for a live threat: if the receiving account may still be open or receiving funds, send the identifiers to the NASC and the receiving bank the same day, without waiting for the refer-back to end.
4. Start from what has already been proven
AFCA runs each new complaint as a new, discrete case to be considered on its merits in complete confidentiality. HSBC admitted in the Federal Court that it failed to comply with the ePayments Code in 97% of cases over 44 months, yet our members with HSBC complaints are still asked to establish what went wrong after this case has proven the victims did not "voluntarily authorise" their scam. AFCA relies on court decisions when they assist the bank, by excluding matters a court has dealt with, but not when court findings would assist the victim.
Do now: Keep an internal and confidential register of regulator findings, AFCA determinations and confirmed systemic issues by firm and typology. Require case managers to check it, maintain confidentiality and tell the complainant whether regulators and law enforcement have confirmed that the member firm complied with "best industry practice". Where a firm has admitted a failure, the firm (not the victim-survivor, as in the current process) must demonstrate to AFCA why it does not apply.
5. Case managers should not talk victims into settling for meagre amounts
Victims regularly tell us they were advised by AFCA staff, early and informally, to expect little, even where published determinations favoured them. Coming from the ombudsman, that advice carries weight and pushes victims toward low settlements. Complainants are also asked to "open" conciliation calls with a statement outlining the legal facts of their case, without ever being told this would happen. Complainants must then explain a complex fraud typology unassisted, against senior bank lawyers who know precisely what legal points they can stand on.
Do now: Dispute resolution advice to a scam victim must be consistent with AFCA's own determinations and given in writing rather than verbally. AFCA staff could run "Ask AFCA anything" Q&A sessions where complainants can get guidance about how complex AFCA cases are resolved. AFCA should summarise the fraud typology so the victim does not have to.
6. Pause the interest on stolen money, especially when defrauded through criminal deception
In seven of the settlement fraud cases in Appendix 1, a bank continued to charge interest on the stolen funds while the complaint was open. One victim waited 20 months for a determination on a $270,000 mule account scam while the sending bank charged interest. The victim is paying the bank for the crime they were victimised by, and AFCA determinations endorse this.
Do now: Ask every Regulated Entity to suspend interest, fees and collection activity on loans connected to the stolen funds for as long as a scam complaint is open, and record and publish which firms decline in a proposed Scam League Table.
7. Make it possible to deal with AFCA paperwork from a mobile phone
Many victims have no desktop or laptop computer at home, and AFCA's portal is hard to use on a mobile device. This is a particular barrier for people with English as a second language, low digital literacy or trauma-related cognitive load. AFCA's duty to help complainants lodge is inconsistently applied, and proposed Rule 1.3.2 says only that AFCA "may" assist.
Do now: Offer phone lodgement and verbal updates over the phone as standard service levels for complex scam complaints, accept documents by email and photograph, and use interpreters by default when a victim asks.
Table 2: Summary of what AFCA can implement today to make EDR a safer experience for scam victimsWhat victims experience nowWhat AFCA can do tomorrowBurden it would removeAuthority forms re-requested; representatives shut out; linked victims closed as a "group"Confirm authority in an email or SMS; attach to all linked complaints from lodgement; phone the victim to talk through before any closure for authorityComplaints closed for authority issuesFiles closed by automated "no response" noticesPhone high-loss scam victims within 10 days before closure; automatic reopening if the victim needs itScam complaints closed for non-responseEvidence lost while refer-backs run in sequenceDay-one preservation notices; parallel refer-back; same-day triage of live mule accountsMedian days from registration to first evidence requestVictims asked to re-prove admitted failuresRegister of admissions and determinations checked at registration; a Scam League Table publishedComplaints resolved by reference to prior findingsInformal advice to expect littleWritten, determination-consistent settlement advice; member firm states its position firstSettlement value as a share of loss, by typologyInterest charged on stolen fundsRequest suspension of interest and collection while the complaint is openFirms declining to suspend interestPortal unusable on a phonePhone lodgement, email and photo documents, interpreters by defaultScam complaints lodged by phone
Part 2: Reverse the burden of proof
A person who has just lost their life savings must currently build their own case at AFCA to have any chance of reimbursement. The evidence they need is held by the banks, which routinely invoke "privacy" to withhold it. The SPF means Regulated Entities must take reasonable steps to prevent, detect, disrupt and respond to scams, and give complainants a statement of compliance with their IDR response. The table below sets out the standard evidence package we recommend AFCA move towards under the new rules to prevent and disrupt scams.
Table 3: The evidence gap in many AFCA scam complaints our community experiencesEvidenceWho holds itWhy the victim cannot get itWhat AFCA could requireTransaction, session, device and IP logs; changes to limits or payeesSending bankInternal systems; sometimes refused as "confidential" until an APP 12 request is madeProduced in every complaint within 21 daysFraud alerts, risk scores and whether a payment was held or queriedSending bankFirms say disclosure would help criminals, but this is already happeningProduced to AFCA; summary shared with victimConfirmation of Payee result, shown to the victim only during the transfer; the bank records relied on for a "match" are never revealed or verifiedSending bankNot visible after the eventProduced in every complaint; banks must prevent payment rather than let scam victims override name matchingTime the firm was notified; recall requests; AFCX messages; funds frozen or returnedSending and receiving banksVictims told recovery "was attempted", nothing moreTimestamped recovery log from each entity, with verified proof from a regulator that the bank recovered the funds it says it didAccount opening date, KYC and CDD records, beneficial owner, first transaction, limit changesReceiving bankVictim is not the receiving bank's customerProduced by receiving bank as a joined partyOnward transfers (at least 3–5 hops)Receiving and all intermediary institutionsVictim cannot see beyond the first accountMoney trail report in every complaint, with confidentiality preserved for law enforcement but assurance given to victimsSuspicious matter reportsAUSTRACConfidential by lawAFCA–AUSTRAC confidentiality arrangement so AFCA can confirm whether the account was reported, as backing for "compliance statements"Police reports and arrestsState and federal policeAvailable only by FOI or subpoena, and usually blocked when they show police failed to investigateAFCA could request "compliance statements" with State and Federal incident numbers to confirm whether the scam is a verified crime
What the rules should say
Every Regulated Entity joined to a scam complaint should produce the items in Table 3 within 21 days, without waiting for AFCA to ask for each one. Sending and receiving banks should produce a money trail report covering at least 3–5 hops and explain, with evidence, why funds could not be recovered. In case 12-24-130239, a bank that was both the sending and receiving institution satisfied AFCA with a single internal Jira note and no explanation of why funds could not be recovered. That should never be enough.
Adverse inference should be the default when information is not supplied
Rule A.9 already requires firms to provide information, and it is routinely resisted. Proposed Rule 1.9.6(a) says an adverse inference "will generally be drawn". Without automatic consequences, Rule 1.9 will suffer the same fate as Rule A.9. We recommend that where material evidence is not produced on time, AFCA must infer that the relevant control failed, must require a statutory declaration after one missed deadline, may order a payment to the complainant for the delay, and must refer repeated non-compliance to ASIC, AUSTRAC and APRA.
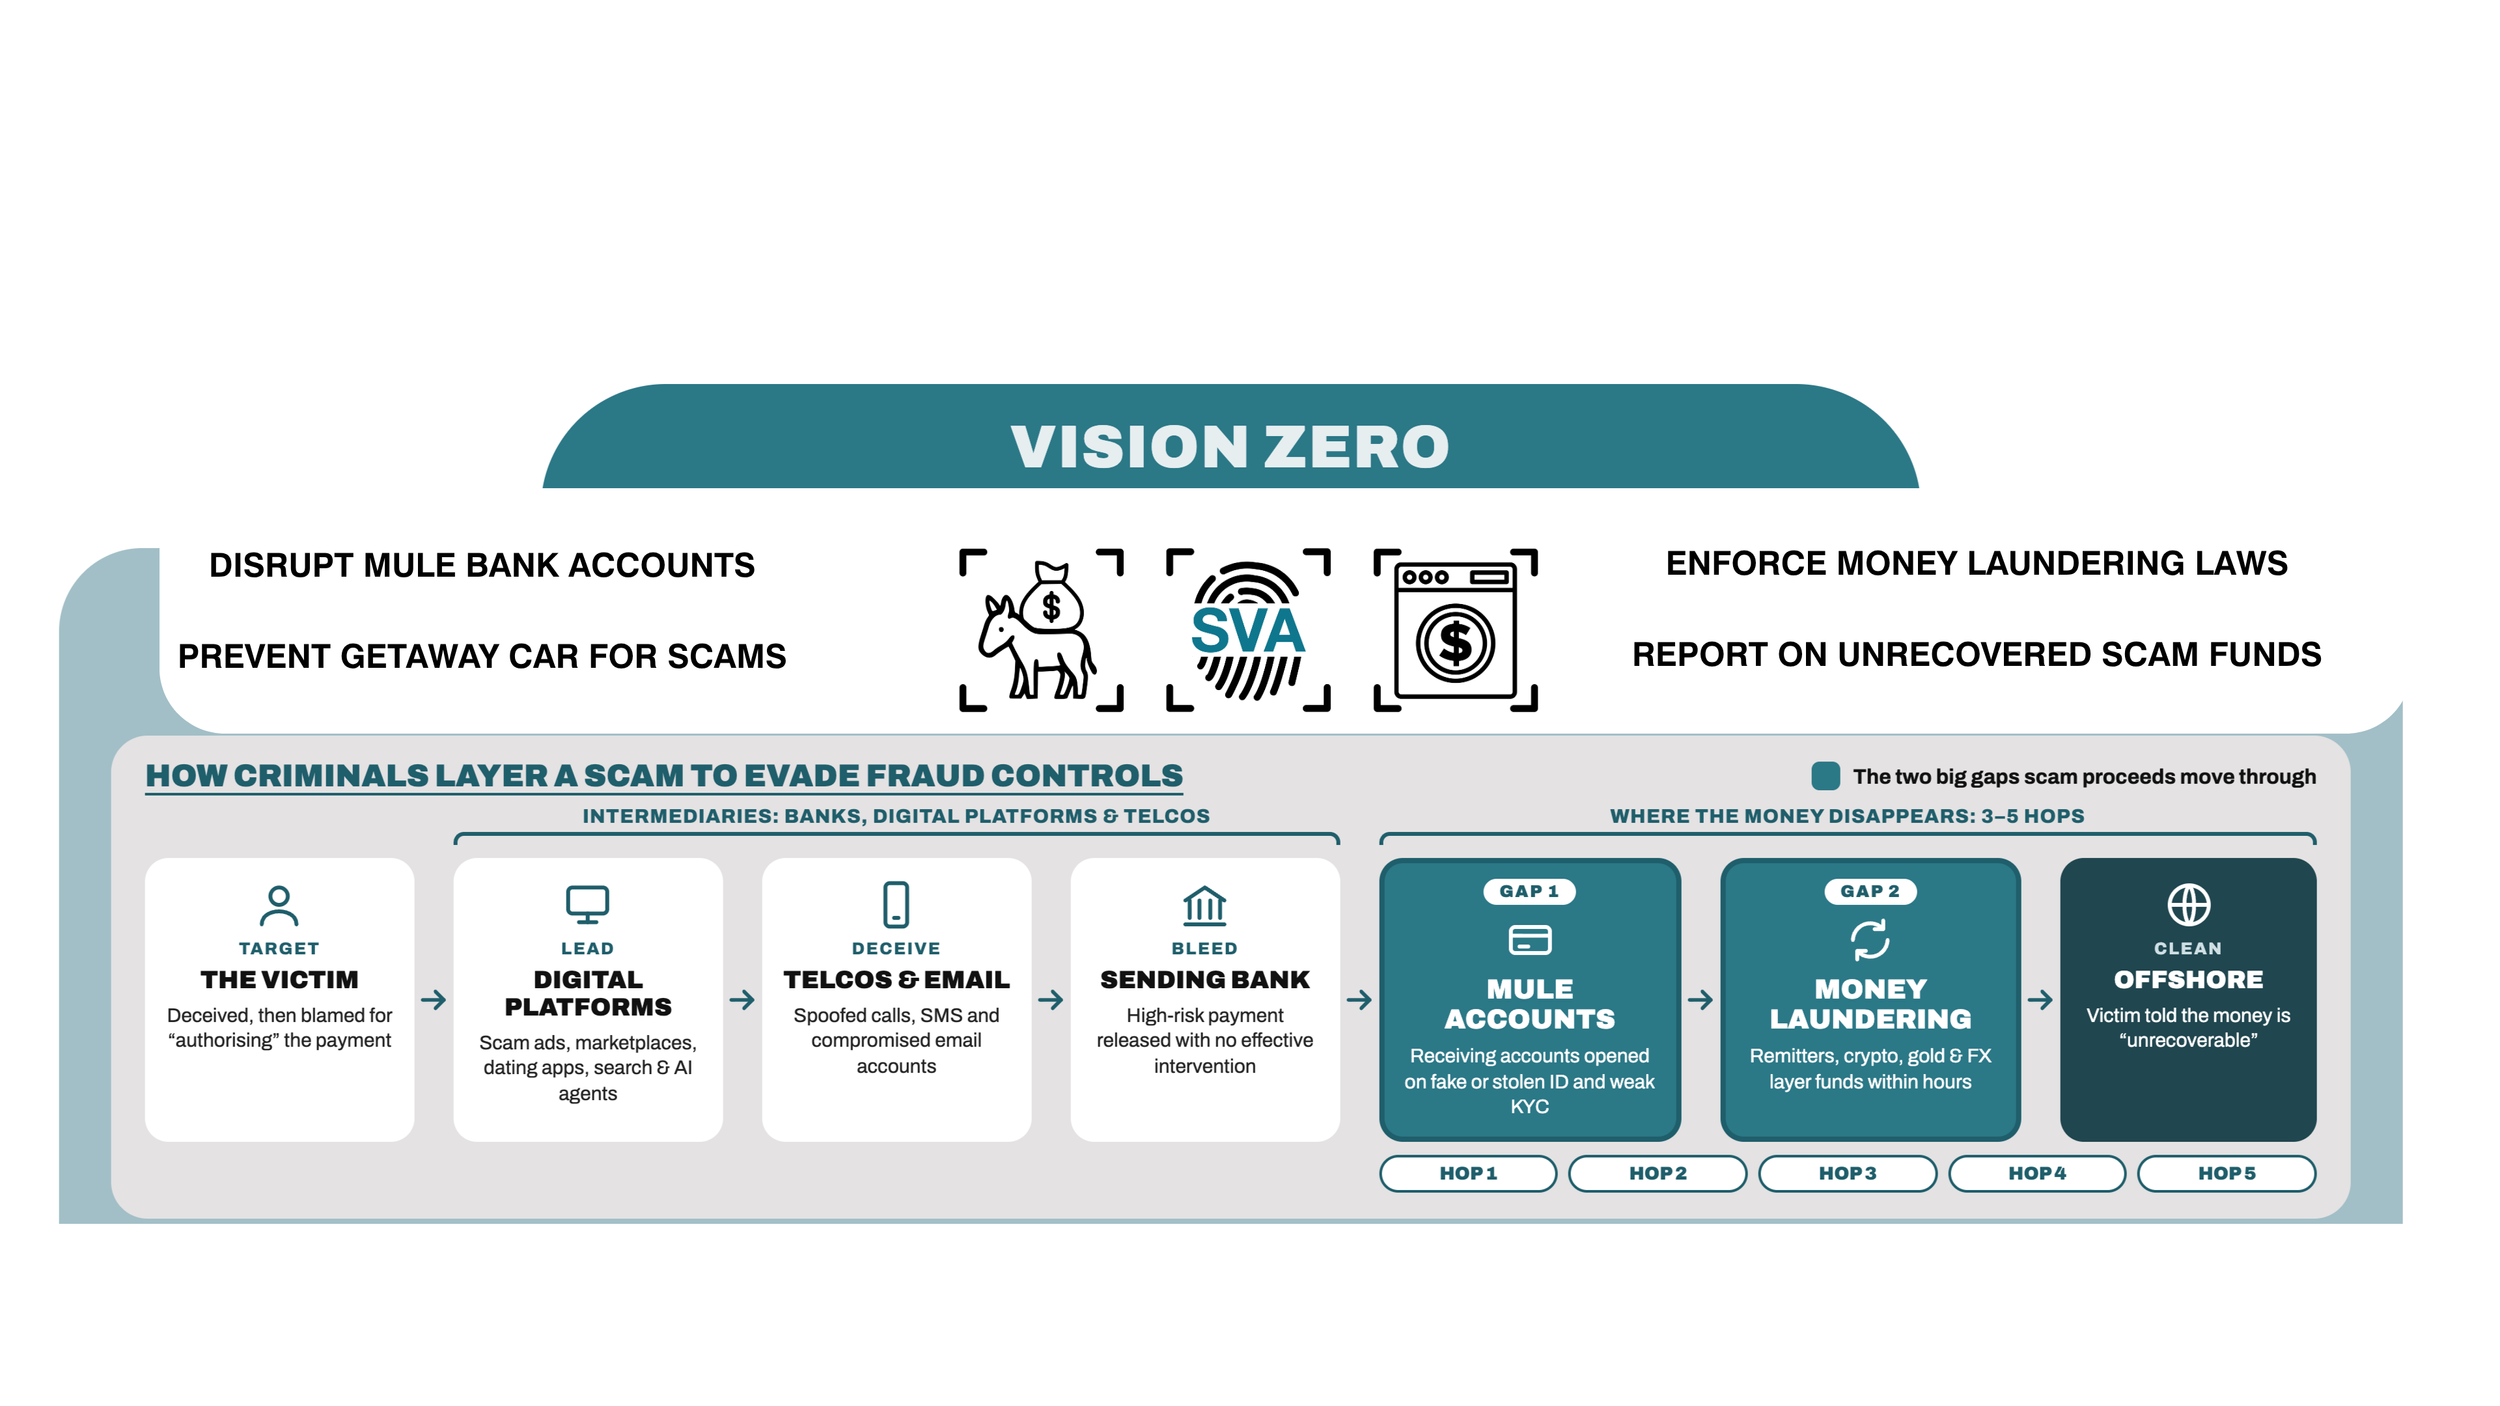
Image 7: Criminally architected thefts and frauds are designed to evade prosecution and reimbursement at AFCA. It's time to break the cycle to disrupt and prevent the crime.
The statement of compliance must be evidenced
A statement of compliance under s 58BZDA that asserts "reasonable steps" without the underlying records should not carry any weight. AFCA's Operational Guidelines should say that the firm bears the onus of showing, with contemporaneous records, which steps it took, when, and why they were reasonable for the scam type.
Deception always defeats "authorisation"
The SPF defines a scam by the presence of deception. A payment induced by bank impersonation, a doctored settlement statement or a fake term deposit is not a free and informed instruction in any meaningful sense. AFCA's Operational Guidelines should state that a victim's apparent authorisation of a deception-induced payment does not, on its own, establish that a Regulated Entity took reasonable steps, and that victims do not need to prove the criminal's intent.
Every entity in the chain is joined
Joinder currently happens in only 1.3% of complaints, yet victims' money often passes through several institutions. AFCA should presume that every Regulated Entity the money passed through is joined, and should do the work of identifying them. Proposed Rule 1.3.2 should say AFCA "will", not "may", help identify Regulated Entities that may be a party.
KYC and AML failures are SPF failures
Mule accounts are created through identity takeover, rented out, or opened through ASIC-registered companies. In the Supercheap Security case, the NSW Supreme Court found the director opened a NAB business account so it could be handed to a third party, and its per-transaction limit was raised from $10,000 to $100,000 before any funds arrived. Failures of account opening, customer due diligence and ongoing monitoring at the receiving bank should count as failures to take reasonable steps under the SPF, and a complaint alleging them should never be excluded as a complaint about "practice or policy" under Rule 2.2.2(c).
Image 8: Without reimbursement, there are no genuine scam prevention or disruption controls in place.
Part 3: Share verified scam intelligence within days, not months
AFCA should refer verified scam identifiers to regulators within 5 business days of a complaint opening. Our community has evidence that mule accounts are being generated at scale onshore in Australia. Criminals rotate mule accounts in days, while AFCA's proposed reporting pathways take months.
SVA considers the proposed Scam Rules a genuine improvement on what happens today. But they treat AFCA's systemic issues function as a slow, firm-first process built for product failures, not for organised crime that moves money through multiple institutions by exploiting insider loopholes that even Australia's Prime Minister is not immune to. AFCA's own consultation paper acknowledges that scams are, by design, committed at scale and intended to have systemic effects.
AFCA holds some of the best verified scam intelligence in Australia
A bank's actionable scam intelligence can be a single unverified report to a regulator. AFCA's evidence has more layers of verification and should be weighted above a bank report. By the time a scam complaint reaches AFCA, the same facts have been tested: the victim's evidence, the sending bank's IDR response, the receiving bank's records, and often a police report. AFCA also sees across institutions in a way no single bank can. Our members' cases show what AFCA already knows:
Linked mule accounts as a systemic problem. In case 12-00-1045764, AFCA was given evidence that doctored settlement instructions contained hidden text layers naming at least two other Commonwealth Bank mule accounts. One held a balance of more than $2.7 million, with transaction data showing Opal card use and small everyday purchases. That evidence stayed confidential when it could have prevented future mortgage misdirection fraud.
One account, many victims. At least 12 Australians paid about $1.36 million into a single NAB business account in the name of Supercheap Security Pty Ltd between 20 May and 22 June 2022. AFCA did not join the complaints together, nor disrupt other high-loss term deposit impersonation scams affecting our community.
Repeated Confirmation of Payee evasion. Criminals used the real, ASIC-registered names of unrelated businesses so the name check returned a match; see case 12-25-247156.
A typology hiding in plain sight. More than 400 HSBC scam victims complained to AFCA before ASIC acted to investigate the bank. The bank later admitted in the Federal Court that it failed to comply with the ePayments Code in 97% of cases over 44 months.
Each of these was actionable scam intelligence that AFCA could have escalated to save the next victim from harm. None reached regulators fast enough, because AFCA is overwhelmed with cases that it can never have enough staff, or accessible technology, to process fast enough.
Banks face a deadline to report scam intelligence, and AFCA should too
The SPF requires regulated entities to report actionable scam intelligence to the ACCC within a period prescribed by the SPF rules, backed by civil penalties (s 58BR). They must also take reasonable steps within a reasonable time to disrupt the activity (s 58BX). Treasury's Explanatory Memorandum says efficient and timely sharing is critical to the SPF's object. AFCA's obligations under s 58DD of the Competition and Consumer Act 2010 (Cth), and proposed Rules 1.17 and 1.18, work very differently.
Table 4: The proposed referral pathway compared with SVA's modelProposed Scam RulesSVA's recommended modelTriggerA systemic issue is identified after investigationAFCA holds evidence that a mule account, mobile number, fake domain or website, or entity was used in a scamFirst stepRaise with the firm and give it a reasonable opportunity to respond (1.17.2)Refer identifiers to the NASC, AUSTRAC, Australian Signals Directorate and SPF regulators; notify the firm in parallel; ensure complainants receive this as part of any "statement of compliance" notification; include it in Scam League Table reportingTimeframeNone specifiedWithin 5 business days of verificationPattern alertsOnly once a systemic issue is confirmedTypology alert after 3 matching AFCA complaints within 90 days, also included in any "compliance statement" and Scam League Table reportingPersonal informationDe-identified by default (1.17.5, 1.18.3)Scam identifiers shared in full, using the existing exception where de-identification defeats the SPF's objectSettled complaintsAFCA "may" refer a settlement (1.18.2)Identifiers from every settled scam complaint referred; confidentiality terms trigger RG 267.61 review by ASIC, and victims can open new cases on the same factsRecipientsSPF General Regulator and Sector RegulatorACCC/NASC, ASIC, AUSTRAC and APRA, and police where a crime is allegedPublic reportingAnnual report (1.20)Quarterly scam intelligence report and annual Scam League Table
AFCA's consultation paper says information-sharing arrangements and memoranda of understanding with SPF regulators are still being developed. We urge AFCA to settle them before the Scam Rules commence, with fixed timeframes written into the rules as quickly as possible.
Confidentiality is not a reason to delay
The SPF already contemplates sharing personal information where it is needed to disrupt scams. Treasury's Explanatory Memorandum gives the examples of the receiving bank account, the scammer's phone number and scam advertisement details. A mule account number is evidence of a crime, not a victim's private information. Proposed Rule 1.17.5 already lets AFCA share identified information where de-identification would not achieve the SPF's object. AFCA's Operational Guidelines should state that scam identifiers will always be shared this way.
Regulators should also share back. AFCA's own scams guidance asks banks whether they received ASIC or AUSTRAC warnings about a recipient. AFCA should receive those warnings directly, and should consider police and regulator reports in its decisions, protecting their confidentiality where necessary.
Why each regulator needs AFCA's intelligence
ACCC and the NASC can issue alerts and use fusion cells to disrupt fast-rising typologies before they scale, as the HSBC scam did in 2023–24.
AUSTRAC can test mule accounts against suspicious matter reports and pursue AML/CTF failures at receiving banks. It has already issued notices to 10 lenders over coordinated mortgage fraud.
ASIC can act on misuse of ASIC-registered companies to open mule accounts and evade Confirmation of Payee, and can use its oversight of AFCA under RG 267 to check that scam settlements comply with RG 267.61.
APRA can treat concentrations of mule accounts, unrecovered scam losses and repeated control failures at an authorised deposit-taking institution as operational risk and a governance issue for its board, not just a consumer complaint. AFCA referral data would give APRA an early, cross-institution view that no single ADI's own reporting provides.
Recommendation: a new Scam Intelligence Referral rule (1.17A)
SVA recommends AFCA insert a new rule alongside Rules 1.17 and 1.18:
Verified identifier referral. Within 5 business days of holding evidence that an account, phone number, website, social media profile or entity was used in a scam, AFCA must give those identifiers to the NASC and relevant SPF regulators.
Early typology alert. Where 3 or more complaints within 90 days share a typology, receiving institution or identifier, AFCA must alert regulators immediately, without waiting to confirm a systemic issue.
Settlements don't erase intelligence. Identifiers from every settled scam complaint must be referred, and settlement terms must never prevent victims reporting to regulators or police.
Money trail reports. The money trail produced under the standard evidence package must be passed to AUSTRAC and the NASC.
Excluded complaints still count. Identifiers in complaints AFCA excludes, including those over its monetary limits, should still be referred.
Public accountability. AFCA should publish quarterly the number of referrals, median days to referral, and funds frozen or recovered, and an annual Scam League Table by firm. Making corporations' scam prevention actions public is a low-cost and simple measure that would immediately make Australia more scam-safe.
Part 4: Lessons from mortgage settlement fraud, HSBC and Supercheap Security
Three different scam typologies, involving different banks and different AFCA cases, all failed at AFCA for the same five reasons. Further detail is in the Appendices.
The deception was architected by criminals exploiting insider threats and cybercrime-as-a-service networks in Australia and offshore. Data leaks, email compromises and other cyber-enabled tricks are sold and traded as cybercrime-as-a-service, with organised criminal groups at the top of the chain. These deceptions are increasing exponentially as Australia allows more data leaks to occur, and frontier AI is ramping up the risk. Scams are a microcosm of failed policy, where delays over "consultation" hurt everyday citizens while illicit capital wins, steals more money and sets up closer to Australian shores in Papua New Guinea and East Timor.
The role of mule accounts was ignored. Whether a mule account was created by identity takeover, rented out, opened through an ASIC-registered company, or operated by a complicit or exploited mule, the sending and receiving banks' roles are rarely tested, even after AFCA's March 2026 receiving bank changes.
The money trail was only traced by law enforcement, and the crime went unpunished. Victims were told by banks that recovery "was attempted", with no evidence of what was tried, frozen or returned. Victims are never assured that banks genuinely recovered the amounts returned to them, nor that funds impounded through proceeds of crime seizures will ever be returned to them. AFCA is their only hope of any recovery, unless they spend hundreds of thousands of dollars in legal fees (as the complainant in case 12-00-1034883 did).
Law enforcement evidence was not used. Logs, recordings and KYC records did not come before AFCA. Any victim who gains reimbursement through AFCA's existing EDR processes has had to find evidence of the criminality behind their fraud themselves.
The pattern was never joined up. Connected complaints were handled one by one, and some were closed by confidential settlement, which we believe is inconsistent with RG 267.61. Scams are evading "classification" as AI ramps up the threat vectors, data breaches and more.
Property settlement misdirection fraud
Criminals obtain a homebuyer's settlement details, usually through a compromised email account at the buyer, conveyancer, law firm or agent. They impersonate the solicitor, conveyancer or PEXA and send doctored payment instructions that redirect the settlement payment into a mule account. The funds are laundered within hours, through gold bullion purchases, ATM cash and foreign exchange, often before the bank tells the homebuyer the money is missing.
SVA has supported 16 cases totalling about $4.42 million, 13 at settlement and 3 after it. Mules were arrested in at least 5, yet 5 matters recovered $0, 6 closed with a confidential settlement, and victims were often left paying interest on the stolen funds. Only 2 of the 13 settlement cases were publicly reimbursed, at about 70%.
The problem is systemic. Treasury and AUSTRAC documents obtained under FOI show CBA had identified around $1 billion in suspect home loans by February 2026, and AUSTRAC has issued notices to 10 major lenders over coordinated mortgage fraud. Lawyers, conveyancers and real estate agents only became subject to AML/CTF obligations on 1 July 2026, leaving the settlement chain exposed for years. Confirmation of Payee is already being evaded: criminals use the real name of an unrelated ASIC-registered business so the name check returns a match (cases 12-25-247156 and 12-25-194305).
Image 9: This evidence, given to AFCA in 2023, could have prevented the property settlement frauds perpetrated against Australians in 2024 if it had been escalated to regulators under SVA's recommendations.
Mortgage fraud typologies, from loan application fraud to settlement misdirection, share the same laundering infrastructure, which operates onshore in Australia. Local bank mules with "lifestyle spending" on their accounts are recruited and then exploited by crime networks to withdraw cash from ATMs, transfer through foreign currency and buy gold bullion (which is apparently also "unrecoverable").
These property-buying frauds threaten the integrity of Australia's $11 trillion residential property market, yet AFCA and the civil courts rarely recognise the criminal deception. Our legal system was not designed for this level of exploitation. First and second homebuyers are especially exposed because they have no established pattern of large payments for a bank's fraud monitoring to compare against. A settlement-sized payment to a new payee, days before settlement, to an account opened recently, should be treated as a known high-risk pattern.
Image 10: Mortgage fraud has many different lead–deceive–bleed–clean typologies, but all are connected to insider problems that no "compliance statement" will ever reveal.
What would have changed the outcome: a day-one preservation notice to the receiving bank; a money trail report showing where the funds went within the first hours; referral of the hidden-text mule accounts in case 12-00-1045764 to the NASC and AUSTRAC; suspension of interest on the stolen funds; and a lead-case approach so each homebuyer did not have to prove the same typology from scratch.
Table 5: Victims absorb the cost of weak mule account and money laundering controlsProperty settlement misdirectionHSBC bank impersonationSupercheap Security term deposit fraudScale16 SVA cases, about $4.42m lost (13 at settlement, 3 post-settlement)1,000+ customers in ASIC's case; 400+ took complaints to AFCAAt least 12 victims transferred $1.36m into one NAB account; evidence Suncorp was also used, and domain evidence shows the pattern was widespread across multiple Australian banksWhere the money wentMule accounts with lifestyle spending and wages mixed inNewly created identity-takeover mule accounts, or direct overseas transfersA NAB business account of an ASIC-registered company, handed over for fraud before its first transactionHow it was launderedGold bullion, ATM cash and foreign exchange; Confirmation of Payee evaded using real business namesCoordinated exploitation of weak banking controlsDispersed to shell companies in the UK and Dubai; $0 recovered despite a Supreme Court winWhat a court or regulator foundMules charged in at least 5 cases; AUSTRAC notices to 10 lendersFederal Court admissions: ePayments Code breached in 97% of cases over 44 monthsO'Brien v Supercheap Security Pty Ltd [2024] NSWSC 1117; criminal charges later droppedWhat AFCA didOnly 2 of 13 settlement cases publicly reimbursed, at about 70%; banks allowed to keep charging interestVictims blamed for "voluntary" passcode disclosure; 8 cases reopened in 2026 for under-compensation but still delayed, despite Federal Court findingsMinimal reimbursement under a confidentiality deed
Scam or fraud?
SVA believes the word "scam" shifts attention to victim behaviour and away from corporations enabling theft. Criminal law professor Penny Crofts' research shows how corporations use sanitised narratives that obscure crime enabled through corporate structures. The UK has shown that mandatory reimbursement can keep a lid on an escalating fraud crisis: its Payment Systems Regulator reports that fraud losses are down, more victims are reimbursed and firms are investing in prevention. Australia should recognise these losses for what they are: fraud committed through the banking system. The Supercheap Security scam was highly architected using ASIC-registered entities and multiple domain registrations for fake versions of real Australian banks (domains the real banks have since bought for themselves).
Image 12: If Supercheap Security had been disrupted in 2022, SVA president Harriet Spring would likely not have lost $1.6 million to the same typology in 2023–24.
Part 5: What the law and ASIC's guidance already require
Much of what SVA suggests in this paper is not new policy. It is contained in existing regulatory guidance for AFCA and its member firms, applied consistently to scam complaints. ASIC must approve the Scam Rules and will consult the other SPF regulators before doing so. We ask ASIC to use that approval, and its ongoing oversight under RG 267, to make sure these requirements are met.
Table 6: Existing obligations and how AFCA should apply them to scamsSourceWhat it requiresHow it should apply to scam complaintsRG 267.61 (EDR settlements)AFCA must oversee settlements so they are limited to the complaint, do not stop referral to a regulator, and are not offered on onerous terms, to avoid AFCA scrutiny, or under duress or misrepresentationReview every scam settlement with confidentiality, non-disparagement or withdrawal terms, or an acceptance window under 5 business days; never allow terms that stop reporting to police or regulatorsRG 267 (systemic issues) and s 1052E Corporations ActAFCA must identify and report systemic issues, including problems affecting many customers or producing repeated similar complaintsTreat repeated complaints about one typology at one firm as systemic once 3 share a pattern; refer identifiers before the systemic investigation endsRG 277 (consumer remediation)Remediation cannot remove a right to complain to the firm or AFCA; assumptions should favour consumers; people wrongly excluded need a review pathwayApply to bank-run scam redress programs such as HSBC's; assess interest at a consumer-favourable rate and consider non-financial lossSPF s 58BR and s 58BXRegulated entities must report actionable scam intelligence within prescribed periods and take reasonable steps to disruptHold AFCA to an equivalent timeframe through a new Rule 1.17A; test each firm's own reporting and disruption in every complaintSPF s 58BZDAIDR responses must include a statement of complianceRequire the records behind the statement; an unsupported statement carries no weight and would continue today's information asymmetrySPF s 58DDAFCA must report systemic issues and certain matters to SPF regulatorsInclude APRA, AUSTRAC and police as recipients where relevant, not only the General and Sector RegulatorsAFCA Rule A.17Once a systemic issue is found, AFCA can require the firm to remedy loss for everyone affected, including people who never complainedCarry this power into the Scam Rules and use it for confirmed typologiesAFCA Rule D.3AFCA can award compensation for non-financial lossAssess non-financial loss in every scam complaint, including where a bank redress program paid none
Part 6: Answers to AFCA's questions
Operational guidelines SVA would like to see to help victims
Scam identifiers (accounts, mobile numbers, domain URLs and other common entities) are always shared with regulators in identified form under Rule 1.17.5.
The contents of the standard evidence package, the 3–5 hop money trail, and what counts as an adequate explanation of failed recovery are shared with complainants, with confidentiality preserved where needed for investigative purposes.
How AFCA weighs police reports, FOI releases, court findings and regulator admissions, even when the law is complex.
That apparent "voluntary authorisation" of a deception-induced payment under the ePayments Code does not by itself show reasonable steps, and victims do not need to prove intent.
Worked examples for property settlement misdirection, bank impersonation, term deposit impersonation and account takeover.
Plain-English guidance on how the six-year time limit applies when a victim learns of a loss years later, along with "Ask AFCA anything" education sessions for victims and a published Scam League Table.
Service standards for authority forms, closure for non-response, phone access and interpreters, with quarterly public reporting.
3.1 SPF complaint lodgement and referral to regulated entities
Q1. Is AFCA's proposed approach to refer-back appropriate for multi-party scam complaints?
No, not as currently framed.
Draft Rule 1.5.2 rightly keeps AFCA's discretion to start immediately, but a default of up to 30 days per entity is inappropriate where several regulated entities have not each had an equal chance to respond positively through IDR. The Treasury draft SPF Rules already give each entity 21 days to issue a Statement of Compliance, so a further 30-day refer-back risks duplicating that period and compounding harmful delays to complainants.
A blanket 30-day refer-back multiplies delay when several entities are involved. Refer-backs should run in parallel, not one after another. AFCA should skip refer-back where crime is alleged or less than 10% of funds were recovered. We believe that a scam league table, and a standard "scam information sheet" shared with the complainant that links the entities and makes the scam infrastructure clear, will also expedite these complaints. We recommend:
Parallel, not sequential. Refer-back periods should run concurrently across all named regulated entities, starting on the same day, so delay does not multiply with each bank, telco or platform in the chain.
Immediate progression in defined cases. AFCA should proceed immediately, without refer-back, where the victim shows the scam involves a reported and valid crime (a ReportCyber or police reference), where less than 10% of funds have been recovered, or where the same scam event is already before AFCA from another complainant (see Q8). This is consistent with our June 2025 and January 2026 SPF submissions.
Pause, never restart. A refer-back period should be paused, not restarted, where a victim is in demonstrated financial hardship, for example where mortgage interest is accruing on a loan the stolen funds were meant to repay. If the same financial banking group already has a scam-related determination on the same scam typology, it should not get a fresh 30 days.
Publish the effect. AFCA should publish how often refer-back is used, for how long, and its effect on time to resolution, so its real-world impact on victims can be scrutinised.
The HSBC complaint cohort shows that refer-back can end a complaint rather than pause it:
AFCA referred complaint 971494 to HSBC on 14 April 2023. It closed the file as "Resolved by FF" on 30 May 2023, although HSBC's fraud investigation was open and nothing had been paid.
In complaint 1069438, HSBC issued a "Final Resolution" letter in January 2024. Its fraud investigation outcome was not issued until 3 May 2024.
HSBC's IDR investigations ran far beyond ePayments Code timeframes. Mr B (12-00-1048367) reported his loss on 26 November 2023 and received HSBC's outcome on 31 July 2024, more than eight months later. His loss came from his home loan account, so interest accrued throughout.
The same cohort shows why an existing determination on the same typology should stop a fresh refer-back:
AFCA published the Mr T determination against HSBC (12-00-1016692) in August 2024. It found that passcodes obtained by a scammer impersonating the bank in HSBC's genuine SMS thread were not voluntarily disclosed, and awarded full reimbursement plus interest.
That same month, AFCA told a complainant it was meeting the Lead Ombudsman "about the HSBC complaints and our approach". Yet complaints 12-00-1048367 and 12-00-1065766 settled at AFCA in November 2024, and the complainant in 12-25-221597 accepted an HSBC offer in April 2025. Each settled below the full loss that the Mr T determination supported.
The Federal Court's orders of 18 June 2026 list the reports behind 12-00-1048367 and 12-00-1065766 among the 1,022 customers affected by HSBC's systemic failures.
SVA also supports raising the automatic IDR reimbursement threshold well above the $3,000 proposed in Treasury's IDR position paper, to $25,000. That is a matter for the SPF Rules rather than AFCA's Scam Rules, but it bears directly on AFCA's workload. Lower-value matters resolved quickly at IDR leave AFCA's limited investigative capacity for complex, high-loss, multi-party cases, which are the cases we see AFCA fail to resolve.
Q2. Have you identified any unintended gaps or consequences in coverage of classes of consumer who may be inadvertently included or excluded by the proposed complaint eligibility settings?
Yes. There are many gaps, particularly in high-loss scam cases.
Impersonation scams, including fixed-term investment and property settlement fraud. The Supercheap Security matters and settlement misdirection scams are examples. Victims risk falling outside coverage where the first point of compromise sits outside a Regulated Entity, even though a financial firm allowed the impersonation to succeed. AFCA should confirm that the sending and receiving banks remain in scope wherever the initial compromise happened. In ASIC v HSBC, HSBC admitted systemic failures in handling reports of unauthorised transactions, and payments made through account compromise, including by social engineering, were treated as made without the customer's authority.
Accounts opened in the victim's name. In complaint 12-26-397786 (earlier 971494, 12-24-161718 and 12-25-221597), the victim's money went into an HSBC Global Account opened in her name, which she says she did not open. It then left in pounds sterling to overseas mule accounts. Her loss spans a sending account, a receiving account, a foreign-currency product and a merchant. The telco layer is also missing from AFCA's view. ACMA found that TeleSign, a transit carrier, failed to pass on or report traceback notices covering more than 11,000 malicious SMS messages in November 2023 and February 2024. Carriers like TeleSign were never before AFCA. The SPF must close that gap.
Membership at the date of lodgement. Requiring the regulated entity to be an AFCA member "when the complaint is submitted" risks excluding victims whose funds passed through a fintech, crypto ATM or foreign-currency platform that later exits the market. Membership at the time of the payment loss transfer should be sufficient. In exploitative crypto ATM scams, for example, the victim can be groomed for three to six months before lodging any complaint.
Who is the "SPF Consumer". Family members, older people and people experiencing coercive control or elder financial abuse are often not the named account holder in a high-loss scam. In HSBC complaints 1049413 and 1066263, the elderly account holders' adult children acted as their representatives, and developed serious health conditions of their own, including a heart condition, anxiety and insomnia. Victims who hold savings through a family trust or small-business entity, as at least two Supercheap Security victims did, should not have to argue their way into eligibility. AFCA should confirm that the person who suffers the loss can complain, and that trust and small-business structures are covered where the Regulated Service is supplied to or for an individual's benefit.
Non-regulated wrongdoers. Mule account holders and shell-company directors are not regulated entities. AFCA should confirm that an unsatisfied court judgment against them does not reduce or exclude a complaint against the regulated entities, beyond preventing double recovery. O'Brien v Supercheap Security Pty Ltd (No 2) [2024] NSWSC 1196 is an example of such a judgment.
Q3. What further guidance regarding this proposed approach would be useful for the AFCA Operational Guidelines?
The Operational Guidelines should:
Explain in plain English, with worked examples, how the six-year time limit applies when a victim learns of the loss quickly but only much later discovers which entity received the funds, or what that entity knew. SVA recommends the limit run from the later date.
Include worked examples for complex typologies: bank impersonation and term deposit scams, settlement misdirection, investment scams using a shell-company mule account, and superannuation scams.
Commit to regular plain-language communications and open "Ask AFCA anything" sessions for complainants and their support people on the Scam Rules and guidelines.
"Awareness of loss" and "awareness of the regulated entity's role" are different dates, as two sets of cases show:
Supercheap Security. The victims knew within days that they had been scammed. They did not learn who held the receiving account, or what the receiving bank knew, until police inquiries, media investigation and court subpoenas years later.
HSBC. Victims knew within hours that money had gone. They learned that HSBC lacked adequate controls on its internal account transfer (IAT) payment rail only on 22 May 2026, when HSBC's Statement of Agreed Facts was published in the Federal Court. The complainants in 12-00-1065766 settled in November 2024, learned of ASIC's proceedings two months later, and HSBC refused to reopen on 20 January 2025.
3.2 Exclusions
Q4. What further guidance regarding this proposed approach to mandatory exclusions would be useful for the AFCA Operational Guidelines?
AFCA should confirm it can still consider a large loss up to the $1.263m limit, and point complainants to court options and legal help for the balance. Complex scams routinely force complainants to run parallel disputes against different parties, for example through the Telecommunications Industry Ombudsman or the OAIC.
In HSBC complaints 1049413 and 1066263, an elderly couple lost $388,350 of their retirement downsizing proceeds across 13 transactions. Partial recoveries came only after their family chased the receiving institutions themselves (Westpac, Cuscal and Monoova). Losses of this size, spread across several entities, need parallel pathways from the start.
Guidance should:
Confirm that the mandatory exclusion for complaints above $1,263,000 in direct financial loss is applied with clear written reasons. AFCA should refer the victim to alternative avenues (court, legal assistance, litigation funding information and the relevant regulator) rather than simply closing the file.
Explain how the exclusion will operate for high-value property settlement and superannuation losses, given fast-rising property values.
Make clear that court proceedings against a mule account holder or non-member entity do not trigger any exclusion for "matters already dealt with by a court" against a different, regulated respondent, provided there is no double recovery.
Report each year, as part of the Scam League Table, how many SPF complaints are excluded on monetary grounds and the total value excluded.
Q5. What further guidance about how AFCA may approach its discretion to exclude complaints would be useful for the Operational Guidelines?
SVA's main concern is proportionality and trauma-informed practice. Guidance should make clear that the discretion to exclude a complaint as "frivolous, vexatious, misconceived or lacking in substance" is not used against a genuine victim who:
repeatedly seeks clarification because AFCA or a regulated entity has not adequately explained a complex, multi-hop scam;
raises new evidence that emerged after a decision (for example from court proceedings, police or FOI);
pursues other lawful avenues at the same time; or
is highly traumatised and so is not always responding with clarity. Dealing with AFCA commonly puts victims back into a trauma state, where they can quickly become frustrated that they are not being heard.
The HSBC cohort shows why:
One victim holds four AFCA case numbers (971494, 12-24-161718, 12-25-221597 and 12-26-397786). No earlier complaint ever reached a merits decision.
Complaints 12-26-406450 and 12-26-439028 were lodged on genuinely new evidence: the Federal Court record in ASIC v HSBC, which did not exist when the earlier complaints (12-00-1048367 and 1069438) closed.
None of these complainants should be treated as vexatious. This is consistent with AFCA's duty to help complainants lodge and progress complaints. AFCA should also publish, in de-identified aggregate form, how often each discretionary exclusion ground is used and against which classes of complainant, so consumer groups can monitor for disproportionate impact.
3.3 Multi-party complaints and complaint resolution approach
Q6. Does the proposed AFCA approach appropriately reflect the multi-party nature of SPF complaints?
Partially.
The joinder and removal mechanisms in draft Rule 1.6 are a sound framework. But AFCA's own data shows joinder occurred in only 1.3% of complaints in FY26. That rate must rise substantially, because SVA members typically report their funds moving through several institutions.
SVA recommends a presumption that every regulated entity through which funds are shown to have passed is joined, unless AFCA records reasons why it should not be. The complainant, who by definition cannot see the money trail, should not have to identify each party and request its joinder.
Supercheap Security. The victims only learned the receiving account belonged to a shell company, not to themselves, after the money was gone. The receiving bank is best placed to explain how that account was opened, monitored and allowed to move funds offshore. In O'Brien v Supercheap Security [2023] NSWSC 21, Ball J struck out the victims' claims against NAB, the receiving bank. His Honour held that a duty on a bank to stop its own customer defrauding strangers would, in effect, be a duty owed to the world at large. Before the SPF, a receiving bank that hosted a mule account owed a non-customer victim almost nothing in negligence. The SPF changes that, and AFCA's joinder practice must now bring receiving banks in as a matter of course.
HSBC. In complaints 1049413 and 1066263, 13 transactions went to newly created payees, mostly accounts at HSBC itself. HSBC was therefore both the sending and the receiving bank, yet no receiving-account evidence was volunteered. The victims were left to chase the other receiving institutions themselves.
The telco layer. The spoofed SMS messages that began these scams travelled through a transit carrier that was never before AFCA.
AFCA's view of the cohort. Advocates acting for several HSBC victims were told AFCA saw "not enough commonality" to treat them as a group. SVA's group complaint (12-26-431688) tests that view.
Q7. What further guidance regarding this proposed approach would be useful for the AFCA Operational Guidelines?
Guidance should set default expectations for:
Tracing depth. AFCA (or the regulators it reports to) should trace a minimum of three to five "hops" as a matter of course, consistent with bank insiders' confirmation that financial institutions can typically trace transactions this far.
Who pays for tracing. The cost should fall on the regulated entities, not the complainant.
Receiving-account evidence. Where a receiving bank is joined, it should produce its account-opening file, beneficial-owner verification and the account's first 30 days of activity, subject to the legal limits on disclosing suspicious matter reports.
Apportionment beyond AFCA's reach. How liability is apportioned where a later-hop entity is a non-member, offshore platform or unregulated individual. The unrecoverable share should not simply fall back on the victim.
The HSBC cases show what happens without these defaults:
HSBC C240138552445 and AFCA complaint 12-26-454918. The complainants were scammed on 27 January 2024. Their funds went to other HSBC accounts and left on 29 January 2024, a two-day window in which they could have been blocked. Their questions to AFCA about where the money went next remain unanswered.
Complaint 12-25-221597. On 23 April 2025, the complainant asked through AFCA for receiving-account and recall records. They were never produced.
Statements of Compliance must carry real accountability. Each regulated entity should explain, in writing, why funds could not be recovered through IDR, EDR, law enforcement or ReportCyber, and when it first learned of suspicious activity on the account.
Q8. How should AFCA adapt its current complaint resolution and decision-making approaches to handle similar SPF complaints under Rule 1.8.2(c)?
Scams increasingly defy categorisation as frontier AI rapidly scales up the financial harm of a targeted exploit. Mortgage fraud, the HSBC SMS impersonation scam and the Supercheap Security case all show why a cohort approach is needed.
Supercheap Security. In the AFCA cases relating to this fraud, the complainants dealt with the same fake AMP staff using the same fake email domains, and paid the same NAB account in their own names within the same week. At least one other CBA customer did the same. Only one CBA customer had a payment blocked, after CBA received intelligence about the fraudulent NAB business account. This is exactly the "same Scam event or activity" that draft Rule 1.8.2(c) is designed to address.
HSBC. The Federal Court's orders list 1,022 customers who reported unauthorised transactions between January 2020 and August 2024. HSBC's redress program is reassessing 1,045 customers. Across the cohort the victims describe the same features:
the same spoofed messages appearing inside HSBC's genuine SMS thread;
the same "fraud team" phone script;
the same internal transfer rail; and
the same control gap, which HSBC admitted ran for 12 months from 29 May 2023.
AFCA had two published determinations covering this typology:
934078 (September 2023, Beyond Bank). Passcodes disclosed to a caller spoofing the bank were not voluntarily disclosed.
12-00-1016692 (August 2024, HSBC). The Mr T determination.
Yet most HSBC complaints closed by settlement below full loss, including 12-00-1048367, 12-00-1065766 and 12-25-221597. We believe a correctly applied lead-case approach would have applied the Mr T reasoning across the cohort. Other bank impersonation scams using the same typology (spoofed SMS bank impersonation) could also have been prevented.
Image 13: Mr C's AFCA case 12-24-130239 revealed that ANZ told him his account was not "eligible" for Falcon security protection, and only showed AFCA a screenshot of an email to its own staff to "prove" the bank had tried to recover stolen funds. Mr C did not voluntarily authorise his payments, and police told him mule accounts were reinstated because they had genuine lifestyle spending. This bank-to-bank mule typology was also present in the HSBC scam for which HSBC was later penalised.
SVA strongly supports AFCA developing a "lead case" or cohort approach under Rule 1.8.2(c) for near-identical scam complaints, so victims do not each have to re-establish the same facts about a common fraud. This matters most where identifiable scam infrastructure is shared, such as domains, spoofed sender IDs and common mule accounts. Any such approach must:
let each victim seek their own compensation and have their individual circumstances weighed;
never justify a lower standard of individual inquiry;
treat what a regulated entity learned from one victim's report as relevant to its conduct towards every later victim of the same event;
take a consistent investigative approach (as outlined in Part 1, building a timeline and a lead–deceive–bleed–clean vector); and
trigger a systemic-issue review and referral under s 1052E of the Corporations Act 2001 (Cth) where the same entity appears across a cohort.
Where a determination already exists against the same bank for the same scam type, it should apply by default unless the member firm shows the facts are materially different. Each victim must still get an individual resolution, with no assumption that an authorisation engineered through deception was voluntary.
3.4 How AFCA will gather and share information for SPF complaints
Q9. Does the proposed information gathering approach appropriately enable AFCA to obtain information necessary to resolve SPF complaints?
No. An information-gathering power is only as strong as the consequence for ignoring it. Banks have already shown they will ignore AFCA requests for information.
Draft Rule 1.9.3 narrows the confidentiality exception, which SVA welcomes. But member firms routinely rely on confidentiality to withhold transaction histories, CCTV, KYC records and account-opening files. SVA members also report bank file notes that do not match their own recollection or records. The HSBC cohort shows each of these problems:
Logs withheld. In complaint 12-25-221597, the complainant asked in writing for her internet banking and IP logs before deciding on HSBC's time-limited offer. She never received them.
Bank findings contradicted by the victim's own records. In complaint 12-00-1065766, HSBC held the complainants liable partly because they had ignored "clear and proximate" in-app warnings. The complainants' contemporaneous notes and screenshots indicate those warnings were introduced months after their scam.
Logs that do not support the finding. In complaints 1049413 and 1066263, HSBC's own logs, obtained through AFCA, showed that the passcodes HSBC relied on could explain fewer than half the disputed transactions.
Alerts not acted on. A consumer advocate who reviewed several HSBC files reports that the logs showed a login from an overseas IP address within a minute of the customer's own login. He also reports HSBC conceding in conciliation that fraud alerts were not reviewed for 12 to 14 hours.
The standard applied versus the facts later admitted. AFCA's preliminary view in 12-00-1048367 (April 2024) was that there is no contractual or legislative requirement for a bank to manually monitor accounts for scams. HSBC later admitted in the Federal Court that it lacked adequate fraud rules, behavioural biometrics and device-identification controls on the rail used in these scams. None of this was known to complainants when they were asked to settle.
SVA recommends the Scam Rules:
(a) Require a standard information package without a request. Sending and receiving regulated entities should automatically produce:
the transaction history for 28 days either side of the scam;
login, device and IP records and any fraud alerts generated;
evidence of the funds' onward path for two to five hops;
Confirmation of Payee name-match results;
the receiving account's opening and beneficial-owner verification file; and
the date and content of any scam intelligence the entity held or received about the account.
(b) Make the adverse inference mandatory. Draft Rule 1.9.6(a) already says an adverse inference will "generally" be drawn. It should be drawn unless the entity proves special circumstances by statutory declaration under Rule 1.9.4. Non-compliance should also be referred to ASIC, AUSTRAC or APRA as a matter of course, using AFCA's reporting duty under s 1052E of the Corporations Act 2001 (Cth).
Image 14: When AFCA fails, individuals lose trust in governments and banks.
(c) Treat KYC and AML/CTF conduct as relevant to the complaint. AFCA should reverse the position in Determination 651819 that AML obligations are owed only to the government. Whether or not those obligations create private rights, a regulated entity's compliance with them is plainly relevant to whether it met its SPF "prevent", "detect" and "disrupt" obligations. That is the correct frame under Part IVF of the Competition and Consumer Act 2010 (Cth). The unexplained opening of an HSBC Global Account in the name of the complainant in 12-26-397786 shows why.
AFCA should also work with regulators and police to supply "compliance statements". These would protect confidentiality for law enforcement purposes while assuring complainants that authorities are taking their scam seriously and trying to hold corporations to account. The information package can exclude the fact or content of a suspicious matter report while still disclosing account-opening, monitoring and timing evidence.
Q10. Is a $10,000 cap appropriate for expert advice costs?
Doubling the cap from $5,000 to $10,000 is a reasonable start, but it will not be enough for the largest matters.
The cap will not cover the largest multi-hop, multi-jurisdiction matters SVA members describe, some involving losses over $1 million and laundering through cryptocurrency, gold or offshore company accounts. SVA recommends AFCA use its "special circumstances" discretion to exceed the cap in genuinely complex matters, and report annually how often and by how much the cap is exceeded.
Our proposed "compliance statements" from regulators and law enforcement would also help establish special circumstances. At present, victims have no assurance that state police are investigating their matters. This is despite state police working with the Australian Financial Crimes Exchange, as part of the Joint Policing Cybercrime Coordination Centre (JPC3), to stop funds leaving Australia. Meanwhile, the lack of transparency means victims cannot tell what happens to funds that are never recovered.
The HSBC cohort illustrates the gap. In Mr B's matter (12-00-1048367), police records later obtained under FOI (SAP2400031153) showed the calls came from spoofed numbers, and that officers initially sought a warrant before realising the scam was architected to move money through different mule accounts and make it unrecoverable. Police then filed the matter on 23 December 2024 with "no further avenues identified".
This should form part of broader fee-transparency reporting, in which AFCA members disclose how they resource their EDR obligations, including internal and external legal and advisory costs to support AFCA cases. The National Anti-Scam Centre could also target fusion cells at fast-rising typologies, such as the Chinese authority impersonation scam, before they scale as the HSBC scam did in 2023–24.
Q11. What guidance should be developed by AFCA to manage the use of GenAI-generated content by parties to a complaint?
Don't penalise victims who use AI to organise their evidence; for many, it is an access-to-justice tool.
SVA supports sensible management of excessively long or repetitive submissions, but cautions against guidance that limits a genuine victim's ability to use AI tools to organise complex evidence and state a claim they could not otherwise afford legal help to prepare. This matters most for people with English as a second language or low digital literacy.
The complainant in 12-26-397786 told AFCA she needed a Mandarin interpreter as early as 14 April 2023. Assisted drafting was the only way she was finally able to answer the 21 questions HSBC put to her in 2026. Several of those questions had no bearing on her facts, for example whether she had downloaded remote-access software. This suggests AI-generated or templated bank or AFCA questionnaires, which are another likely source of strain on AFCA.
Guidance should distinguish clearly between:
(a) a complainant using AI to help present their own genuine evidence and account, which should be encouraged as an access-to-justice measure; and
(b) a regulated entity or its paid representative using AI to generate bulk, templated or evasive responses. This is the more likely source of the "strain" AFCA describes and should be the primary target of any guidance.
All parties should remain responsible for the accuracy of what they submit, consistent with the Federal Court's Generative AI Practice Note cited in AFCA's paper.
We are also concerned about law firms profiting from the rise in AFCA cases by offering "no frills" legal dispute services. Some firms are charging superannuation fraud victims up to $15,000 per case. That is up to twice what other victims of similar superannuation frauds have been asked to pay, with some signed up at $7,500. We welcome AFCA's acknowledgment that the new rules will make this practice proliferate, and we urge government and regulators to do everything possible to stop the continued financial exploitation of people suffering life-changing scam losses.
3.5 Proposed monetary and compensation limits for SPF complaints
Q12. Do the proposed compensation limits appropriately reflect the nature and impact of scam-related harm that should be considered by AFCA?
Aligning the direct financial loss limit with the $1,263,000 monetary limit is an improvement, but not a sufficient one, given the rising harm from property and superannuation fraud. In particular:
(a) the limit will still exclude the largest property settlement and investment scam losses SVA members report, some above $2,000,000 in a single event;
(b) doubling the non-financial loss cap to $12,600 per regulated entity is welcome but modest against the reality of scam trauma, which members describe as relationship breakdown, loss of housing and diagnosed mental health impacts lasting years; and
(c) none of the limits address the compounding harm of a victim paying interest on a loan, or drawing down retirement savings, while a complaint is unresolved. In one NAB mule-account case SVA has raised with AFCA, the victim has waited more than 20 months for a determination.
HSBC victims show how this plays out:
In 12-00-1048367, $49,900 was scammed from a home loan, and interest was charged on the loss for the whole of the eight-month IDR investigation and the AFCA process that followed.
A single mother of three lost $49,965 on 2 February 2024. She borrowed from friends for eight months to cover rent, food and school costs before her funds were returned.
HSBC's own 2026 redress program has since paid interest to complainants such as those in 12-00-1065766, which shows interest was always calculable, yet it was not awarded while those complaints were before AFCA.
SVA recommends AFCA's decision-making approach explicitly direct Decision Makers to consider suspending or reversing interest on the disputed amount as a standard interim step while an SPF complaint is on foot, not only in a final determination. Where a victim has had to access superannuation early because of the scam, the lost earnings and any tax cost should be recognised as indirect financial loss.
Q13. Are the proposed limits for legal and other professional costs adequate?
No.
The $5,000 cap (plus indexation) is inadequate for property settlement and complex multi-party investment scam matters, where victims may need a lawyer, forensic accountant or fraud specialist simply to understand their own case.
In HSBC complaints 1049413 and 1066263, the family was asked, after the dispute had been negotiated, to sign an additional indemnity letter. They feared it would affect their rights if new information emerged, and avoided signing it only because a not-for-profit legal centre intervened. SVA recommends:
raising the cap for losses above $100,000, and wherever a victim needs a professional to respond to a regulated entity's own legal representation in conciliation;
allowing AFCA to recognise reasonable costs of prior court proceedings against non-regulated wrongdoers where those proceedings produced evidence AFCA relies on; and
publishing fee data for paid representatives (see Q19), so the right level for these limits is evidence-based.
We also propose that raising the IDR reimbursement limit to $25,000 would give complainants a "standing start" to resort to civil litigation if they need to. SVA would prefer that AFCA becomes the free, fair and accessible dispute resolution service intended under legislation, but regularly sees that this is impossible in scam complaints where criminals use insider threats to exploit broken internal systems that AFCA, regulators and law enforcement will never become aware of.
3.6 Decision-making approach
Q14. Does the proposed alignment of non-financial loss wording with AFCA's existing Financial Firm Rules appropriately capture the degree of non-financial loss that may be suffered in SPF complaints?
No. Scam harm includes trauma, suicidal thoughts, family breakdown and losing a home, often made worse by the trauma of dispute resolution.
Scam-related non-financial loss is qualitatively different from the "inconvenience" contemplated by the existing wording, which was developed for ordinary financial services disputes. Victims in our network report post-traumatic stress, suicidal ideation, family breakdown and loss of their home, arising from the scam and compounded by an institution's conduct during the dispute, such as continuing debt collection or interest charges.
The HSBC cohort shows harm caused by the institution's conduct after the scam, not only by the scam itself:
In 12-00-1048367, the complainant wrote that being told the liability fell on him, rather than on the bank whose systems were spoofed, was "almost as distressing as the scam itself".
In 1049413 and 1066263, the victims' adult children were also traumatised and developed a heart condition, anxiety and insomnia while managing the dispute for their non-English-speaking parents.
In 1069438, the complainant's account was restricted from 30 October 2023 to 3 May 2024. The Federal Court penalised this type of conduct separately.
SVA recommends scam-specific wording that expressly recognises psychological and relationship harm caused or worsened by a regulated entity's conduct during and after the scam, including delay, poor communication and refusal to engage with new evidence, not only harm from the entity's role in enabling the scam. AFCA's own paper acknowledges these post-scam conduct harms; the rule wording should reflect them. Delay is the most harmful factor of all, which is why SVA also supports raising automatic IDR reimbursement to $25,000 (see Q1).
Q15. Should parties be required to notify AFCA of terms of settlement of any EDR complaint for the purposes of public reporting and closing the complaint?
Yes. Parties should be required to notify AFCA of settlement terms.
AFCA should publish de-identified, aggregate settlement data for scam complaints, including typical settlement amounts as a proportion of loss, by scam typology and by regulated entity, so systemic under-compensation can be identified. The HSBC cohort shows why. The resolution letter in 12-00-1048367 recorded that the bank "assumes no liability" and foreshadowed a deed of release. In 12-25-221597, the complainant accepted an offer within a 14-day window. She had not received the logs she had asked for, and did not have the interpreter she had told AFCA she needed. When the complainants in 12-00-1065766 asked HSBC to reopen after learning of ASIC's proceedings, HSBC relied on their settlement and on the claim that "each case is unique".
Settlements reached through AFCA during 2023–24 had several features:
releases covering complaints to "any court or authority";
confidentiality backed by clawback;
non-disparagement clauses; and
acceptance windows as short as one business day, put to elderly or non-English-speaking complainants.
SVA also recommends that draft Rule 1.16.3's prohibition on non-disclosure clauses be extended to settlements of SPF complaints reached at any stage of AFCA's process. At a minimum, no settlement clause should prevent a complainant from:
telling AFCA the terms of settlement;
reporting the underlying conduct to a regulator, law enforcement, a parliamentary inquiry or the media; or
warning other consumers about the specific fraud typology involved.
This supports AFCA's own statement that SPF outcomes should not be subject to confidentiality arrangements that prevent appropriate transparency and disclosure of participant conduct to regulators.
Q16. What further guidance about AFCA's proposed approach to decision-making would be useful?
Guidance should:
explain, with worked examples, how liability will be apportioned between regulated entities under the SPF framework once finalised, and confirm that a victim need not identify which entity breached which obligation before AFCA will investigate;
set out a clear, accessible process for a complainant to ask AFCA to reconsider or reopen a complaint when material new evidence emerges from court proceedings, police investigations, FOI or media inquiries;
address how AFCA will treat victims whose earlier determinations applied pre-SPF standards, for example the widespread pre-2024 banking position that the payee name in a transfer instruction is not checked, now superseded by Confirmation of Payee and the SPF "prevent" and "detect" principles; and
confirm whether such victims have any avenue to have their matter reconsidered under the new framework, and if not, say so plainly so they can pursue other options.
Complaint 12-00-1065766 shows the gap. HSBC refused to reopen it in January 2025. The complainants' report is listed in the Federal Court's orders among the 1,022 affected customers. HSBC's 2026 redress program then paid them interest but no further principal, leaving about $5,958 of their $47,808 loss unrecovered. Without a clear reconsideration pathway, material new evidence of this kind cannot reach a decision-maker.
Image 15: AFCA's failure to force member firms to obey the law on mule bank accounts and money laundering has directly contributed to Australia's escalating scam crisis.
3.7 Expectations of party behaviour
Q17. Does reference to AFCA's Engagement Charter in Rule 1.2.2 assist stakeholders in their understanding of how they should participate in the AFCA process?
The Engagement Charter is a helpful reference point, but it does not reset the power imbalance SVA members experience at AFCA.
HSBC victims describe this imbalance directly. In 12-00-1048367, the complainant says he was told that if he pressed harder he might end up with nothing. Another HSBC complainant says she felt pressured and threatened by her AFCA case manager and stopped engaging, which harmed her initial case outcome. Another complainant alleges that an HSBC case manager told them to "get down on my knees and thank me for the $2000".
Complainants are often asked to open conciliation calls with their own statement, only for an experienced bank lawyer or bank case manager to respond with detailed knowledge of prior determinations and banking law that the complainant had no knowledge of. SVA recommends that the Engagement Charter, or the Scam Rules directly:
require each regulated entity to give the complainant its position, reasons and the documents it relies on, in writing, before any conciliation call; and
require disclosure of the internal and external legal, accounting and advisory services the entity has engaged on the complaint, with costs measured and reported in aggregate.
This ensures AFCA does not create a new systemic problem in which victims must pay professionals to participate in what is meant to be a free, fair and accessible scheme. It also aligns with licensees' existing duty to act efficiently, honestly and fairly under s 912A(1)(a) of the Corporations Act 2001 (Cth). In the superannuation fraud cases we support, we see other victim support groups actively encourage victims to use paid legal or financial advisers at AFCA without disclosing that AFCA is supposed to be a free, fair and accessible dispute resolution service.
Q18. Should the definition of 'Paid Representative' be expanded to include lawyers and accountants? Does this give rise to any unintended consequences?
No objection, as long as financial counsellors, community workers and family members can still help freely.
SVA opposes a for-profit industry growing off scam victim harms and believes AFCA could put its revenue to better use by offering more accessible communication to help victims, including regular "Ask AFCA anything" sessions and tailored, trauma-informed case management that helps victims understand the complexity of their case rather than automatically expecting victims to deal with it. Guidance should include:
a plain-English, WCAG-compliant decision tree, with translations, showing which rules apply to a complaint;
an online training library for complainants and support people, written to a Year 9 reading level, covering complaints that span the 31 March 2027 commencement date or involve an entity that is both a Financial Firm and a Regulated Entity; and
links to previously published determinations on similar scams, especially panel determinations.
Q19. Are there other industry, regulatory or system-wide reforms that should be considered to address the conduct and engagement by paid representatives in EDR?
Yes.
AFCA acknowledged in its webinar that the new rules are likely to encourage more for-profit law and advice firms charging victim-survivors. We have already seen this, with SOS Super spruiking for-fee services to victims at fees between $7,500 and $15,000 for what should be a free service. SVA recommends:
(a) a public register or reporting mechanism under which law firms and paid representatives disclose the fees they charge clients in SPF complaints, so financially devastated victims can weigh the value of a paid service; and
(b) a requirement that regulated entities disclose at the outset which external legal representatives and advisers they have engaged on the complaint. Banks, telcos and digital platforms can always out-resource a complainant, and full disclosure is vital to understanding the secondary markets that fraud is creating.
Recommendation (a) is likely to need Treasury or ASIC action beyond AFCA's Rules; AFCA can nonetheless collect and publish the data it already receives as part of the Scam League Table.
Image 16: Global fraud amplifies the market power of financial criminals. AFCA must protect Australians while not allowing legal firms to further exploit scam victims who feel they need paid representatives.
Conclusion
AFCA's proposed Scam Rules are a genuine step forward, but they will not change what our members keep experiencing unless AFCA changes how it works as well as what its rules say. Criminals deceive, a mule account receives the money, the money is laundered, and the victim is left to prove it at AFCA, sometimes after their authority form has gone missing or their file has been closed by an automated notice.
The three typologies in Part 4 tell the same story. Homebuyers are losing settlement funds to mule accounts controlled by criminal networks, and even where mules were arrested, victims were left paying interest on stolen money. HSBC admitted failing to apply the ePayments Code in 97% of cases over 44 months, after more than 400 customers had been through AFCA, and some HSBC cases remain unresolved at AFCA in September 2026. Supercheap Security victims won in the NSW Supreme Court and have recovered nothing.
In each case, AFCA held pieces of the pattern but did not share them fast enough to protect the next victim. With the changes we propose, AFCA can:
stop its own processes adding to victims' harm, starting tomorrow;
place the evidence burden on the firms that hold the evidence;
refer verified scam identifiers to regulators within 5 business days;
hold receiving banks and the whole laundering chain accountable;
stop confidential settlements silencing victims; and
publish a scam league table.
Appendix 1: HSBC
Ten HSBC customers in our community remain under-compensated or awaiting resolution at AFCA, despite the Federal Court proceedings and ASIC's statement that further payments would be made by the end of July 2026.
What the Federal Court proceedings delivered
The Federal Court imposed a $35 million penalty on HSBC on 18 June 2026 for failing to protect customers from scams. HSBC admitted its failures.
The penalty was reduced partly because HSBC committed to repay 1,045 customers through a Customer Redress Program. The Court did not order the redress or set its conditions, so victims cannot enforce it.
The $35 million penalty (order 4) and $2.3 million in costs to ASIC (order 6) go to the Commonwealth, not to victims. Only AFCA can order compensation to individual victims.
Reported unauthorised transactions totalled $34.6 million. As at 21 May 2026, HSBC had returned $27.9 million, of which only $7.1 million came through the redress program (SSAFA [58]).
Why the redress program leaves HSBC scam victims short
HSBC reassesses its own liability. 68 Phase 1 customers (16%) were found "customer liable" and receive nothing (SSAFA [51], [55]), by the same bank that admitted systemic failure to apply the ePayments Code from January 2020 to August 2023.
Low interest. Lost earnings were calculated at the rate of the account the money left (SSAFA [54]), not the RBA cash rate used in AFCA's Mr T determination. RG 277 expects assumptions that favour consumers.
No non-financial loss. HSBC admitted some customers suffered non-financial harm, but the program pays only principal and lost earnings. AFCA can award non-financial loss, but only if the victim complains.
Earlier settlements. Phase 3 reassesses 138 settled complaints (SSAFA [49]). Some 2023–24 settlements carried confidentiality, withdrawal and non-disparagement terms, signed before HSBC's admissions were public.
Appendix 2: Bank complaints are rising
If July 2026 is typical, complaints against the major banks will rise again in 2026–27, with deposit-taking payments and housing finance among the top AFCA complaint types at almost every bank. Projections are SVA's simple annualisation of July 2026 and are indicative only.
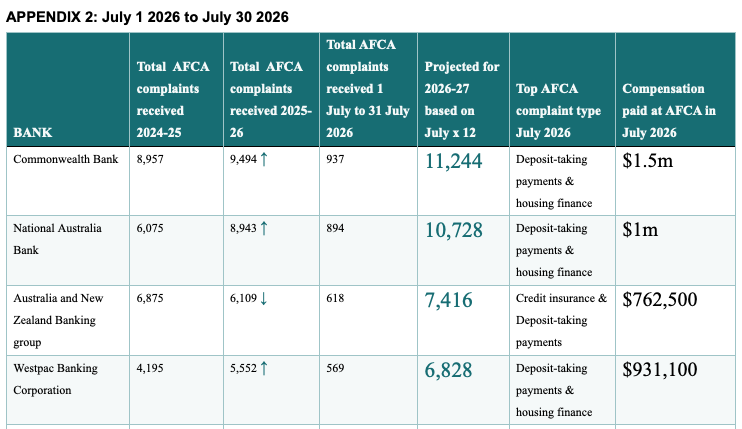
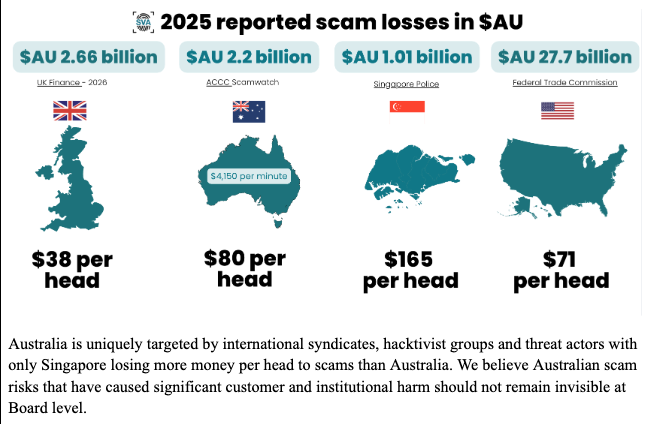
Prudential accountability can ease harm
Every dollar an Australian loses to a scam is treated as their problem — until a regulator decides otherwise. This submission argues APRA already has the tools to change that: the same prudential powers used to hit Bendigo Bank with a $50 million capital add-on could just as easily apply to HSBC, where a Federal Court found years of known, unfixed control failures. So why hasn't it?
Scam losses need to be treated as a Board-level risk, with appropriate auditing and governance standards at financial firms to tackle fast-rising economic crime, writes Scam Victim Alliance in this submission about APRA’s new prudential standards

We welcome APRA's review of the prudential governance framework. We ask that the systemic risks of financial crime and scams be treated as material governance and operational risks that boards of ADIs must oversee. The Government already expects APRA to strengthen financial-system resilience, safeguard Australians' money and data against cyber threats, oversee emerging AI risks and hold regulated entities accountable for governance and risk-management failures capable of causing significant harm.
That harm is already occurring. Systemic weaknesses in identity takeover, scam detection, mule-account controls, payment interventions, complaint intelligence and remediation have exposed Australian consumers and small businesses to devastating financial and non-financial losses. We believe that when these weaknesses reveal material deficiencies in an institution's risk-management framework – which we contend happened to HSBC Australia between 2023 and 2024 – they should be considered prudential issues, not simply individual customer disputes.
As Australia's only self-funded, volunteer-led community dedicated to supporting people experiencing life-changing harm from financial crime and scams, we urge APRA to adopt stronger Board accountability, assurance and oversight of these risks to improve outcomes for all Australians.
Prudential Accountability Could Prevent Financial Harm for Thousands of Australians
APRA's purpose is to identify and respond to significant risks within financial institutions and the financial system, while holding Boards and management accountable for the prudent operation of their institutions. Scam Victim Alliance believes the Scam Prevention Framework legislation alone cannot deal with the threat of cyber-enabled financial crime and must be complemented by broader legislative, regulatory and prudential reform.
Our organisation believes existing ADI governance frameworks are failing to keep up with rapidly evolving systemic scams that expose Australians to sophisticated financial crime. We believe threat actors, crime networks and hacktivist groups are weaponising banking platforms and processes to steal and defraud customers, and that we need a whole-of-ecosystem approach – including reformed prudential standards – to protect Australian bank shareholders and customers from fast-escalating harm.
CPS 510 already imposes strong obligations for Board responsibility, information flows, conflicts management, fitness and propriety, and whistleblower protections – but these obligations do not explicitly address scam and financial crime risk or the intelligence generated through financial complaints.
Our organisation believes this could be a governance gap which means an ADI can technically comply with CPS 510 while its Board receives little meaningful information about financial crime losses and customer harm; fails to consider whether directors and senior executives have demonstrated effective oversight of these risks; and remains unaware of how rapidly evolving technology and control gaps are enabling new scam typologies. Most importantly, recurring scam typologies can remain classified as ‘individual customer matters’ that are blamed on ‘authorised’ transactions rather than recognised as evidence of systemic control failures or poor ADI governance.
This submission has three sections:
Suggested changes to CPS 510
HSBC case study: how 1,000 Australians were harmed and how it relates to Bendigo Bank
Scam and financial crime governance audit ideas
Section 1: SVA Proposed Changes to CPS 510
SVA asks APRA to amend CPS 510 so that scams and complaints relating to financial crime risks are explicitly built into:
The Board's non-delegable responsibilities (paragraph 13).
The policy governing what information reaches the Board (paragraphs 20–22).
The Risk Committee's monitoring role (paragraph 45).
The Audit Committee's oversight role (paragraph 41).
The definition of a reportable conflict (paragraph 74).
The fit and proper test for directors and executives (paragraphs 84–86).
The Board skills matrix (paragraph 47).
The annual Board performance assessment (paragraph 51).
Active enforcement of existing whistleblower protections (paragraphs 95–101).
The hallmark of good governance is not only how an institution responds after regulatory action, but whether a Board can spot warning signs early enough to prevent the need for regulatory action or law enforcement investigation in the first place. We think executive teams and Boards should be regularly scanning their business complaints data for any indication of new systemic typologies appearing.
The table below sets out suggested amendments, mapped to the exact paragraph of the draft standard.
ClauseWhat CPS 510 currently saysWhat SVA asks APRA to considerPara 13Lists the Board duties that can never be handed to someone else, e.g. setting risk appetite and overseeing “financial and operational resilience.”Add scam and fraud loss oversight to this non-delegable list, so a Board cannot treat scams as a customer-service matter that never reaches Board level.Paras 20–22Requires a policy on what management information reaches the Board, and requires senior managers to brief the Board “clearly, timely and transparently.”Require the policy to specifically cover scam and fraud complaint volumes, AFCA determinations and dispute outcomes, not only financial and prudential risk data.Para 45Sets out the Risk Committee's job: monitor risk position against risk appetite, advise on risk culture, and oversee how management implements the risk strategy.Add scam and fraud losses, mule-account activity and repeat scam typologies as matters the Risk Committee must specifically monitor and report on.Para 41Sets out the Audit Committee's job: oversee compliance and financial reporting, and ensure audit issues are “managed and rectified in an appropriate and timely manner.”Require the Audit Committee to review patterns in scam-related customer complaints and external dispute resolution outcomes as part of its oversight role.Para 74Requires entities to identify, assess and manage all conflicts affecting customers, and keep a conflicts register.Confirm that a bank knowingly or unwittingly facilitating scam infrastructure (e.g. hosting mule accounts, ignoring internal fraud flags) is a conflict that must be logged and escalated under this paragraph.Paras 84–86Sets the “fit and proper” test for directors and senior executives: skill, character, judgement, and any adverse findings against them.Require entities to consider a candidate's track record on customer harm – AFCA determinations, ASIC action, or repeated complaint failures – as part of the fit and proper assessment.Para 47Requires a documented “Board skills matrix” covering the skills and experience the Board needs, based on the entity's risk profile.Require fraud, scams and financial crime literacy to be a named category in the skills matrix, given the scale of scam losses now facing regulated entities.Para 51Requires an annual performance assessment of the Board, committees and directors against their objectives.Require the annual assessment to specifically evaluate how the Board handled scam and complaint risk that year, not only general risk-management performance.Paras 95–101Already protects staff, ex-staff, auditors and contractors who disclose problems to APRA, and bans confidentiality clauses that would silence them.Ask APRA to actively monitor and enforce these protections, given evidence that confidential settlement deeds in scam disputes may currently discourage disclosure.
Section 2: HSBC Case Study
The $34.6m Systemic Failure That Hurt More Than 1,000 Australians
Refer SA firefighter victim impact statement
On 13 December 2024, ASIC commenced civil penalty proceedings in the Federal Court; the matter concluded in June 2026 with a $35 million penalty against the bank. Despite the fine and the negative publicity order, HSBC Australia has been sold to Blackstone Capital for a profit, while Scam Victim Alliance continues to represent customers who remain under-compensated for their losses. Scam Victim Alliance is still representing under-compensated HSBC customers at no charge to them, asking the Australian Financial Complaints Authority (AFCA) to reimburse given that the bank has not.
Total HSBC customer losses (2020 – March 2024)$34.6m+
Losses via internal transfer rails with no fraud detection capability$25.8m
Reporting cohort affected1,024 customers
Rise in bank impersonation reports in a single year380%
ASIC Federal Court civil penalty (concluded June 2026)$35m
Customers Scam Victim Alliance is supporting (Aug 2026)7 for <$200,000
Customers still undercompensated at time of penalty 100+ in court docs, SVA representing 8 of these at AFCA
Between 2020 and March 2024, criminal networks exploited HSBC Australia's internal account transfer payment rails, which had no fraud detection capability. This was not a single error but a corporate control gap that was allowed to run for years while customer losses accumulated. While we do not profess that such a small fine or $34.6 million leak of money was ever a prudential risk to HSBC Australia – HSBC Australia was always comfortably capitalised and liquid – imagine if the Board of HSBC Australia had intelligence in 2022 and 2023 that warned it of a looming systemic weakness with its internal payment rails.
The Government's Statement of Expectations to APRA
On the same day the Federal Court handed down its findings in ASIC v HSBC, the Government's July 2026 Statement of Expectations (SoE) to APRA removed any remaining basis for APRA treating scam and fraud control failures as ASIC's or AFCA's problem alone.
The newly published SoE requires APRA to “require that regulated entities implement prudent practices in relation to risk management” (clause 2.4). Scam controls are risk management. There is no carve-out in that instruction for fraud losses simply because they appear as a “scam” rather than a balance-sheet risk.
The SoE further requires APRA's capability to be “matched to emerging threats” and aligned with the Government's cyber security framework (clause 2.10). Scam typologies – spoofing, mule networks, AI-enabled social engineering – are an emerging threat to the payments system that could quickly scale and escalate as frontier AI and quantum computing arrive.
Clause 4.3 asks APRA to take “decisive action where systemic prudential or member outcome risks and failures in governance or risk management, have the potential to cause significant harm” – and names a direct comparator (“platform investment governance”). HSBC's conduct is the banking-sector equivalent: governance failure, known internally for years, causing systemic consumer harm.
Clause 4.6 requires regulated entities to maintain “robust cybersecurity arrangements to ensure the financial and operational resilience of those entities.” Fraud and scam controls sit inside operational resilience and are not a separate category APRA can ignore.
And clause 4.10 supplies the sharpest instrument: a “supervision-led and preventative approach… with a clear willingness to escalate to formal directions and enforcement action where necessary to prevent or remedy significant harm to depositors.” This is a government instruction to act before a $35 million Federal Court penalty is required – not after.
APRA already has precedent for treating governance failure as a capital and prudential issue, not merely a conduct one. Since 2018, APRA has imposed 5 capital overlays on insurers, 7 on banks, and 13 additional licence conditions on RSE licensees for governance concerns. Yet scam and fraud losses – despite the Federal Court's own finding that HSBC's failures were governance and operational-risk failures – have so far triggered only ASIC conduct action and AFCA dispute resolution, never APRA's capital-overlay or enforceable-undertaking machinery under APS 112 or CPS 510.
The new SoE removes APRA's ability to leave that gap open. If HSBC's own leadership knew about its control deficiencies for years and customers absorbed the loss, that is precisely the governance failure clause 4.3 instructs APRA to act “decisively” on – and clause 4.10 instructs APRA to escalate through formal directions before harm accrues, not respond only once a court has forced its hand.
Scam Victim Alliance calls on APRA to use its Statement of Intent, issued in response to this SoE, to commit to:
Treating sustained fraud control failures as a governance and operational-risk matter which could trigger capital overlays under existing CPS 220 / APS 112-style powers rather than a regulatory matter referred on to ASIC or AUSTRAC or a customer dispute at AFCA.
Publishing supervisory expectations on fraud-control adequacy, in the same way APRA already does for cyber and operational resilience.
Publicly reporting, per its Annual Performance Statement obligation under clause 7.5, on how many ADIs have been subject to heightened supervision or capital add-ons for fraud/scam control deficiencies – closing the transparency gap SVA has already identified around undisclosed AFCA settlement outcomes.
Structural Comparison: Bendigo Bank vs HSBC Australia
On 18 August 2026, APRA imposed formal licence conditions on Bendigo and Adelaide Bank under s9AA(1)(a) of the Banking Act 1959, following an independent root cause analysis (Deloitte, commissioned at APRA's direction). They found Bendigo's non-financial risk management weaknesses were extensive, that the bank lacked a complete and reliable view of its regulatory obligations, material risks and key controls, and that material deficiencies in governance, accountability, compliance management, risk oversight and risk management capability had persisted despite years of remediation activity. APRA is maintaining Bendigo's existing $50 million operational risk capital add-on until it is satisfied the underlying prudential concerns are fixed, and worked jointly with ASIC and AUSTRAC on the response.
Our HSBC victim-survivor Mr B has just had his SAPOL FOI file (SAP2400031153) released – of the $49,900 he lost through HSBC's compromised Digital Secure Key process on 25 November 2023, the funds were broken into first-hop payments including two separate Bendigo Bank accounts (also Macquarie and Suncorp) before being further co-mingled with other scam-typology funds and dispersed into additional mule accounts. Bendigo Bank is a documented receiving institution in the same mule-laundering chain that moved Mr B.'s HSBC funds beyond recovery. What's more, state-funded police agencies have not arrested anyone in connection with the financial crime, which police state in Mr B.'s FOI file was orchestrated by an overseas syndicate.
Bendigo BankHSBC AustraliaDeloitte RCA: longstanding, pervasive non-financial risk management weaknesses; control gaps for yearsFederal Court (ASIC v HSBC, 18 June 2026): known control gaps for years, ePayments Code breaches in 97% of cases examined, inadequate prevention/detection/investigation/remediationRoot cause established by an APRA-commissioned independent reviewNo root cause established via independent review, but detailed in a Federal Court judgment, orders and statement of agreed facts – a higher evidentiary bar than Bendigo's own RCAAPRA licence conditions imposed – Independent Reviewer, Rectification Plan, Board attestation, quarterly reporting, FAR accountability tie-inNo APRA licence conditions imposed to date$50m operational risk capital add-on maintained until fixedNo capital add-on imposed
If weaknesses identified by a bank-commissioned consultancy report can trigger licence conditions on Bendigo, SVA believes a Federal Court's judicial findings of sustained, known control failure at HSBC might also respectfully be considered as a trigger for prudential licence conditions.
The Federal Court's findings in ASIC v HSBC were not just about financial losses but also that the bank – which has now sold to Blackstone Capital – also:
failed to have adequate systems to prevent and detect unauthorised transactions;
failed to comply with ePayments Code requirements in 97% of cases examined;
failed to properly advise customers how to regain access to their accounts after fraud-related restrictions were imposed; and
had deficiencies spanning prevention, detection, investigation, remediation and governance which were recognised by the Court as “serious… widespread and systemic.”
What SVA Urges APRA to Consider
Our organisation would urge APRA to consider:
Commissioning an independent root cause analysis of HSBC's scam and fraud control failures, mirroring the Deloitte RCA process, with findings reported directly to APRA, ASIC, AUSTRAC and State police agencies.
Imposing licence conditions under s9AA(1)(a) requiring HSBC to appoint an Independent Reviewer (subject to APRA veto), prepare a Rectification Plan with defined Target States, measurable Rectification Activities, and firm timelines, and provide quarterly reporting and Board Risk/Audit Committee minutes to APRA.
Considering whether an operational risk capital add-on is appropriate given that HSBC has sold out of Australia, on the Bendigo model, that cannot be removed until HSBC demonstrates – to APRA's satisfaction – that its scam and fraud detection controls meet the standard the Federal Court found absent.
Tying accountability to remuneration, requiring HSBC to reflect these obligations in the Accountability Statements of its FAR Accountable Persons and demonstrate that variable remuneration reflects whether rectification targets are being met so the executives who oversaw the control gaps face direct financial consequences, not just the shareholders and customers.
Requiring Board-level attestation from the HSBC Australia Chair and Risk/Audit Committee chairs once rectification is substantially complete.
Coordinating with ASIC and AUSTRAC, as APRA did with Bendigo, given the mule-account and money-laundering dimension of this case (Bendigo, Macquarie and Suncorp accounts all featured in the fund trail), recognising that HSBC's outbound control failure and Bendigo's inbound mule-account failure are two ends of the same laundering pipeline.
Australia is uniquely targeted by international syndicates, hacktivist groups and threat actors, with only Singapore losing more money per head to scams than Australia. We believe Australian scam risks that have caused significant customer and institutional harm should not remain invisible at Board level.
Section 3: Scam & Financial Crime Governance Audit Ideas
The Board could ensure that scam and financial crime risk is explicitly identified within the entity's risk management framework as a material non-financial risk, with a documented risk appetite statement, key risk indicators and escalation thresholds.
Definitions
Scam risk means the risk of financial loss, data compromise or customer harm arising from deception intended to induce a customer, employee or counterparty to transfer funds, disclose credentials, or redirect a payment.
Financial crime risk includes scam risk together with money laundering, mule account activity, identity theft and organised-crime-enabled fraud that uses the ADI's products, processes, staff interactions or payment rails to facilitate social engineering.
Complaint intelligence means the systematic analysis of Internal Dispute Resolution (IDR) complaint data and External Dispute Resolution (EDR) complaint data for the purpose of identifying emerging typologies, control weaknesses and systemic risk, as distinct from case-by-case issues.
Systemic control failure means a control weakness such as staff training, technical gaps, process gaps, audit controls or other internally examined processes that has affected, or is reasonably likely to affect, more than one customer, or that reflects a structural gap in fraud, cyber or financial crime controls.
Escalation Framework and Board Reporting
The Board's governance framework could set out how scam and financial crime risk is escalated from operational and complaints teams to senior management and the Board, and the maximum timeframes within which escalation must occur once a systemic control failure is identified.
The Board, or the Board Risk Committee acting on the Board's behalf, should report at least quarterly (and more frequently where risk indicators are elevated) covering, at a minimum:
scam losses and attempted scam losses, by emerging typologies, particularly examining how each customer became a lead, the deception at play, the transactional bleed and the money laundering/getaway vehicle that made the funds unrecoverable;
reimbursement and recovery rates and outcomes;
scam complaint volumes and trends, including IDR outcomes and EDR outcomes through AFCA;
emerging fraud typologies;
mule account activity detected and actioned;
identity takeover threats and patterns;
scam detection rate and value of scams prevented; and
systemic control failures identified since the last report and remediation status.
Reporting could be accompanied by management's assessment of root causes and trend direction, not just transaction-level or complaint detail alone. The Board Risk Committee's charter could explicitly include oversight of scam and financial crime risk within its mandate, consistent with the Board committee requirements of CPS 510 paragraphs 35 to 41. Where an entity combines its Audit and Risk Committees under CPS 510 paragraph 37, the combined committee must demonstrate dedicated agenda time for scam and financial crime risk at each meeting at which paragraph 3.3 reporting is presented.
Board Skills and Capability
The Board skills matrix required under CPS 510 could include demonstrated capability, across the Board collectively, in: cyber-enabled fraud; financial crime; artificial intelligence-enabled risk; digital identity; operational resilience; and organised crime threats.
Gaps identified against paragraph 3.8 could be addressed through the Board renewal plan or a documented director development plan, consistent with CPS 510 paragraph 49.
The annual performance assessment required under CPS 510 paragraph 50, and the independent performance assessment required under CPS 510 paragraph 53 for significant financial institutions, could evaluate how effectively the Board and its committees have overseen scam risk, emerging fraud trends, customer outcomes, remediation programs and the implementation of corrective actions.
Working with Complaint Intelligence
Entities could treat complaint data arising from suspected scams and financial crime as governance intelligence, with significant trends in complaint data – repeated typologies, recurring reimbursement disputes, or a common control weakness identified across multiple complaints – triggering a documented root-cause analysis, independent assurance review, and reporting to the Board Risk Committee. The entity could maintain a documented process for feeding root-cause findings back into fraud control design, customer remediation practice, process change and staff training. We believe reimbursement rates should be measured as part of this.
Escalation and Regulator Notification
Where the Board or senior management becomes aware of scam typologies scaling, the entity could escalate this to APRA, and to ASIC, AUSTRAC and the ACCC as relevant – not just the Fintel Alliance or the Australian Financial Crimes Exchange – according to the nature of the failure, within a timeframe set out in the entity's governance framework and, absent a documented justification, no later than 10 business days from identification.
An entity shouldn't rely on the resolution of individual AFCA or internal complaints as a substitute for escalation required under paragraph 5.1 where the underlying control failure is systemic and scaling on a week-to-week or month-to-month basis.
The Board must ensure management identifies and monitors scam and fraud risks that arise across the customer transaction ecosystem, and not only within the entity's own systems, including risks arising in novel and unusual ways through channels that suddenly scale or appear ‘unusual’.
Assurance and Audit
The entity's internal audit function, consistent with CPS 510 paragraphs 42 and 44, must include in its annual program an assessment of the Board's oversight of scam and financial crime risk, covering at a minimum:
verification that Board reporting under paragraph 3.3 occurred at the required frequency and content;
evidence of complaint-trend analysis and root-cause reviews;
existence and effectiveness of the senior executive accountability arrangement;
documented escalation to regulators for systemic control failures; and
evidence of ecosystem risk monitoring.
Conclusion
Our organisation believes scam and financial crime risk should sit alongside financial and operational resilience as a material governance responsibility requiring direct Board oversight. The Scams Prevention Framework – which is not rolling out until March 2027 – will require regulated entities to document governance policies and obtain annual senior-officer certification. However, the SPF's own Explanatory Memorandum acknowledges that code compliance does not equate to compliance with its governance principle, leaving “adequate governance” open to interpretation.
APRA's prudential toolkit is what can close that gap, as CPS 510 can turn a certified governance policy into a Board that is accountable, with capital and licence consequences, for whether that policy actually works. Directors and senior executives could be assessed on their actual track record in managing fraud risks and protecting customers from foreseeable harm by understanding rising systemic scam types.
Risk and Audit Committees could have an explicit mandate to examine scam losses, complaint intelligence, emerging typologies and systemic control failures – including settlement terms and any confidentiality provisions attached to scam-related IDR and AFCA outcomes. This would close the gap between information held deep within an institution and the risks ultimately visible to those responsible for its governance.
Existing whistleblower protections under CPS 510 should also operate effectively where employees seek to expose systemic scam or fraud-control failures. This is particularly important given SVA's concerns about confidentiality provisions, including those attached to AFCA-facilitated settlements, potentially discouraging disclosure of wider systemic problems that the SPF's disclosure and reporting obligations do not reach.
Our suggestions do not require APRA to be given an entirely new regulatory toolkit but instead tweak existing prudential governance mechanisms to prioritise recognising scam and financial crime risks – providing the structural accountability the SPF's governance principle was designed to encourage but, on its own, has no power to enforce.
ASIC Chair Sarah Court has promised timely reimbursement to HSBC victims after the historic case.
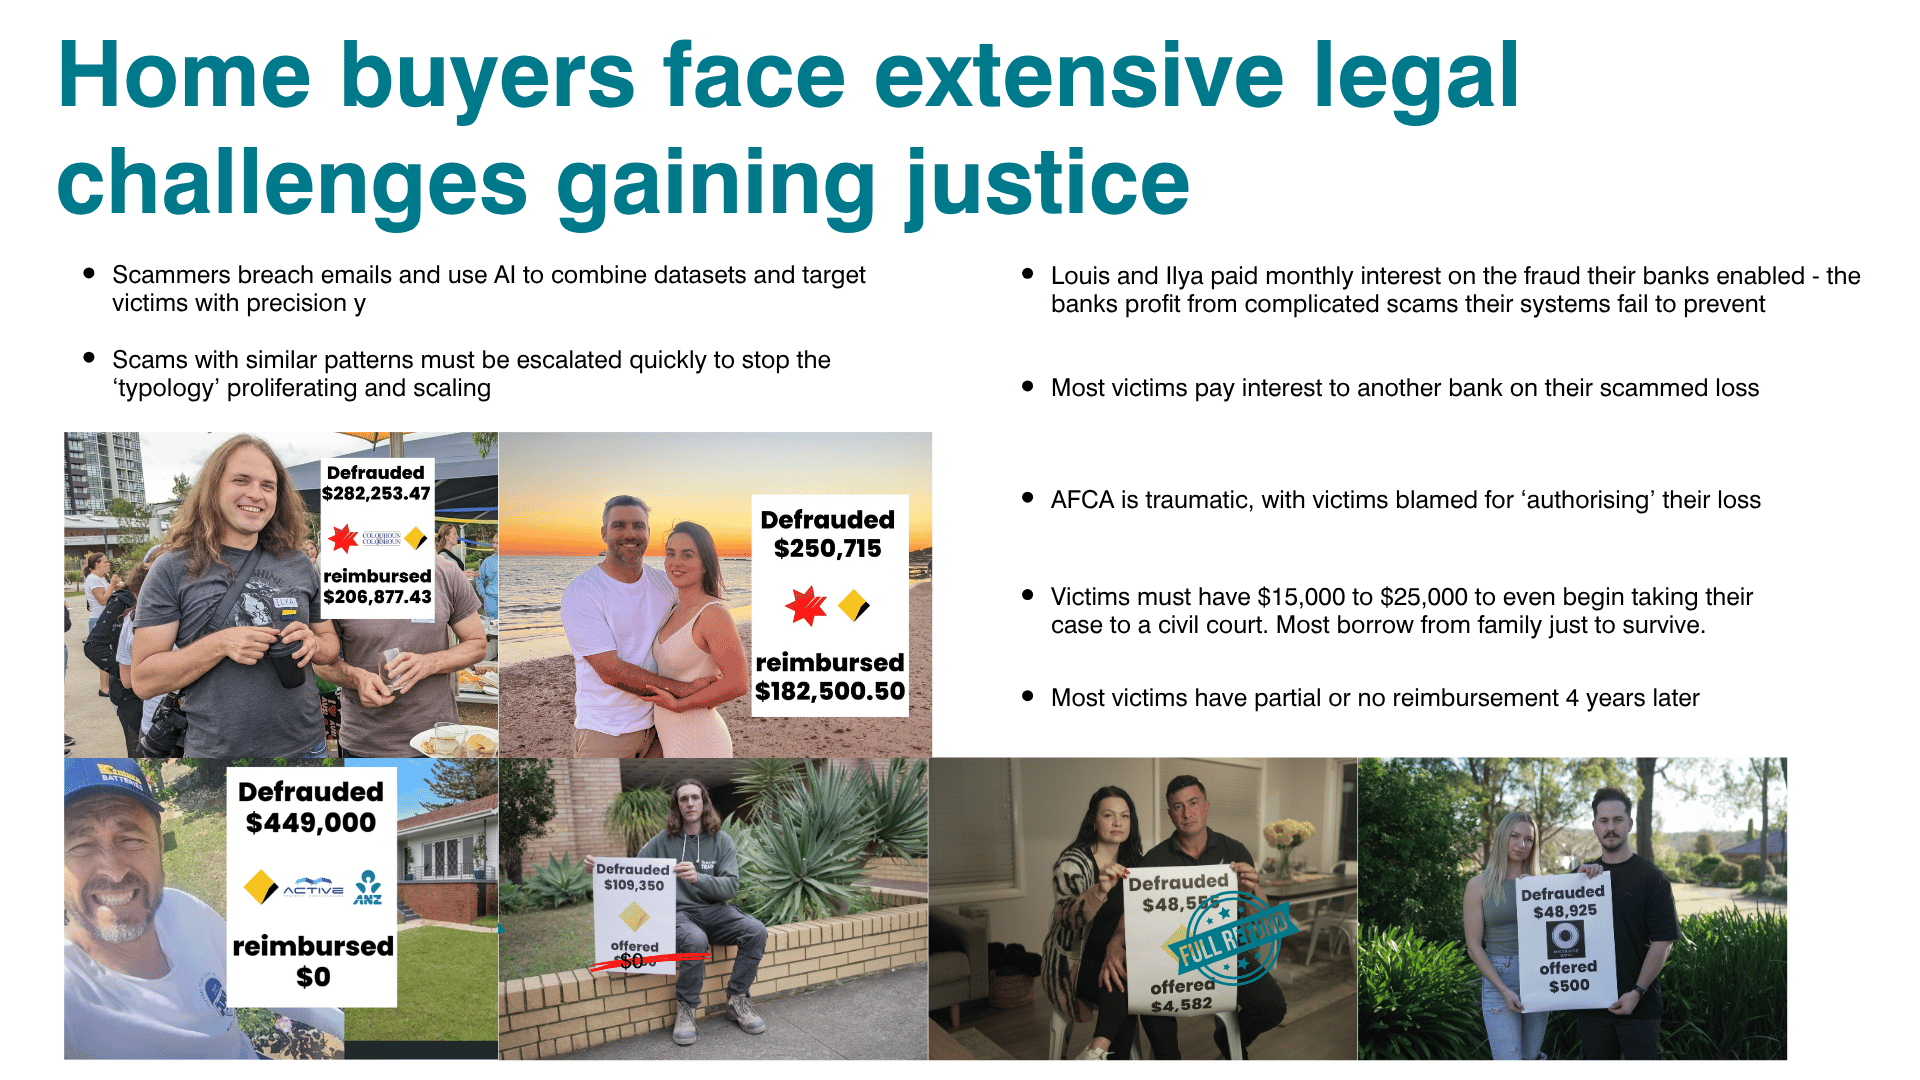
Threatened with costs: why nsw homebuyers need help dealing with lawcover
The NSW home purchasing process is open to exploitation by Serious and Organised Crime, with victims left in legal limbo. Neither Lawcover nor Australian banks will plug the gaps, meaning that buying a home in NSW can leave people with life-changing losses that no-one will refund them for.
Criminals are slipping fake bank details into solicitors' email threads at the moment of settlement. For the families who lose everything, the fight against their lawyer’s insurer is only one part of the battle. Payment redirection losses rose 9.3% in 2025, yet the federal Scams Prevention Framework doesn't cover email. Here's one gap we are asking the NSW Parliament to close to stop life-changing financial losses plaguing NSW homebuyers.
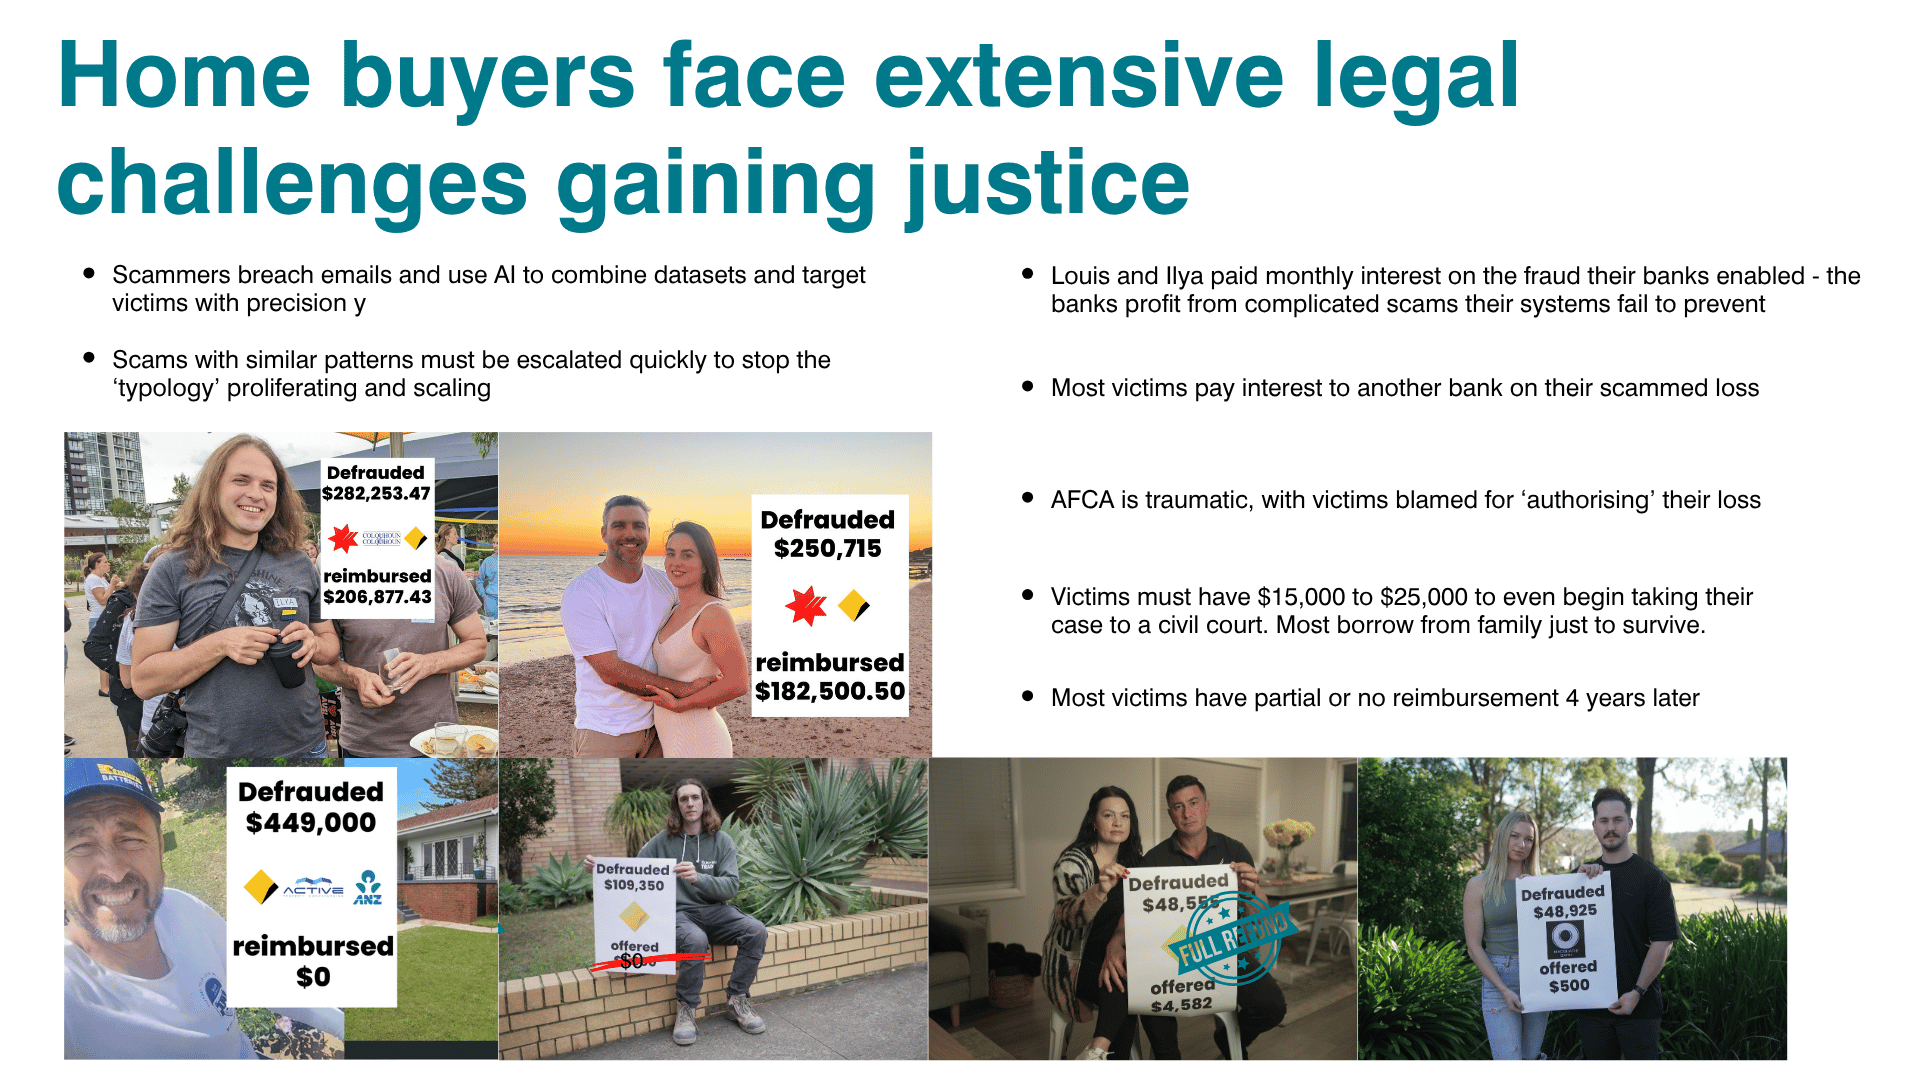
5 reforms the NSW Parliament could consider to help MORTGAGE FRAUD victim-survivors
Does Law Society ownership of the dominant insurer for these crimes create an unmanaged conflict of interest requiring structural separation or independent oversight.
Could genuine market competition would improve claims outcomes and give consumers an alternative to a single gatekeeper.
Whether independently verifiable digital-forensics standards should be mandatory before a "no compromise" finding can be relied on to deny a claim.
Whether higher, mandated trust-account and email-security standards should apply to property settlement transactions.
Whether defrauded third-party consumers should have a standing, cost-protected pathway to challenge a Lawcover denial such as through NCAT or a similar State-based tribunal system.
Mortgage fraud victim-survivors suffer extreme financial losses when organised crime exploits gaps in the system to steal their property settlement funds. These survivors are trapped in an impossible liability circle.
The bank blames the customer. The lawyer points to the criminal. The insurer disputes liability. State police are under-funded and the Australian Federal Police simply run a reporting system tracking what happened, but never chasing the money trail. The victim-survivor homebuyer is left carrying all the financial consequences, along with the shame of being scammed and blamed.
These property misdirection fraud cases raise a larger public-policy question. NSW requires property transactions to operate within a highly regulated electronic conveyancing system, and earns substantial tax revenue from property transactions. Yet when organised criminals exploit weaknesses around that system, who is ultimately responsible for making an innocent homebuyer whole? Certainly not Lawcover.
For the NSW homebuyers who we support after their life-changing fraud loss, their trust in Government and banks is forever broken. They did what Australians are encouraged to do: saved, borrowed and bought a home. Then criminals stole the money intended for their home purchase and no-one accepts any responsibility for the loss.
With only one company allowed to sell insurance to lawyers in NSW, and it being owned by the same group that's supposed to watch over lawyers (the Law Society of NSW), there's no effective insurance to protect citizens from a highly destructive economic crime they can rarely recover from financially or emotionally.
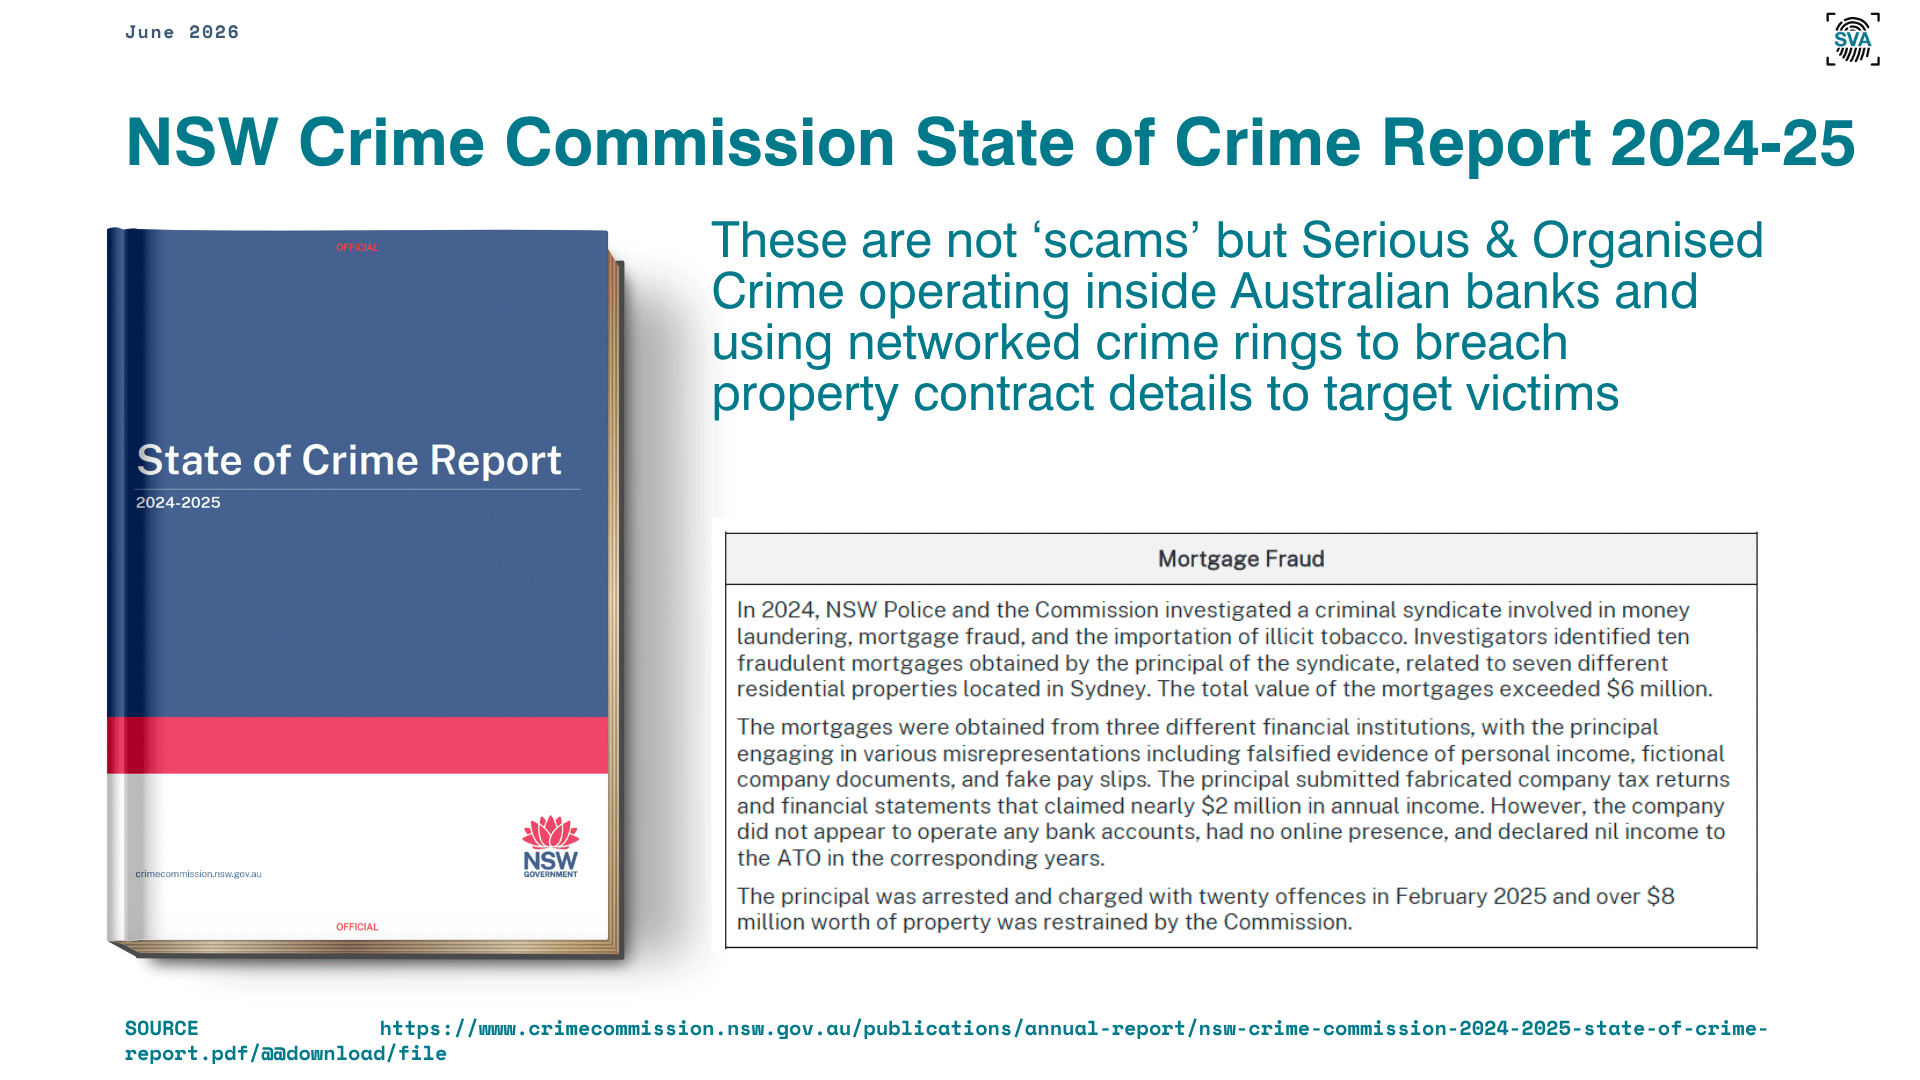
The problem with Lawcover for victims of property misdirection fraud
Imagine being lucky enough to buy a home in NSW, the State with the most expensive house prices. You follow the rules, engage a solicitor or conveyancer, obtain a mortgage and transfer perhaps hundreds of thousands of dollars through a property settlement system you have every reason to believe is safe. Then criminals get inside the communications surrounding the purchase.
Fraudsters have compromised the lawyer or conveyancer's email, monitored to get the property settlement details and at precisely the right moment, they use AI invoice-swapping software to insert fraudulent bank details into what appears to be the real email of your solicitor. The buyer follows what looks like an authentic instruction and sends their deposit or settlement money to a criminal-controlled mule bank account.
In minutes, a family's life savings can disappear. Many victims lose their property and their deposit. Others borrow money from friends and family and end up further in debt. The banks often capitalise the scammed loss into the mortgage and charge interest on the whole thing.
Banks blame lawyers/conveyancers ... Australian Financial Complaints Authority blames the victim ... Real estate agents keep collecting personal data ... criminals keep winning
When that happens, homebuyers discover there's no such thing as 'safe as houses' in NSW, where solicitors and banks both have licence to blame the homebuyer for falling victim to a crime they have little to no ability to foresee. The bank will blame the customer who authorised the payment. The lawyer will say it wasn't their system that was compromised. Police might investigate the crime but cannot necessarily recover the money when the mule bank account has been created through a fake identity takeover. Meanwhile, the mortgage and interest remains payable.
Then there is the lawyer's professional indemnity insurer, Lawcover. It is owned by the Law Society of NSW, who also says lawyers don't have to show a defrauded customer their IT and email systems were protected.
NSW solicitors are generally required to obtain their compulsory professional indemnity insurance through Lawcover, which operates within the institutional structure of the NSW legal profession. For a devastated homebuyer seeking compensation, this can create an extraordinary imbalance: the consumer has suffered a life-changing loss, but the institutions with the information, insurance and resources needed to establish what went wrong largely control what happens next.
That matters particularly in payment-misdirection fraud. Determining responsibility may require extensive forensic examination of the solicitor's email environment, access logs, cybersecurity controls, warnings and communications. A homebuyer usually has access to none of that evidence. The solicitor and insurer do. So does the bank. Yet no-one helps the homebuyer
SVA submits that this inquiry should look beyond pricing to the human and systemic cost of an unaccountable monopoly, and offers to provide further confidential case material to assist the Committee.
Scam victim-survivors are trapped in an impossible liability circle. The bank blames the customer. The lawyer points to the criminal. The insurer disputes liability. State police are under-funded and the Australian Federal Police simply run a reporting system tracking what happened, but never chasing the money trail. The victim-survivor homebuyer is left carrying all the financial consequences, along with the shame of being scammed and blamed.
These property misdirection fraud cases raise a larger public-policy question. NSW requires property transactions to operate within a highly regulated electronic conveyancing system, and earns substantial tax revenue from property transactions. Yet when organised criminals exploit weaknesses around that system, who is ultimately responsible for making an innocent homebuyer whole? Certainly not Lawcover.
For the NSW homebuyers who we support after their life-changing fraud loss, their trust in Government and banks is forever broken. They did what Australians are encouraged to do: saved, borrowed and bought a home. Then criminals stole the money intended for their home purchase and no-one accepts any responsibility for the loss.
With only one company allowed to sell insurance to lawyers in NSW, and it being owned by the same group that's supposed to watch over lawyers (the Law Society of NSW), there's no effective insurance to protect citizens from a highly destructive economic crime they can rarely recover from financially or emotionally.
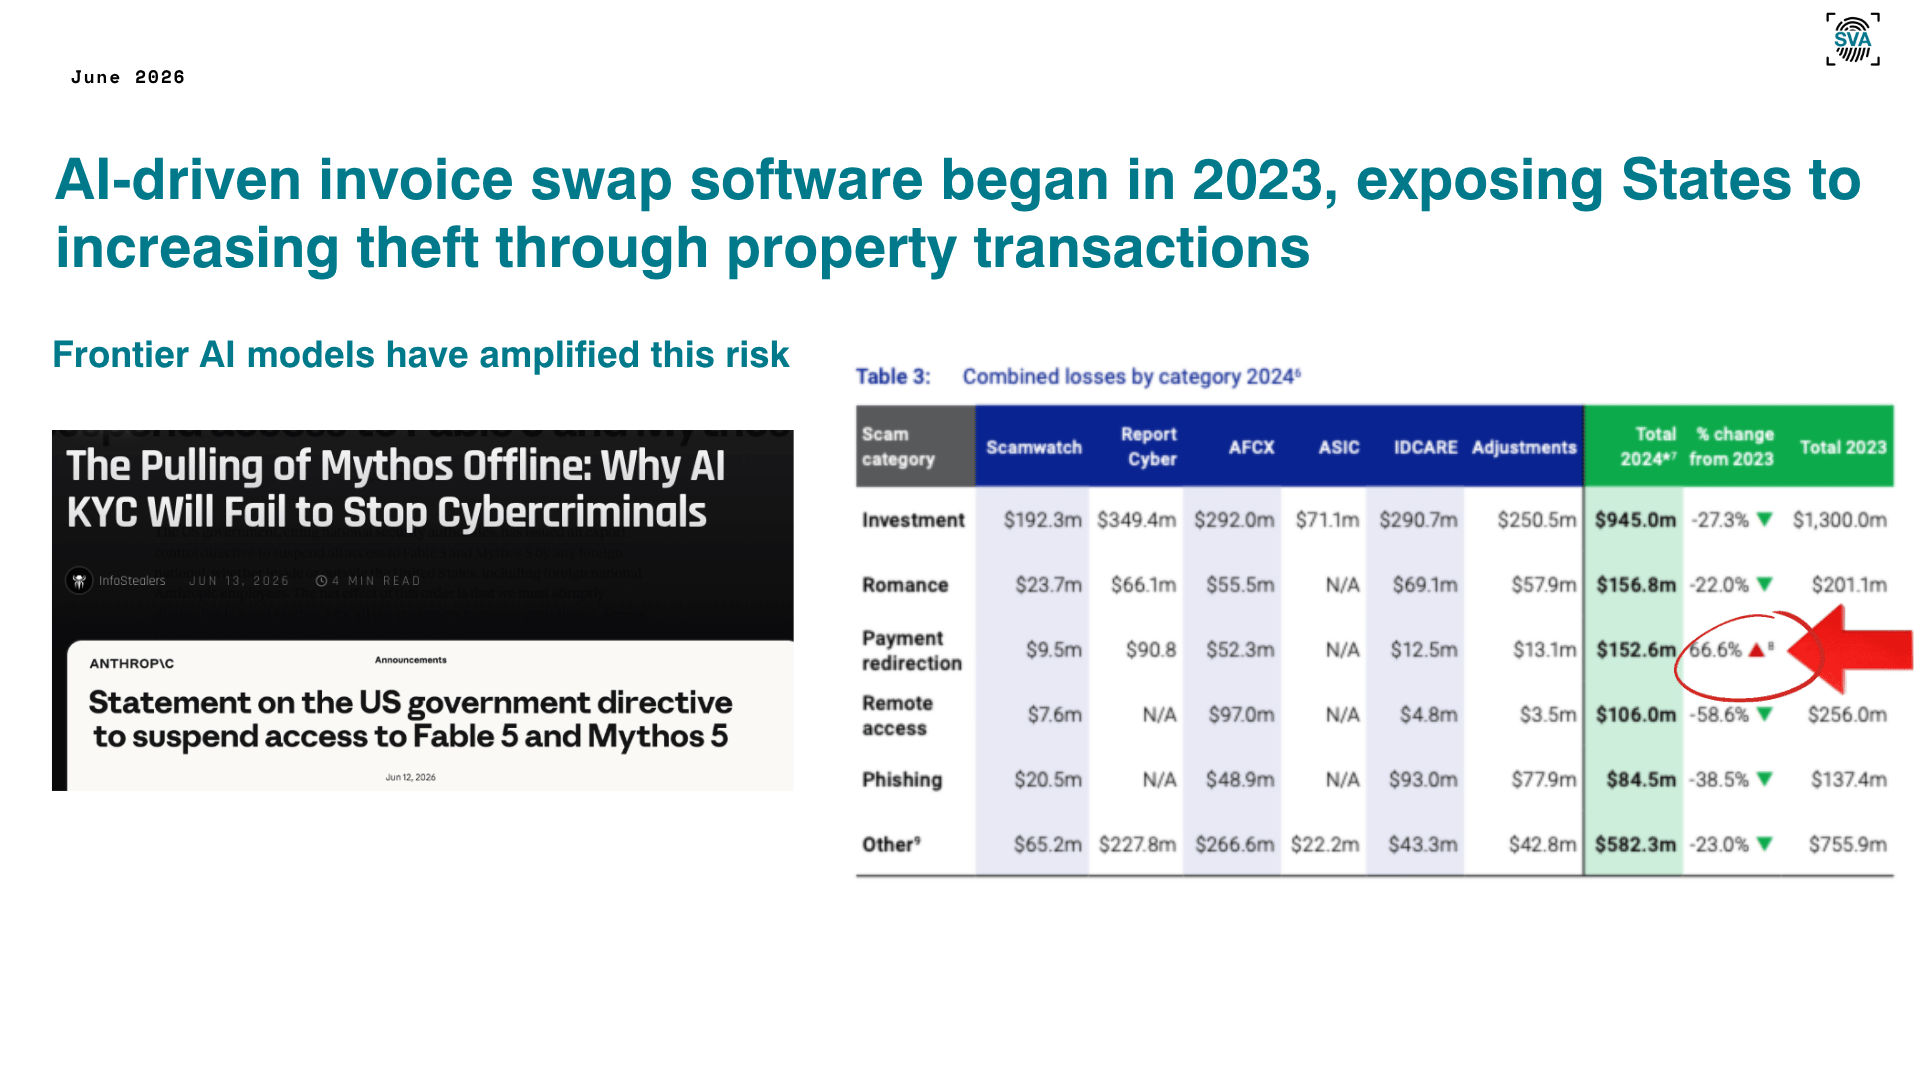
2. How Lawcover's insurance monopoly has added to the harm of property misdirection scams for NSW homebuyers
When people buy a house in NSW, the Government forces them to transact electronically through PEXA or Sympli. NSW Fair Trading has acted to try to fix this problem. A Property Payment Redirection Scams Roundtable was held in April 2026 and a national working group is addressing the issue.
Ultimately, Lawcover, like banks, is one of the parties with the power to award reimbursement and demand forensic interrogation of the lawyer's IT systems. However, because Lawcover and the Law Society of NSW are also the same body deciding whether to pay victims back, it's not a fair fight.
Lawcover increasingly threatens victim-survivors with the insurer's costs if they pursue recovery through civil litigation, effectively doubling the financial risk of a homebuyer going down this pathway.
[Image: "NSW Fair Trading is acting but we need Lawcover reform." Photo of the Property Payment Redirection Scams Roundtable, 24 April 2026, alongside the NSW Fair Trading summary document.]
The federal government's new Scams Prevention Framework [4] is designed to protect people from scams. But this exact kind of scam, stealing house-settlement money, isn't covered by those new rules because email is exempt. So even the newest protection doesn't catch this hole.
Meanwhile, the criminals who got away with the money continue to scale their harms, and we see new mortgage fraud typologies emerging all the time.
For many of our victims, the police investigate and find the mule bank account used in the scam wasn't even a real, registered account, so nobody could be charged. No investigation. No court case. The victim loses the money AND nobody goes to jail. This happened to Will and Jess, who bought their first home in Camden back in 2023, and can't afford to move into their home.
Lawcover passes the blame around, nobody is properly checking the forensic evidence, and victims are left with no real place to go for help. Our organisation first raised the complex harms of property settlement fraud with NSW Fair Trading in 2025 and was pleased that Fair Trading Commissioner Natasha Mann escalated it as an issue of national significance. Our charity has assisted a number of NSW and interstate families who lost their life savings, home deposits or settlement funds to property payment redirection fraud, and then subsequently tried to seek recovery or justice from the solicitor's professional indemnity insurer, Lawcover.
This submission goes to paragraphs (a) and (d) of the Terms of Reference: the impact of the current settings resulting in an effective monopoly provider, and other related matters. We ask the Committee to look beyond pricing and into what the Lawcover monopoly, and its ownership by the Law Society of NSW, means in practice for a growing class of consumers: homebuyers and sellers whose settlement funds are stolen through banking mortgage fraud, solicitor email compromise and payment redirection scams.
In August 2026, AUSTRAC [5] uncovered co-ordinated mortgage fraud across 10 Australian banks, with professional facilitation from brokers, accountants and conveyancing professionals referenced in other media articles [6].
3. Homebuyers are being widely dudded, and not just because NSW has the most expensive property market in Australia
Property payment redirection scams are not a fringe problem. The National Anti-Scam Centre recorded $166.8 million in payment redirection scam losses in 2025, up 9.3% on 2024, placing this category among Australia's five highest-loss scam types. Total reported scam losses in Australia reached $2.18 billion in 2025, a 7.8% increase on the year before.
Property-related fraud losses are lucrative, which is why they are a target. New PEXA research [7] reveals homebuyers in 2026 are less confident that they can spot a scam than in 2025. Self-rated confidence fell from 51 per cent in 2025 to just 41 per cent in 2026, despite years of scam-awareness campaigns. Increasingly sophisticated techniques such as AI voice cloning are making the traditional advice to simply "spot the scam" much harder to follow.
When buyers and intending buyers were shown a mock scam email, one in three said they would transfer money to the fraudulent account. Relying on consumers to detect increasingly convincing fraud is not an effective safety system, but neither is the existing courts, law enforcement or Australian Financial Complaints Authority system.
Almost nine in ten Australians rate buying property as one of life's most stressful experiences. Stress, urgency, unfamiliar processes and enormous financial transfers converge at precisely the moment consumers are expected to detect tiny anomalies in otherwise convincing communications. The evidence points to a fundamental problem with placing primary responsibility on the buyer: the more sophisticated scams become, the less realistic it is to expect an anxious homebuyer to serve as the final fraud-detection system protecting hundreds of thousands of dollars. Lawcover has already proven it will join in to deny accountability in these complex crimes.
Case after case follows the same pattern: threat actors gain access to a solicitor's or conveyancer's email thread, waiting to see the property contract details before sending the buyer a fraudulent instruction with 'updated' bank details that looks identical to genuine correspondence.
In each of these matters, and in others our organisation is aware of, the homebuyer or seller followed the process their solicitor told them to follow, using the same email thread they had used throughout the transaction.
4. Lawcover's dual role creates a structural conflict of interest that leaves victims with nowhere to go
Because Lawcover is the near-universal insurer for solicitors in this State, and is wholly owned by the Law Society of NSW, the same body responsible for regulating the profession, a defrauded homebuyer faces a single gatekeeper who is simultaneously the insurer assessing the claim, financially interested in denying it, and structurally connected to the regulator meant to hold the profession to account. There is no competing insurer to approach, and no independent forensic body a claimant can turn to for a second opinion. The NSW Conveyancers Institute runs a similar monopoly and also denies claimants.
In the matters our organisation has reviewed, Lawcover investigates using its own or the law practice's chosen IT contractor, concludes there was 'no evidence' of email compromise, denies liability, and threatens the claimant with an adverse costs order if they do not withdraw. Correspondence sent by Lawcover states plainly that Lawcover 'sympathise[s] for the loss suffered by them due to the fraudulent conduct of a third party', while maintaining that 'it is not appropriate to look to the law practice for recovery in relation to that loss', before warning that Lawcover and the law practice 'may... rely on this letter on the question of costs in any proceedings, including costs payable on an indemnity basis.'
A defrauded homebuyer, already out of pocket by tens or hundreds of thousands of dollars, is placed in the position of having to accept the word of the very body with a financial incentive to deny the claim, or risk a costs order if they press on. This is not a level playing field, and it is a direct consequence of the lack of competition and independence the Committee has been asked to examine.
A recurring feature of these disputes is that Lawcover's forensic denials are not independently testable by the claimant. They use a firm called Zirilio, which our forensic experts have examined and described as a 'fig leaf' covering up the sources of the email breaches, which are wide and varied.
In one matter, correspondence records that no DKIM (DomainKeys Identified Mail) authentication signature was present on the relevant messages at all, meaning there was no cryptographic basis on which anyone could rule compromise in or out, yet a firm conclusion of 'no compromise' was still communicated to the claimant and used to deny the claim. In another set of matters, doctored bank documents used to facilitate the fraud were found, on close inspection, to contain 'hidden text': invisible, embedded transaction data lifted from an entirely unrelated customer's real banking history and pasted beneath the misdirected payment instructions. There was also evidence of previous frauds involving other NSW law firms.
Where the same insurer that is assessing liability for an email-compromise claim also selects or instructs the forensic examiner, controls what is disclosed to the claimant, and holds an effective monopoly over the market the claimant must deal with, there is no independent check on the reliability of 'no evidence of compromise' findings. Competitive reform that introduces genuinely independent insurers along with independent forensic verification standards would materially improve outcomes for consumers.
Solicitors' professional indemnity insurance is usually discussed as a question of professional risk management. For the families our organisation has assisted, it has determined whether they ever see their stolen deposit or settlement funds again. A monopoly insurer, owned by the regulator, investigating itself and denying claims under threat of costs, is not a system that can be trusted to deliver fair outcomes for the growing number of Australians targeted by property payment redirection fraud. Financial and economic crime is a growing problem all over the world. In the UK, property misdirection fraud is mandatorily reimbursed within a month [8]. In Australia, there is no mandatory reimbursement. We urge the Committee to treat the consumer harm set out in this submission as central to its inquiry, and we would welcome the opportunity to provide further case material, including the underlying correspondence referred to above, on a confidential basis if that would assist the Committee.
References
[1] "INTERPOL Report Warns of Increasingly Sophisticated Global Financial Fraud Threat." Accessed 20 June 2026. https://www.interpol.int/News-and-Events/News/2026/INTERPOL-report-warns-of-increasingly-sophisticated-global-financial-fraud-threat
[2] "Scam Victim Alliance Winners 2026." The MAIAs – Money Awareness & Inclusion Awards. Accessed 19 June 2026. https://www.maiawards.org/winners-2026/
[3] United Nations Office on Drugs and Crime (2025). Survivor-informed action brief on combating fraud. https://www.unodc.org/res/organized-crime/GFS/publications/UNODC_Survivor-informed_action_brief_on_combating_fraud.pdf
[4] "Scams Prevention Framework Codes and Rules Exposure Draft." Treasury Consult Hub. Accessed 9 September 2026. https://consult.treasury.gov.au/c2026-765133
[5] "Fintel Alliance Uncovers Coordinated Mortgage Fraud across Major Lenders." AUSTRAC. Accessed 7 September 2026. https://www.austrac.gov.au/news-and-media/media-release/fintel-alliance-uncovers-coordinated-mortgage-fraud-across-major-lenders
[6] Blair Jackson, "$4bn Issue Overwhelming Aussie Banks." Yahoo Finance, 29 June 2026. https://au.finance.yahoo.com/news/4bn-issue-overwhelming-aussie-banks-051418191.html
[7] PEXA Australia, "Property Settlement Scam Awareness, Behaviours and Attitudes in Australia, 2026." Accessed 7 September 2026. https://www.pexa.com.au/content-hub/settlement-scams-index/
[8] "APP Fraud Reimbursement Protections." Payment Systems Regulator (UK). Accessed 9 September 2026. https://www.psr.org.uk/information-for-consumers/app-fraud-reimbursement-protections/
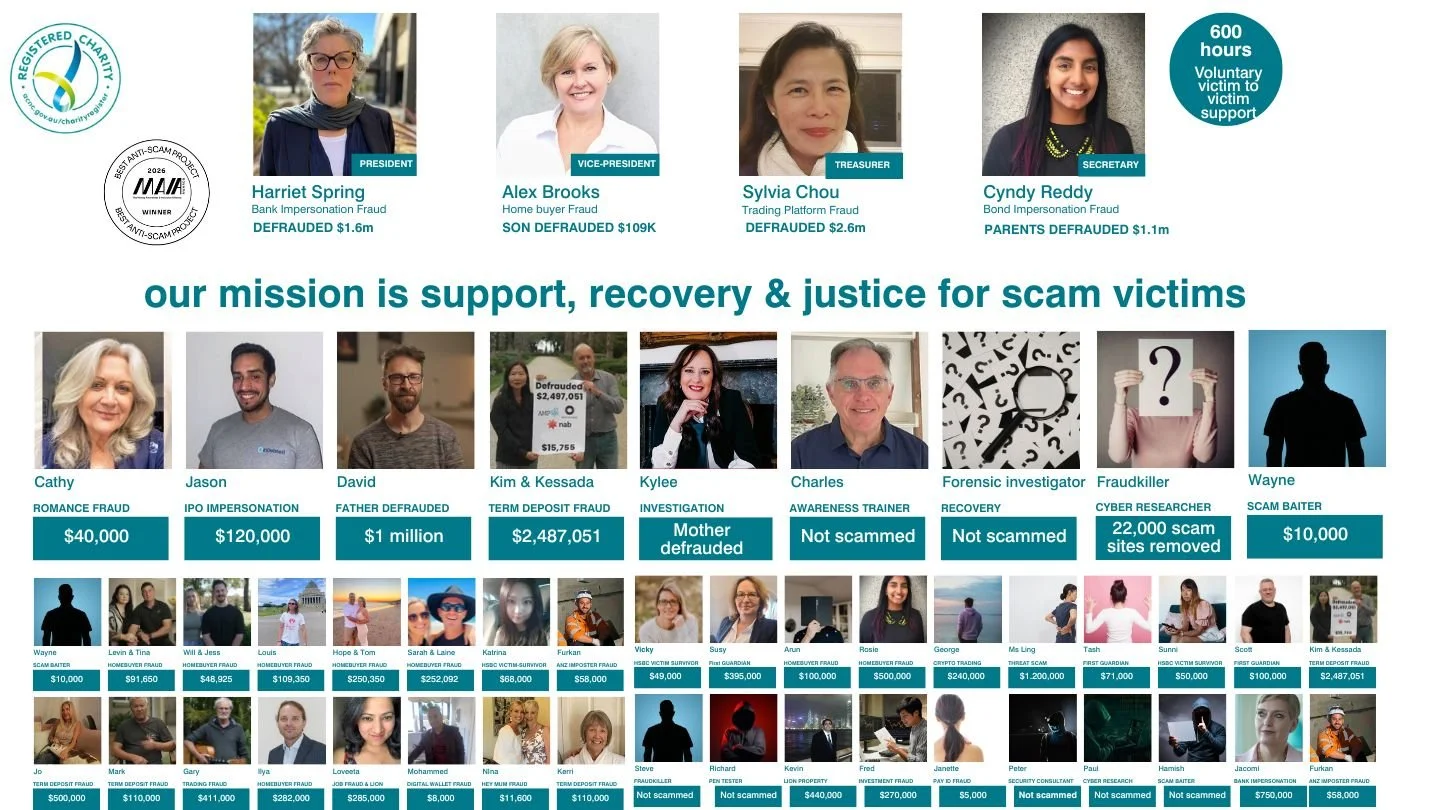
AFCA must Reopen HSBC Scam Cases Following Historic Federal Court Findings
The Federal Court's landmark $35 million fine and findings against HSBC cast doubt on whether scam victims received fair outcomes through AFCA. Scam Victim Alliance is calling for affected cases to be reopened so victims can receive the full compensation they should have received in the first place.
The Federal Court's findings and $35m fine against HSBC raise broader questions about whether Australia's external dispute resolution system can deliver timely and fair support and compensation for scam victims whose losses resulted from systemic failures in Australia's banking system. Scam Victim Alliance is calling on AFCA to oversee affected cases and ensure that the under-compensation and victim-blaming .
ASIC Chair Sarah Court has promised timely reimbursement to HSBC victims after the historic case.
Scam Victim Alliance (SVA) is calling for all HSBC scam victim cases that were denied, under-compensated, or settled through AFCA’s traumatic dispute resolution processes to be urgently reopened following the Federal Court's landmark findings against HSBC Bank Australia.
On 18 June 2026, the Federal Court ordered HSBC to pay $35 million in penalties after finding widespread failures in fraud prevention, customer investigations and account restoration processes.
The Court found that HSBC failed to have adequate systems to prevent and detect unauthorised transactions, failed to comply with ePayments Code requirements in 97% of cases, and failed to properly advise customers how to regain access to their accounts after restrictions were imposed.
Scam Victim Alliance believes these findings fundamentally call into question the fairness of previous AFCA outcomes and published determinations for many victims who sought redress through the Australian Financial Complaints Authority (AFCA).
Many victims endured lengthy and traumatic complaint processes while attempting to recover money lost through criminal mule and money laundering activity.
SVA has serious concerns that some victims felt pressured by AFCA to accept low settlement offers and confidentiality agreements simply to obtain partial reimbursement when they were desperate to reclaim their life savings.
We are specifically supporting seven victims to seek timely redress for their under-reimbursement, namely:
Mr L – December 2023 loss: $330,000. AFCA compensation 1049413 & 1066263: $257,850.
Ms K – October 2024 loss: $50,000. AFCA compensation 1069438: $10,000.
Mr and Mrs W – January 2024 loss: $95,000. AFCA compensation 1076903: $75,000.
Ms Q – April 2023 loss: £32,900. AFCA compensation 12-25-252337 and 971494 and 1274358: $9,500.
Mr B – November 2023 loss: $49,000. AFCA compensation 12-00-1048367: $45,000.
Mr C – November 2023 loss: $24,371. AFCA compensation: $5,000.
Mr and Mrs R – July 2023 loss: $47,808. AFCA compensation 12-00-10657766: $38,850
The Federal Court findings raise questions about the barriers Australian scam victims face, particularly being forced to be told their losses were their own responsibility when the Court has now established that HSBC's failures were widespread and systemic.
Scam Victim Alliance is calling for:
All HSBC scam victims who did not receive 100% reimbursement or interest on their losses to be reopened and compensated through AFCA;
A moratorium on relying upon previous AFCA determinations and/or deeds for “full and final settlement” involving HSBC scam complaints;
A regulatory review of AFCA’s harmful and traumatic dispute resolution processes for scam victims, already in shock and financial distress after being victims of crime and systemic weaknesses in our banking system;
A review of failed detection of systemic issues when similar scam typologies involving criminal exploitation of Australian financial payments systems go unreimbursed;
The publication of all data showing how many HSBC spoofing and scam victims accepted confidential settlements and the shortfall of each settlement compared to the loss;
An independent examination of whether AFCA processes compounded victim harm with a view to working towards how AFCA can move towards a trauma-informed external dispute resolution process in line with the United Nations Office on Drugs and Crime survivor-informed action brief on combatting fraud.
AFCA to examine making each HSBC victim truly financial ‘whole’ after the court findings, including non-financial compensation and lost interest; Immediate reforms to AFCA’s scam dispute resolution processes to ensure victims are not forced through prolonged and re-traumatising dispute resolution processes given the ongoing delays in the Scam Prevention Framework rollout.
The Court accepted that HSBC had known for years that fraud risks against its customers were increasing, that there had been a lack of investment in fraud controls, and that additional controls were available to better protect customers.
It also recognised that customers suffered both financial and non-financial harm.
Scam Victim Alliance says this case exposes a broader national problem.
“Scam victims are harmed three times: first by organised criminals, then by corporate and institutional failures, and finally by exhausting civil dispute resolution processes at AFCA or in the civil legal system that force them to repeatedly relive their trauma,” said Scam Victim Alliance president Harriet Spring.
"The HSBC case exposes a disturbing truth: institutions can know where the risks are within their own systems, yet still force consumers to absorb the harm. It simply has to stop. All people victimised by criminal scams deserve the corporations who failed them to compensate,” she said.
“Australian scam victims denied fair outcomes at AFCA deserve another chance after these court orders. Justice must extend to every victim left behind by AFCA and Australia’s poor justice process for those fleeced by criminal scammers."
Consumers should not bear the cost of delayed investments in fraud detection while money mules and money laundering proliferates in our banking system.
As Assistant Treasurer Dr Daniel Mulino proposes delaying implementation of the Scams Prevention Framework beyond its initial start date of 2025, stronger scam protections cannot wait until 2027.
Every delay creates more victims and exposes more Australians to criminals fleecing them while corporations and AFCA push the blame and cost on to consumers.
ABOUT SCAM VICTIM ALLIANCE
For more information Harriet Spring - President harriet@scamvictimalliance.org.au; Alex Brooks - Vice President alex@scamvictimalliance.org.au. Sylvia Chou - Treasurer sylvia@scamvictimalliance.org.au
Scam Victim Alliance is an ACNC-registered community of volunteer scam victim survivors and their loved ones offering support to victims needing support, recovery and justice after being scammed. We are the proud winners of the 2026 best anti-scam project in the Money Awareness and Inclusion Awards.
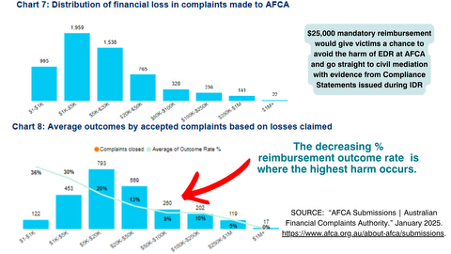
SOURCE: AFCA submission on the SPF in 2024
While the bulk of scam losses are at the lower end of the financial scale, AFCA’s own submission to the Scam Prevention Framework codes reveals that the higher the loss, the less chance there is of reimbursement
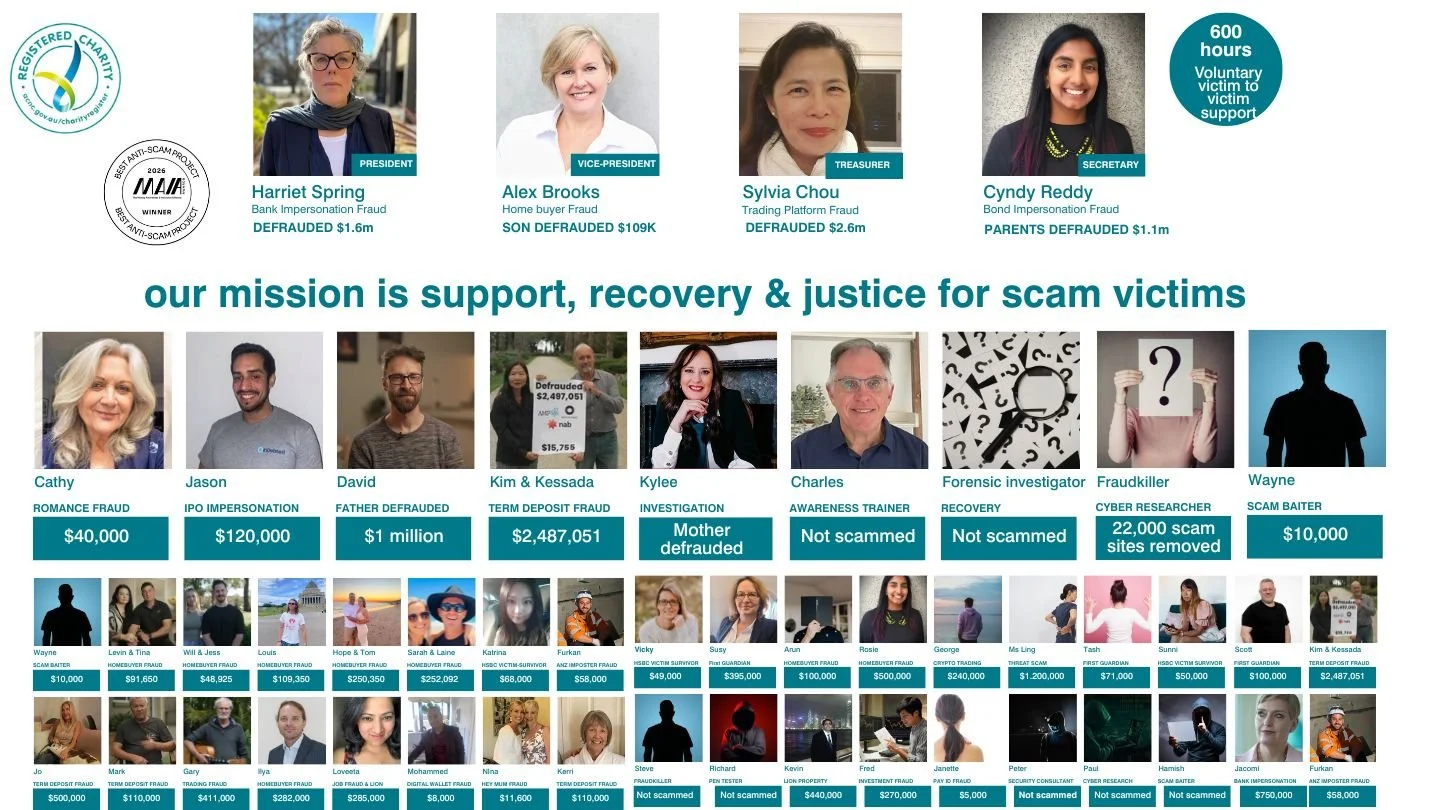
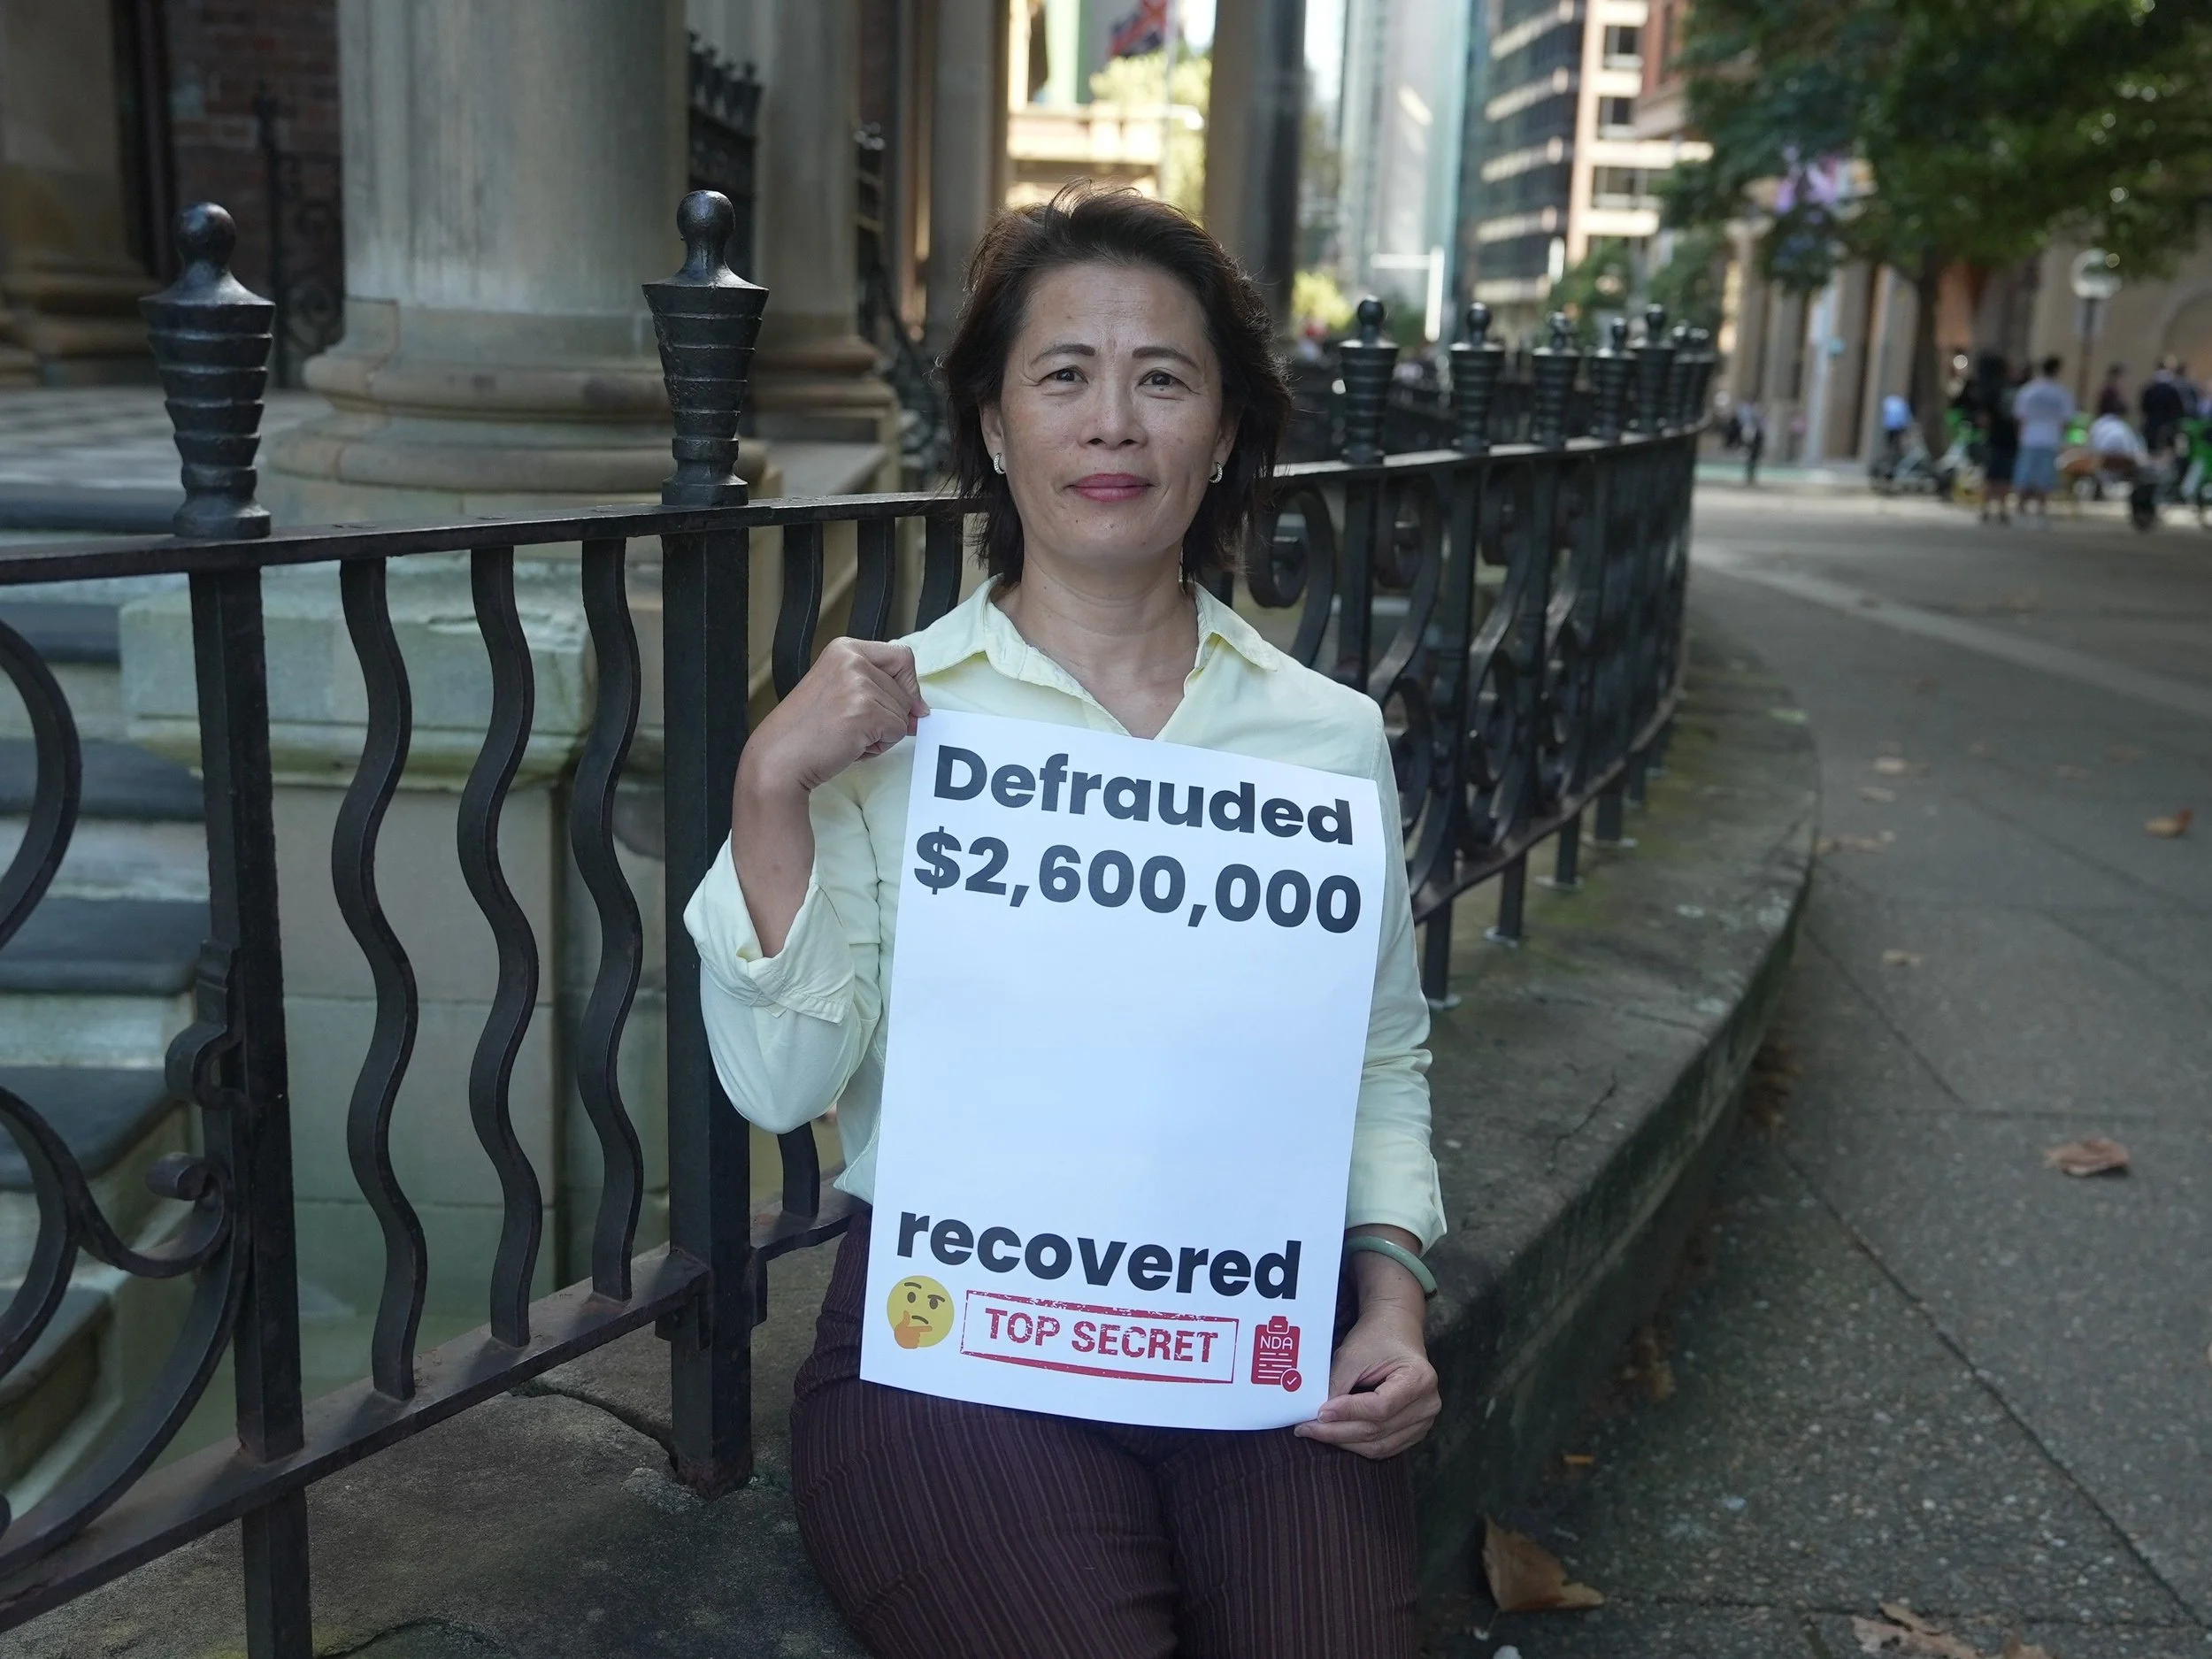
Scam prevention codes must save Australians from harm & trauma
Scam Victim Alliance has a new submission to the Treasury’s latest consultation on the Scam Prevention Framework. Our submission argues that scams are driven by organised criminal networks that exploit regulatory loopholes and fragmented corporate responsibility. Building on our earlier recommendations—including $25,000 mandatory reimbursement, stronger scam intelligence, improved consumer education, and a Royal Commission into financial crime—it focuses on three priorities: preventing delays that allow criminals to exploit loopholes (particularly in email, online marketplaces and crypto ATMs), improving support for victims navigating Australia's complaints system, and adopting a "safe systems" approach that targets the underlying infrastructure of organised scam networks rather than treating scams as isolated incidents.
Australia's scam crisis is a failure of systems, with Governments caught unaware as to how fast, complex and industrialised fraud crime is. This submission explains how organised crime exploits gaps in regulation, why current responses are making the problem worse, and what Government, Treasury and industry could do to stop the harm from financial crime ruining people’s lives.
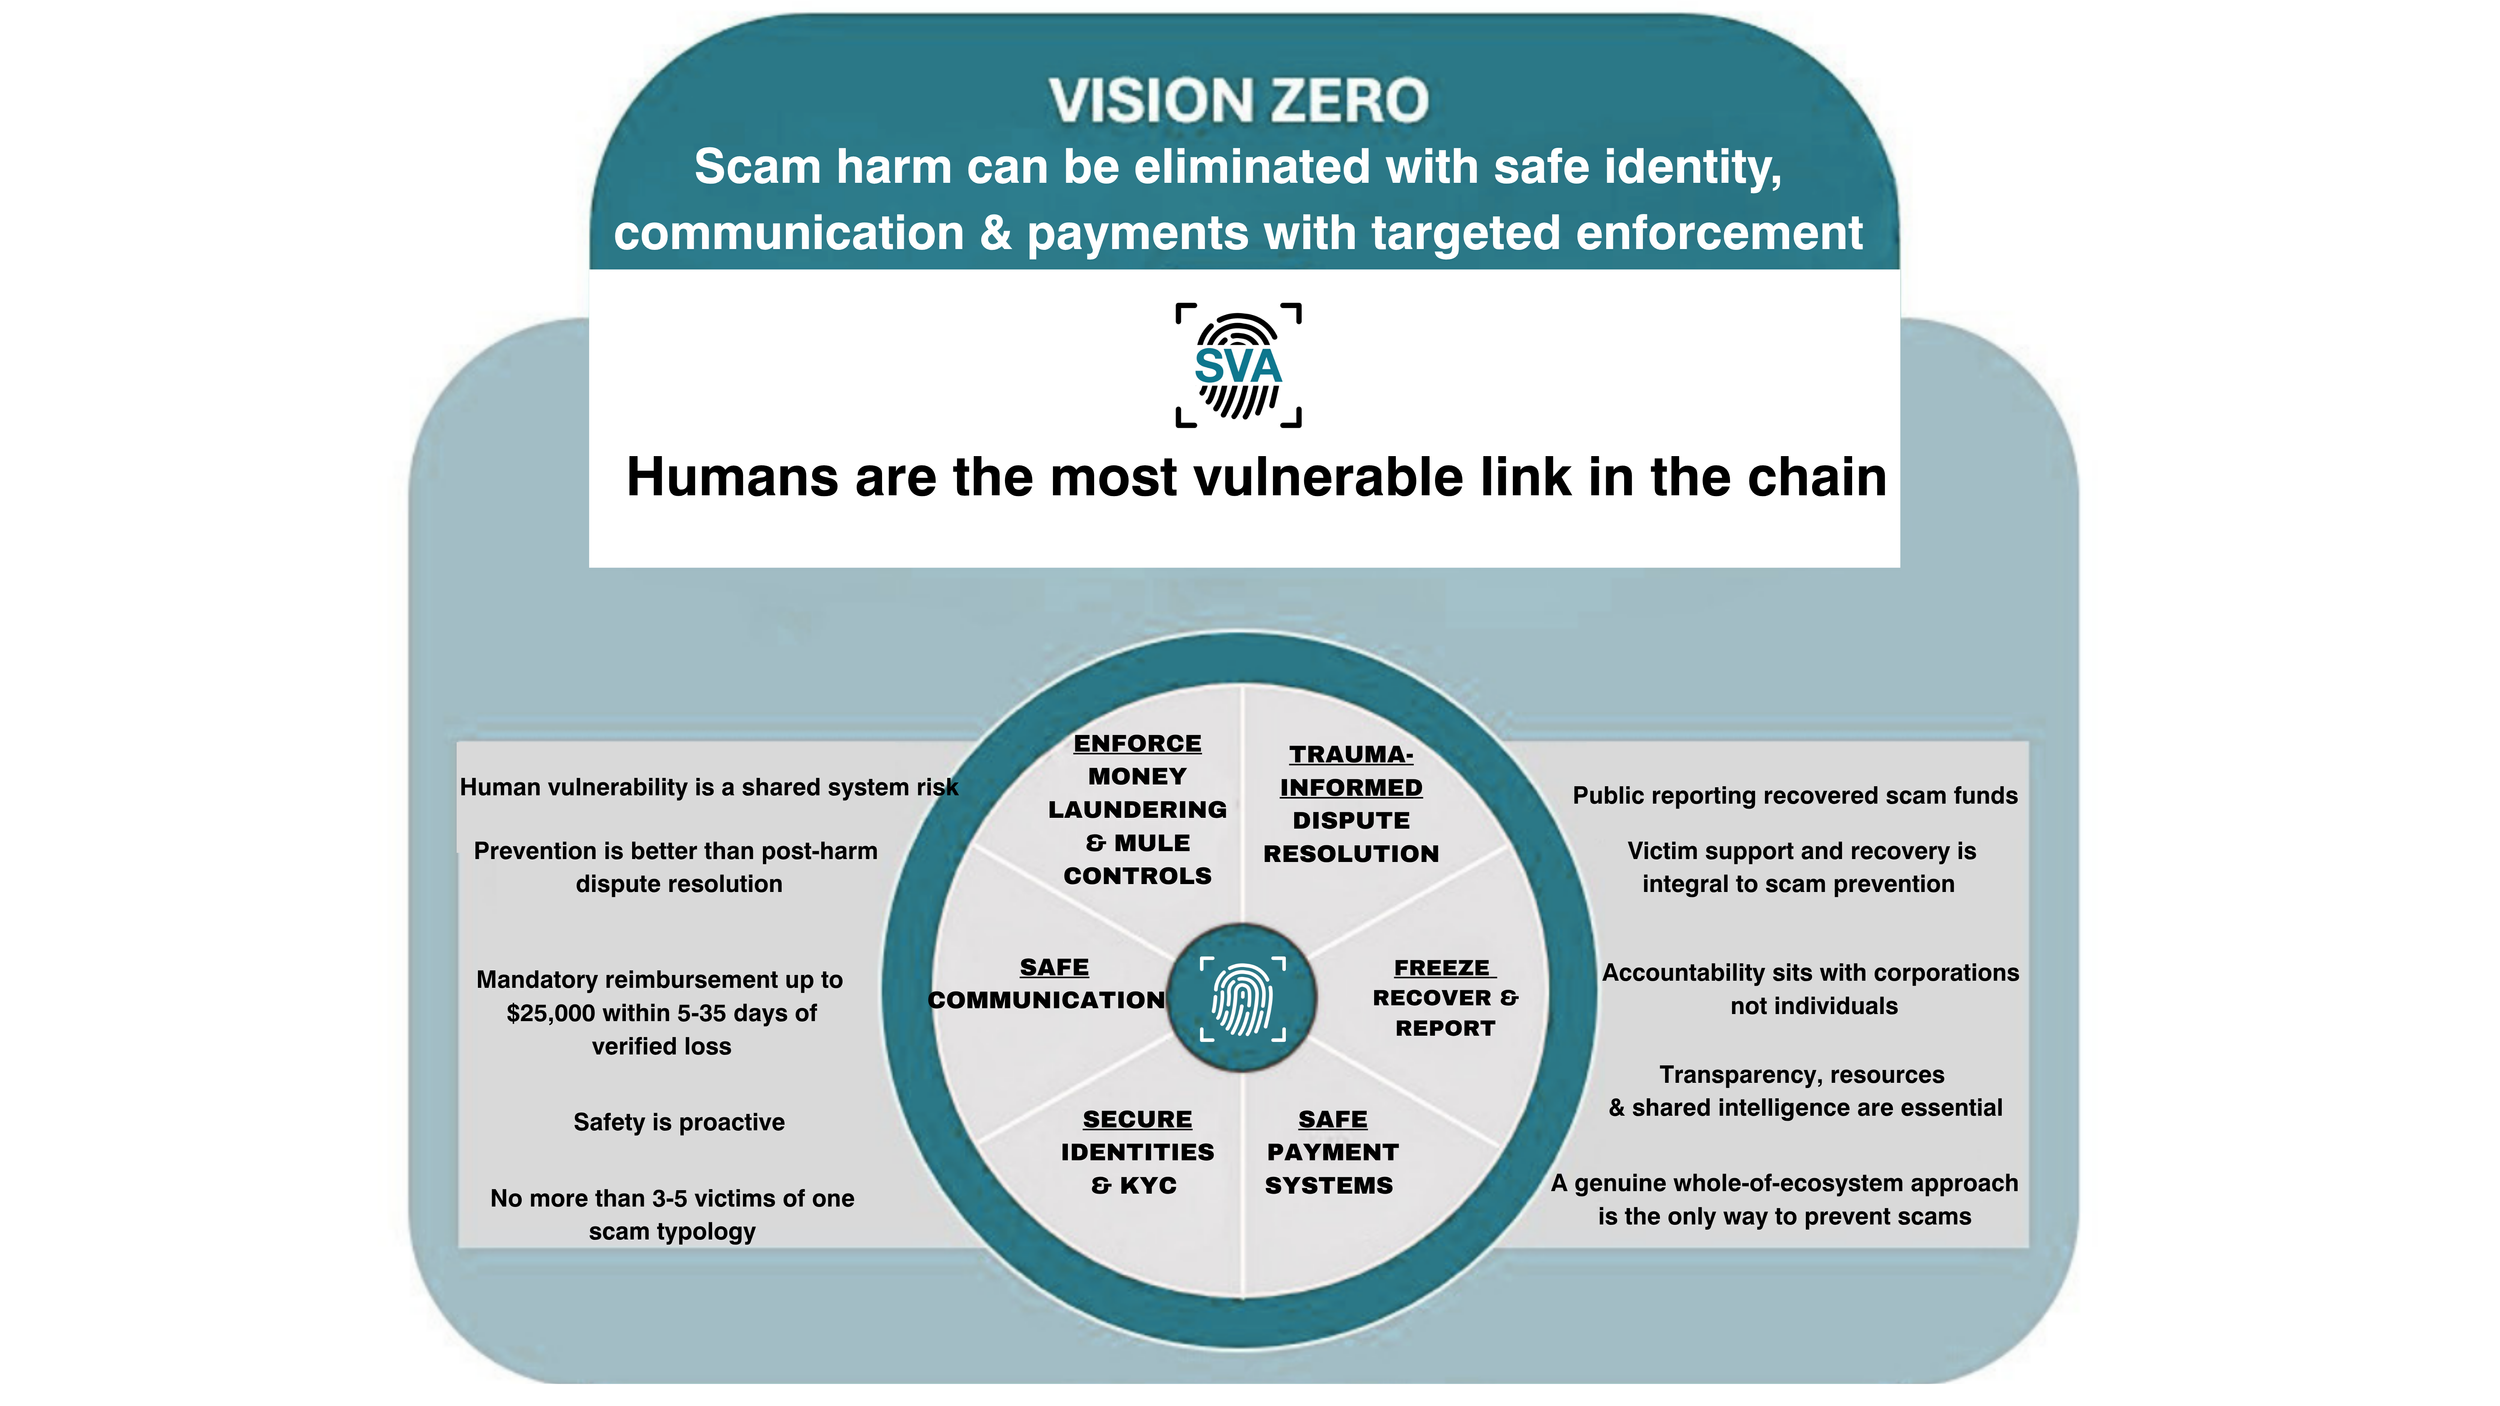
Executive summary
We are Australia's only self-funded, volunteer-led community, working directly to support victims through the complex harms global organised crime networks are wreaking on everyday citizens who trust their governments and banks to protect them.
We walk side-by-side with victim-survivors to deal with the overwhelming horror of financial crime, traumatic dispute resolution processes and broken enforcement systems in Australia.
Our ACNC-registered charity won the Best Anti-Scam Project of 2026 in the Money Awareness and Inclusion Awards. We helped consult with the United Nations Office on Drugs and Crime to develop the survivor-informed action brief to tackle fraud, which we implore the Government to implement.
We welcome the June 2026 Scam Prevention Framework (SPF) consultation, which rightfully shifts criminal responsibility onto corporations to prevent scams.
No country is untouched by the harm of scams, money laundering and illicit capital. Fraudsters, and corporate insiders typically scheme with other networked actors to specialise in finding the “legal loopholes” to commit deceptive fraud - please read Appendix H to understand the mechanics.
We stand by our January 2026 Scam Prevention Code submission, which included the following recommendations to protect Australians from the grave financial and psychological harm of scams:
1. All entities in scam chains must be designated and follow prescribed fraud controls, with instant reimbursement up to $25,000 for re-used scam infrastructure.
2. Scam education improvement with a hotline and Scam Infrastructure League Table publishing clear Scamwatch reported warnings to centralise and harmonise the system.
3. Regulators and law enforcement must detect scam infrastructure using regulatory and law enforcement subpoenas, compiling anonymised data for publication and transparency. Actionable Scam Intelligence is urgent and must begin immediately.
4. Mandatory IDR reimbursement up to $25,000 for verified scam losses paid within 5-35 days.
5. All designated sectors must have clear reimbursement, freezing and takedown obligations backed by infringement powers for recovery and be fined within 30 days of a breach.
6. A Royal Commission into financial crime with 6-year common law protections to apply to receiving banks.
This new submission to the SPF Treasury consultation focuses on 3 chief concerns:
SECTION 1 Delays in making the SPF operational risks the regulations and codes becoming a “scam proliferation playbook”, where schemers will develop more sophisticated scams - specifically exploiting gaps in failing to designate online marketplaces. crypto ATMs and email scams
SECTION 2 More funding is needed for victim support through horrific Australian Financial Complaints Authority (AFCA) External Dispute Resolution (EDR) processes, particularly given the court orders made in the ASIC v HSBC case.
SECTION 3 A ‘safe systems’ approach is needed to solve the scam crisis, with transparent investigative resources dedicated to scam typologies replicated across more than 3-5 cases - high value scam syndicate activity must go beyond ‘investment’ and ‘romance’ typologies to truly protect Australians.
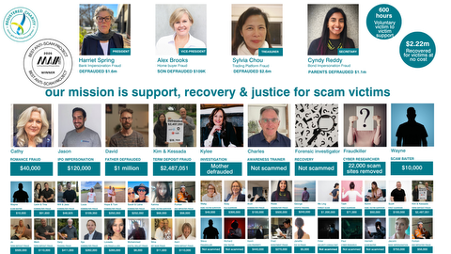
Our community are all volunteers following our ACNC charter to support victims at no cost to victims experiencing the highest harm.
SECTION ONE: The SPF risks becoming a scam proliferation formula as criminals exploit loopholes
AUSTRALIANS EXPECT GOVERNMENT TO PROTECT CITIZENS FROM CRIME, NOT EXPOSE THEM TO BLAME & VICTIMISATION
Scam and fraud victims get more support from the government and law enforcement after being punched and robbed on the street than they do losing hundreds of thousands of dollars to elaborate deceptions and fraud perpetrated through banks or online and telco communication channels.
We applaud the SPF’s attempts to tie ‘controls’ to reimbursement but it is simply unacceptable that the “whole ecosystem approach” will no longer cover the top contact method for scams - email. Crypto ATMs are increasingly used only for scamming and we believe an immediate ban on these is required. Banks are increasingly debanking mules to protect themselves as the SPF begins, but there is an urgent need for humane intervention of exploited and gaslit mules such as the woman outlined in Appendix B of this submission. The danger of job and romance scams morphing into harmful threat scams means online marketplaces must also be captured by designations to prevent harm.
We acknowledge the SPF’s mention of impersonation controls and urge the Treasury to specify this more clearly. We are seeing phone calls impersonating trusted authorities morphing into dangerous threat scams as criminal networks pretend to be from the Australian Federal Police, ASIC or the
“A BANK THAT OPENS AN ACCOUNT WHERE MONEY IS BEING TRANSFERRED BY A FRAUDSTER IS AN ACCOMPLICE TO FRAUD. IT IS NOT A QUESTION OF WHETHER OR NOT A BANK CAN RECOVER THE MONEY … IT IS A QUESTION OF WHETHER OF NOT A BANK IS PERMITTING A FRAUD TO TAKE PLACE BY NOT KNOWING WHO THEIR CUSTOMER REALLY IS.” - the former head of Royal Bank of Scotland Sir Peter Burt[5]
Australian Tax Office and coerce people into giving up valuable personal information and payments. One victim was under the control of the scammer for 21 days, sharing intimate details of her location - including when she was going to the toilet. Her bank, Westpac, now charges interest on her scammed loss of more than $840,000.
Close the AI Scam Gap: Consumer vulnerability should be anticipated as criminal networks weaponise AI agents, data theft and frontier AI models
The emergence of frontier models and AI agents creates new risks for Australians under the Scams Prevention Framework. As AI systems increasingly search, recommend and execute actions on behalf of consumers, scammers will manipulate those systems through false signals, coordinated disinformation and impersonation. Consumers are the weakest link in this chain of harm. The SPF should explicitly require banks to assess AI-mediated scam risks - particularly impersonation - and implement safeguards while committing to share intelligence across sectors. AI platform designations should be considered now as a matter of urgency, along with designating crypto, email and online marketplaces, where harm is already entrenched.
SECTION 1: Key recommendations:
A “whole of ecosystem” approach to the SPF is nonsense if email is not designated. The key information on email vectors that needs to be part of compliance statements include:
Device, location and personal data on who created the email account used in any part of a scam
The email header information behind emails misdirecting payments
Which platform - Gmail, Microsoft and Yahoo are commonly used - allowed the scam email to be sent
How the email breach likely occurred (this is currently very difficult due to multiple vectors of breaches and insider threats)
If any other domain is behind the email, e.g. travel.io, then who registered the domain
A signed compliance statement from the financial firm, other professionals (e.g. lawyers) stating there were no data breaches or insider threats.
Online marketplaces have high harm from scam syndicate activity tricking people into complex payment scams or using their online searches as ‘lead’ vectors to target people for other threat, job or relationship frauds. The type of information that needs to be on compliance statements from these frauds includes:
Who created the social profile - the email and mobile number and location data associated with it
The external URL links used to trick or deceive a consumer
The bank/payment account tied to any payment offers or advertising accounts
Crypto ATMs need to be banned, given their proliferation in Australia. Victims using these machines deserve to be counselled through humane interventions that help them understand how muling works. These gaslit mules pose a difficult challenge that will require corporations debanking them to resource appropriately and safely as part of the SPF.
SECTION TWO: Delays until 2027 expose Australians to more trauma, blame and theft
AFCA EDR PROCESSES TRAUMATISE VICTIMS - REFORM IS URGENT
The delays to hearing cases relating to the SPF until March 2027 are unacceptable.
The uncontested June 18 Federal Court case ASIC v HSBC demonstrated banks do not lack knowledge of their broken scam controls but will delay redress and force consumers to absorb the consequences. A bank’s highest legal obligation is to protect their shareholders, not uphold consumer laws.
Furthermore, the way AFCA amplified and escalated the harm upon HSBC victims seeking help from the ombudsman requires an urgent Government review. AFCA forced HSBC scam victims to sign “shut up and go away” goodwill payments which have now put victims in a complex position if they signed restrictive deeds to receive less than 100% reimbursement. Scam Victim Alliance calls on AFCA to reopen HSBC cases with the new evidence heard in the federal court and issue public determinations on each case for transparency.
AFCA created extensive delays for HSBC victims before its “Mr T” determination was passed 13 months after the victim’s initial scam. Even with the win of this determination, other HSBC victims whose scam operated in slightly different ways - which is common amonst all scam typologies - were shamed for “releasing more than one OTP” to their scammers and therefore denied justice and fairness.
HSBC’s pattern of denying scam liability and shifting the blame to other vectors has been replicated by other banks, including ANZ who also had SMS spoofing scams that resulted in severe losses to their customers. ANZ even allowed their customers to be robbed by mules on ANZ platforms, and AFCA’s determination still blamed the victim while claiming Australian law forces the ombudsman to make these determinations.
THE SCAM DOESN'T HAPPEN JUST ONCE. IT HAPPENS OVER AND OVER AGAIN. FIRST, MULES STEAL YOUR MONEY. THEN YOUR BANK OR SUPER FIRM TELLS YOU IT’S NOT THEIR RESPONSIBILITY. THEN YOU ARE PUSHED INTO A LONG, EXHAUSTING AFCA PROCESS THAT TAKES MONTHS OR EVEN YEARS. NO-ONE FULLY EXPLAINS HOW TO BEST ARGUE YOUR CASE.- Taylor, 43, scammed of $420,000 superannuation in a complex ASIC-registered managed investment collapse.
Scam Victim Alliance contends that AFCA has been misinterpreting the existing protections against fraud in Australian legislation because it doesn’t have case managers with the skill needed to pursue the full reaches of its fairness jurisdiction.
Furthermore, when AFCA seeks external counsel to get legal advice on complex situations like scams, many corporate legal firms are also incentivised to insist to AFCA that existing fraud protections under legislation and common law are unclear, as their firms make money from providing more complex advice. It is Scam Victim Alliance’s belief that existing laws protect against mules and money laundering, but the Government and regulatory timidity has prevented this happening.
AFCA’s dogged insistence that Australia required law reform before it could do better for scam victims is not strictly true. Our experience of supporting victims through the AFCA process is that the ombudsman service regularly:
Forces complainants to negotiate against themselves.
Fails to explain the legal concepts at play in the complaint until the very end of negotiations, when AFCA case workers commonly bully and intimidate complainants into accepting lowball offers “because that’s all they will get”.
Doesn’t demand corporations share required information for complainants (particularly with CCTV footage), refusing to identify whether AUSTRAC suspicious matter reports or systemic issues have been escalated as part of the case.
Victims must have overwhelming evidence of financial firm failures to win their scam case at AFCA. Read the raft of different victim experiences at AFCA on Product Review to see the reality of everyday citizens’ experiences with the financial ombudsman.
Resolves scam complaints that total up to $2.6 million over a range of transactions, but not a single scam loss involving $1.2 million in one transaction.
Refuses to use its ability to waive interest on scam losses, forcing victims to be exploited by their banks for profit in complex cases.
AFCA is increasingly claiming it doesn’t have “jurisdiction” so it can get out of having to deal with complex scam cases, with new complaints being ruled out before they go to case management (where there are lengthy delays).
Many of our victim community report their case managers refusing to embrace the complexity of their case. Victims from non-English speaking backgrounds not only cannot understand the process but can rarely find the words to challenge the case manager’s limited understanding. This is why information transparency is so important.
AFCA case managers betray the organisation’s own fairness jurisdiction by refusing to see connected scam typologies and treating them consistently. The following three cases all involved in-branch handling of email payment misdirection of property settlements, yet had extreme differences in AFCA determinations:
Mr and Mrs C Panel Determination- reimbursed 70%.
Mr F Panel Determination - reimbursed 70% but not the $1800 a month interest NAB charged on the scammed loss.
Mr & Mrs D Non-Panel Determination - reimbursed $0 and has now had to spend $110,000 taking civil legal action.
In cases (a) and (b), there was an extra connection with ‘hidden text’ in the payment instructions revealing a Commonwealth Bank customer was unwittingly or knowingly part of the networked scam infrastructure - the fact that AFCA treats each case in isolation rather than a systemic failure requiring complainant compensation demands urgent review. Not all AFCA cases reach determination, particularly if the bank agrees to settle - in these cases, like in Levin Salaberry’s homebuyer email fraud - the bank will reach a confidential settlement and force the complainant to sign a restrictive deed. AFCA endorses this approach.
It is up to the Australian Government to demonstrate stronger leadership than simply accepting AFCA’s poor interpretation of existing common law, legislative and code protections against fraud. Delays to the SPF have put citizens and taxpayers in harm’s way.
We know that regulatory reform is challenging, but the SPF was supposed to be in place by the first quarter of 2025. It is ludicrous that ‘industry consultation’ has forced more losses on consumers during the last two years. In the case where the regulator ASIC took rare action against HSBC after overwhelming evidence the bank forced hundreds of consumers to take the blame for broken systems.
We urge the Australian Government to re-examine the successful elements of the United Kingdom’s mandatory reimbursement scheme, which would have most high-harm cases reimbursed within 2 weeks of a financial crime upending their lives. This will not only prevent consumer harm but also cost the industry less over time, by keeping disputes out of AFCA.
POOR REIMBURSEMENT OUTCOMES AT AFCA PUT AUSTRALIANS IN HARM’S WAY
“WHEN I WAS SCAMMED IN 2012, I GOT ALL MY MONEY BACK. WHEN I WAS SCAMMED IN A JOB SCAM, I RECEIVED ONLY $6,000 NON-FINANCIAL COMPENSATION FROM AFCA. WHEN RECOVERY COMPANY PAYBACK CONTACTED ME, I PAID THEM BECAUSE I DID NOT REALISE IT WAS A SCAM. I COULD NOT BELIEVE HOW BADLY AFCA’S FAILED PROCESSES PUT ME AT RISK OF THESE PREDATORS.” - Vaishali, 42, lost $25,000 to a recruitment scam and $3500 to Payback.
Scam Victim Alliance ally, psychologist Caroline Micallef (see Appendix C) notes that individuals and the Australian taxpayer unwittingly bears the cost of scam harm, which doesn’t show up as a direct cost measured by Scamwatch statistics:
“In the last six years I have seen clients who are experiencing trauma from financial scamming. This is a new cohort of clients who, when they first discover they have been scammed, the psychological response is acute and overwhelming. Some immediate reactions can be physical illness, breathlessness, a sense their world has collapsed and can represent the onset of what often becomes a prolonged psychological crisis.
Not only have they lost money but sometimes the most important relationship in their life (romance scams, their savings, their creditworthiness, and sense of self worth. Victims often find themselves cut off from family and friends. The feeling of shame can be so pervasive it prevents victims seeking assistance and can persist for years after the financial loss.
The psychological effects extend well after the incident. There can be lasting anxiety and difficulty trusting others. Another response is grief, for loss of money, their savings, their credit rating and most of all, self worth. Without timely intervention, victims are likely to develop greater symptoms and difficulties that add to the burden on mental health services, homeless services, acute medical services and community welfare supports.
”
Fraud and scams are A national economic security problem
The highest harm scam victims are those facing losses greater than the current proposed mandatory reimbursement of $3,000. Victims with higher losses undeniably face more complex scam typologies (with 11-15 different networked elements exploiting loopholes). Many Australian victims are unwittingly placed at risk of recovery scams due to the complexity and barriers of AFCA’s limitations.
The complexity and holes in coverage of the SPF risks baking in the existing inequity and information asymmetry, which is causing untold personal, financial and mental anguish to Australian consumers.
Scam Victim Alliance Treasurer Sylvia Chou, who lost $2.6 million in a complex scam that started with a Facebook ad and ended with banks profiting from her misery, was sectioned in a mental health facility. The greatest mental distress came during dispute resolution at AFCA, when she expected an ombudsman to see the crimes that had been perpetrated against her. The threat of bankruptcy also meant she would not be able to earn an income as an accountant.
Most victims of high-loss scams face a long journey and legal battle, believing the initial scam is where the harm lies. It is only 3-6 months after their scam that victims realise they are in a constant state of anxiety and panic that is wearing them down mentally and emotionally. They hold out hope that AFCA’s dispute resolution can help them, only to realise very quickly that AFCA’s horrific processes blame and shame them for authorising their loss. We see this is the time when suicidal ideation and self-harm becomes a common experience in our victim community.
SOURCE: AFCA submission on the SPF in 2024
While the bulk of scam losses are at the lower end of the financial scale, mandatory reimbursement at $25,000 with full access to compliance statement evidence would protect victims from post-scam trauma harm.
Without considered pathways to de-escalate scams and fraud, Australia’s fragmented post-victimisation journey will continue to destroy savings, livelihoods and people’s trust in government and corporations.
If digital communication ecosystems continue being weaponised against citizens, this economic threat will quickly distort into a national security threat, too, where certain groups become radicalised forever.
“YOU JUST WANTED SOMEONE TO SAY SORRY FOR WHAT HAPPENED, BUT NOBODY DOES - THEY JUST BLAME YOU FOR AUTHORISING THE WHOLE STUPID THING.” - Frank, 72, a South Australian cancer survivor, lost $175,000 in a fraudulent property investment after moving his retirement savings due to concerns about “Trump’s war”. ASIC added the company to its Moneysmart Investor Alert List just four weeks after the scam
A mandatory reimbursement threshold of $25,000 will reduce costs for regulated entities over time by preventing thousands of low-value disputes from escalating into lengthy AFCA External Dispute Resolution (EDR) processes, which could cost multiple entities high determination fees.
We believe mandatory $25,000 reimbursement can help de-escalate the harm experienced by high-loss victims, as well as give them a starting point to decide whether to take their complex fight to civil courts and mediators, who may be better placed to deal with the situation.Mandatory reimbursement creates a stronger incentive for banks, telecommunications providers and digital platforms to invest in prevention, detection and disruption measures, as preventing scams becomes cheaper than managing disputes after harm occurs. It also reduces complaint volumes, administrative costs and reputational damage. A $25,000 threshold recognises that rapid intervention is more efficient than prolonged litigation-style processes. The UK experience shows that mandatory reimbursement is a stronger protective factor than having none at all.
Scam prevention should prioritise restoring consumers quickly and directing industry resources toward systemic risk reduction rather than costly post-harm disputes.
SECTION 2 SVA key recommendations:
Recognise the complex PTSD and harm scam victims in Australia face, and resource early intervention to stop the taxpayer bearing complex costs of scamming.
Reconsider delays to SPF and revisit the need to publish and share information with victims as part of a “safe systems” approach to resolving the scam crisis.
Harmonising and centralising scam prevention and investigation capabilities so victims can call one phone number to identify or report a scam (with language and translation for Mandarin, Arabic and Vietnamese language groups).
Ensure that mandatory reimbursement is re-examined to save greater costs and horrific delays by going through the AFCA process. We would be particularly keen to see a UK-style mandatory reimbursement scheme with a minimum $25,000 limit.
Understand that prompt and swift reimbursement avoids harm and will save Governments, corporations and taxpayers money over the long-term.
Consider funding complex AFCA cases with a “support fee” that corporations must pay in addition to other AFCA fees if case resolution takes more than 12 weeks at EDR.
SECTION THREE: Financial harm for high-loss victims is real and urgent
ASIC V HSBC HAS SET STANDARDS TO START OBLIGATIONS SOONER
The new consultation claims consumers are given IDR from 30 June 2026 and EDR from 1 January 2027, but there is no corresponding right for consumers to see or compare regulated entities' compliance performance before this time.
We contend the ASIC v HSBC Federal Court case demonstrates that some proposed SPF obligations may indeed have already moved beyond matters suitable for consultation.
We contend that the Federal Court case with HSBC may have created legal precedent necessary for stronger corporate controls to protect consumers. The Federal Court identified deficiencies in prevention, detection, investigation, remediation, governance and consumer restoration processes. The SPF should therefore distinguish between areas requiring innovation and those requiring mandatory baseline standards. “Reasonable steps” and principles-based flexibility cannot substitute for controls whose absence has already been judicially recognised as causing systemic consumer harm.
Comparing the Scam Prevention Framework with the Federal Court's findings in ASIC v HSBC
Flexible, principles-based obligations
Current SPF proposal
Flexible, principles-based obligations.
Federal Court finding
Some fraud controls are already objectively necessary.
Treasury could now examine
Introduce enforceable minimum standards before March 2027.
Scam intelligence sharing
Current SPF proposal
Better scam intelligence sharing, although Actionable Scam Intelligence is not yet clearly defined.
Federal Court finding
Financial institutions already possessed significant scam intelligence.
Treasury could now examine
Introduce mandatory reimbursement of up to $25,000 to create stronger incentives for industry prevention.
Industry capability
Current SPF proposal
Build industry capability over time.
Federal Court finding
Institutions had known about scam risks for years but failed to act transparently.
Treasury could now examine
Determine whether the real problem is a lack of intelligence—or a lack of enforcement.
Non-financial harm
Current SPF proposal
No recognition of non-financial harm.
Federal Court finding
The Court recognised non-financial harm in the Amended Joint Submissions on Liability and Relief:
"In the absence of those Key Controls, customers were at greater risk of suffering both financial loss and non-financial harm. Some customers did suffer those harms."
Treasury could now examine
Recognise human vulnerability as a system risk and introduce enforceable compensation for non-financial harm.
"Reasonable steps"
Current SPF proposal
Future-oriented regulation based on "reasonable steps".
Federal Court finding
Many minimum expectations have already been established by the Court.
Treasury could now examine
Create clear, transparent and enforceable obligations without requiring victims to pursue lengthy AFCA disputes.
Safe disruption powers
Current SPF proposal
Safe disruption powers.
Federal Court finding
Disruption itself can create consumer harm if poorly managed.
Treasury could now examine
Review and reform AFCA so dispute resolution no longer compounds victim harm.
The court’s orders to HSBC should now set the baseline for mandatory industry obligations, including AFCA’s oversight of previously determined cases. This is particularly important given the initial Government promises to roll out the SPF from the beginning of 2025. It is clear that delays have added to consumer harm and economic insecurity. HSBC victims are living, walking proof that this has occurred.
THE DISGUSTIFYING TRUTH OF BEING A SCAM VICTIM IN AUSTRALIA
One member of our community coined the word "disgustifying" to describe the moment she discovered the truth of how her bank, online social media and government failed to protect her. After draining her superannuation and making repeated payments through her bank to help her online partner "Alven" escape Syria, she learned that every dollar stolen had been funnelled through Australian banking money mules into what she now believes was accounts likely controlled by Africa’s ‘Yahoo Boys’ and scam networks. She had been tricked into taking out low-doc loans, which compounded her loss. The money she believed was saving the life of the online partner she had sent intimate photos to was instead helping fund what Interpol has described as a “global crisis” of human trafficking and other harms.
The SPF places significant obligation on industry but minimal new obligation on the Government to fund the investigative infrastructure required to pursue organised scam syndicates exploiting and weaponising Australian banking and communication infrastructure against citizens.
We believe there cannot be more delays in actionable scam intelligence and we need more regulatory capability to publish data around things like:
● Known mule bank accounts reported to Scamwatch, the Australian Financial Crimes Exchange, the Global Signal Exchange and state and federal law enforcement (this should be done regularly to help gauge how dangerous the banking system is for scams,
● Known spoofed telephone numbers used in previous frauds investigated by ASIC,
● Known accounts flagged to AUSTRAC through SMR and TTR reports that are associated with other known scam typologies.
We would also contend that part of the harm to victims is not adequately measuring scam losses or how effective warnings and education campaigns are. We would also ask the Federal Government to find a better way to measure the taxpayer impost of looking after scam victims after losing life-changing amounts of money.
Investment scams, superannuation fraud and the high-loss scams our victim community experiences do result in individual losses exceeding $100,000 and sometimes reaching more than $2,000,000. We have one particularly egregious case of a $6,000,000 scam.. These are more than opportunistic crimes - they involve scripted social engineering campaigns, professional money laundering networks and offshore coordination which evade the skill and capability of Australian regulators and law enforcement.
Home purchase fraud must also be recognised as a priority category. Property transactions in Australia routinely exceed $500,000 — in major metropolitan areas, frequently $1 million or more. Conveyancing scams, where criminals intercept communications between buyers, solicitors and conveyancers to redirect settlement funds, represent some of the largest single-victim losses in the scam ecosystem.
A first home buyer losing their deposit or settlement funds is not merely suffering financial harm. They are potentially losing decades of savings in a single transaction, with no prospect of recovery under the current framework and no realistic path to any meaningful redress.
These criminal attacks specifically target the conveyancing and legal sector, a largely unregulated scam surface under the current SPF. Email compromise at the point of settlement is a known, documented attack vector that has destroyed families financially and should be treated with the same investigative priority as superannuation fraud. Treating any of these crimes with the same resources allocated to a $500 parcel scam is problematic.
SECTION 3: SVA key recommendations:
SVA recommends the establishment of dedicated, properly resourced investigation units, with specific mandates covering:
● Large-loss investment fraud (individual losses exceeding $25,000);
● Superannuation scam syndicates;
● Home purchase and conveyancing fraud involving settlement fund diversion and laundering through gold, foreign currency and cash;
● Cryptocurrency-linked laundering networks connected to scam proceeds.
These investigation units should have direct access to AFCA complaint data, Report Cyber, ACCC Scamwatch reports and ASIC intelligence — with legal authority to act on cross-referenced leads without requiring victims to re-report through separate channels. It should report on recovered funds and make sure these are not put into general proceeds of crime pools, but dedicated to advancing protection and investigation of scams.
We would like to see Scamwatch offer a centralised service and co-ordinated phone line that gives victims realtime information on what is a known scam.
We believe a ‘safe systems’ approach is urgently needed - see Appendix E - How safe systems can help.
We believe Scamwatch needs to report the recovered scam money as well as scammed losses. Singapore now does this. Currently, Australian banks have no accountability to show those funds have truly disappeared and simply lie to AFCA and get away with it.
We know that JPC3 is working in cooperation with the AFCX and there have been successful intelligence sharing that now stops money leaving Australian shores - so why aren’t banks recovering more funds for scam victims? How can the Australian Government make the chain of custody more accountable to scam victims who simply cannot believe the lies they are told after they’ve fallen victim to criminals exploiting gaps in our systems.
Mandatory reimbursement leads to Scam Resilience: stronger together
The UK's 2026 Annual Fraud Report demonstrates why Australia's Scams Prevention Framework (SPF) must be built around systemic prevention and fund recovery with mandatory reimbursement rather than a slow and steady approach to ‘reasonable steps’.
Fraud is both an industrialised crime and a national security threat. In 2025, the UK recorded a record 4.06 million fraud cases, an 11 per cent increase on the previous year, with £1.28 billion stolen from consumers and businesses. On average, eight UK people were defrauded every minute and almost £2,500 was stolen every minute. Yet banks simultaneously prevented £1.68 billion in unauthorised fraud, stopping 70 pence of every £1 of attempted theft. In Australia, our banks will brag about their investment in anti-fraud measures while simultaneously blaming victims for authorising transactions into mule accounts hosted on their platforms.
The latest UK information shows the fastest growing scams are no longer traditional bank impersonation scams. Losses from investment scams reached a record £221.5 million, purchase scams £118.1 million, romance scams £39.2 million and advance fee scams £58.4 million. These scams overwhelmingly originate online, with 66 per cent of APP fraud beginning on digital platforms and a further 17 per cent via telecommunications channels.
The rise of elaborate deceptions around the globe demonstrates that criminals are increasingly exploiting artificial intelligence, impersonation, deep fakes, threats and social engineering rather than technical vulnerabilities. The SPF should therefore recognise that victims are not failing because they lack intelligence or awareness. Criminals are exploiting predictable human behaviours at industrial scale. Australia's response must move beyond consumer education towards enforceable, shared obligations across banks, telecommunications providers, digital platforms, dating applications, crypto platforms and emerging AI agents and a holistic supportive scam recovery pathway. We need law reform across the board to deal with fast-changing crime vectors.
ENDNOTES
1. “INTERPOL Report Warns of Increasingly Sophisticated Global Financial Fraud Threat.” Accessed June 20, 2026. https://www.interpol.int/News-and-Events/News/2026/INTERPOL-report-warns-of-increasingly-sophisticated-global-financial-fraud-threat.
2. “Scam Victim Alliance Winners 2026.” The MAIAs - Money Awareness & Inclusion Awards, n.d. Accessed June 19, 2026. https://www.maiawards.org/winners-2026/.
3. United Nations Office on Drugs and Crime. (2025). Survivor-informed action brief on combating fraud. United Nations. https://www.unodc.org/res/organized-crime/GFS/publications/UNODC_Survivor-informed_action_brief_on_combating_fraud.pdf
4. Scam Victim Alliance. “Scam Victim Alliance Urges 6 Changes to SPF Designations and Codes to Protect Australians.” Accessed June 21, 2026. https://scamvictimalliance.org.au/submissions-blog-updates/cash-mandate-submission-sva-d94mh.
5. “Cryptocurrency ATM Scams | AUSTRAC.” Accessed June 20, 2026. https://www.austrac.gov.au/general-public/cryptocurrency-atm-scams.
6. 7NEWS. “The Single Email That Cost an Australian Woman $732,000.” May 4, 2022. https://7news.com.au/business/property/wa-woman-loses-732000-to-property-scam-after-responding-to-fake-email-c-6674754.
7. Commonwealth of Australia Federal Court of. “ASIC v HSBC Bank Australia Limited.” Text. Federal Court of Australia, June 19, 2026. https://www.fedcourt.gov.au/services/access-to-files-and-transcripts/online-files/asic-v-hsbc.
8. Hussain, Ali. Pay out to Fraud Victims, Demands Ex Bank Chief. n.d. Accessed June 21, 2026. https://www.thetimes.com/business/companies-markets/article/pay-out-to-fraud-victims-demands-ex-bank-chief-qskv2rc55vv.
9. Scamwatch. “Scam Statistics.” Text. Australian Competition and Consumer Commission, April 8, 2026. Australia. https://www.scamwatch.gov.au/research-and-resources/scam-statistics.
10. “Determination For Case 12-00-1016692 · Customer Self-Service.” Accessed June 22, 2026. https://my.afca.org.au/searchpublisheddecisions/kb-article/?id=f9f8941f-7379-ef11-ac20-000d3a6acbb4.
11. “Determination For Case 12-24-130239 · Customer Self-Service.” Accessed June 22, 2026. https://my.afca.org.au/searchpublisheddecisions/kb-article/?id=ba8cf7fe-c58e-f011-b4cc-00224892c723.
12. “How AFCA Makes Decisions | Australian Financial Complaints Authority.” Accessed June 22, 2026. https://www.afca.org.au/what-to-expect/how-we-make-decisions.
13. ProductReview.Com.Au. “Australian Financial Complaints Authority (AFCA) Reviews.” June 14, 2026. https://www.productreview.com.au/listings/australian-financial-complaints-authority-afca.
14. “Determination For Case 12-00-1045764 · Customer Self-Service.” Accessed June 22, 2026. https://my.afca.org.au/searchpublisheddecisions/kb-article/?id=add1b211-8384-f011-b4cc-002248112dcc.
15. “Determination For Case 12-00-1061026 · Customer Self-Service.” Accessed June 22, 2026. https://my.afca.org.au/searchpublisheddecisions/kb-article/?id=8894dc11-27c4-f011-bbd3-7ced8da1919d.
16. “Determination For Case 12-00-1034883 · Customer Self-Service.” Accessed June 22, 2026. https://my.afca.org.au/searchpublisheddecisions/kb-article/?id=548b5513-5825-f011-8c4d-002248937998.
17. Content Renegade - Alex Brooks. Alex Brooks Asked MP Stephen Jones Financial Services Minister about Scams. 2024. 04:56. https://www.youtube.com/watch?v=2HZ9P36wg-A.
18. “One Year on: Impact of APP Reimbursement on Victims.” Accessed June 20, 2026. https://www.psr.org.uk/news-and-updates/latest-news/news/one-year-on-impact-of-app-reimbursement-on-victims/.
19. “Alert: Money Recovery Scam Using Fake Documents to Impersonate ASIC – Www.Payback-Recovery.Com.” News item. Accessed June 22, 2026. https://www.asic.gov.au/about-asic/news-centre/news-items/alert-money-recovery-scam-using-fake-documents-to-impersonate-asic-www-payback-recovery-com/
20. “Investor Alert List - Moneysmart.Gov.Au.” Accessed June 21, 2026. https://moneysmart.gov.au/check-and-report-scams/investor-alert-list#!impersonation-of-oakmere-capital-pty-ltd-oakmere-capital-com--4258
21. Australia, Commonwealth of Australia Federal Court of. “ASIC v HSBC Bank Australia Limited.” Text. Federal Court of Australia, June 19, 2026. https://www.fedcourt.gov.au/services/access-to-files-and-transcripts/online-files/asic-v-hsbc.
22. Duffin, Perry. “The Nigerian ‘Blood Cult’ Targeting Lonely Australians with Romance Scams.” Stuff, April 4, 2025. https://www.stuff.co.nz/world-news/360641133/nigerian-blood-cult-targeting-lonely-australians-romance-scams.
23. INTERPOL releases new information on globalization scam centres. Available at: https://www.interpol.int/en/News-and-Events/News/2025/INTERPOL-releases-new-information-on-globalization-of-scam-centres (Accessed: December 30, 2025).
24. UK Finance. “Annual Fraud Report 2026.” Accessed June 16, 2026. https://www.ukfinance.org.uk/policy-and-guidance/reports-and-publications/annual-fraud-report-2026.
25. “Are Technical Support Scams Getting More Advanced?” Accessed June 21, 2026. https://blog.gaborszathmari.me/are-technical-support-scams-getting-more-advanced/.
26. Scam Victim Alliance. “Deceived! An Investment Scam Nightmare for Sylvia Chou.” Accessed June 25, 2026. https://scamvictimalliance.org.au/victim-survivor-stories/scammed-silenced-and-still-fighting-sylvias-26m-battle-for-justice.
27. “Investor Alert List - Moneysmart.Gov.Au.” Accessed June 25, 2026. https://moneysmart.gov.au/check-and-report-scams/investor-alert-list#!gg-capital-group-limited-trading-as-bluelexus--1236 .

How the Compensation Scheme of Last Resort must protect superannuation from scams
Australian superannuation is being stolen by sophisticated schemes, and the financial system isn't built to protect it. Managed Investment Schemes are collapsing and leaving thousands of Australians without the superannuation they have spent a lifetime saving. Here’s what SVA suggests Treasury should do about it.
Your superannuation is a target for criminals and the Compensation Scheme of Last Resort (CSLR)is the only compensation mechanism currently available for those who lose a lifetime of savings from which they can never recover. This is Scam Victim Alliance’s submission to the Treasury Consultation on CSLR reforms.
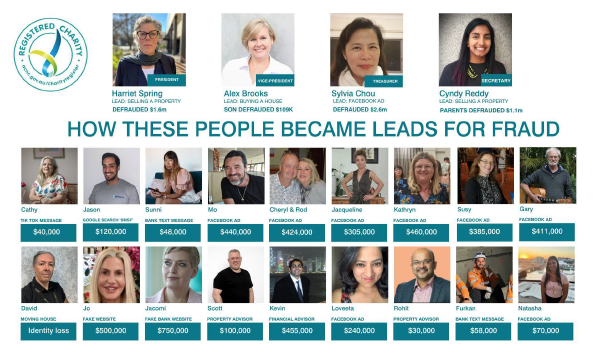
Executive summary
Scam Victim Alliance supports fraud victims through the trauma that follows life-changing loss. We support groups who experience lead generator harms which switched them into fraudulent self-managed superannuation schemes that ‘collapsed’ and were most likely designed as fraudulent schemes.
The Scam Victim Alliance (SVA) is a not-for-profit organisation representing Australians harmed by scams, cyber-enabled fraud and financial crime. Our members have lived experience of complex victimisation that begins with a financial loss and ends in years of complex legal fights and battles that retraumatise people and exacerbate the initial financial harm. We welcome the opportunity to submit lived experience feedback to Treasury's consultation paper, Enhancing member protections in the superannuation system.
[Image: SVA committee and members, showing losses from bank transfers, super rollovers and investment transfers ranging from $30,000 to $2.6 million]
Superannuation savings are being raided by criminally fraudulent networks.
Scams involving superannuation are not simply financial losses. They are life-altering events that leave Australians facing long-term financial insecurity, emotional trauma, damaged relationships and, in many cases, permanent reductions in retirement dignity and quality of life. We see dangerous vulnerabilities in Australia's identity, superannuation and banking system, with mule accounts, money laundering and criminal networks constantly exploiting opportunities to steal superannuation, tax refunds and other savings Australians may have. This submission argues that protecting Australians' retirement savings must now be understood as both a consumer protection issue and a national financial crime priority.
Harriet Spring, President, Scam Victim Alliance
Executive summary
For Australians, superannuation is not simply an investment. It is legislated and a necessary retirement safety net at a time when the government-funded Age Pension does not keep up with living expenses [1] and Aged Care [2] and Home Care [3] requirements are becoming increasingly expensive.
Public discussion and policy responses still focus overwhelmingly on First Guardian and Shield [4] losses rather than the systemic weaknesses that Treasury and regulators have had oversight of. This problem not only robs victims today, but also steals from future taxpayers, who will increasingly be required to stump up for shortfalls to manage an ageing population who have had their superannuation savings stolen.
Regulatory and law enforcement weaknesses mean that organised syndicates [5], cyber-enabled fraud networks [6] and increasingly sophisticated social engineering tactics [7] are targeting superannuation savings at an industrial scale. These attacks are not confined to retirees but increasingly target working-age people, too.
Younger Australians are increasingly being manipulated into fraudulent investments and relationship frauds, duped into high-risk superannuation switching arrangements, or compromised through linked digital identity breaches. The devastating financial losses mean these victims' superannuation will not "go far" and will further deplete Australia's ability to collectively look after its defrauded population.
The rapid growth of artificial intelligence (AI), impersonation technology and automated scam infrastructure means this threat is likely to accelerate significantly in coming years. Criminal networks are evolving faster than Australia's current consumer protection, anti-scam and superannuation governance frameworks. Our organisation has seen three growing categories of harm.
Harm 1: Unauthorised access to superannuation accounts. In these cases, criminals compromise linked systems such as identity documents, email accounts, mobile phone services or myGov credentials before targeting superannuation balances. Once control of these systems is obtained, scammers can intercept security codes, reset passwords and initiate fraudulent transactions or account changes. Some members of our community have unwittingly had their identities stolen after moving house, experiencing a data breach or being the victim of a previous scam. These members commonly experience fraudulent tax refund lodgements, superannuation rollovers or withdrawals, and the nightmare of having to put credit freezes in place to protect themselves.
Harm 2: Scam-induced withdrawals or super rollovers. Here victims are manipulated into voluntarily withdrawing their superannuation and transferring funds into fraudulent investment schemes. This happened in the First Guardian and Shield situation (10,000–12,000 victims), and also in the Australian Fiduciaries Limited [8] collapse (600 victims), the Lion Property Group [9] collapse (600 victims) and other unscrupulous schemes [10]. Fraudulent investment schemes are now architected with multiple ASIC-registered entities, poor (and likely deceitful) auditing practices, and poorly managed investment schemes, some registered and some not. The harm scales through several channels:
low-cost digital ads placed on social media and in traditional media ad networks like Taboola and Outbrain
lead generation activity used to get around cold-calling sanctions
investment opportunities marketed as legitimate and sophisticated
Harm 3: Traditional organised scam compound activity. Sometimes known as "pig butchering", romance scams and investment scams are now morphing into highly engineered attacks on Australians. These scams can also involve threats and impersonation of our most trusted authorities: police, regulators, banks and government authorities like Medicare. Some of our community members are being victimised in relationship frauds and coached into claiming releases from their superannuation for medical reasons. The criminals then manipulate victims into paying their released superannuation money into the many mule accounts within Australia's banking system, where the money is laundered and victims have no redress.
Importantly, scam-related losses are not confined to retirees. Younger Australians increasingly hold significant superannuation balances and are being targeted through online investment fraud and identity compromise. This means superannuation fraud should not be viewed solely as a retirement issue, but as part of Australia's broader cybercrime and financial crime challenge.
SVA strongly supports:
stronger governance obligations for platform trustees, particularly those involved in the First Guardian and Shield debacle;
codified due diligence requirements, especially for banks, ASIC, auditors and the Australian Taxation Office;
waiting periods for certain super rollover and switching transactions;
stronger scrutiny of advice-fee deductions;
enhanced compensation and redress pathways for victims, particularly through the Australian Financial Complaints Authority (AFCA); and
tighter regulation of lead generation and investment promotion models.
1. Mandatory scam disruption for large super withdrawals and rollovers
Trustees, banks, superannuation funds and "custodians" who hold credit or financial services licences should be required to implement mandatory scam-risk checks where:
a member is transferring substantial balances to newly established SMSFs or super rollover products;
funds are being rolled into non-diversified investment products and managed investment schemes;
auditors are not from a respected Australian firm that does quality work;
unusual withdrawal or rollover behaviour is detected; or
known red-flag indicators are present, like rapid placement and layering of funds or rapid deposits and withdrawals.
This should include mandatory customer contact by licensed financial firms, cooling-off periods and independent verification requirements. It should also include strong reimbursement obligations when licensed firms and accounting professionals like auditors fail to get it right.
AUSTRAC's recent indicators of suspicious activity [11] for the superannuation sector are welcome. However, they remain too heavily focused on traditional fraud, identity misuse and post-event transaction behaviour, rather than the reality of organised cyber-enabled fraud and AI-driven social engineering.
We think these indicators should be strengthened to better detect three things: scam-induced superannuation switching, behavioural manipulation, and coordinated criminal infrastructure operating across banking, telecommunications, digital platforms and superannuation systems simultaneously. Current indicators focus largely on unusual transaction size, fraudulent documents or account compromise after harm has already occurred. They do not adequately capture the behavioural and contextual indicators that often precede catastrophic losses. They also do not tie corporations charged with looking after superannuation to reimbursement obligations when they fail.
Case study: Ms T, targeted by relationship fraud twice, super also stolen
Ms T has an acquired brain injury. She had a successful career as a project manager but fell into deep depression after experiencing catastrophic relationship fraud, during which she took out several unsecured credit facilities. She borrowed money from family but still ended up homeless, living in her car. She rebuilt her life until she was targeted by a second relationship fraud. This is a common experience, as scam crime organisations know that previous victims are vulnerable to retargeting with a fresh, new approach. This time she was targeted through Instagram by an "army doctor trapped in Syria" who needed her help to get out.
During the second relationship fraud, the criminal suggested Ms T take out unsecured loans through Citi, Zip Pay and Zip Plus. Her physical health spiralled due to a hip injury. Her scammers had gained knowledge of the Australian superannuation early release conditions, and they manipulated her into making medical release claims against her large Australian industry super fund. A $20,000 release from her superannuation was successful. But rather than the funds being used to treat her medical condition, the scammers directed payments through a multitude of Australian mule bank accounts, PayPal, Steam gift cards and other gift cards. More than a dozen transfers, ranging from about $1,500 to $6,000, went to personal accounts at Bankwest, Commonwealth Bank, ANZ, Great Southern Bank and Bank First.
Ms T's case reveals that scams are directly eroding Australians' retirement savings through coercive superannuation withdrawals and the proliferation of mule accounts on Australian banking platforms. This happened alongside Centrelink dependency, high-risk loans and repeated scam indicators that financial institutions failed to interrupt. When the trauma of discovering the whole scheme was a fraud unfolded, the mental health harms were immense, and suicidal ideation is a common experience for victims. At this point, victims often urgently require access to their superannuation but cannot get it because they have already sent it to scammers.
Cases like this demonstrate that superannuation losses are not limited to SMSF investment fraud or illegal early access schemes. Increasingly, organised criminal networks exploit and socially engineer emotionally vulnerable consumers, leveraging Australia's lax banking and money laundering system controls to drain retirement savings in real time.
Takeaway: Any proposed Treasury reforms should explicitly recognise scam-induced superannuation depletion as a major financial crime and consumer protection issue. That requires mandatory intervention and reimbursement obligations, enhanced transaction monitoring and clearer compensation pathways for victims.
2. Stronger digital identity and account security protections
Australia urgently requires stronger protections against identity compromise across the banking and superannuation systems.
Minimum protections should include:
secure government identities robust enough to thwart organised crime networks that create mule accounts at scale to defraud ATO tax returns and engineer superannuation rollovers;
stronger recovery protections where identity, email or mobile phone/SIM compromise is suspected;
mandatory telephone alerts for changes to Australian Taxation Office, Medicare or superannuation fund contact details or linked accounts; and
rapid freeze mechanisms where fraud is suspected, or automatic reimbursement when licensed financial corporation failures are identified.
Case study: A banker experienced a data breach and later discovered that four Military Bank mule accounts had been created in his name. He only found out after his accountant queried why he was amending past tax returns.
3. Regulation of investment advertising and lead generation
Many superannuation scam victims are initially targeted through social media advertising and lead generation funnels that appear legitimate. Lead generation activity connected to superannuation switching or investment promotion should face significantly higher scrutiny, licensing obligations and enforcement, as outlined in our submission to Treasury's other consultation. We see harm not only in investment or SMSF creation, but also in "scam recovery", "AI trading" and other false opportunities.
[Image: flowchart "How one ad click can lead to people losing all their super"]
How one ad click can lead to people losing all their super:
Ads are targeted to people looking to improve their superannuation.
The victim clicks on an ad and submits their email and phone number.
A lead generator calls the victim, who reveals more and more personal information.
The lead generator learns how much super the victim has, and the victim is on the hook.
A licensed Statement of Advice is issued.
The victim is conned into "switching" to an SMSF.
The underlying managed investment schemes "collapse". This is fraud: victims are robbed, but there is no investigation.
ASIC and APRA do not communicate with victims.
Some victims take action through AFCA and the CSLR.
Liquidators are slow to report, and victims are not a priority.
Victims are left with no recourse.
4. Royal Commission, mandatory reimbursement and simple compensation pathways
Consumers currently face fragmented and inconsistent recovery pathways after superannuation-related fraud. SVA supports reforms requiring trustees and platforms to compensate members where governance failures, inadequate controls or poor due diligence contributed to losses. The AFCA process is difficult, traumatic and unlikely to lead to any redress for victims, compounding the harm they experience.
Compensation frameworks should recognise scam-related harms where consumers were manipulated through sophisticated deception, not only traditional unauthorised access.
We believe regulators like ASIC should be notifying victims of investment and superannuation losses, so that victims know the pathways available to pursue recovery or reimbursement, such as applying to the Compensation Scheme of Last Resort (CSLR).
Because AFCA is so harmful and traumatic for victims, the discretionary Act of Grace payments [12] and the Scheme for Compensation for Detriment caused by Defective Administration (CDDA Scheme) [13] need to be made clear for victims seeking redress.
AFCA takes a quick box-ticking approach to resolving complaints through its external dispute resolution (EDR) process. It commonly adds to the trauma and distress that victims feel, particularly when their cases are mired in delays and AFCA's determination and membership fees are prioritised over payments to victims.
SVA submits that the evidence emerging from Shield, First Guardian, Prime Trust, Lion Property Group, Australian Fiduciaries and related matters demonstrates the need for a Royal Commission into financial crime, regulatory failure, superannuation switching misconduct and compensation system gaps across Australia's financial services sector.
The issues revealed by Treasury, ASIC and Department of Finance material are not isolated operational failures. They point to systemic structural weaknesses involving:
conflicted financial advice ecosystems;
inadequate platform trustee oversight;
weak inter-agency coordination;
inconsistent regulatory intervention;
unclear liability allocation; and
significant barriers to compensation and procedural fairness for victims.
Importantly, Treasury and ASIC correspondence released under Freedom of Information [14] concerning the CDDA Scheme raises serious questions. It suggests Australians may have been effectively denied meaningful access to compensation pathways that Parliament intended to exist for losses connected to defective regulatory administration.
The Treasury correspondence disclosed under FOI suggests a prolonged and unresolved jurisdictional vacuum in which:
ASIC's CDDA authorisation lapsed in 2015;
Treasury and ministers subsequently argued they could not determine claims involving ASIC because of ASIC independence concerns;
victims were redirected toward Act of Grace processes instead; and
substantial claims appear never to have been determined on their merits.
SVA is deeply concerned this may have created a practical denial of procedural fairness for victims of alleged regulatory failures and defective regulator administration. This is particularly concerning when victim-survivors of SMSF fraud continue to pay ongoing accounting and ASIC registration fees, and in some cases fines, that add to the harm.
We believe a Royal Commission should therefore examine:
whether current compensation and redress frameworks for fraud and scams are fit for purpose;
whether victims are being improperly excluded from Government compensation pathways and denied procedural fairness;
whether the CDDA, Act of Grace, AFCA and CSLR frameworks create structural barriers to fair compensation, particularly when victims are not notified in a timely way to apply for this limited redress;
whether regulatory agencies act promptly and effectively in response to known fraud and crime risks;
the role of lead generators, advisers, platforms, banks and SMSFs in enabling consumer harm;
whether current laws appropriately allocate liability for fraud and investment-related losses; and
whether Australia's financial crime response adequately reflects the scale of organised cyber-enabled fraud affecting consumers, and the potential harm it can cause to trust in governments.
SVA submits that without a comprehensive public inquiry, Australia risks repeating the same cycle observed after previous financial collapses and the 2018–19 Banking Royal Commission: widespread consumer harm, fragmented accountability, delayed reform and inadequate compensation outcomes.
Consumers should not be forced to navigate opaque jurisdictional disputes between agencies while suffering catastrophic losses connected to regulatory failures or systemic misconduct.
5. Recognition of fraud as a financial crime and productivity issue
Scams and cyber-enabled fraud are no longer isolated consumer issues. They represent organised transnational financial crime causing widespread economic and psychological harm to Australians. The risk of illicit capital flowing to offshore actors is real, and it causes grave trafficking harms in other countries around the globe.
Superannuation protections should therefore be designed not only as consumer safeguards, but as part of Australia's broader anti-money laundering, cybercrime and financial crime response. A cohesive national fraud strategy that treats these crimes as both a national security issue and a consumer protection issue is now urgent.
6. Artificial intelligence will increase scale and harm
SVA is concerned that artificial intelligence (AI) is rapidly increasing the scale and sophistication of financial crime targeting Australians, including superannuation members. The immediate threat is not speculative "superintelligent" AI systems. It is the industrialisation of existing scam techniques such as phishing, smishing, impersonation and fraudulent investment advertising on social media platforms.
The social engineering playbooks behind these scams already exist and are highly effective. AI removes the remaining operational bottleneck by allowing criminal networks to automate and scale deceptive communications, relationship grooming and fraudulent investment promotion at volumes previously impossible without large human workforces.
This creates a profound asymmetry between criminals and defenders, and between criminals and victims. Criminal actors are unconstrained by governance, ethics or compliance obligations. Financial institutions, trustees and technology providers, by contrast, remain bound by fragmented regulatory settings that often limit their ability to deploy effective detection systems. The increasing use of real-time payments and rapid superannuation switching mechanisms further reduces the opportunity to detect and disrupt fraudulent transactions before funds become unrecoverable.
Australia urgently requires a regulatory framework that supports responsible AI-enabled fraud detection, stronger behavioural monitoring capabilities and clearer guidance for institutions seeking to identify scam-related activity before catastrophic losses occur. Without urgent action, AI will dramatically accelerate the scale of financial harm experienced by Australian consumers and superannuation members.
AI systems are now "agentic": they can access databases, read documents, execute workflows and interact with external systems through basic OAuth sign-ins [15]. This dramatically expands the consequences of social engineering and prompt injection attacks. In practical terms, criminals may no longer need sophisticated malware or traditional hacking techniques to compromise systems if AI-enabled tools can be manipulated into performing unintended actions on their behalf.
SVA believes Australia urgently requires clearer national guidance on the responsible use of AI for scam and fraud prevention. This should include stronger frameworks for secure AI system design, behavioural anomaly detection, digital identity protection and real-time intervention capabilities. Without rapid regulatory and technical adaptation, AI-enabled fraud risks will increasingly undermine trust in banking, superannuation and digital financial systems, while exposing Australian consumers to catastrophic and large-scale financial harm.
SVA believes Australia has a structural and systemic problem of fraud inside our trusted financial systems. Lead generation, conflicted advice, fast SMSF establishment, weak switching friction, poor platform due diligence and inadequate redress are all symptoms of this structural problem. Treasury material has recognised that scammers exploit how easy SMSFs are to establish. This includes cases where people are persuaded to roll over balances from APRA-regulated funds into newly created SMSFs, after which funds may be stolen from an SMSF bank account controlled by scammers.
SVA contends that past frauds like Astarra Trio and Prime Trust reveal an endemic pattern of victims being left in a redress gap, where no agency accepts practical responsibility for deciding compensation claims on their merits.
Our conclusion
Australians should be able to trust that their retirement savings are protected from sophisticated criminal exploitation. When these protections fail, we believe the CSLR must be a quick and painless process by which to recover and start rebuilding superannuation assets.
Treasury's proposed reforms are an important step forward. However, stronger preventative safeguards, scam-specific intervention measures and clearer compensation pathways are essential to restoring public trust and protecting Australians from devastating financial harm.
The Scam Victim Alliance welcomes continued engagement with Treasury on these reforms.
References
"Retirement Standard." ASFA. Accessed 10 May 2026. https://www.superannuation.asn.au/consumers/retirement-standard/
Eagar, Kathy. "Best of 2025 – Government Is Planning Hardship for Older Australians Living at Home." Pearls and Irritations, 9 January 2026. https://johnmenadue.com/post/2026/01/best-of-2025-government-is-planning-hardship-for-older-australians-living-at-home/
SBS News. "'No Vacancies': Australia Is Getting Older — and We're Facing a 'Conundrum.'" 11 June 2026. https://www.sbs.com.au/news/article/will-federal-budget-keep-pace-with-ageing-australians/ltljydliy
ABC News. "Collapses Expose Deep Flaws in Australia's $4.3 Trillion Super System." 18 September 2025. https://www.abc.net.au/news/2025-09-19/first-guardian-shield-collapse-asic-and-superannuation-flaws/105783328
ASIC. "22-363MR Melbourne Woman Sentenced after Stealing Millions from Superannuation and Share Trading Accounts." Media release. Accessed 10 May 2026. https://asic.gov.au/
Taylor, Josh. "$500,000 Stolen in Australian Super Fund Data Breach." The Guardian, 4 April 2025. https://www.theguardian.com/australia-news/2025/apr/04/australian-super-funds-compromised-cybersecurity-data-breach-hack
Poptodorov, Kon (LexisNexis Risk Solutions). "Op-Ed: Protecting Superannuation Accounts from Rising Cyber Security Risks." Cyber Daily, 7 May 2025. https://www.cyberdaily.au/security/12061-op-ed-protecting-superannuation-accounts-from-rising-cyber-security-risks
ASIC. "Australian Fiduciaries Ltd." Accessed 22 May 2026. https://www.asic.gov.au/
ASIC. "Lion Property Group." Accessed 22 May 2026. https://www.asic.gov.au/
ASIC. "26-093MR ASIC Permanently Bans Queensland Property Developer Trent Giumelli from Financial Services." Media release. Accessed 22 May 2026. https://asic.gov.au/
AUSTRAC. "Indicators of Suspicious Activity for the Superannuation Sector." Accessed 10 May 2026. https://www.austrac.gov.au/industry-and-business/education-and-resources/publications-and-resources/indicators-suspicious-activity-superannuation-sector
Department of Finance. "Act of Grace Payments." Accessed 22 May 2026. https://www.finance.gov.au/individuals/act-grace-payments-waiver-debts-commonwealth-compensation-detriment-caused-defective-administration-cdda/act-grace-payments
Department of Finance. "Scheme for Compensation for Detriment Caused by Defective Administration (CDDA Scheme)." Accessed 22 May 2026. https://www.finance.gov.au/individuals/act-grace-payments-waiver-debts-commonwealth-compensation-detriment-caused-defective-administration-cdda/scheme-compensation-detriment-caused-defective-administration-cdda-scheme
Department of the Treasury. "FOI – Australian Securities and Investments Commission (ASIC)." 4 May 2026. https://treasury.gov.au/the-department/accountability-reporting/foi/3041
Obsidian Security. "OAuth Vulnerabilities Every Security Team Should Know." Accessed 11 May 2026. https://www.obsidiansecurity.com/blog/oauth-vulnerabilities-security-teams
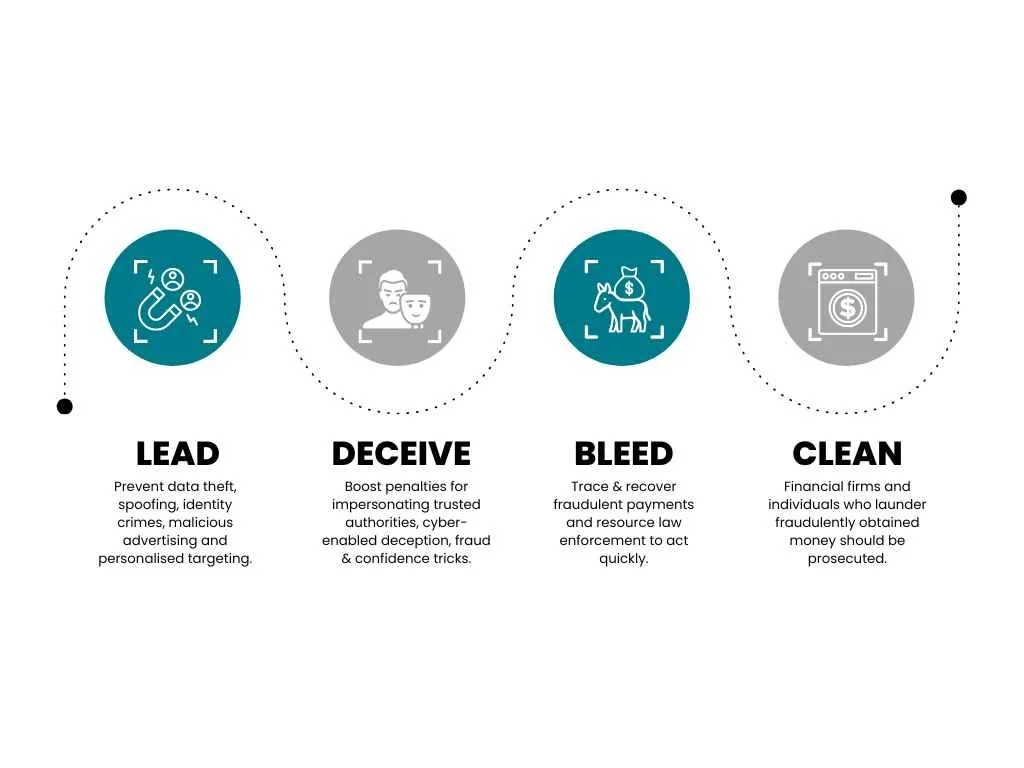
industrialised lead generation IS a financial crime blind spot
Scam Victim Alliance Every believes every major financial fraud follows the same pattern of LEAD-DECEIVE-BLEED-CLEAN. Victims are identified, profiled and nurtured long before they lose money or realise they’ve been defrauded. This submission argues that Australia's regulatory system focuses almost entirely on the moment money is stolen, while ignoring the industrialised lead-generation ecosystem that makes large-scale fraud possible.
Superannuation fraud is no longer primarily a consumer protection problem. It is a national economic security problem. The First Guardian, Shield and Australian Fidiciaries Ltd collapse of ASIC-registered managed investment schemes needs transparency and reforms to prevent more Australians losing their superannuation.
Executive summary
Scam Victim Alliance is a community of fraud victims supporting hundreds of Australians through the trauma that follows life-changing financial crime.
We welcome Treasury's recognition that lead generation sits at the beginning of the chain of events that can ultimately cause significant consumer harm.
Our experience suggests the problem may be larger than currently recognised, with “check your super” advertising thriving online.
Lead generation has evolved into the industrial front-end of organised financial crime and fraud. Today's criminal enterprises use the same advertising technology, behavioural profiling and customer acquisition techniques as legitimate businesses. Australians searching online to compare their superannuation, invest for retirement, recover scam losses or simply look for a new job can unknowingly enter sophisticated fraud funnels designed to identify, influence and eventually exploit them.
A compromised online banking login can reportedly be purchased for less than US$10. Digital advertising can then be used to identify and recruit thousands of potential victims at scale. Artificial intelligence is accelerating this process, making scams cheaper to run, more convincing and far harder to detect.
Australia's regulatory framework has not kept pace.
Our submission argues that lead generation should be viewed as critical financial fraud infrastructure rather than simply another form of advertising.
Unless governments regulate the beginning of the fraud journey, enforcement will continue to occur only after Australians have already lost their homes, retirement savings and financial security.
7 key Scam Victim Alliance recommendations to improve lead generation
Assume all Australians are targets for organised cybercrime as low-cost cybercrime-as-a-service offers shifts profit incentives towards criminal extraction of wealth from Australia’s legitimate banking and superannuation systems.
TAKEAWAY: Recognise fraud as an economic productivity and national security threat and respond quickly as AI and Quantum computing rapidly amplify the harm.
Ban algorithmic digital advertisingfor high-risk financial products, including scam recovery, comparing superannuation, investing, AI trading, creating SMSFs and “investing in property through your super”. Mandate that digital platforms, registered businesses and AI platforms retain advertising viewed against on user profiles to ensure victim redress and a successful ‘whole of system’ approach to preventing, disrupting and enforcing scams and fraud.
TAKEAWAY: Build technical capture and licensing requirements into lead generation and fraud facilitation - including ‘native content’ and ‘educational content’ and ‘website quizzes’ to ensure fraud victims can trace back the social engineering pathways after they have suffered a loss. It is critical that platforms capture and save financial services ads to be able to trace back which actors placed and profited from the lead generation and the downstream commissions.
Ban high-harm vehicles and facilitators for fraud such as weak auditors and crypto ATMs The best fraudulent schemes lay the groundwork over months, much like the First Guardian-Shield lead generation systems. Preventing the manipulation of Australians into believing a scheme is in their best financial interest is where the focus should be. Prohibiting social engineering through misleading online articles, website tools to “compare super”, “recover scam losses” or invest in “AI trading” used as lead capture unless independently verified and transparent with clear license numbers, with domain registrants also required to keep data on corporate entities..
TAKEAWAY: Introduce civil and criminal liability for professional facilitators — including lawyers, accountants, auditors, company formation agents, crypto ATMs, SMSF creators — who recklessly enable the creation and scaling of fraudulent financial schemes.
Adopt a victim-centred and ‘safe systems’ approach to fraud redress, including law enforcement follow-up, mandatory reimbursement and no-cost victim support through the Australian Financial Complaints Authority, as per Australia’s pledge at the UN Global Fraud Summit[1].
TAKEAWAY: Establish a national fraud strategy, similar to Britain’s Fraud Strategy 2026-2029[2] policy paper to guide a cohesive regulatory and enforcement approach
Ensure government identities cannot be forged to create more mule accounts which continue fraud harms. The Treasury must recognise the growing economic absurdity of identity fraud: leaked driver licence and passport credentials can be purchased online for under $10, while governments and victims bear replacement and remediation costs many times higher — often $30 or more for a driver licence and substantially more for passports and associated recovery processes.
TAKEAWAY: Australia should examine integrated anti-fraud identity models such as Singapore’s Singpass and MyInfo framework, which securely connects government identity verification with banks, telecommunications providers and regulated institutions in real time. A nationally coordinated digital identity ecosystem would significantly reduce impersonation fraud, mule account creation and document misuse while lowering long-term remediation costs for both governments and consumers.
Make fund recovery of fraud reportable and measurable. Singapore is already capturing this data[3] to measure how much of its citizen legitimate wealth is being hijacked by cybercrime to fund and scale further global crime harms.
TAKEAWAY: ACCC’s Scamwatch should report fund recoveries, not just reported scam losses. Australia should make fraud recovery rates formally reportable and measurable across banks, regulators and law enforcement agencies, recognising that stolen money is not simply an individual consumer loss but part of a global criminal economy that funds wider harms including human trafficking, child exploitation, drug trafficking and wildlife crime.
Hold a royal commission into financial crime and fraud. Australia should establish a Royal Commission into financial crime and fraud to examine the rapid industrialisation of scams, superannuation investment fraud, mortgage fraud, cyber-enabled theft and organised money laundering across the economy.
TAKEAWAY: Financial crime is no longer an isolated consumer issue — it is a growing national economic security threat. A Royal Commission would help expose the scale of organised fraud operating across Australia, identify systemic failures and build the coordinated safeguards, intelligence-sharing systems and accountability mechanisms needed to protect Australians from increasingly sophisticated transnational criminal networks, as Australia pledged at the recent UN Global Fraud Summit.
All Australians with money are ‘leads’ for malicious fraud schemes
Lead generation, cold-calling and other forms of ‘marketing’ create predictable pathways for fraud that begin long before any money is lost. Even before AI accelerated the disruption of financial services markets, consumers have long relied on Google searches, online ads, comparison tools and word of mouth advice from friends, as well as aggregators like Product Review or TrustPilot.
In a modern digital economy, individuals have their details and online cookies captured and passed along simply by reading legitimate commercial news websites. Scammers increasingly recruit victims through the same algorithmic advertising infrastructure that underpins Australia’s commercial news ecosystem.
Diagram (ii) Algorithmic ads on TheAge.com.au recruit leads for a range of businesses, both legitimate and illegitimate
Major publishers rely on a layered ad-tech stack—including content recommendation engines such as Outbrain and Taboola, programmatic ad exchanges like Google Ad Manager and supply-side platforms such as Magnite—which dynamically auction and optimise content placement based on engagement metrics. These algorithmic systems are designed to maximise click-through rates and user attention, not to assess the legitimacy of underlying content. As a result, scam actors can cheaply purchase targeted exposure and exploit behavioural profiling tools, which sell cheaply to the types of actors who orchestrated the First Guardian and Shield collapse.
Note that a ‘high value individual’ can be someone who is looking at content relevant to a major life event like trying to find a new job, getting married, having a baby, moving house, planning retirement or looking to invest. All of these life events are ‘leads’ for malicious industrialised fraud actors who have breached Australia’s trusted infrastructure (such as the Penthouse Syndicate inside NAB).
This creates an environment where fraudulent investment ads, impersonation content, and other scam vectors are distributed at scale alongside legitimate journalism. The fragmentation of responsibility across multiple intermediaries further weakens accountability, enabling scammers to rapidly test, iterate, and optimise deceptive campaigns in ways that mirror legitimate digital marketing practice, where algorithmic advertising ramps up the harms.
Evidence from the First Guardian and Shield collapse Facebook and Google ads highlights how industrialised and algorithmic lead-generation ecosystems create the on-ramp for large-scale financial harm. Testimony indicates the existence of organised “lead gen” networks in Queensland and Victoria spruiking website landing pages that got people to ‘check their super’ or ‘compare their super’. Actors from these schemes have told Scam Victim Alliance that between $20m and $40m was spent on digital ads over several years recruiting the 10,000 to 12,000 people who later lost money to these schemes.
The First Guardian and Shield loss experience further suggests that regulators can only detect misconduct after funds have been misappropriated. The collapse of Australian Fiduciaries Ltd followed a similar pattern, with nurses particularly exposed to the ‘lead-engage-convert’ model spruiking collapsed NDIS property schemes that enriched multiple .
The challenges experienced by consumers seeking redress through mechanisms such as the Australian Financial Complaints Authority, the Compensation Scheme of Last Resort, the CDDA or Act of Grace discretionary schemes highlight a deeper structural issue that requires urgent resolution.
There is a massive accountability gap for regulators, government agencies and trusted corporations holding credit, investment and other financial services licences while redress for harm remains limited and fragmented. When harm arises from lead generation practices that fall into regulatory grey areas, agencies and corporations will never be seen to have breached a specific duty.
When consumers can suffer significant financial loss without access to meaningful redress, it means our regulatory and enforcement frameworks do not adequately capture the early-stage conduct that set the harm in motion. This misalignment between how harm actually occurs and how responsibility is assessed underscores the need to bring lead generation activities more clearly within the regulatory and enforcement perimeter.
Strengthening oversight of lead generation is therefore not only a preventative measure, but a necessary step to restore accountability across the system. By clearly defining when lead generation activities constitute a financial service, extending obligations to those who influence consumer decision-making, and addressing incentive structures that prioritise conversion over suitability, the regulatory framework can better reflect the realities of how financial harm occurs. Without these reforms, compensation schemes will continue to struggle to deliver outcomes for affected consumers, as the origin of harm remains structurally disconnected from the points at which responsibility is currently assessed.
Artificial Intelligence is scaling harm
Artificial intelligence is improving efficiency across the financial system, but also amplifying risks like synthetic identity, misinformation, disinformation and fraud. Our community has lived experience (and large financial losses) which show structural apathy, political inertia, and financial institutional design failures are scaling the financial harm.
Consumers are often presented with promotional content that mimics trusted guidance, without clear, consistent or comparable disclosure of commercial intent, remuneration structures, or the risks associated with the recommended actions. By the time an unwitting consumer is on a call with an adviser or lead generator, they are already primed to accept bad advice.
Digital platforms have enabled the large-scale use of low-cost, algorithmically targeted advertising to circumvent longstanding protections such as bans on cold calling. Our engagement with victims involved in recent collapses such as First Guardian, Shield, Australian Fiduciaries Limited and Lion Property indicates that this ecosystem remains active. Advertisements across platforms such as YouTube and Facebook continue to funnel consumers into conversations with entities functioning as lead generators, operating under business models driven by switching fees and downstream commissions. These interactions frequently lead consumers toward complex and high-risk strategies—including SMSFs, leveraged property investment, scam recovery or speculative offerings—without the benefit of clear, standardised, and consumer-tested disclosures that would enable genuine comparison or informed consent.
Meanwhile, the corporations at the heart of these schemes also seem able to set up property developments and managed investments that also defraud banks and other finance companies by double-mortgaging assets that have little to no regulatory scrutiny. This submission calls for urgent reform: banning algorithmic ads for high-risk products, mandating licensing and vetting of all promoters, prohibiting deceptive comparison platforms, and adopting victim-centred enforcement including restitution and protections from further penalties.
OXIL research shows scam and fraud targeting is now based on situational vulnerability
Large-scale analysis of scam activity shows that modern fraud is not random but engineered. Lead generators build trust through a ‘funnel’ that starts with a signal of intent from a vulnerable consumer. Digital platforms succeed at not simply marketing, but also scaling systems in which individuals are identified, filtered and engaged at moments when they are most susceptible to influence.
By leveraging personal and behavioural data, lead generation systems are able to prioritise those most likely to respond, effectively targeting vulnerability at scale. These systems operate using a combination of broad exposure and targeted engagement. Consumers may first encounter generalised advertising, but are quickly funnelled into more personalised interactions that build trust and momentum over time. This creates industrial-scale pipelines of potential victims, where influence is applied progressively rather than at a single point of decision. By the time a financial product or investment opportunity is presented, the individual has often already been psychologically primed, making the eventual decision appear voluntary while being shaped by earlier interactions.
When engagement, phone calls and relationship building is driven by repeated exposure, emotional cues and tailored messaging, traditional notions of consent—such as clicking on an advertisement or opting in to be contacted—do not reflect genuine understanding or agency.
This means the Treasury must urgently support a shift in regulatory approach. Rather than placing responsibility primarily on individuals to identify and avoid harm, there is a clear need to recognise lead generation as part of the broader harm pathway. This requires a safeguarding model that addresses risks earlier in the chain, ensuring that systems capable of identifying and influencing vulnerable consumers are subject to appropriate oversight, accountability and intervention.
Fraudsters have been emboldened by Australia’s weak approach to enforcing the law or addressing cyber-enabled financial harm. Fraudsters can use technology, fake identities, social media and sophisticated financial schemes to steal billions from ordinary Australians every year. These crimes hurt families, destroy retirement savings and weaken trust in banks, government and the financial system itself.
Scam Victim Alliance contends that improving identity protections, stopping dangerous advertising practices, holding facilitators accountable and building stronger cooperation between banks, regulators and law enforcement, Australia can make it much harder for organised fraud networks to operate. We believe money laundering laws can be used more effectively to stop the harm.
Fraud prevention should not depend on ordinary people spotting highly sophisticated crime on their own. Australia needs safer systems, faster action and stronger accountability before more people lose their homes, savings and futures.
Endnotes & references
Scam Victim Alliance. About Scam Victim Alliance.https://scamvictimalliance.org.au/about
Voce A, Morgan A. The Costs of Serious and Organised Crime in Australia. Australian Institute of Criminology, 2025.
Reserve Bank of Australia. Financial Stability Review: Financial Stability Implications of Artificial Intelligence. September 2024.
United Nations Office on Drugs and Crime. Global Fraud Summit 2026 Pledges.
UK Government. Fraud Strategy 2026–2029.
Ministry of Home Affairs (Singapore). Scam Loss Recoveries in the First Half of 2025.
Dastoor C. Calls to Fix Shield, First Guardian Anti-Hawking Loophole. Professional Planner, 20 August 2025.
Taylor C, Taylor A, Sutherland J, Hakmeh J, et al. Rethinking Scam Prevention: Large-Scale, AI-Powered Analysis for a Safeguarding Approach. Oxford Information Labs.
Taylor, Carolina Caeiro, Alice Taylor, James Sutherland, Joyce Hakmeh, Emily. “Rethinking Scam Prevention: Large-Scale, AI-Powered Analysis for a Safeguarding Approach - Research.” Oxford Information Labs. Accessed April 20, 2026. https://www.oxil.co.uk//research/rethinking-scam-prevention-large-scale-ai-powered-analysis-for-a-safeguarding-approach.
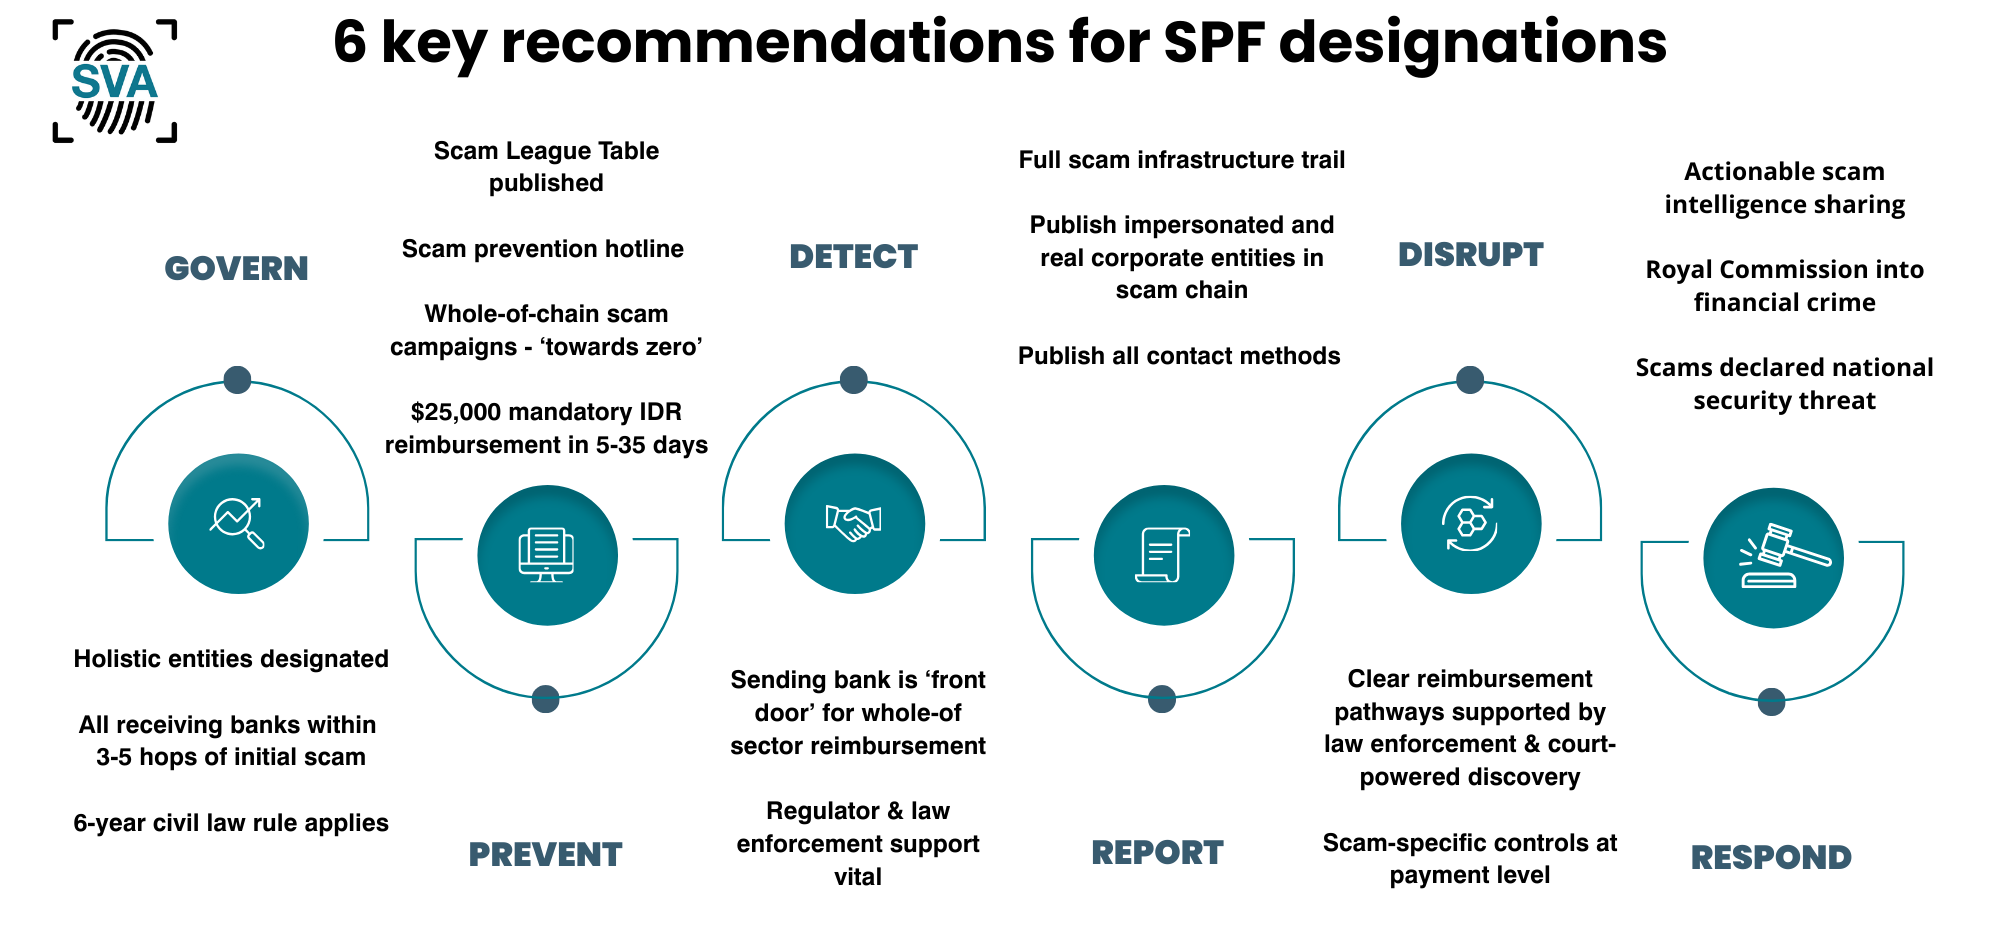
SVA Speaks out about scam prevention framework codes
Scam Victim Alliance has 6 key recommendations to stop Australia entrenching the harm of scams in response to Treasury’s SPF codes and designations.
Scam Victim Alliance spent our Christmas holidays writing this submission to Treasury about it’s world-leading reforms to fight scams. The SPF risks becoming a framework of good intentions that will actually increase scam harms unless the Codes impose clear and enforceable obligations on regulated entities
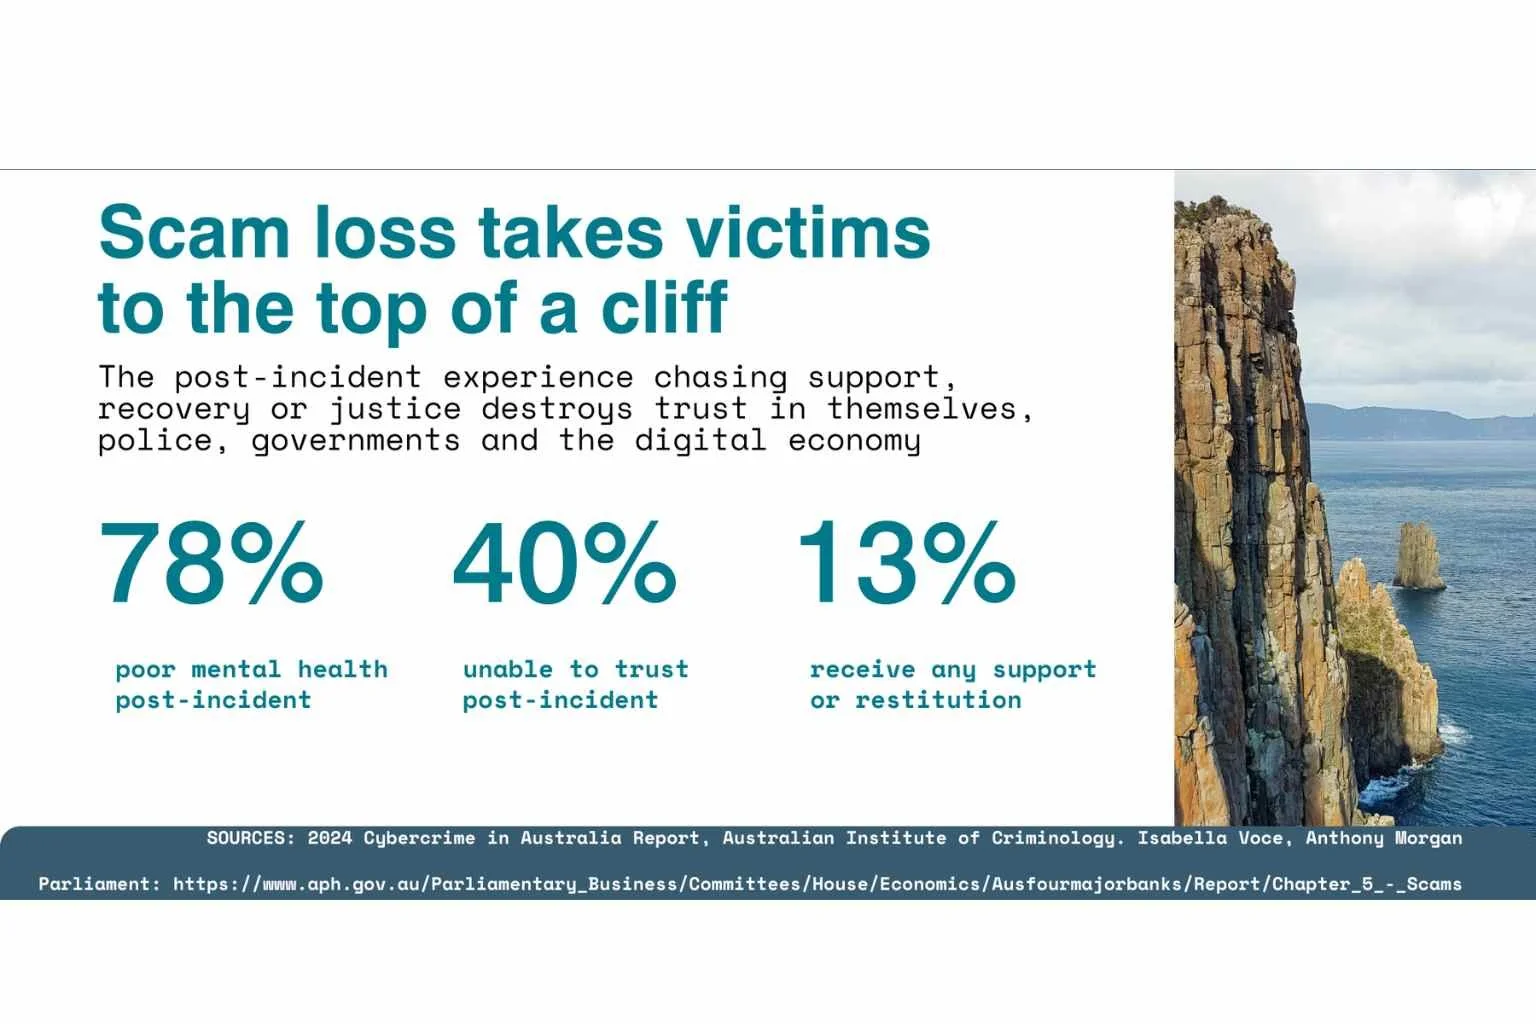
Executive summary
Our lived experience gives us deep insight into how scammers manipulate digital payment systems — and how banks, telcos, and digital platforms have allowed their infrastructure to be weaponised. Australian corporations are unwittingly funding what Interpol has called a “global crisis” of human trafficking and other criminal harm. We welcome this opportunity to make a submission to the SPF Treasury consultation.
Scam Victim Alliance (SVA) was founded in May 2025 to support Australians devastated by scam frauds, abandoned by a system that delivers inconsistent recovery processes and untold trauma.
Scam fraud hits hardest in Australia’s most vulnerable communities—older Australians and those from culturally and linguistically diverse (CALD) backgrounds—forcing taxpayers and individuals to carry the cost of the escalating scam fraud crisis harming all nations around the globe. Australia now faces scam compounds setting up shop on its doorstep—in Timor-Leste, New Guinea, Palau and Fiji, no doubt attracted by the rich pickings of Australia’s poorly protected payments markets.
We believe that if the clear recommendations from the 2019 Banking Royal Commission into Misconduct in the Banking, Superannuation and Financial Services Industry had been successfully implemented and enforced by APRA and ASIC, much of the scam-related harm experienced since 2020 could have been significantly reduced, as detailed in Appendix A. If scam losses and their downstream impacts were properly accounted for, the true cost to taxpayers would be staggering.
For example:
● Since 2019, 272,000 Australians over 65 have lost their superannuation to scams. If just 70% of these people had to then claim an Age Pension due to not having any superannuation, this would add an estimated $8.33 billion annually to Aged Pension costs.
● And if just 70% of Australia’s estimated 1.25 million scam victims since 2021 required Medicare-funded psychological support, it would cost taxpayers approximately $1.24 billion in mental health care.
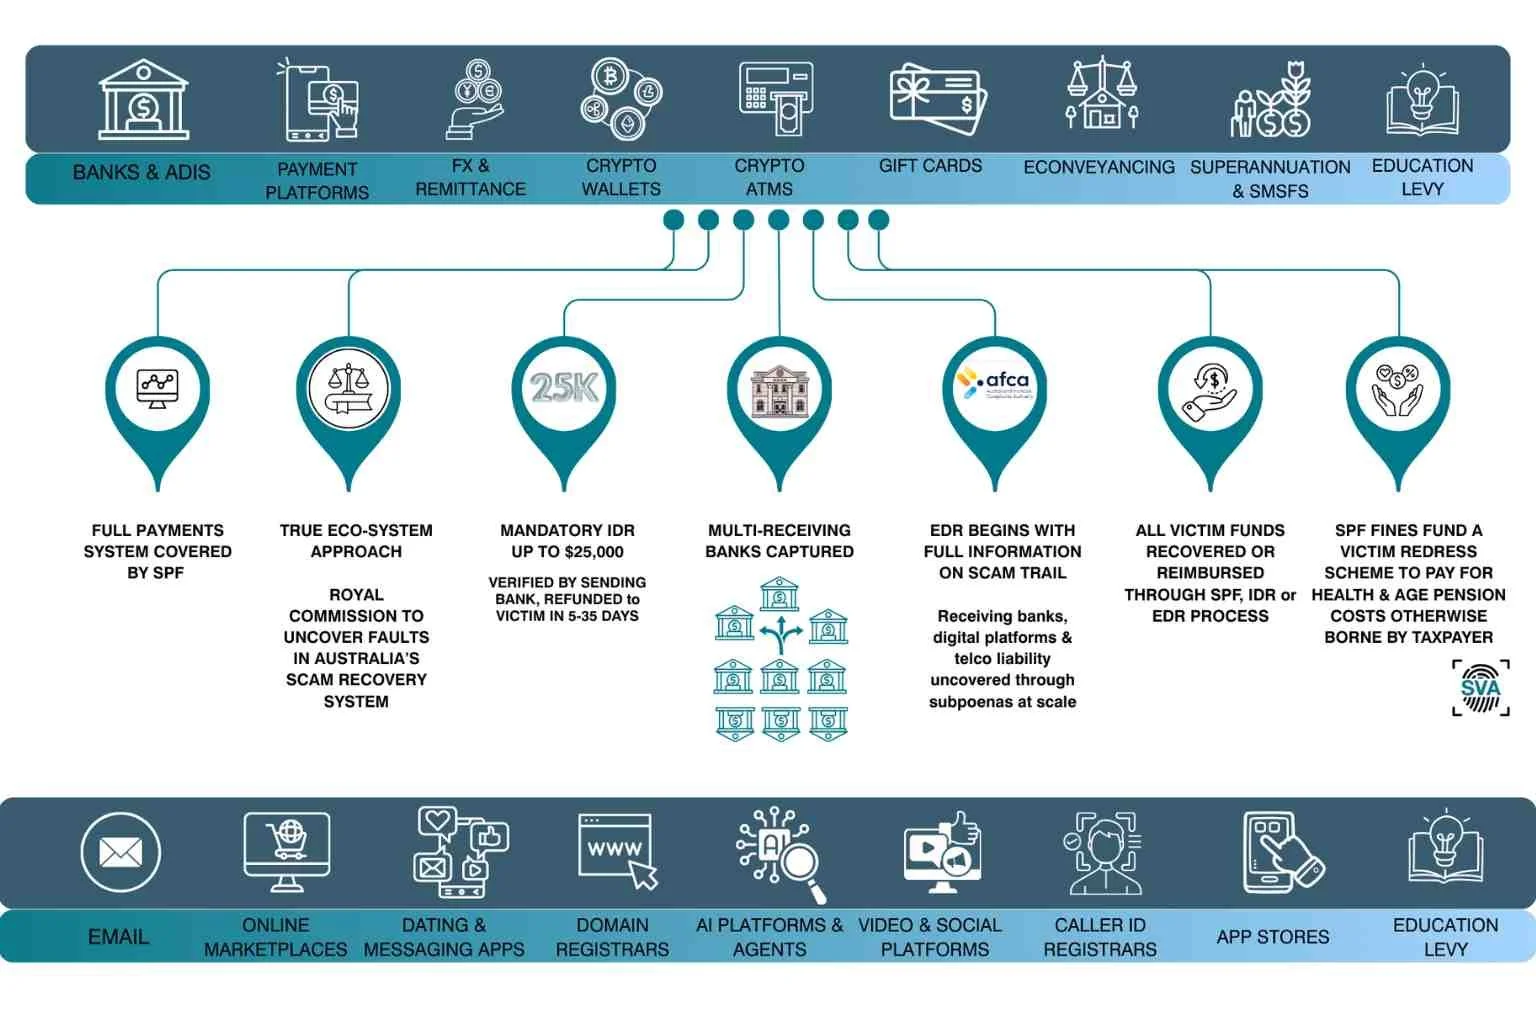
Our executive summary recommends key inclusions and designations to stop scams proliferating and make a genuine attempt to reimburse consumers.
These costs represent real and growing pressure on Australia’s public services, all while institutions that failed to prevent scam fraud are not held financially accountable.
In addition, we believe two critical failures have left Australians exposed to an untested legal liability that’s enabled large-scale theft from individuals through scams:
1.Banks have refused to acknowledge that their platforms and processes have been conduits for criminal fraud.
Banks have remained wilfully blind to their role in the fraud crisis, relying on the same strategies of denial used during the 2019 Royal Commission. Banks and payment platforms deflect from their facilitation of fraud (including impersonation and payer manipulation fraud) by insisting that scam losses are customers’ fault, even though banks have legal duties:
not to allow mule accounts to be established that don’t meet Know Your Customer (KYC) standards,
raise red flags for known scam patterns,
transparently recover scammed funds.
Banks spend millions marketing their “scam defences” and boasting about AI and staff investments — yet still blame customers when their own processes and failures to train staff on known scam typologies fail. Banks have ignored basic safeguards like 48-hour payment holds or MFA for high-risk transfers, such as property purchases or superannuation, and shifted the blame to customers rather than invest the paltry $100m needed to establish CoP before the fraud crisis escalated in 2020.
2. Regulators and Government failed to implement Confirmation of Payee (CoP) as part of the ePayments Code review early enough to protect Australians.
In 2019, Consumers Federation of Australia called out the lack of “meaningful sanctions to create an effective deterrent for non-compliance” in the ePayments Code, leaving Australians uniquely exposed to fraud. The ePayments Code - along with the Banking Code - are sometimes contentiously misinterpreted by an over-run External Dispute Resolution body, the Australian Financial Complaints Authority (AFCA).
In Part 2: Introduction of this submission, we outline how corporate failures have emboldened domestic fraudsters to escalate their tactics. In Part 3: Consultation questions we specifically explain the 6 key recommendations outlined in our Executive Summary below and in Part 4. Whole of ecosystem approach we offer our conclusions. Evidence for our recommendations is then provided in our Appendix items.
We welcome the draft Scam Prevention Framework (SPF) and newly published codes and designations which promised: “Victims will have clear pathways to compensation if the business fails to meet robust standards.” — Former Assistant Treasurer Stephen Jones on 13 February 2025 when he promised the SPF Codes would protect Australians and be operational from July 1 2026
Upon release of the designations from Treasury, analysis published in Australia’s leading financial newspaper stated:
“The definition of reasonable steps is rubbery enough to give the banks, telcos and social media platforms a “get out of jail free” card … Compounding that problem is the fact there will be no legally enforceable actionable scam intelligence for at least two years.” — Australian Financial Review’s Tony Boyd on 22 December 2025 about the newly released Treasury consultations and position paper this submission focuses on
SVA believes individual victims and taxpayers bear the cost of financial crime that corporations profit from. We believe the SPF designations must be significantly improved with 6 recommendations.
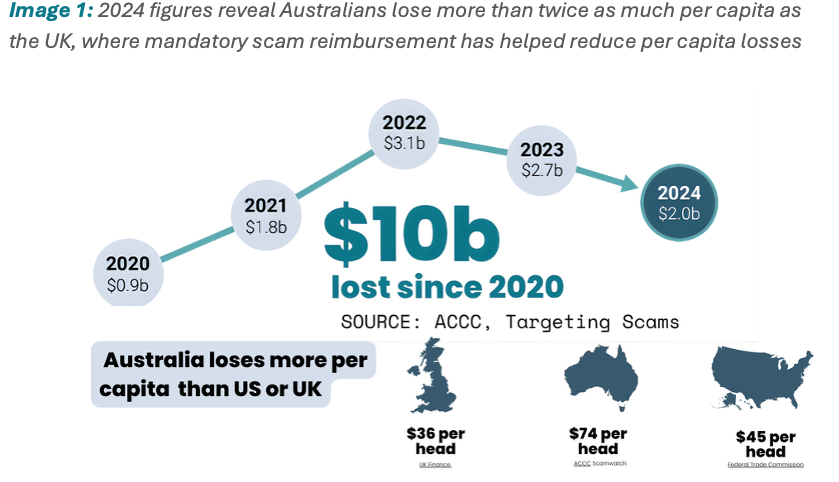
Recommendation 1. Governance works only if all entities in scam chains are designated
All relevant sectors must be designated under the SPF to ensure whole-of-ecosystem accountability and give the framework any chance of achieving its policy intent. This includes:
● Banking & Payments: All ADIs, non-bank remitters (especially foreign currency remitters such as Wise, Revolut or OFX), cryptocurrency exchanges and ATMs, eConveyancing platforms (PEXA and Sympli), gift card services, payment providers (BPay, PayID, Monoova, Cuscal, PayTo etc), and superannuation funds.
● Digital Platforms: Email hosts (e.g. Gmail, Outlook, Yahoo), online marketplaces (Meta, Gumtree, eBay), dating apps and platforms (Tinder, Hinge etc), domain registrars (e.g. GoDaddy, Ventra IP), Hosting platforms (e.g AWS or entities responsible for servers not serving illegal material), Caller ID registrants (e.g. Hiya), AI agents (e.g. ChatGPT, Claude, Gemini), App stores (side-loading malware is a key scam vector).
Furthermore, we believe that ASIC’s Registers and MoneySmart Investor warnings must be held to the same standard as the SPF dictates for regulated entities. Our community believes ASIC’s investor warnings have failed to keep up with known scam patterns and actively endangered people to invest in imposter and investment scams that could have been prevented through up-to-date warnings and a hotline to check for known scam types.
Additionally, an education levy should apply to designated sector ASIC registrations to fund a Safe Systems approach to scam awareness.
The SPF risks becoming a framework of good intentions that will actually increase scam harms unless the Codes impose clear and enforceable obligations on regulated entities.
The proposal for equal apportionment of scam-related compensation among institutions is problematic. Banks have historically borne the responsibility for safeguarding customer funds. Diffusing bank liability must be tied to demonstrated levels of responsibility and control failure—not arbitrarily split. Without enforceable standards and fair redress mechanisms, this framework will not only fail to protect Australians, it will entrench systemic gaps and allow industry actors to continue passing the cost of preventable fraud onto victims and taxpayers.
Recommendation 2. Prevent scams with a hotline and Scam Infrastructure League Table in advance of Actionable Scam Intelligence-sharing
A scam education campaign and consumer hotline should be funded through an ASIC levy on all SPF-designated entities or funded by proceeds of crime. Scam infrastructure reporting must begin in the first half of 2026 with the NASC publishing a Scam Infrastructure League Table, updated quarterly, listing the most misused corporate brands (including impersonations of government entities like the Australian Tax Office), mule accounts, phone numbers and scam ad, email and website tactics — with strict liability for entities failing to block repeated abuse. Consumers must be able to call a hotline to find out if they are paying a known scam account, receiving calls from a known scam number or receiving ads, emails or phone numbers from known scam compound devices or locations.
Furthermore, scam infrastructure data can already include existing intelligence like:
● Known mule accounts reported to Scamwatch, the Australian Financial Crimes Exchange, the Global Signal Exchange and state and federal law enforcement information,
● Known spoofed telephone numbers used in previous frauds investigated by ASIC,
● Known accounts flagged to AUSTRAC through SMR and TTR reports that are associated with other known scam typologies.
We would also contend that part of the harm to victims is not adequately measuring scam losses or how effective warnings and education campaigns are. We would also ask the Federal Government to find a better way to measure the taxpayer impost of looking after scam victims after losing life-changing amounts of money.
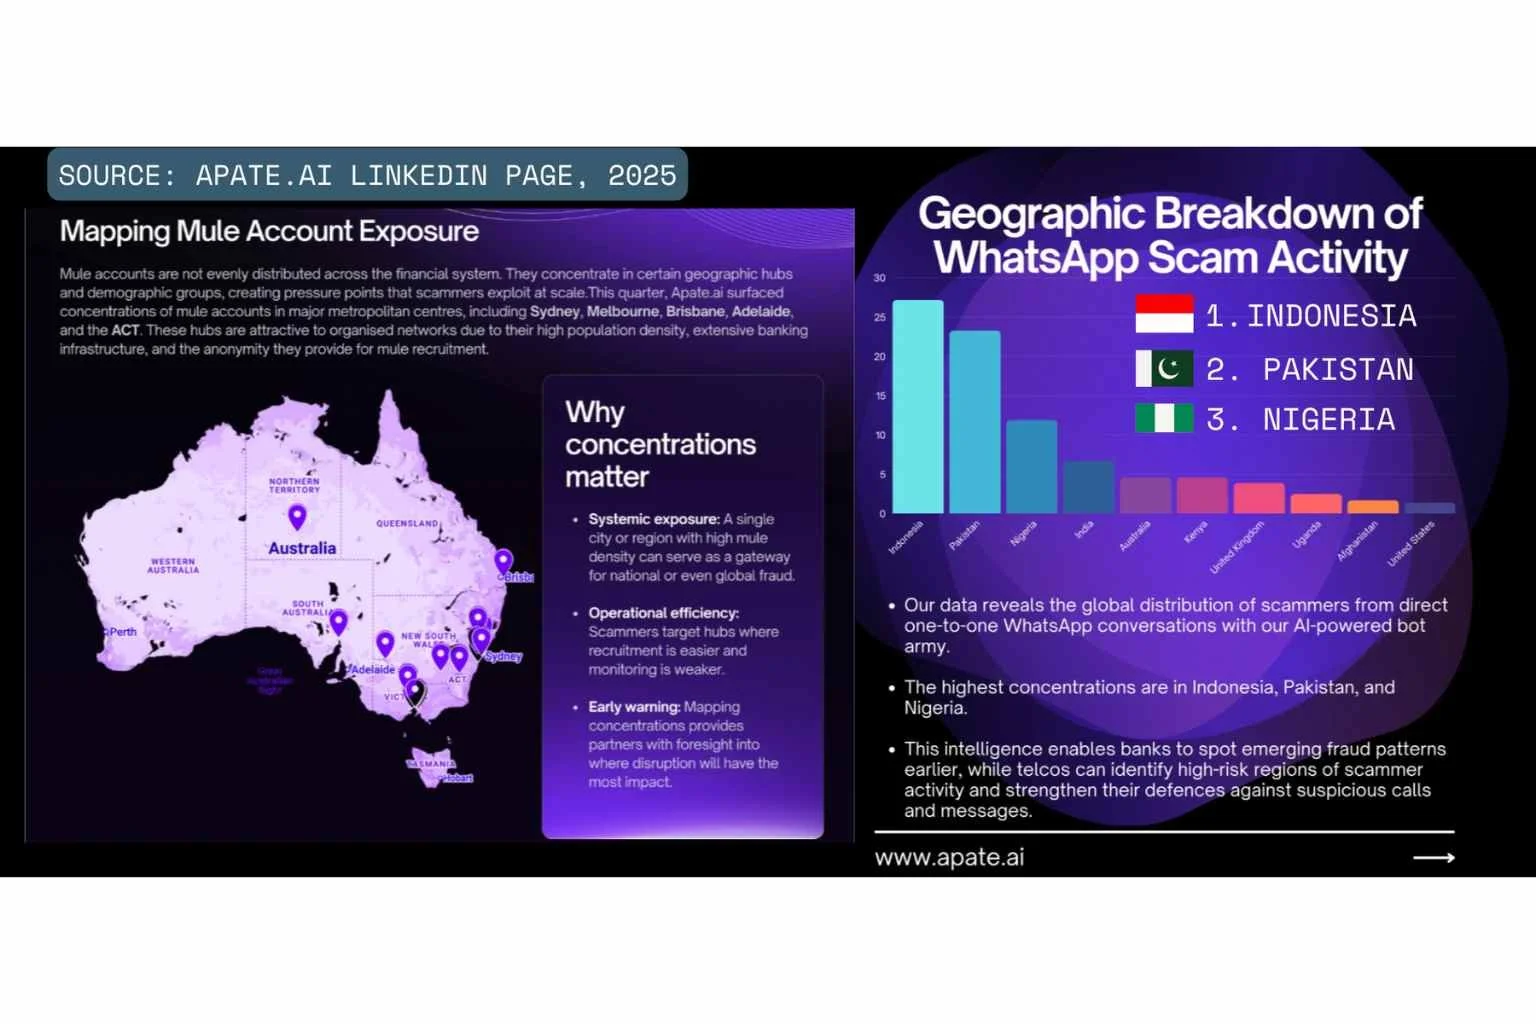
Recommendation 3. Detect by having sending banks as single ‘front door’ for whole-of-sector reimbursement, supported by regulators and law enforcement
Banks are best placed to act as the front door for scam reporting, verifying losses with their customers before collecting full scam infrastructure data (e.g. malicious ads, email headers, hosts of illegal content, mule accounts, fake domains, impersonated brands) to help detect patterns and trigger liability across non-bank sectors. Regulators and law enforcement would support this scam infrastructure reporting.
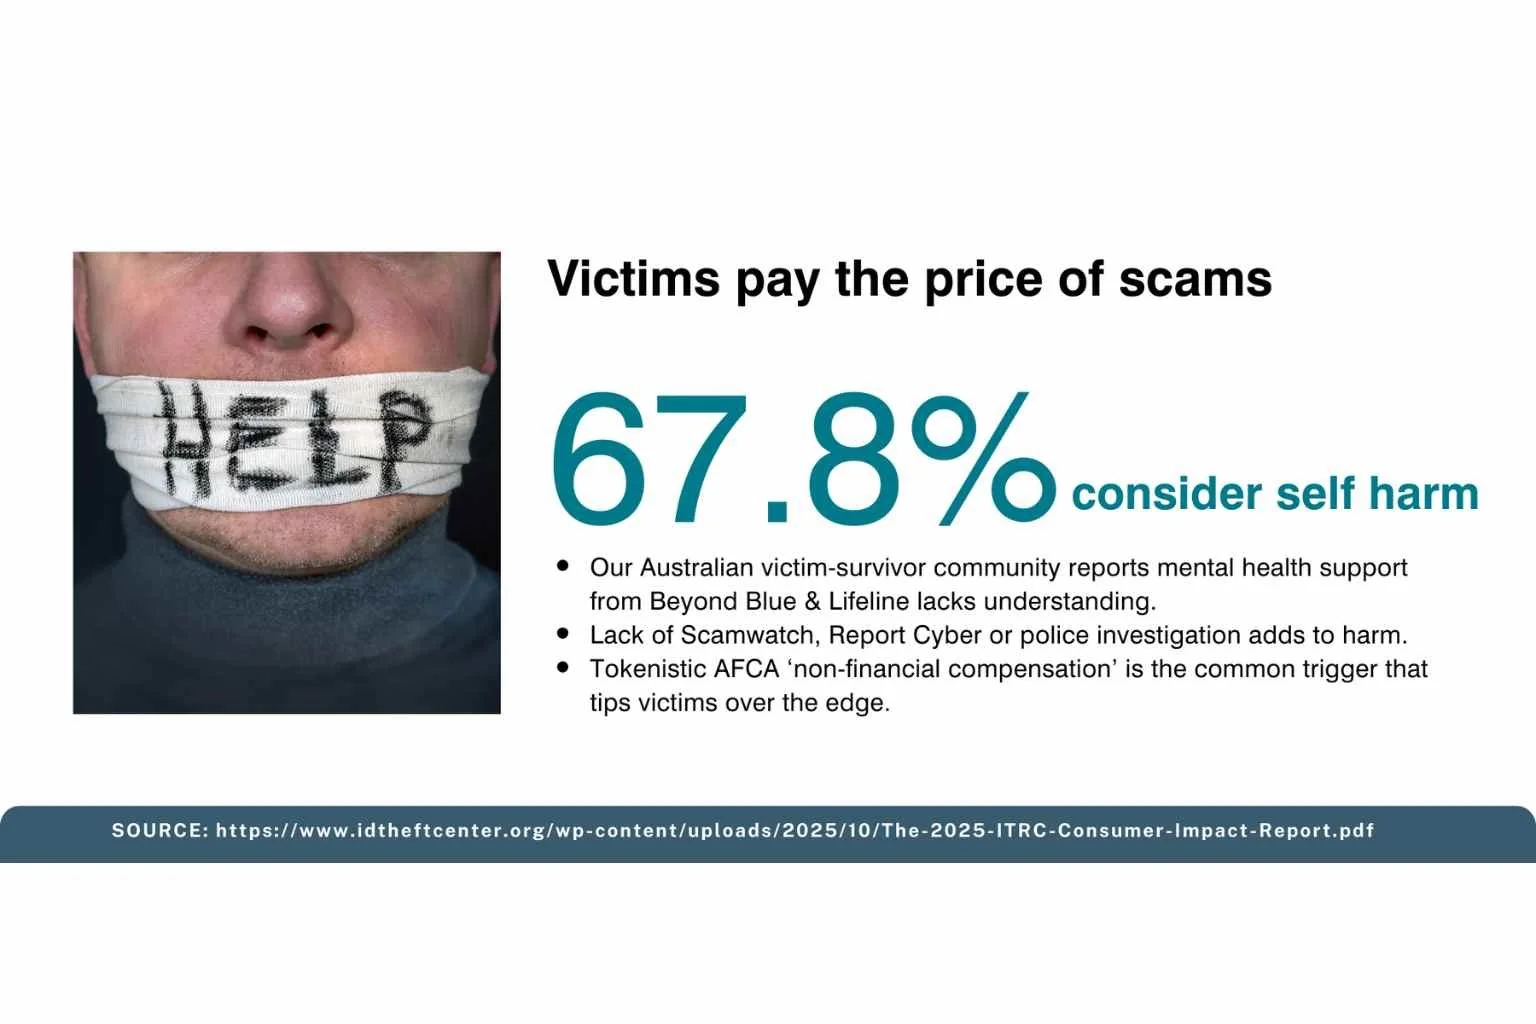
Recommendation 4. Report full scam payment‑trail disclosure to trigger a 5-35 day IDR reimbursement up to $25,000 with funds recovered from other SPF entities through infringement notices and court enforcement.
Banks must verify scam losses and pay up to $25,000 at IDR within 5–35 days. If a case is unresolved, regulators and law enforcement must subpoena the full scam trail - including scam infrastructure and receiving banks - before escalation to EDR or recovery from other sectors.
SVA recommends the full scam infrastructure trail must be subpoenaed quickly (ideally by day 36 after the scam report if mandatory $25,000 IDR reimbursement fails) to trigger early detection and disruption. Strict liability must apply to any entity that fails to block or shut down known scam infrastructure. All SPF fines should fund a victim redress scheme to fund ongoing reimbursement and mental health programs.
A separate ASIC scam education levy should apply to designated sectors and this education must be responsive and agile in the same way road safety campaigns and education adapts to high-risk road use trends. Education campaigns must be whole-of-sector focused and educate about corporate compliance culture, mule accounts and money laundering to prevent harm before it starts. This must include a free, language-supported telephone hotline for the public to check scam warnings and report suspicious activity — especially for vulnerable or non-digital consumers.
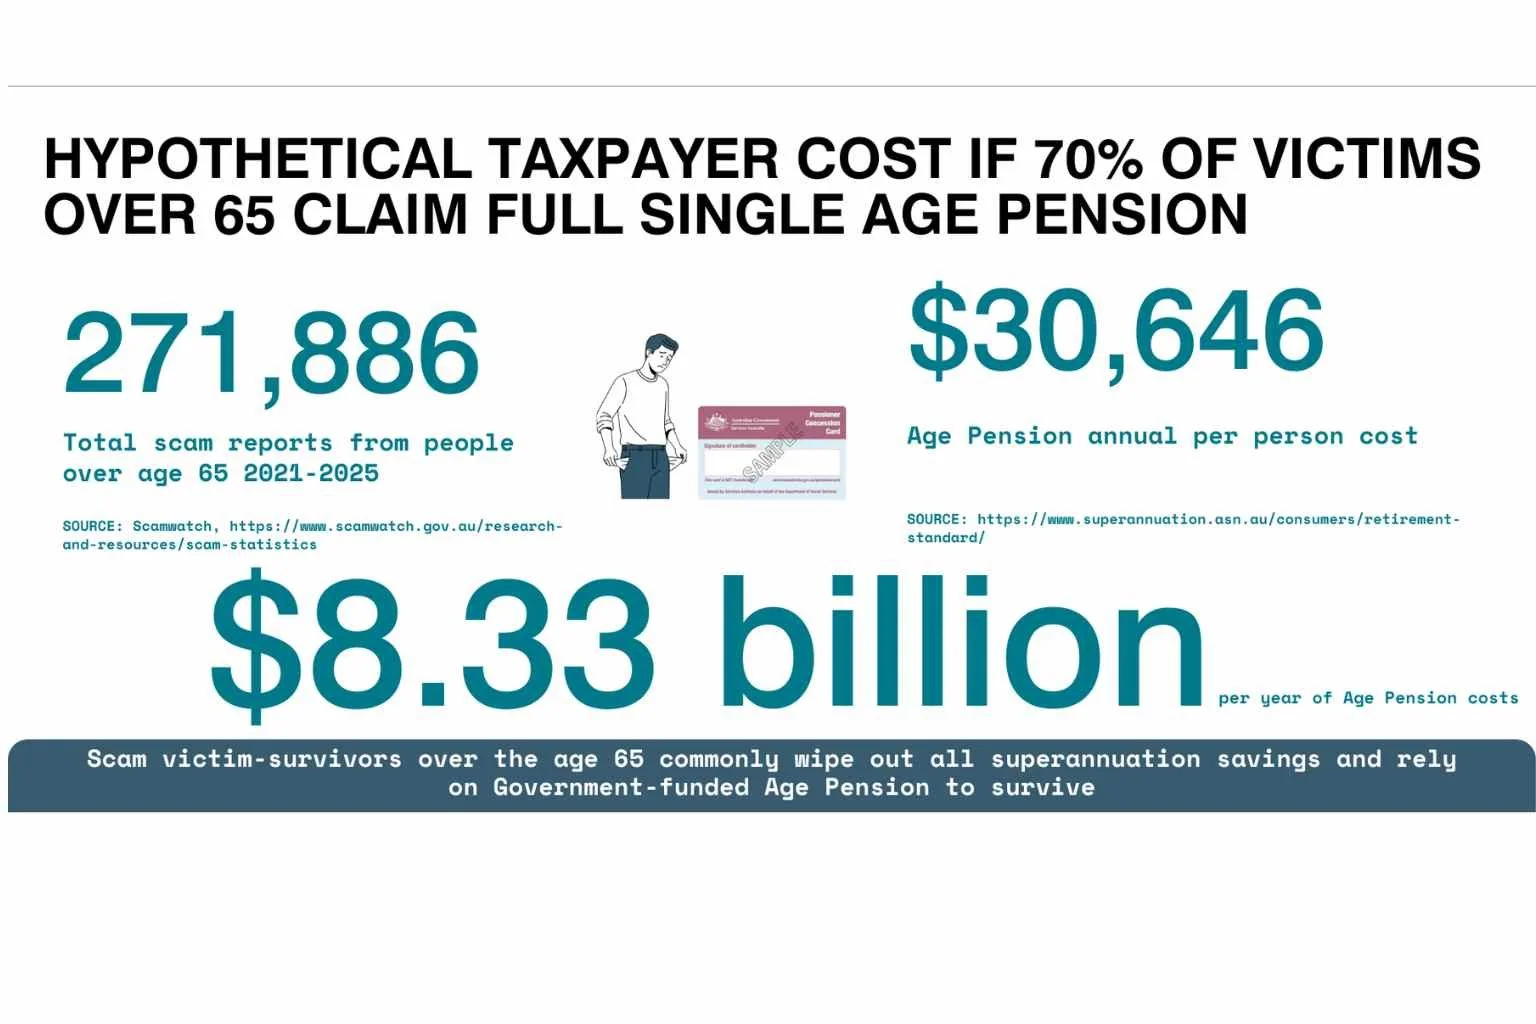
Recommendation 5. Disrupt by ensuring all telcos, digital platforms and banks have clear reimbursement, freezing and takedown obligations - backed by law enforcement
Fast, clear Internal Dispute Resolution (IDR) is the most effective way to stop scams in their tracks. When all designated corporations face a financial incentive—such as IDR up to $25,000 in reimbursement and larger penalties—they’ll act quickly to freeze and recover stolen funds. Fear of financial loss will displace the current wilful blindness, driving action desperately needed to protect victims and save taxpayers.
We believe a nationally co-ordinated approach like Australia has used to tackle road safety can be emulated to restore safety and trust to our digital economy, potentially by considering issues like:
Mandatory cybercrime insurance (like compulsory third-party insurance to register a car)
Fines and infringements issued by law enforcement to SPF entities (like speed camera or parking infringements - failure to pay results in heavier fines and criminal offences)
Education and targeted enforcement Additional ASIC levies on high risk SPF entities fund a scam hotline, with the National Anti-Scam Centre (NASC) publishing true and verified scam data that tells the public the truth about corporations’ role in scams — whether impersonated or genuine. We would also encourage public reporting of corporate investment in staff training around scams and month-by-month marketing spend.
Recommendation 6. Respond with a Royal Commission into financial crime with the 6-year common law protections to apply to receiving banks
A Royal Commission into financial crime, mule laundering and systemic failures is required to deliver accountability and lasting reform. SVA is concerned that the erosion of existing common law rights under the SPF (i.e. existing bank liability) is reduced from the pre-SPF 100% down to 50% or less if other SPF entities are involved, hence we demand the 6-year common law rule must apply.
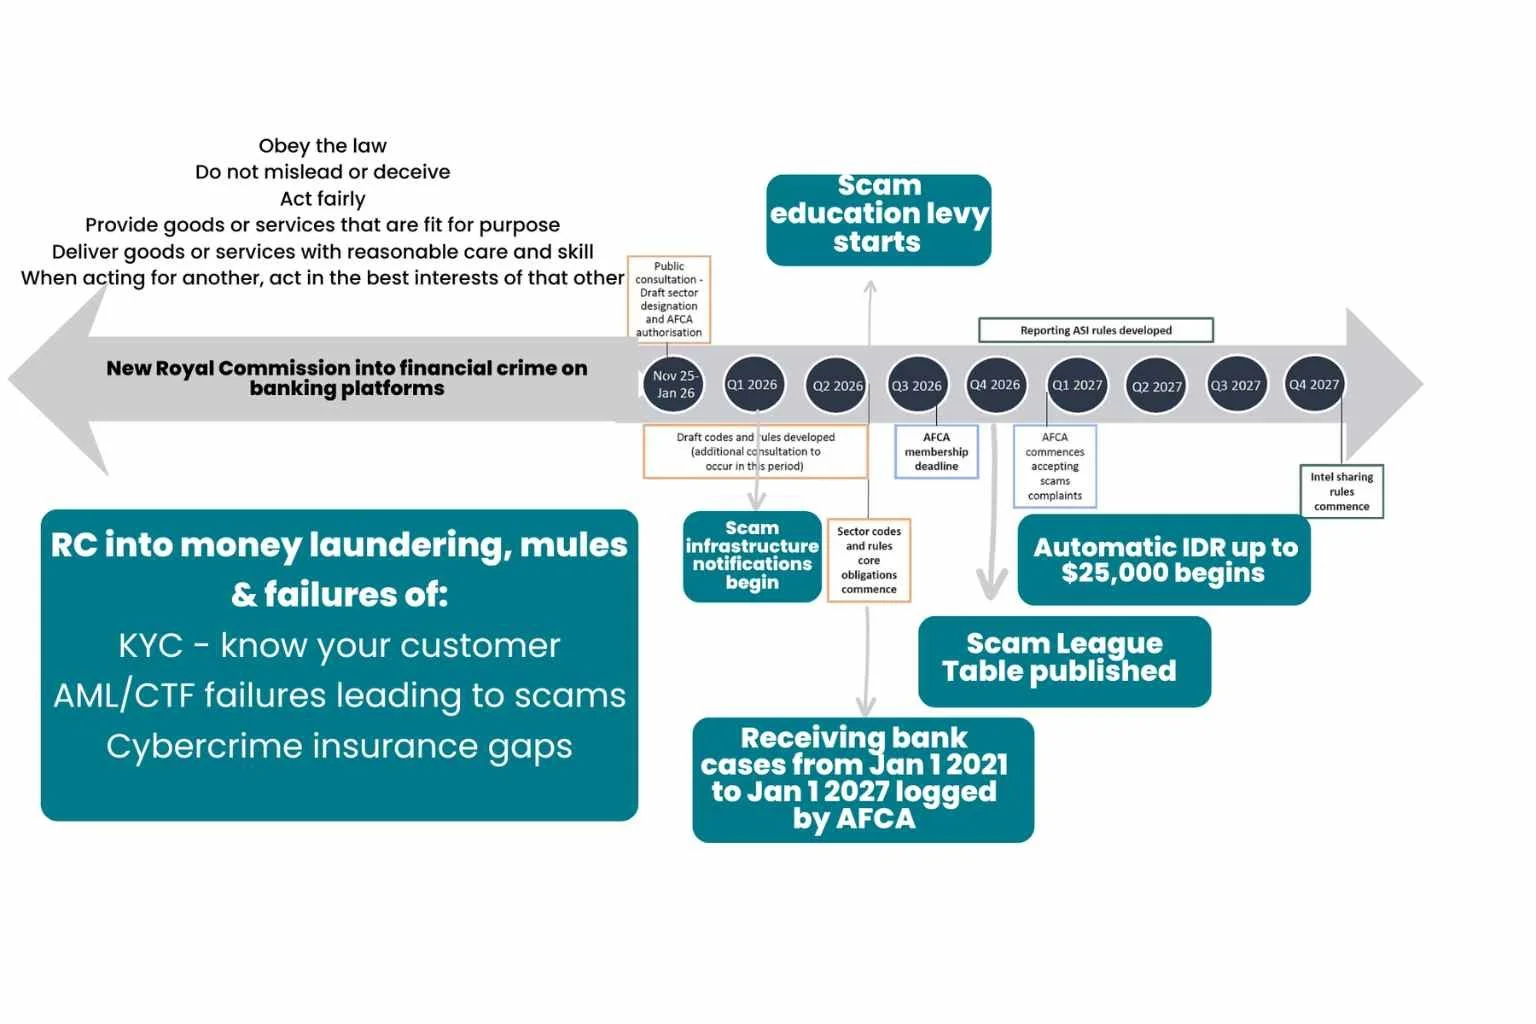
We propose a Royal Commission is necessary to investigate how financial crime has infiltrated Australian financial services with so little reimbursement to consumers.

SVA Calls for a Mandated Right to Pay in Cash to stay safe in the digital economy
Scam Victim Alliance urges Treasury to maintain cash as a protected pathway for consumers to transact safely.
With Australians losing more per person to scams than the US or UK, Scam Victim Alliance is urging the government to preserve cash access as a basic consumer protection in a broken digital economy.
We urge Treasury to view mandated cash acceptance as a critical measure to preserve consumer rights, limit harm from financial crime and uphold economic fairness
As a national network of scam victims and harm reduction advocates, we are acutely aware of the risks of our digital economy, which continues to fail Australian consumers and expose them to financial crime.
Many of our victims were trying to open a term deposit, buy a home or move or transfer their superannuation savings when they were targeted by criminals operating with impunity across Australia’s banks, digital platforms and telcos.
We urge Treasury to view mandated cash acceptance as a critical measure to preserve consumer rights, limit harm from financial crime and uphold economic fairness.
Australia needs a resilient and inclusive economy that allows cash to be accepted for essential goods and services
Digital fraud risks must be acknowledged as a driver of financial harm, with cash and cheques the only alternative for vulnerable consumers to transact safely Australians are being actively victimised by the lack of consumer protection in the digital economy, suffering higher per capita scam losses compared to the US and UK in 2023 and in 2024.
Banks and digital platforms have shifted accountability for modern fraud on to customers, rewriting their account terms and conditions to push scam liability onto customers.
Given that most of Australia’s fraud protections existed in the Cheques Act – and that cheques are being sunsetted – the right to use cash remains vital for protection from financial harm caused by lax digital and banking controls that have seen cyber-enabled crime flourish.
Many of our community members are so traumatised by their extreme financial losses that they wish to never use digital apps or online banking again.
The ePayments Code further harms consumers by actively blaming them for falling victim to a financial crime and ‘authorising’ their own loss.
Australia’s Banking Code offers more protection for consumers transacting face to face in a bank branch rather than online, which again underlines the need for broad access to cash and cheques.
• Payment misdirection fraud is the fastest growing scam type, according to the ACCC, so access to cash is a vital consumer protection.
Telcos, banks and digital platforms allow impersonation and deception with little consequence – the Scam Prevention Framework still has no codes or rules to hold corporations to account.
Banks charge interest on financial crime losses and the Australian Financial Complaints Authority endorses this . Consumers urgently need government to step up and hold a Royal Commission into the state of financial crime and money laundering across Australia’s digital economy.
Scam Victim Alliance believes the scourge of financial crime can only be addressed when the government realises the true extent of how corrupted Australia's payments system has become.
There are regulatory loopholes, rampant money laundering and profit-seeking from legitimate and illegitimate stakeholders that effectively make authorised push payment frauds legal and highly successful.
MONEY LAUNDERING ON THE STREETS OF MELBOURNE

Hope & Tom Clifford had their $250,715 property settlement money stolen in a sophisticated fraud that was set up on Snapchat with a $5000 offer to a money mule. The mule then drove around the streets of Melbourne, laundering the $250,715 by buying a gold bar, changing it into foreign currency and withdrawing cash.
Dubbo couple Hope and Tom Clifford had their $250,715 property settlement stolen by a mule with a Commonwealth Bank Account. Court documents revealed the mule was paid $5000 by malicious actors to receive the Clifford’s misdirected funds into his personal bank account, which is still operated by the mule today.
The crime gang network had also breached the Clifford’s solicitor’s email to send a forged and misdirected Commbank payment instruction to the Cliffords.
The Cliffords then went into their local NAB branch to do the payment in person. Court documents reveal the money mule was driven around Melbourne withdrawing cash from ATMs, buying foreign currency and a $94,000 gold bar with the $250,715 proceeds, which meant no money was recoverable to the Cliffords or their bank.
The mule received just 150 hours community service, with no conviction recorded. The justice system did not force a recovery or compensation order on to the mule.
No other people were arrested. This level of on-shore money laundering reveals the need for a whole-of-society approach to fighting financial crime.
The initial misdirected payment happened inside a NAB bank branch, while NAB was engaged in an enforceable undertaking with AUSTRAC to prevent money laundering.
• Digital fraud is a daily threat, not a fringe issue In this context, cash is not just a payment method—it's a tool of financial autonomy.
It is the only payment form that cannot be hacked, reversed, profiled, or denied by an algorithm. Mandated cash acceptance is one way for consumers to avoid the cybersecurity risks of online transactions.
APRA’s stakeholder survey reveals 91 per cent of banks, insurers and super funds describe cyber risks as critical or high risk, yet consumers often have no choice but to use it.
The government's own data confirms that scam losses are rising, and digital systems are failing to prevent it.
Maintaining cash access is a practical safeguard for individuals who have been, or may become, financial crime victims.
People victimised by romance and investment fraud often have their digital financial identity compromised and become unwitting money mules — including hacked bank accounts, drained savings, and flagged bank transactions.
In the aftermath of their fraud, their online banking can be locked or put under investigation. Some of these people are also ‘debanked’ and not allowed to operate accounts again. Many are too traumatised to trust digital payment systems again.
Cash becomes romance and investment fraud victims' only safe and immediate way to:
• Regain financial control without relying on compromised accounts
• Pay for essentials like food, transport, and accommodation during recovery
• Avoid re-traumatisation from using the same digital channels where the abuse occurred
• Protect privacy and limit further surveillance or manipulation from perpetrators, especially in cases involving coercive control.
2. The cash mandate must apply to all essential goods and services
Limiting cash acceptance to fuel and groceries will exclude key essentials that people rely on to live, including:
• Medicines and pharmacy items
• Rent and housing costs
• Utilities (electricity, gas, water)
• Public transport and essential travel
• Telecommunications (phones and internet)
This is not a theoretical issue. Many Australians - especially older people, regional residents, people with disabilities, and financially excluded groups - are being left behind in the digital economy.
A narrow cash mandate creates loopholes that accelerate digital coercion and economic control by institutions, who continue to profit by turning a blind eye to financial crime on their platforms.
We urge Treasury to require cash acceptance for all essential transactions to ensure consumer protections.
IAN WILLIAMS: A CASE STUDY AS TO WHY CASH IS VITAL FOR VULNERABLE AUSTRALIANS
Pensioner Ian Williams was scammed $1300 from his Google Pay Ubank account, operated by NAB.
His bank – and the Australian Financial Complaints Authority - blamed him for the fraud, even though he had CCTV footage showing criminals buying gift cards with his card, more than 100km from where he was located at the time of the payment.
Ian has been in a two-year+ fight self-representing himself at court to seek justice. His health has suffered.
As a consequence of the trauma and financial cost, he now refuses to transact digitally. He relies on cash to participate in the economy.
“My money is not safe in the bank, and if there is an issue, I will be blamed. If I have cash on me, I have control of it," he says.
“In the bank I have no control over my transactions, no security, no support.”
Ian contends the bank has still not given an adequate reason as to how his $1300 was taken from his account, only accusing him of being responsible for it.
3. The $500 cash limit is unreasonably low if we want to be prepared for natural disasters or cyber outages
Many essential costs exceed $500, including:
• Rental bond payments
• Quarterly utility bills
• Essential car repairs
• Bulk groceries or fuel purchases for remote travel
A $500 ceiling effectively blocks consumers from using cash in situations where it matters most.
If there is concern about abuse (e.g. large-scale money laundering), exceptions can be carved out — but the default must support high-value essential cash payments, with monitoring.
This is the approach Minister Tony Burke has outlined for monitoring crypto ATMs .
Reserve Bank Governor Michelle Bullock has acknowledged how essential cash is – even though just 10 per cent of economic transactions are done with it – and confirms that it must be available as a back up when digital systems are unavailable (such as in a natural disaster, digital outages or a cyber attack on vital infrastructure).
4. Retailer cash exemption pathways are too wide
The current proposal seems to allow the ACCC to exempt entire retail chains or site classes from holding cash.
It also exempts all businesses under $10 million turnover, including many mid-sized regional retailers. In practice, this means a regional town may have zero cash acceptance points for essentials, even where local demand is strong.
The proposed regulatory design prioritises operational comfort for retailers over the public interest.
We recommend:
• Narrowing the small business exemption to <$1 million turnover
• Requiring transparent public reporting of all exemptions granted by the ACCC.
Cash acceptance cannot become optional based on the subjective operational preferences of corporations.
5. Supermarkets and large chains must maintain meaningful cash capacity
While we welcome the "reasonable opportunity" language in the draft, it is vague and easily undermined in practice.
We already hear from victims who face:
• Long queues at the only staffed register
• "Card-only" signage at self-checkouts
• Staff discouraging cash through misinformation or passive barriers
To avoid these abuses, we recommend:
• Requiring at least 50% of payment terminals at large retailers to accept cash
• Prohibiting signage that discourages or misrepresents cash acceptance
• Mandating staff training to support compliance with money laundering laws
Cash acceptance must be functional and practical, not just technically present.
6. The cash mandate must be monitored and enforced
Regulation without enforcement invites exploitation.
Treasury must ensure:
• Clear reporting obligations for retailers
• A consumer complaint mechanism for breaches
• Published penalties and compliance data to build trust
The proposed 6-month grace period should be shortened or phased with public progress reporting to ensure momentum is not lost.
The right to use cash must not be quietly eroded through neglect, loopholes, or economic exclusion.
If Australians cannot rely on digital systems to protect them — and current scam statistics show they cannot — then the government must protect the option to pay safely with cash.
We urge Treasury to strengthen the draft regulations by:
• Expanding the mandate to all essentials
• Lifting the cash transaction ceiling
• Tightening exemptions
• Enforcing real-world compliance
• Releasing the codes and rules that support the Scam Prevention Framework
We urge the federal government and its regulated agencies to work harder with financial institutions and groups such as ours to stamp out blatant money laundering and financial crime across the Australian system.
Digital dependence does not deliver economic resilience or justice.
Cash is one pathway for consumers to remain protected while transacting in the economy given the appalling lack of consumer protections for people being robbed through their bank accounts in Australia.
The Scam Victim Alliance stands ready to work with government to protect the economic dignity and security of all Australians.
Scam Survivors Urge Lawmakers to Close Loopholes in Australia’s Crypto Bill
Scam Victim Alliance urges Treasury to mandate reimbursement, fund asset recovery, and expand crypto regulation, warning that reform without restitution fails victims and emboldens financial criminals.
Scam Victim Alliance urges Treasury to mandate reimbursement, fund asset recovery, and expand crypto regulation, warning that reform without restitution fails victims and emboldens financial criminals.
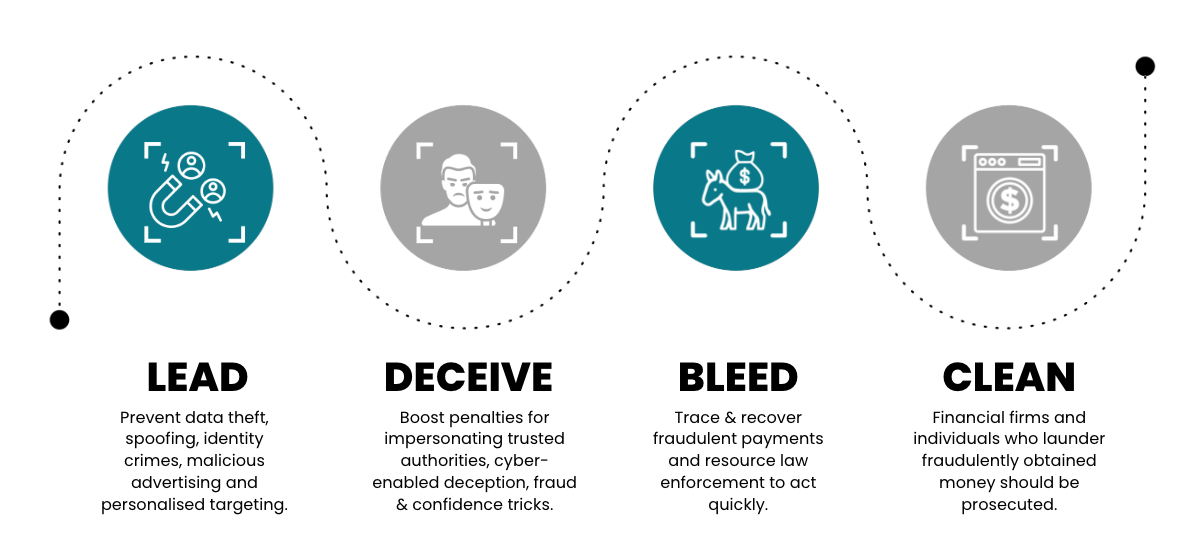
All scams - whether they relate to crypto or not - follow these four patterns.
Submission: Feedback on the Treasury Laws Amendment (Regulating Digital Asset, and Tokenised Custody, Platforms) Bill 2025
Scam Victim Alliance a group of cyber-enabled fraud and money laundering victims with lived experience of the harm that Australia’s financial system unwittingly inflicts on everyday Australians trying to pay, transact or invest in assets to secure their future.
We welcome the Australian Government’s initiative to modernise the regulatory framework for digital asset platforms and tokenised custody platforms, as set out in the Exposure Draft Bill, Explanatory Memorandum, Fact Sheet, and Consultation Questions.
The policy intent - to enhance consumer protection, close regulatory gaps, and align with international “same activity, same risk, same regulation” principles - is sound. However, we draw attention to glaring omissions in consumer restitution and recovery of lost or stolen digital assets.
1. Regulation Must Include Protection and Reimbursement
If the government wants to regulate digital assets as financial products, it must also ensure these assets have the same regulatory protection as money and securities in the traditional financial system.
While the Bill applies general obligations to licensees (such as acting efficiently, honestly, and fairly, and maintaining adequate compensation arrangements), this does not go far enough.
A reimbursement and recovery mechanism must be explicitly included in the law, especially for retail consumers who suffer loss due to:
• cyber-enabled deception that deceives retail end users;
• platform insolvency,
• fraud and theft,
• operational failure or hacking, or
• negligence, theft or fraud by licensed intermediaries.
Regulation without restitution will leave consumers unprotected in the very situations that prompted this reform.
The history of banking regulation in Australia shows that without mandatory reimbursement (for example, when victims of authorised push payment fraud are left uncompensated), institutions will always prioritise commercial interest over consumer recovery.
The Australian Payments System Review in 2021 rightly pointed out how rife fraud, trickery and deception is amongst tokens, digital asset platforms and tokenized custody platforms and it’s our lived experience that this has escalated dramatically since 2021.
We regularly hear horrific stories of harm where people believe they are ‘investing’ or ‘trading’ only to have their life savings hijacked by financial criminals. These victims are then commonly de-banked by the traditional financial system, losing access to the vital accounts needed to rebuild and recover after such devastating experiences.
Financial crime is a complex global issue which we believe can be more effectively tackled domestically by improving law enforcement and regulatory outcomes across four main pillars.
2. The Government and Law Enforcement Must Leverage Crypto Traceability Tools and Law Enforcement Must Be Resourced to Recover Assets from Overseas
Unlike fiat or traditional money, digital assets are inherently traceable.
Modern blockchain forensics tools allow rapid identification of wallet addresses, asset movement, and ownership patterns. The government should therefore:
• establish a dedicated crypto tracing and recovery taskforce jointly operated by Treasury, ASIC, AUSTRAC, and the AFP with adequate resourcing to fund international recovery;
• empower regulated exchanges and wallet providers to comply with asset-freezing and restitution orders; and
• require reporting and cooperation frameworks between exchanges and law enforcement.
This would ensure that regulation does not merely impose compliance costs but also provides meaningful remedies for victims. Like the way Australian Financial Complaints Authority funding works, these protections could be funded by levies on larger financial firm profits rather than a direct levy on a flourishing startup industry. The funding could also be tied to the loss amounts sending financial firms lose to financial crime each year, ensuring that the firms with the most power to reduce crime invest to prevent it.
3. Protection Must Extend Beyond Centralised Exchanges
The consultation papers correctly note that major losses have occurred because custodial intermediaries hold assets without adequate segregation or protection.
However, the regulatory perimeter should also consider:
• Hot and cold wallet storage (both institutional and private),
• Tokenised asset custody outside exchange environments,
• Decentralised or hybrid custodial services, and
• Cross-border platforms that service Australian consumers but operate offshore.
Without addressing these, consumer protections will remain incomplete and inconsistent.
We also believe the issue of crypto ATM machines in publicly available areas needs to be examined, as these can become hotspots for financial crime victims being duped and deceived into becoming unwitting money mules.
We support Treasury and law enforcement actions to scrutinise the cash-to-crypto and deception-to-crime pipelines to actively prevent financial crime being committed on Australian territory. We believe financial crime can be more easily thwarted by focussing law enforcement efforts
4. A Statutory Consumer Reimbursement Scheme
A reimbursement mechanism, similar to the UK’s mandatory fraud reimbursement scheme should be established for digital asset transactions.
This scheme should:
• require regulated platforms to contribute to a consumer protection fund,
• guarantee reimbursement to small business and consumers for verified cases of loss due to platform failure or unauthorised transactions, and
• ensure rapid resolution through AFCA or a new equivalent statutory body, such as a Payment Systems Regulator.
This would close the gap between financial regulation and consumer outcomes, ensuring the regime truly delivers “same risk, same protection.”
Banks refused to help, Australian crypto platform did. Consumer-centric reform that reimburses
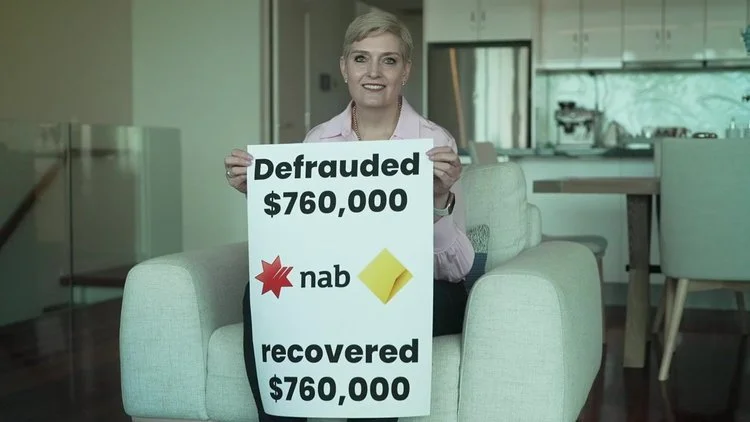
Australia should support a globally competitive tokenised custody and digital asset platform industry. This vision will not be realised if the sector is dominated by a handful of established financial institutions that suppress innovation to develop secure and decentralised financial services.
While we support major banks taking action to limit high-risk crypto transactions under the banner of consumer protection , we must also call out the double standard evident in the case of Scam Victim Alliance supporter Jacomi Du Preez , who lost $760,000 to a sophisticated bank impersonation fraud.
Jacomi had received a life insurance payout following the death of her husband and sought to place the funds in a term deposit. She approached both Commonwealth Bank and National Australia Bank, asking them to verify the legitimacy of the Macquarie Bank term deposit platform she was directed to. Both banks declined, telling her it was her own responsibility.
After realising she had been scammed, Jacomi contacted a friend in Treasury, which helped trace the funds from the banks to various recipients. She was not provided with visibility into who controlled the platforms that received her money, but she independently contacted the platforms to report the fraud.
In a remarkable act of integrity, Elbaite, an Australian digital asset platform that held a portion of the stolen funds, returned the money after Jacomi reached out. According to her, CEO Morty Tollo personally responded and refunded the full amount without delay.
As a survivor-led organisation, we commend Elbaite’s victim-first response, which stands in stark contrast to the lack of proactive support from major banks. This case illustrates that emerging digital platforms can, and do, demonstrate leadership in protecting consumers—often better than traditional financial institutions.
We urge regulators to ensure that all participants in the financial ecosystem are held to the same standards, and that the regulatory environment fosters innovation, fairness, and accountability—not protectionism.
Consumer outcomes must be the primary focus. Regulatory frameworks should not serve to entrench monopolies or prioritise the interests of powerful lobby groups at the expense of safer, more innovative solutions.
Every financial crime victim deserves to know:
• Where their money went,
• Which platforms received it, and
• For law enforcement to pursue the offenders
• For law enforcement to be incentivised to respond to these crimes by allowing them fast access to the required transaction information and strong enough laws to prosecute offenders.
We strongly support increased funding for law enforcement to trace and recover stolen funds and digital assets—no matter the platform or jurisdiction involved.
5. Alignment with the Original Intent of Digital Assets
It is important to recognise that the purpose of cryptocurrencies and digital assets was to decentralise financial control and reduce dependence on traditional banks and governments.
If the government seeks to regulate this space, it must do so without replicating the same systemic failures seen in banking—particularly the lack of accountability for consumer loss and slow response to fraud.
We believe the government has a responsibility to fund law enforcement – or law reform – to strengthen that ability to control individuals, digital asset platforms and financial firms in Australian territories who:
• Perpetrate or encourage others to perpetrate cyber-deception, impersonation, identity crimes, privacy breaches, email theft, mail theft, spoofing and other pre-transaction financial crimes
• Recruit money mules and commit identity fraud, spoofing, digital deception and other acts that lay the groundwork for modern push payment fraud
• Fail to release timely information to law enforcement when a crime has been reported.
Summary of SVA Recommendations
1. Include a statutory reimbursement and recovery framework within the Bill for losses incurred through licensed platforms.
2. Establish a national crypto asset recovery and trace unit within Treasury/ASIC/AUSTRAC which is funded to pursue active recovery of assets.
3. Mandate cooperation between regulated exchanges, custodians, and law enforcement for tracing and restitution.
4. Expand coverage to include hot/cold wallets and cross-border custody arrangements.
5. Ensure retail consumer protection parity with traditional finance.
6. Examine cheap and effective ways to bolster law enforcement’s ability to respond to financial crime.
7. Look at the issue of ‘de-banking’ crypto-related financial crime victims from traditional financial firms like banks – strengthen the chain of custody on payments to eradicate crime and identify perpetrators.
The proposed framework is a crucial step forward. However, to build public trust and deliver true consumer safety, regulation must come with protection.
Australians must not face the same gaps in accountability and restitution that currently exist in the banking system.
Thank you for considering our submission.
Sincerely,
Harriet Spring
President

Survivors Call for Fraud-Proof Payment Reform
The Scam Victim Alliance submission to the Reserve Bank
Scam Victim Alliance (SVA) is a not-for-profit organization of survivors with lived experience of scams and cyber-enabled fraud. We welcome the opportunity to provide this submission to the Reserve Bank’s (RBA’s) call for submissions2 on Merchant Card payment costs and surcharging.
We believe Australia’s payment system must be safe by design and come at as little cost as possible to consumers, who drive the engine of our economy. Fraud in instant payments is 10x higher3 than regular credit transfers and despite claims by card schemes they are ‘secure’, PayDay News reports payment fraud as a $1b problem4.
Cyber-enabled deceptions are rampant across payment systems with victims increasingly being deceived into initiating payment. We urge the Reserve Bank to consider this rising fraud problem – particularly business email compromise and ghost tapping issues – as it considers submissions for card payments and surcharging.
Efficiency and competition in payments must not come at the cost of consumer vulnerability to global transnational scamming. Interpol has called financial crime a global crisis5. We believe Australia is losing more per capita than comparable nations ($74 per head in 2024 compared to the UK’s $36 per head) to deception and organised scams. We ask the RBA to be aware that Australia's payment and financial systems need industry regulation and controls to stop this scourge. Right now, corporations deny all liability and make victims bear the cost. This is not acceptable when people pay surcharges to participate in the digital payments system.
Surge in card-not-present payments: GHOST TAPPING & OTHER FRAUD MUST BE ADDRESSED
A payment type of high concern is ‘ghost tapping’6, where Google Pay and Apply Wallets are mysteriously used by fraudsters. Financial institutions and the Australian Financial Complaints Authority lay the blame for these frauds at the consumer, who do deliver informed consent to these transactions, yet wear the cost.
A community member with a Commonwealth Bank-linked Google Pay wallet experienced more than 20 fraudulent payments, 5 card replacements and losses greater than $10,000. He was never told how the compromise occurred, only that “he released the codes and authorised the payments”. No evidence was provided by his bank, yet determination 12-00-1102187 makes him liable.
Another community member Ian Williams7i experienced the same Google Pay issue, yet had police evidence to prove other criminals made the transactions that his bank NAB said he authorised. He has represented himself in court to fight this matter to hold powerful corporations to account.
We support the RBA’s reform direction and request a focus on real-time fraud risks, safety transparency, and shared accountability across all actors in the payments ecosystem to better manage fraud.
Surcharging can serve as a friction point that prompts consumers to pause and verify the payment process, which is a crucial safety feature in digital payment environments.
SVA urges the RBA to weigh payment safety as an equal pillar alongside competition and efficiency. Simpler, safer, and more transparent payment processes and costs should be prioritised for consumers, including things like:
First-time payment holds (enabling fraudulent payments to be easily recalled)
Certain high risk payments such as superannnuation, property or purchases for large items like cars or renovations should have risk scoring and opt-in payment delays.
We believe innovation in fraud protection must be a consideration in any regulation to ensure fast-changing payment frauds can be disrupted by industry, who should bear the cost rather than push liability on to consumers.
We ask that any savings from payment surcharges are reinvested into consumer safety mechanisms, such as those listed above. We support any move that shifts incentives toward fraud prevention and helps institutions and payment providers make the digital economy safer.
We would also suggest global payment giants be required to align with Australian standards and participate in domestic scam prevention data sharing. We support phased implementation to reforms, but strongly urge scam mitigation measures be fast-tracked given the extent of losses being experienced by Australians.
Consumers deserve to know how their payment service providers rank in preventing scams and believe they should be required to report scam incident rates, funds recovered and risk mitigation practices.
We would like financial payment providers – or government – to develop an industry-wide Payment Safety Scorecard, similar to energy efficiency ratings, that genuinely help consumers reward corporations and payment providers that prevent financial crime and scams.
In conclusion, we would like to see Australia's payment systems do more to protect consumers from scams and financial crime. While innovations like real-time payments offer convenience, they also accelerate the fraud cycle, leaving victims little recourse. Scam Victim Alliance (SVA) welcomes the Safety by Design (SbD) principles outlined in AusPayNet’s July 2025 report, and we urge regulators and industry stakeholders to consider mandatory frameworks to protect people.
The transformation of Australia’s payment infrastructure must be built on trust, safety, and accountability. Technology has enabled sophisticated scams; now, it must be used to stop them. Survivor-led design, embedded safety features, and system-wide transparency can prevent life-altering financial losses. We welcome the opportunity for ongoing open dialogue and look forward to constructive reform to reduce the harm Australian scam victims experience.

Economic reform roundtable submission
The Scam Victim Alliance advocates for 5 key reforms to reduce the financial and emotional harm experienced by Australians who fall victim to cyber-enabled deceptions and crime.

Financial crime is a severe handbrake on productivity
The Scam Victim Alliance (SVA) is a not-for-profit community of survivors of cyber-enabled fraud and scams. We welcome any chance to contribute to the Economic Reform Roundtable and urge the federal government to consider the deep damage that scams and fraud inflict on financial wellness and productivity. Australia reported scam losses per capita were more than double those of the United Kingdom in 2024 and higher again in 2023.
Behind each statistic is a person, who commonly experiences shame, humiliation and long-term financial distress. Australian scam victims receive between 2 to 5% reimbursement, which increases marginally to 10% if victims complain to the Australian Financial Complaints Authority, where they undergo significantly elevated harm and are blamed for their scam.
Interpol, Amnesty and Operation Shamrock explain that transnational crime syndicates are behind the escalation in financial crime around the world. In 2023, scams took 0.11% of Australia’s GDP in reported losses. One UK fraud expert told our group “Australia is the number one fraud target in the world”, with professional scam compounds increasing the desks they devote to scamming Australians, who are considered trusting and wealthy by global standards.
Every scam - whether romance, investment, phishing, SMS or otherwise - depends on two key enablers:
1. The deception or impersonation of a trusted entity (or entities);
and
2. Money laundering to rinse the origin of scammed funds ‘clean’ to avoid being recovered by law enforcement or financial institutions.
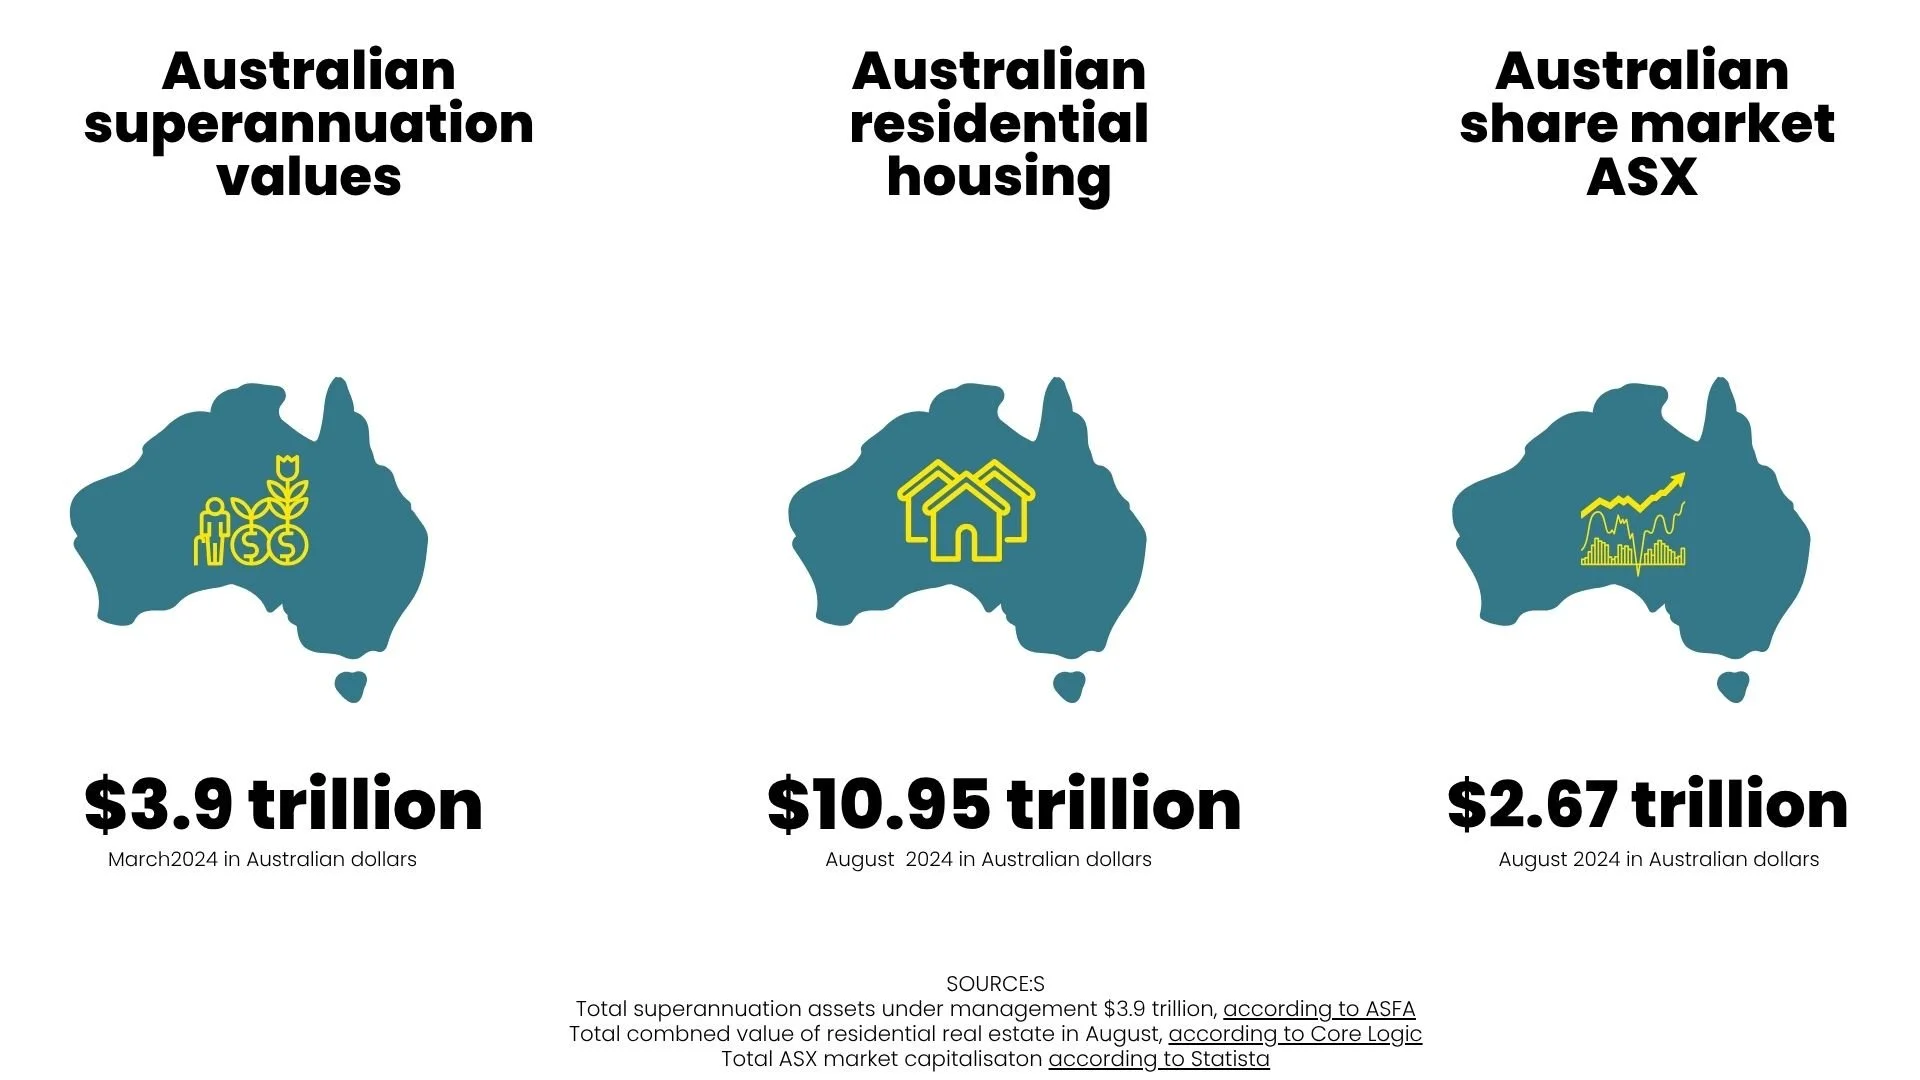
None of this is in the national interest. Ignoring the epidemic of global scamming is not fiscally responsible in a cost-of-living crisis. Nor does it strengthen Australia’s budget sustainability. And with the rapidly increasing sophistication of Artificial Intelligence (AI), the situation will likely worsen without urgent legislation and regulatory changes.
Considering this, we offer the following recommendations for meaningful reform. Every Australian age group - from young to old – loses large amounts of money to scams. As a group with lived experience of navigating Australia’s broken system, we propose:
1. Government-led digital identity
Australia urgently needs a national digital identity framework that is resilient to fraud and impervious to criminal misuse. Public trust in government agencies and institutions is eroded when identities on banks, social media, email, the open web, telecom messages and calls can be impersonated with ease. Edelman’s 2025 Trust Barometer reveals Australians’ trust in governments and institutions is currently at an all-time low.
2. Create an economy-wide KYC Framework and better privacy
Know Your Customer (KYC) processes must be unified across banks, telcos, digital platforms, and financial service providers. Current fragmentation fuels risk and asks people to share their data across multiple platforms. Australia’s largest corporations have breached personal data - from Qantas to Medibank to Optus - and scammers wash the leaked data together to build profiles that are then targeted for scams and frauds.
3. Criminalise money laundering as integral to fraud-fighting
Fraud and money laundering are inseparable crimes. Stronger enforcement and clarity in law -mirroring reforms proposed under the AML/CTF regime - are essential to prevent stolen funds from flowing from Automatic Teller Machines into foreign currency, gold bars, crypto ATMs and other onshore and offshore ‘placement and layering’. State and federal law enforcement must have more power to use criminal justice laws. We also recommend increased transparency for scam victims to learn whether their stolen money is funding the crimes against humanity seen in overseas-based scam compounds.
4. Reform regulatory and law enforcement capacity
Australia’s current regulatory frameworks have failed to keep pace with cyber-enabled financial crime. Nationally harmonised laws - like the Australian Consumer Law - could empower agencies to act faster, more consistently, and at lower cost to taxpayers. We need to simplify the state-funded burdens these crimes are putting on our taxpayer-funded resources, which are currently inadequate and unsuccessful at delivering justice or restitution.
5. Require cybercrime insurance as a condition of housing incentives
The horrifying rise of real estate and home buyer scams, particularly through Business Email Compromise, demands immediate response. No financial institution offering federally subsidised housing loans should be allowed to operate without insuring consumers against cyber fraud. Many banks are profiting by charging interest on scammed losses and will have no incentive to change without government action.
6. Fund trauma-informed support for scam victims
The human cost of scams is not just financial. Dedicated mental health and trauma support services must be made available - beyond Medicare - to help victims recover and re-engage with the economy. We have many victims who can no longer function the way they once did. The scam is the first problem - it’s navigating justice (or the lack of it) and the devastating financial consequences that most victims report as debilitating.
7. Cut through the red tape nightmare to improve Scam Prevention Framework
While the proposed Scam Prevention Framework is a step in the right direction, in its current form it risks creating a bureaucratic nightmare - overburdening government agencies and traumatising victims, and clogging up courts with costly, time-consuming disputes.
Instead, the framework should be reworked to adopt key elements of the UK’s reimbursement model, which shifts responsibility onto the private sector - where the capacity and incentives to drive efficient, innovative solutions already exist. In the UK, this has reduced fraud by comparison to other wealthy scam-targeted countries. Mandatory reimbursement has not created the ‘honeypot’ that lobby groups have falsely claimed.
Rather than layering-on complex regulation that still forces justice on a case-by-case basis which is difficult and expensive to enforce, we need a smarter approach. We need banks, telcos and platforms to do better, not just the bare minimum. A well-designed “carrot and stick” model would encourage these industries to invest in fraud prevention and customer protection, rather than the current regime that encourages a race to the bottom with AFCA trying to pick up the pieces of each individual case.
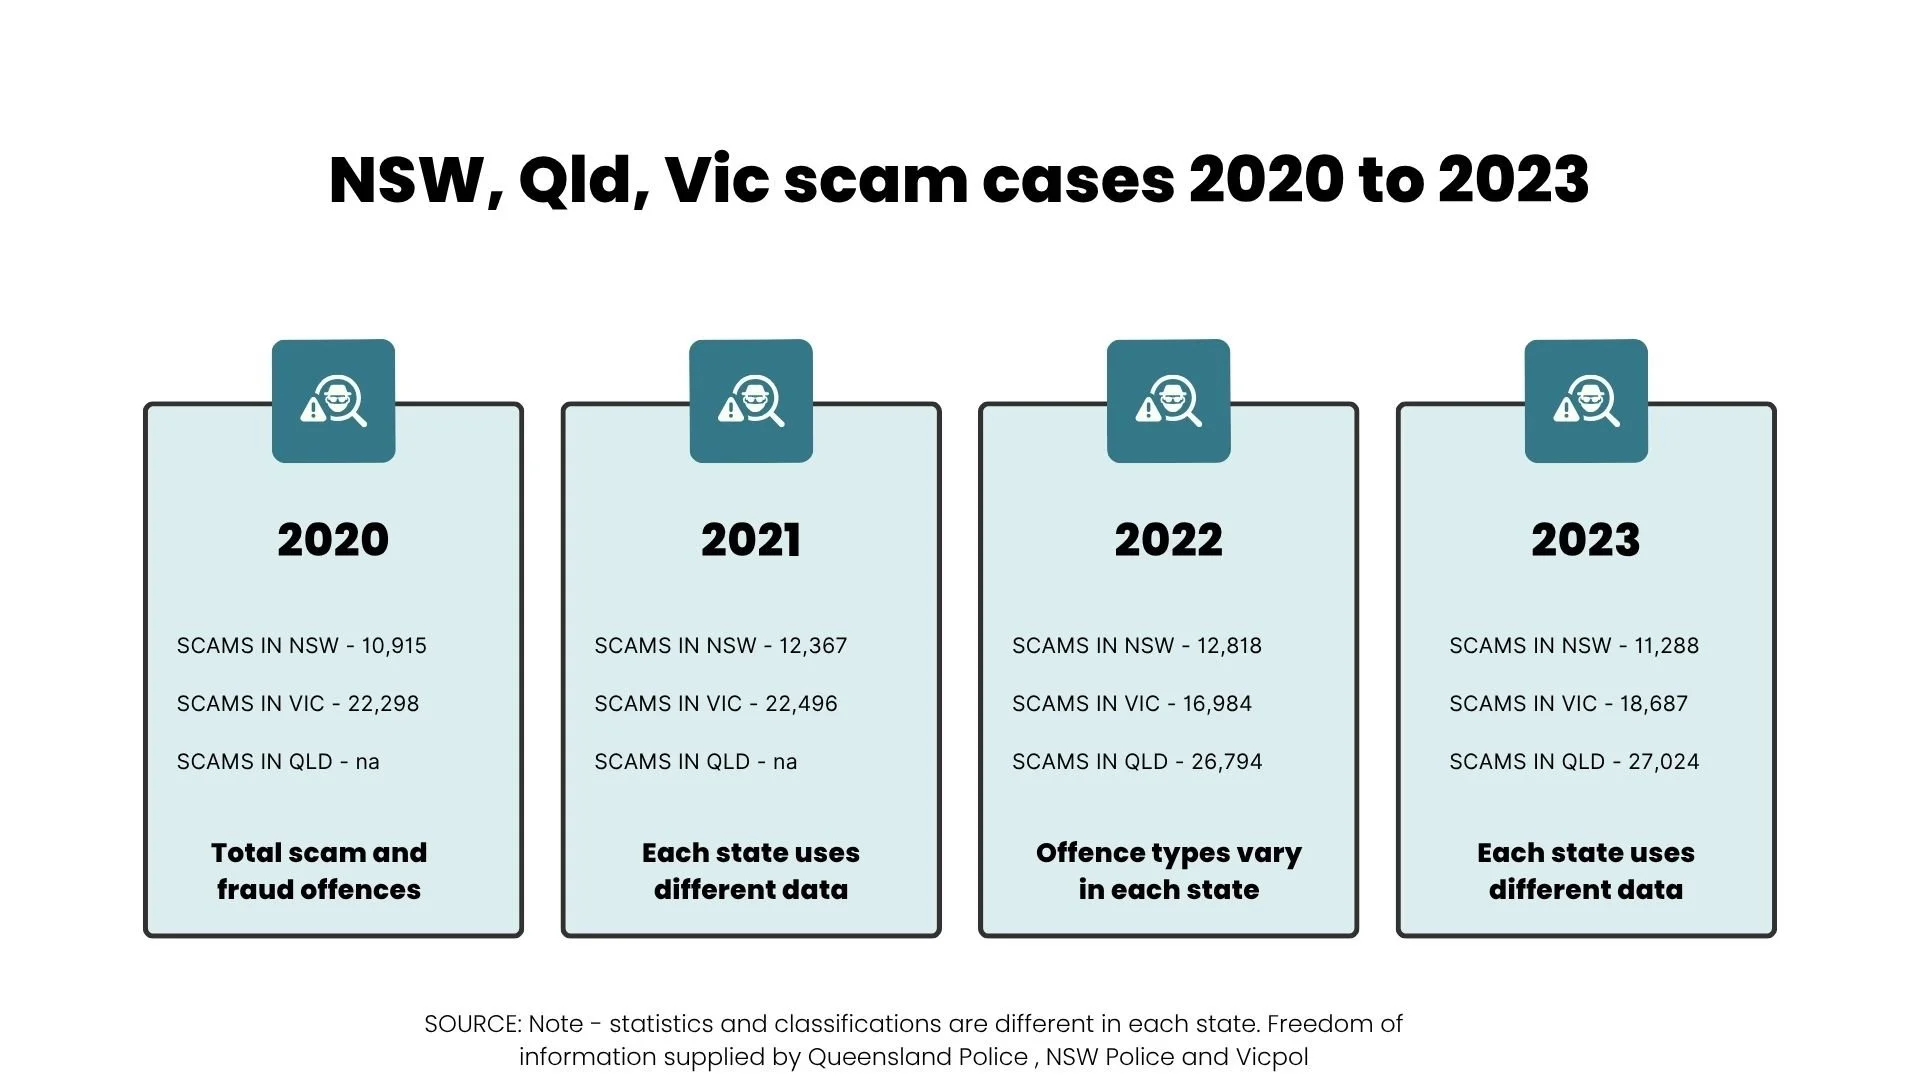
Scams are a hidden productivity crisis
Scams are not just a consumer protection issue; they are an economic emergency. Scamwatch reported $2 billion in losses in 2024, with Consumer Action Law Centre saying 30% of victims do not report their losses. We believe the under-reporting is much higher. Scammed money could be better utilised to invest in homes, businesses, and community life.
As more Australians are defrauded, money is siphoned offshore, often into the hands of international crime syndicates. This weakens our tax base, limits our ability to fund services, and undermines long-term productivity.

The UK has acknowledged this. Its Attorney General recently argued that fighting fraud is essential “to kickstart economic growth.” Australia must do the same.
Addressing scams by improving identity systems, harmonising enforcement, and protecting victims will rebuild public trust and immediately enhance productivity. Every dollar that stays in our legitimate economy strengthens it.
Our submission speaks directly to the Roundtable’s goal of creating a more dynamic and resilient economy. We advocate that:
• Addressing scams is a prerequisite for sustainable economic growth.
• Plugging the holes that allow financial crime to thrive will preserve capital, restore confidence in institutions, and support households and businesses in a rapidly digitising economy.
• Strengthening identity systems, harmonising regulation, and enforcing accountability will make Australia safer for innovation, accelerate the adoption of trusted digital tools, and free up resources that can be invested in the net zero transformation, skills development, and more efficient service delivery.
For every dollar we protect from fraud, we gain productivity, trust, and the opportunity to invest in a stronger future. We are eager to engage further and share survivor-led insights that can shape a safer and more trustworthy financial system.
Thank you for considering our submission.
Sincerely,
Harriet Spring
President
Scam Victim Alliance
AUSTRAC money laundering submission from SVA
SVA advocates for scam victims to be able to check that AUSTRAC has received an appropriate suspicious matter report from their financial institution if they’ve been the victim of financial crime or money laundering
Scam Victim Alliance (SVA) is a not-for-profit organisation of survivors with lived experience of scams and cyber-enabled fraud. We welcome the opportunity to provide feedback on the Second Exposure Draft of the Anti-Money Laundering and Counter-Terrorism Financing Rules 2025. The reforms proposed are a significant step forward in strengthening Australia’s AML/CTF regulatory regime.
The aim of this submission is to:
Stop scam and fraud victims bearing the financial cost of the $2+ billion lost to scams, the majority of which involve money laundering in Australia.
Increase the trust of the Australian public in the Australian financial system and AUSTRAC in particular through increased transparency.
The draft rules do not yet go far enough to address critical gaps in consumer protection, institutional accountability, and regulatory transparency. The AML/CTF framework must not only detect and deter crime, but also protect victims and hold negligent institutions accountable.
In relation to the proposed AML/CTF changes, the SVA:
Supports mandatory reimbursement of victims where financial institutions failed in their AML/CTF obligations. We recommend amending the AML/CTF Rules to require mandatory reimbursement where a financial institution’s breach of AML obligations materially enabled the commission of a financial crime;
Supports enforceable and public penalties for institutions facilitating or enabling financial crime. We recommend introducing a structured penalty regime and require AUSTRAC to publicly list all enforcement actions with plain-English summaries of the breach and penalties issued;
Supports greater transparency by AUSTRAC regarding AML/CTF breaches, investigations, and penalties. We recommend AUSTRAC being subject to legislated requirements to release annual data on suspicious reports, breaches, investigations, and penalties, including sectoral risk trends and redacted breach summaries to support public oversight;
Supports penalties for entities providing designated financial services without being registered with AUSTRAC. We recommend that the AML/CTF Rules be amended to clearly empower AUSTRAC to:
Investigate and fine entities offering designated services without registration;
Publish enforcement outcomes;
Proactively monitor for compliance breaches by non-registered operators.
Supports tightening registration standards for Remittance and Virtual Asset Service Providers. Registration alone is not enough. In fact, in some cases, registration can give false legitimacy to scam operations, especially among Remittance Service Providers (RSPs) and Virtual Asset Service Providers (VASPs).
It is important that we strengthen systemic risks and consumer safety at a structural level.
AUSTRAC’s updates in the Second Exposure Draft mark commendable progress. However, to strengthen Australia’s AML/CTF framework further, AUSTRAC must:
Enhanced Suspicious Matter Reporting (SMR) tailored to scams;
Prioritise victim protection;
Enforce accountability and transparency;
Provide public transparency of AML/CTF Enforcement and Reporting;
Actively and transparently penalise unregistered and negligent actors, including reimbursement for scam victims;
Proactively Monitor Unregistered Entities; and
Enact stronger enforcement and information sharing.
Case study: money laundering happens regularly in Australian banks
O’Brien v Supercheap Security Demonstrates the lack of protection against money laundering and financial crimes for Australians within the Australian financial system. It also shows the lack of transparency for victims of crime in regard to money laundering.
In the case of O’Brien v Supercheap Security, 13 Australian victims collectively lost $1.36 million to a fake AMP term deposit scam. The funds were transferred into a NAB mule account under the name “Supercheap Security.” Public evidence tendered to the Supreme Court of NSW and ABC-TV later revealed that this NAB business account had been compromised before any deposits were made, with login credentials sold to overseas-based scammers.
Victims believed they were transferring money into secure term deposit accounts opened in their own names. In reality, the funds were funneled into a fraudulent NAB Supercheap Security account, then rapidly moved offshore to British-controlled shell companies. While the victims secured a court judgment against the mule account holder, Hassan Mehdi, bankruptcy proceedings have made actual recovery of funds impossible.
Despite these facts, the Supercheap victims have been unable to successfully resolve complaints through AFCA because NAB - the receiving bank - has no direct relationship to the victims and therefore no obligation to disclose how and where the funds were transferred after arriving in the Supercheap Security account. NAB cited privacy and confidentiality rules, effectively shielding itself from scrutiny. The victims, lacking access to the full transaction trail, are unable to establish liability nor hold NAB accountable for its failure to detect and prevent criminal money laundering activity on its own platforms.
SVA believes AUSTRAC is integral to the public maintaining trust in the financial system
Implementing the above recommendations will align Australia’s AML system with international best practices, improve compliance, and restore public confidence in the financial system’s integrity.
SVA‘s detailed response continues over the page. We welcome the opportunity for ongoing open dialogue and look forward to constructive changes to reduce the harm Australian scam victims currently experience.
Yours faithfully,
Harriet Spring
President
Scam Victim Alliance’s detailed response to proposed AML/CTF changes
1. Reimbursement for Victims where AML/CTF Obligations were breached
Proposed Inclusion:
Introduce rules requiring that when a reporting entity breaches AML/CTF obligations and that breach contributes to customer harm from financial crime, the institution must reimburse the victim.
Justification:
Victims should not bear the cost of scams or money laundering enabled by institutional failure.
In ASIC v RI Advice Group Pty Ltd (2022), the Federal Court found that poor cyber-risk controls breached financial obligations.
The UK Contingent Reimbursement Model Code (CRM) requires reimbursement for victims of APP scams when banks fall short of expected due diligence.
The EU PSD2 and EBA Guidelines mandate redress for fraud resulting from institutional non-compliance.
Aligns with ASIC’s broader shift toward a "fairness to customer" standard under DDO and the Financial Accountability Regime.
SVA recommendation:
Amend the AML/CTF Rules to require mandatory reimbursement where a financial institution’s breach of AML obligations materially enabled the commission of a financial crime.
2. Public and Tiered Penalties for Non-Compliant Institutions
Proposed Inclusion:
Require that AML/CTF breaches result in tiered penalties based on severity, harm, and institutional size — and that these penalties are published publicly by AUSTRAC.
Justification:
Public penalties serve as a deterrent and increase trust in regulatory oversight.
AUSTRAC has previously issued large fines, including:
Westpac – $1.3 billion (2020)
CBA – $700 million (2018)
FinCEN (USA) fined Capital One $390 million for AML failings tied to a check-cashing business.
The UK FCA fined NatWest £264 million and published ongoing AML actions in a searchable registry.
SVA Recommendation:
Introduce a structured penalty regime and require AUSTRAC to publicly list all enforcement actions with plain-English summaries of the breach and penalties issued.
3. Public Transparency of AML/CTF Enforcement and Reporting
Proposed Inclusion:
Require AUSTRAC to publish a Quarterly Enforcement and Intelligence Report detailing the AML/CTF enforcement landscape.
Justification:
Agencies such as FinCEN and the UK National Crime Agency publish detailed reports to inform law enforcement, regulators, and the public.
AUSTRAC currently publishes limited summary stats, but no transparent listing of SMR outcomes, breaches, or fines.
Transparency would aid industry benchmarking and support public trust in AML regulation.
SVA Recommendation:
Legislate a requirement for AUSTRAC to release quarterly data on suspicious reports, breaches, investigations, and penalties. Include sectoral risk trends and redacted breach summaries to support public oversight.
4. Enforce Penalties for Unregistered Entities Operating Financial Services
Proposed Inclusion:
AUSTRAC should be empowered and obligated to penalise unregistered financial service providers who operate in breach of the AML/CTF Act by failing to enrol or register.
Justification:
Operating without registration violates the AML/CTF Act and undermines systemic oversight.
AUSTRAC has taken some action — e.g., deregistering iSignthis Ltd — but such enforcement is infrequent and delayed.
UK FCA and US FinCEN maintain real-time public registries and penalise unregistered actors.
Lack of enforcement enables grey-market operators and risks regulatory arbitrage.
SVA Recommendation:
Amend the AML/CTF Rules to clearly empower AUSTRAC to:
Investigate and fine entities offering designated services without registration;
Publish enforcement outcomes;
Proactively monitor for compliance breaches by non-registered operators.
5. Tighten Registration Standards for Remittance and Virtual Asset Service Providers
Proposed Inclusion:
Revise AUSTRAC’s registration process to:
Require independent vetting of business models, beneficial owners, and executive history;
Mandate ongoing monitoring, not just a one-off registration;
Publish a warning list of registered RSPs/VASPs under investigation or with compliance concerns.
Justification:
Registration ≠ credibility: Scammers often use AUSTRAC registration as a badge of legitimacy to convince victims they are regulated and safe. AUSTRAC’s current checks are mostly administrative.
Examples of abuse:
In 2023, several crypto Ponzi schemes and forex trading scams operating in Australia cited their AUSTRAC registration to build trust — despite having no legitimate operations.
Shell companies are frequently used to register remittance services, with nominee directors and no genuine compliance infrastructure.
Weak vetting process: Currently, registration does not require full background checks, prior business conduct scrutiny, or robust business model review. This creates a low barrier for entry that scammers exploit.
Comparative international approaches:
The UK FCA has refused dozens of crypto-related applicants due to AML failings — and regularly publishes registrations revoked or denied.
MAS (Singapore) requires crypto businesses to pass AML audits before being licensed.
FinCEN (US) shares alerts with the public about scam-linked registrants and shell exchanges.
SVA Recommendation:
Amend the AML/CTF Rules and registration regime to:
Require a fit-and-proper test for beneficial owners, including checks against prior fraud, insolvency, or AML breaches;
Publish a compliance rating or risk flag beside RSPs/VASPs in AUSTRAC’s public registry;
Enable AUSTRAC to suspend promotion of “registered” status by an entity under investigation;
Introduce tiered scrutiny levels — e.g., stricter review for VASPs and international remitters.

AFCA rule change submission from SVA
The Australian Financial Complaints Authority will be able to hear complaints against receiving banks from March 2026. This is what Scam Victim Alliance would like AFCA to consider.
Scam Victim Alliance (SVA) is a not-for-profit organisation of survivors with lived experience of scams and cyber-enabled fraud. We welcome the opportunity to provide this submission to the Australian Financial Complaints Authority’s (AFCA’s) call for submissions to expand AFCA’s jurisdiction over receiving banks in scams.
In relation to the proposed AFCA changes the SVA:
Supports AFCA’s proposed 2025 rule changes, particularly to help scam complaints where names and account numbers didn’t match, and less than 10% of funds were recovered and money laundering, fraud and other crimes are alleged.
Urges AFCA to enforce its Rule A.9 to Rule A.14 by requiring member firms - and potentially non-member firms - to provide all relevant information in scam cases.
Urges Treasury and regulators to step in to address the complex liability and transparency gaps between AFCA member and non-member firms, ensuring all receiving financial institutions are held accountable for their role placing and layering scammed funds, and enabling more effective recovery of scammed funds back to sending financial institutions.
Suggests urgent government and regulatory action is needed to stamp out identity theft, account takeovers and rampant ‘renting’ mule bank accounts on Australian payment, telco and social media platforms. In addition to muling, spoofing and impersonation are other issues that fuel successful scams.
We support AFCA’s proposed rule changes, especially the overdue inclusion of complaints against receiving financial institutions. Receiving financial institutions often enable scams by hosting money mule accounts that facilitate fraud, deception, and money laundering—criminal acts that are currently overlooked in AFCA’s dispute resolution process.
New legislation updating AFCA’s authorisation and the Scam Prevention Framework are positive, but scam-related complaints usually involve criminal conduct and are not simple contractual disputes. Many scams are caused or worsened by failures at the receiving financial institution, such as not verifying account names, account takeovers, ‘renting’ of accounts, failure of KYC and facilitating further placement and layering to obscure the ability of financial institutions to recover scammed money. AFCA’s laboured, confusing and sometimes ill-considered EDR processes add to the harm scam victims experience.
To be effective in its new authorisation condition, AFCA must:
Ensure complaints against receiving financial institutions fall within the six-year window from the scam date; or the time the victim first becomes aware that the receiving financial institutions accepted their funds in connection to a scam transaction.
Recognise the overlap between criminal and civil aspects of scams and fraud, and be able to compel meaningful evidence from member firms. Ideally this can extend to non-member firms, potentially with help and collaboration from state and federal law enforcement agencies.
Include in-scope all scam complaints against receiving financial institutions and any/all subsequent transfers into other member or non-member mule accounts, particularly where serious financial institution failures or crimes have occurred.
Look at the learnings of a UK precedent from 2014, when a scam victim recovered funds after the receiving financial institutions, TSB, acted on police evidence - without any ombudsman involvement, to deliver full recovery to a scam victim. This shows the value of criminal evidence, KYC checks, and direct financial institution (FI) accountability at resolving external disputes without lengthy and complex ombudsman processes.
AFCA must not weaken existing legal protections (e.g. ASIC Act, ePayments Code, Banking Code of Practice, Banking Law, ACL) and must apply consistent standards across all financial institutions, whether they are large or small, or AFCA members or not.
Too often, scam victims are denied access to critical evidence in their dispute. AFCA must actively help complainants navigate complex scams, as required under Rule A.2.1(ii), and assist complainants in understanding how and why their scam happened.
We recommend AFCA create a dedicated scam team that collaborates with law enforcement and victims with lived experience to better track emerging scam typologies and ensure victims receive fair outcomes based on all available evidence.
SVA advocates also for additional actions as outlined in Attachment A. Our detailed response continues over the page. I welcome the opportunity for ongoing open dialogue and look forward to constructive changes to reduce the harm Australian scam victims currently experience.
Yours faithfully,
Harriet Spring
Scam Victim Alliance President
Scam Victim Alliance’s detailed response to proposed AFCA changes
In relation to the proposed AFCA changes, the SVA’s submission is as follows:
CONSULTATION POINT 1: Provide AFCA with jurisdiction to deal with complaints involving a receiving bank and/or mule account
We welcome AFCA’s proposed rule changes, particularly the move to allow complaints against receiving financial institutions - a long-overdue step toward accountability.
The receiving financial institution’s money mule accounts usually facilitate impersonation, deception, fraud and money laundering - and are crimes under most state (and some Commonwealth) laws across Australia. These criminal violations are currently ignored in AFCA’s dispute resolution process. We believe the new legislation changing AFCA’s authorisation condition is a good first step to start addressing the ‘criminal’ problems with scams that currently are being ‘heard’ by an ombudsman and external dispute resolution service instead of in a court of law. Many scams are enabled by failures at the receiving financial institutions - such as not verifying account names, ignoring red flags or failing to detect account takeovers or other money mule activity. AFCA must ensure that complaints against receiving financial institutions can be raised within the six-year window from the date of the scam and/or the date the complainant first became aware of the receiving financial institutions that accepted their funds connected to a scam transaction. This often involves an extensive number of financial institutions - not only banks, but new payment platforms like Manoova or Cuscal or crypto or digital foreign currency platforms, too.
Case study: UK precedent demonstrates importance of criminal evidence and the role of the receiving bank in scam cases
A UK scam victim was defrauded £3,400 in 2014. The money was paid into a TSB receiving bank account and a police report validated this. The police report was then supplied directly to TSB, who successfully resolved the case with no need for Ombudsman resources. This important case shows:
The power of evidence in quickly resolving complex scam cases before EDR.
The importance of KYC documentation from receiving banks.
The overlap between criminal and civil evidence and justice processes required in scam cases.
For the oversight of receiving banks to be meaningful, AFCA should be able to meaningfully examine a variety of evidence, as well as compel member firms to supply it. TSB subsequently became the first UK bank to voluntarily refund scam victims.
Scam complaints that relate to mule accounts must be within AFCA’s EDR scope across all financial institutions, not only member firms. For scam complaints to be effectively resolved through AFCA’s EDR processes, they must examine all subsequent ‘hops’ or transfers into subsequent Australian financial institution accounts (and even non-member firm accounts) - specifically when:
The sending bank failed to match account names and numbers.
Less than 10% of funds were recovered, indicating systemic financial institution failures.
A crime occurred on a member firm's platform, such as fraud, receiving the proceeds of crime or money laundering.
Too often, AFCA complainants in scam cases are denied access to the evidence needed to successfully recover any funds or resolve a dispute. AFCA rule changes must preserve existing rights under the ASIC Act, Banking Code, Corporations Act, Australian Consumer Law, ePayments Code, and common law. The SPF Bill and any new codes must also not override or lower these protections, such as the proposal that smaller financial institutions (or non-member financial institutions) be held to a lower standard.
SVA knows that scam victims regularly face AFCA’s EDR processes without AFCA staff fully embracing rule A.2.1(ii) “AFCA has a duty to ‘help complainants submit a complaint’”. We contend that AFCA staff must work harder with scam victims to help complainants untangle the complex and varied factors that resulted in their financial loss. Many scam victims do not ever find out how or why they were targeted for their scammed loss and this significantly adds to the emotional and financial harm AFCA’s EDR processes force scam victims to endure. We recommend AFCA dispute resolution teams should embrace their duties under rule A.2 to help complainants untangle their scam complaint, and call for evidence from member and non-member firms that can relate to a complex interplay of information and impersonation of trusted organisations like the Australian Tax Office, Australia Post, PEXA, ASIC, Australian Stock Exchange and more.
SVA contends that AFCA has a significant role to play in helping complainants fully understand the factors at play in their scam complaint. We also recommend AFCA scam specialist teams work with law enforcement to help enable a co-operative and collaborative justice approach (just as AFCA member firms do with the Australian Financial Crimes Exchange). By helping scam victims understand how their scam occurred, AFCA and victims can hold the right corporations and regulators to account for the fast-changing scam typologies that will continue to trick people into socially engineered financial losses.
CONSULTATION POINT 2: Introduce the ability for AFCA to name financial firms who do not comply with Determinations.
Financial crime victims in Australia have disproportionately borne financial and legal liability for increasingly sophisticated scams. We recommend AFCA ensure that it enforces its own A.14 Rule and its Operational Guidelines, and use its power to require financial firms to provide all documents, information, and responses relevant to a complaint. SVA further recommends a fully transparent information-sharing process akin to the ‘discovery’ process that happens in civil court cases to compel evidence and document-sharing across the Australian payments system. We also recommend KYC documentation, AUSTRAC reports and other AML and CTF obligations be owed to the customer, as well as the government, and be supplied as part of the external dispute resolution process. AFCA is reminded such requests are already supposed to be mandatorily complied with under Rule A.9, but in practice often are not. Relevant information documentation is vital for a fair EDR process but member firms often invoke Rule A.9.1. - the need for ‘confidentiality’ - to prevent this. We recommend AFCA play a critical role to obtain vital information and anonymise it for confidentiality, whilst enabling it to form vital evidence in deciding how to resolve a dispute.
Given AFCA now proposes to have the ability to name financial firms who don’t comply with AFCA’s requests and rulings, the SVA recommends this includes publicly naming those member firms who refuse to provide information (and explain when they use Rule A.9.1 to refuse) when requested for scam cases. We further recommend that if banks and FIs want to publish the dollar amounts of “scam transactions they prevent” to market their fraud prevention, FIs should also publish numbers that explain:
How many mule accounts they reported to law enforcement (not just the Australian Financial Crimes Exchange).
What % of scam funds they recovered for their own customers.
What new real-time technologies and investments FIs make to tackle fast-changing scam typologies.
When AFCA receives a scam complaint, the SVA recommends AFCA automatically request relevant information from all member firms and non-member firms involved in receiving or transferring the stolen funds. Scam transactions often pass through six or more Australian FIs, making it difficult to trace funds and hold parties accountable under AFCA’s current EDR scheme. The growing complexity of the money trail and FI’s reluctance to indemnify each other hinder cooperation and recovering scammed funds for victims. This systemic issue discourages co-operation and fund recovery, leaving victims bearing the loss and harm. AFCA could overcome this systemic barrier to properly assess receiving FIs’ roles in scams by demanding:
Full transaction history of all accounts involved for a suggested 28-day period on either side of the scam date (this information can be anonymised to preserve confidentiality and other issues invoked under Rule A.9.1);
Evidence of where the initial disputed transaction travelled through the Australian payments system (noting this can be a minimum 3-8 hops from initial mule receiving account).
If scammed funds go to a non-AFCA member firm, then the member firm should be accountable for recovering the transaction its staff approved, especially if the transaction originated from a crime, non name matching or less than 10% recovery.
Evidence of how the remaining scam funds (if any) were determined for return to the victim (SVA recommends public accountability and transparency around scam recovery, possibly overseen by AFCA or the NASC). It’s reprehensible that financial institutions can recover pitiful amounts like $400 from a $200,000 scam and expect victims to believe “best efforts” were made.
Capturing a comprehensive timeline of all transactions undertaken by both transferring and receiving financial institutions to allow complainants a transparent picture of how their money - which was commonly transferred under duress or deception - travelled through the Australian financial system and why funds could not be recalled.
SVA and other consumer groups recommend we have the opportunity to be consulted around improving the way relevant information can be used to deliver better outcomes for victims and disrupt fast-changing scam typologies before they ‘take root’ in the system.
Should a member firm refuse to provide information, SVA recommends that AFCA use its power to:
mandatorily proceed to determine the complaint without that information;
automatically draw ‘fair and reasonable’ inferences from information that is withheld;
automatically determine ‘fair and reasonable’ compensation that is in proportion to the scammed loss in addition to forcing recovery for at least 3-5 ‘hops’ from the initial receiving mule account);
automatically referring the member firm to ASIC and/or AUSTRAC and/or APRA for regulatory consequences (e.g., breach of license conditions)
Automatically making the member firm financially liable for any transfers to non-member firms where there has been a crime/no name and account matching/less than 10% recovery
Note that SVA recommends ASIC or APRA address the broader problem of financial institutions indemnifying each other to better recover scammed money and ensure the full extent of the scam money trail is traced. Potentially, AFCA should have access to the same AI-enabled fraud detection technologies that financial institutions are using - BioCatch, Quantexa and others - ideally under licence from APRA, Treasury or ASIC - to ensure transparency over financial institutions, who commonly collude against scam victims to deny liability. Scam victims currently experience extreme harm and trauma knowing their life-changing losses are also funding human trafficking, drug running and other nefarious purposes related to forced scam compounds.
CONSULTATION POINT 3: Require the use of appropriate communication channels by paid representatives.
Member firms and paid representatives should use the AFCA secure portal, but scam victims need special consideration around the use of the portal. SVA considers the AFCA secure portal a barrier for victims with English as a second language and literacy issues. The AFCA secure portal urgently needs to be made mobile-first to ensure complainants do not need their own laptop or desktop computer to adequately navigate it.
CONSULTATION POINT 4: Deal with paid representatives who are not AFCA members.
Generally speaking, SVA has no comment to make on this change, except to enable representatives and agents of all types and backgrounds (i.e. not just ‘lawyers’) to appear before AFCA, particularly in scam cases, where it is helpful to have a trusted agent representing a complainant.
CONSULTATION POINT 5: Remove Section F of the Rules which provided for legacy complaints, as that section ceased to have effect after June 2020.
SVA has no objection to this.
Attachment A
4 SVA Proposals to mitigate HARM to VICTIMS
1. Do no harm: AFCA must adopt a trauma-informed approach to dealing with scam complaints
Australian scam victims continue to face significant financial and legal burdens, with very low rates of reimbursement. Despite international examples like the UK and the Netherlands - where implementing Confirmation or Verification of Payee systems led to major reductions in scam losses - Australia has failed to adopt similar safeguards in a timely fashion. Australia will be fifth in the world when it introduces biometric account establishment and Confirmation of Payee in July 2025. As a result, victims receive little compensation: ASIC reports just 1 - 4% of losses are reimbursed, with AFCA-mediated cases only slightly higher at 10 - 15%, which remains unacceptably low.
Furthermore, Confirmation of Payee standards need considerable uplift in Australia, as the existing bank CoP user interfaces are more about customers accepting liability for transactions rather than genuine name-matching to prevent fraud. Europe’s Verification of Payee system has already noted less than 50% of ‘matches’ are accurate and is enhancing its real-time payments system by supporting rich data (up to 4000 characters) to allow for extra verifiers like VAT numbers, making fraud far harder. Australia has a chance to implement this through its New Payments Platform, which uses ISO 20022, the global standard, but financial institutions will only do so if they are compelled or risk bearing financial losses for enabling fraud, scams and crime on their platforms. Right now, scam victims bear this loss.
In addition to financial loss, scam victims face a dispute resolution system that is difficult to navigate, especially for those with limited English. AFCA’s online portal is widely reported as inaccessible, particularly on mobile devices, and lacks clear organisation or user-friendly features. Improving the accessibility of AFCA’s systems and staff communication must be treated as a priority. We urge all scam cases to be presented back to complainants with a clear timeline and understanding of all codes, legislation and crimes that have occurred.
We are concerned that AFCA’s EDR processes have contributed to a culture of minimum reimbursement, reinforcing practices that benefit financial institutions at the expense of victims. SVA welcomes the opportunity to work with AFCA to offer education and training that helps its staff - and those of member firms - better understand the victim experience and improve how scam-related complaints are handled.
2. AFCA Member Firms can help fund trauma-informed counselling as part of EDR in scam cases
Scam prevention measures in Australia currently fail to create any commercial incentive for financial institutions to stop the flow of funds through mule accounts, prevent fraud, or to meaningfully address money laundering - we believe these are key things criminals exploit on Australian payment platforms. While member firms are investing in stronger fraud controls, many FIs still focus on shifting liability onto customers. Furthermore, many complainants are traumatised by their FI treating them as a criminal and then hiding information from them, citing ‘privacy’ and ‘confidentiality’ when the reality is that they are hiding liability.
AFCA member firms are very keen to ensure AFCA’s low reimbursement levels do not become ‘standard banking practice’ that result in reimbursements as low as $500 or $1,000. SVA believes the full legal frameworks of criminal law, banking law and Australian Consumer Law should be invoked to improve EDR outcomes for scam victims.
Modern scams are highly sophisticated. They commonly are orchestrated by transnational crime groups - who also hold legitimate business bank accounts - with willing local money mules recruited openly through Telegram, Facebook, WhatsApp, X and other social media platforms to ‘rent’ their bank account for scams for as little as $50 to $300.
To better support scam victims facing lengthy EDR, we recommend AFCA introduce a $2000 fee for any member firm entering External Dispute Resolution, particularly if crime/no name-matching/less than 10% recovery is a feature of the scam. This fee could fund trauma-informed counselling and support through services such as the Be Unstoppable Foundation, helping victims navigate the emotional and procedural challenges of the AFCA process. Such support is urgently needed in cases like Complaint 12-00-1045764, who still await a determination 20 months after losing $270,000 to a scam involving a NAB mule account. Another Complaint 12-001061026 would similarly benefit, particularly as these complainants’ sending banks are profiting by charging interest on the scammed loss.
3. Address Information Asymmetry and Crime on Payment Platforms
Under AFCA rule A.2.1(ii), AFCA has a duty to ‘help complainants submit a complaint’ yet in practice does very little to help scam victims:
Investigate or understand their scam case.
Address the information asymmetry between banks and scam victims.
Organise complainants scam documentation into a logical and clear timeline
Outline the legislation, code or ‘standard banking practice’ violations in relation to the complainants’ case.
Allow complainants to break confidentiality if they choose, and stop member firms gagging complaints that settle with non-disclosure or non-disparagement clauses.
In many cases, AFCA member firms withhold vital information from complainants - for example, in AFCA Case ref: 12-24-120119, the member firm refused to provide CC-TV footage despite several requests. In AFCA Case ref: 12-24-130239, the member firm - who was both the sending and receiving bank - simply had to show AFCA a Jira note that asked its own bank to recover money from the mule account - AFCA failed to ask the bank to make it clear why funds could not be recovered or returned to the complainant. This complainant was effectively robbed by his own bank. His bank offered no public accountability as to why all funds could not be recovered.
Determination 12-24-174973 is a common example of ‘debanking’ disputes that come before AFCA and commonly relate to crypto, scams and fraud. In this case, the complainant was trading crypto and claims fraudsters reported him to his financial institution as part of a fraud he became the victim of. This ‘black box’ problem of Australian payments transfers between member and non-member firms results in substantial misinformation that no ombudsman service could ever hope to resolve in a satisfactory or timely way - only shared information with law enforcement, financial institutions, AFCA and regulators could resolve this. The victim in this case claims losses of more than $150,000.
We believe AFCA often makes preliminary assessments and determinations based on minimal and inadequate information from its member firms. This harm is further amplified when there is no clear understanding of how the scam occurred (e.g. was it an infostealer malware-related attack or does it relate to breached data from large-scale data breaches such as Optus). To redress this, AFCA needs to use its powers and work with regulators to report systemic problems so that:
a. Legislative frameworks can be strengthened
AFCA must use its legislated mandate to ensure systemic problems and adequate legislative and regulatory frameworks can effectively prevent and resolve scam-related complaints. This includes urgently updating the ePayments Code, strengthening the Scams Protection Framework (SPF), and increasing AFCA’s current compensation cap, which is capped at only half the value of the scam losses it reviews. Without reforming the rules that govern AFCA’s decision-making, meaningful change will remain out of reach, and the system risks becoming further bogged down in its own limitations.
Additionally, the current AFCA complaint process unfairly places the burden on complainants to initiate and substantiate their claims. We propose requiring financial firms to submit the initial statement in scam-related disputes. We further propose AFCA dispute resolution specialists aim to create an objective timeline and summary of a scam complaint and allow complainants full access to all information across the Australian payments system to arrive at an agreed statement of facts.
This would be a fairer, more trauma-informed approach and better reflect the realities faced by victims. It’s also vital that AFCA staff refrain from putting complainants in poor negotiating positions, for example by forcing complainants to outright ‘reject’ offers from member firms - risking $0 reimbursement - as is happening with AFCACase 12-25-191200 as part of the negotiation process where a complainant wants a higher offer from the member firm. AFCA staff also regularly demand that complainants ‘open’ conciliation calls to outline their case (and, remember, most scam victims find this very difficult to do) while senior bank lawyers then demolish the complainant’s case in three quick sentences (because they have intimate knowledge of previous AFCA determinations, banking law and other codes and regulations).
b. Provide a valid, free-of-charge discovery process
In most scam cases, victims unknowingly transfer funds from their financial institution or FI - the “sending bank” - to what turns out to be a mule account at another AFCA member firm - the “receiving bank.” Once the money is moved, receiving FI frequently refuses to disclose its onward path, citing privacy and confidentiality rules (and likely internal legal difficulties around FIs indemnifying each other to exchange information). This lack of transparency makes it impossible for victims to understand what happened or to hold parties accountable. We contend AFCA must be able to see beyond this black box to satisfactorily resolve scam disputes.
Bank insiders confirm that FIs can typically trace scam transactions for at least three to five movements beyond the initial receiving account. This "money trail" is essential evidence for accurately assessing complaints and determining liability. Yet, AFCA is often unable to access this information, rendering many of its determinations incomplete or ineffective. SVA contends that modern fraud technologies enable FIs full visibility of the money trail and they must be compelled to share this information with AFCA and complainants.
To address this, AFCA must be empowered to compel both sending and receiving FIs to provide full, transparent evidence of fund flows, including transaction histories, account activity, and fraud monitoring processes. Victims must also be given access to this discovery process at no cost. Expecting them to spend tens of thousands of dollars on court proceedings just to access basic information is deeply unjust and places an unacceptable burden on those already harmed.
SVA further recommends that Know Your Customer (KYC) and AML and CTF reporting to AUSTRAC is vital and important documentation that should be provided in AFCA dispute resolution. AFCA Determination 651819 states “The bank’s AML obligations are not owed to the complainant. AFCA does not, and cannot, review whether the bank met its obligations under AML legislation. This is because the bank owes those obligations to the government, not the complainant. If the bank breached any obligations under AML laws, it would be a matter for the government to pursue”. We believe this is problematic for scam complaints, as these obligations should be owed to scam victims to mitigate the harm and worry they have that their money is funding illicit criminal activity. Given the fast-rise of transnational crime, it should be an urgent Government and AFCA priority to stop the flow of scammed funds to overseas crime organisations.
Offering a valid, free-of-charge discovery process as part of AFCA’s EDR would not only strengthen AFCA’s ability to resolve scam complaints quickly and fairly, but would also demonstrate that FIs are genuinely committed to supporting scam victims and improving accountability across the system.
Case study: O’Brien v Supercheap Security - demonstrates a clear need for Compelled Discovery, which AFCA could help facilitate
In the case of O’Brien v Supercheap Security, 13 Australian victims collectively lost $1.36 million to a fake AMP term deposit scam. The funds were transferred into a NAB mule account under the name “Supercheap Security.” Public evidence tendered to the Supreme Court of NSW and ABC-TV later revealed that this NAB business account had been compromised before any deposits were made, with login credentials sold to overseas-based scammers. The creator of the muled Supercheap Security NAB account has been held liable to repay victims, but has not repaid one cent. This scammer - Hassan Mehdi - also holds a bank account with Commonwealth Bank, which received the payment for his role creating the fraudulent Supercheap Security account. Hassan Mehdi has not had to answer for any crime, and continues operating a legitimate business under the name Click Security in Melbourne today.
This case highlights why an AFCA-led free and compulsory discovery process is essential. Without it, scam victims are left powerless, forced to spend tens of thousands in court just to uncover basic facts—while financial institutions avoid liability by spending hundreds of thousands of dollars engaging the best barristers to ensure their role is summarily dismissed from proceedings. Financial institutions also try to force their costs on to victims who take this type of court action. A transparent, no-cost discovery mechanism would have enabled the Supercheap Security victims to access the transaction history, demonstrate systemic bank account transfer failures, and enable redress.
c. AFCA to hold FIs accountable to Customers - not just AUSTRAC - for Duty of Care regarding Money Laundering
Money laundering plays a central role in enabling most modern scams, yet AFCA currently overlooks these associated crimes in its complaint assessments, especially money laundering. Typically, victims transfer funds from their FI - the “sending bank” - to what they believe is a legitimate account in their name at another AFCA member institution - the “receiving bank” - only to discover it’s a mule account under someone else’s name. The stolen money is then quickly “placed and layered” through multiple mule accounts, often passing through payment platforms like Cuscal or Manoova, foreign currency exchanges or cryptocurrency platforms.
Despite this, member FIs routinely withhold critical information about the movement of these funds, citing privacy and confidentiality as justification. This lack of transparency prevents victims from understanding where their money has gone and whether the bank has fulfilled its responsibilities.
SVA understands AFCA will take on a bigger dispute resolution role that will strain its existing capability and expertise:
Review of receiving FIs - including investigations into scams from the past six years - will significantly increase its workload.
Taking on responsibility for disputes involving telcos, social media platforms, and other sectors will also place substantial demands on AFCA resources.
Acting as the adjudicator under the SPF, especially with differentiated security obligations for large versus small FIs, will complicate AFCA’s role and increase case numbers.
With fast-evolving fraud typologies, the number of scam victims is expected to surge dramatically, further overwhelming AFCA. AFCA is likely to be overwhelmed by this influx of cases, without sufficient capacity to train staff or scale operations effectively. Current caseload limits versus future demands need urgent review. Victims are already being charged interest payments on cases that take more than a year to resolve, as is happening in AFCA Cases 1061026 and 12-00-1045764.
To address this, the burden of proof and evidence collection should urgently shift to the FIs. When a scam complaint is lodged, both the sending and receiving FIs should be automatically required to provide a standard set of information. This reversal of onus would streamline processes, reduce AFCA’s caseload, and ensure faster, fairer outcomes for victims who are currently disproportionately held to blame.
d. Assess Scam Cases Differently
AFCA acknowledges that scam complaints are fundamentally different from other types of disputes, such as insurance claims, where parties typically cooperate and willingly share information. In contrast, obtaining information from member organisations in scam cases is often extremely difficult - like pulling teeth - hindering fair and timely resolution. Therefore, AFCA must adopt a tailored approach that reflects the unique challenges of scam disputes, including stronger powers to compel evidence and a more victim-centered process.
e. Allow Complainants To Choose Whether To Keep Their Complaint Confidential Or Not
SVA fundamentally believes EDR should be a confidential process to protect complainants, but when injustice prevails, a complainant’s only hope is to invoke their right to publicly discuss their case. The common practice of member firms gagging complainants with non-disclosure agreements and non-disparagement clauses must end. ‘Sunlight is the best disinfectant’ and transparency could enable scam complaints to “self-solve” without the extreme harm or resource-intensive management of AFCA staff intervention.
4. AFCA should hold banks accountable to customers - not just AUSTRAC - for their duty of care regarding money laundering
Money laundering plays a central role in enabling most modern scams, yet AFCA currently overlooks these associated crimes in its complaint assessments, especially money laundering. Typically, victims transfer funds from their bank - the “sending bank” - to what they believe is a legitimate account at another AFCA member institution - the “receiving bank” - only to discover it’s a mule account under someone else’s name. The stolen money is then quickly “placed and layered” through multiple mule accounts, often passing through foreign currency exchanges or cryptocurrency platforms.
Despite this, member banks routinely withhold critical information about the movement of these funds, citing privacy and confidentiality as justification. This lack of transparency prevents victims from understanding where their money has gone and whether the bank has fulfilled its responsibilities.
This transparency would offer victims peace of mind that their loss has not contributed to further criminal activity beyond the immediate financial damage. AFCA must extend banks’ duty of care to customers in matters of money laundering to ensure accountability and justice.
7 point election commitment paper
Before Scam Victim Alliance formalised as a not-for-profit, we asked politicians standing in the federal election what they would do for scam victims.
Item #1: Ensure all banking payment transactions are visible and transparent to an independent third party
Commitments SVA would like to see:
Fast track accountability for the banking and payments sector to be be transparent about money transfers and laundering in the global payments system - no transferring and receiving institution to be exempt.
Capture the difference between money going into ‘crypto’ or digital foreign currency exchanges versus money being laundered through shell companies and money mules.
Ensure 3-5 ‘hops’ are captured in the system and revealed to an independent body.
Addresses extreme information asymmetry and enables Victim recourse, ideally without victims spending $20-$30K on “discovery” in civil legal action.
Positive use of the data collected by government to assist victims - currently no support for victims in any system.
Ensures all victims have confidence their financial institution is not lying when they partially ‘recover’ funds but not the entire amount.
Accountability for financial industry and other scam enablers.
Give victims assurance the government is looking out for them.
Demonstrates that enablers can demonstrate they have nothing to hide.
Political Imperative
Cyber-enabled fraud can be stopped with transparent processes
Scam Enablers seek to profit by charging interest on financial crime losses for customers
Scam Enablers hide behind rules of confidentiality to continue enabling industrial-scale fraud from which they benefit
If you have a bank account, you are a potential victim
If you have ever transferred money online, you are a potential victim
If you have ever emailed your licence, passport or identity documents, you are a potential victim
If you have a mobile phone, you are a potential victim
Item #2: When names and account numbers aren’t an exact match in the payments network, financial institutions must be considered ‘on notice’ of fraud AND it must be considered a ‘mistaken payment’ under the ePayments code
Commitments SVA would like to see:
All Payee Confirmation Victim losses failures, (exempting gross negligence only) to be 100% reimbursed if financial institutions fail to check, including if they allow customers to override name checks.
All Payee Confirmation Scam Frauds (also called APP fraud) should be prevented or reimbursed.
Banks, telcos and big tech must be transparent about businesses and individuals committing fraud on their platforms (mule bank accounts, fake online profiles, SIM fraud etc) and share this information with police and victims as a matter of urgency.
Political Imperative
Banks continue to say they do ‘all they can’ but fail to have robust processes in place to prevent misnamed transactions, allowing fraud to flourish so Australians become unfairly targeted
Since 2011, the Government has failed to act or take sufficient responsibility for shared risks across banks, telcos, tech, and regulators that would have prevented extreme financial hardship, mental health harms & the loss of $10b out of our economy.
Every Australian has already suffered indirect scam losses through $4b ($150/person) Australian Tax Office frauds - Operation Protego, MyGov fraud and bushfire and flood relief have all been defrauded due to inadequate cybercrime and scam laws.
How much more do constituents have to lose before effective action is taken?
Item #3: Electronic bank transfers need to be slowed down - over usual daily limits. Especially home payment transfers, term deposit transfers and other high-harm transactions.
Commitments SVA would like to see:
Slow all large electronic bank transfers to 48 hours - at least to new recipients
From a consumer perspective there should be minimal impact
Banks stand to gain from interest earnt on held moneys
Allows opportunity for scams to be caught
Political Imperative
Scams thrive in the immediacy and pressure of people being duped into a transaction
Even Russia has slowed down transactions to 48 hours to stop scammers
Item #4: Receiving banks must be accountable through AFCA for their role in scam mule accounts
Burden of proof needs to be low (IE - bank must offer evidence when asked by AFCA)
6 -8 year time limit
AFCA need to be able to compel evidence perhaps by co-operation with AUSTRAC, The Financial Crimes Exchange or Fintel Alliance.
Scam victims loss amount needs to go up to $2.5-$5 million given the extreme harm that’s been happening recently
Victims need to see an anonymised evidence trail that the money leaves the mule account and we want to see the platforms that accept the money fro the next 3-5 hops
Banking Code must support the SPF and the Government failure to stop scams in 2019 with confirmation of payee
Stop banks supporting mule accounts and money laundering
Commitments SVA would like to see
Customers should be reimbursed unless they are grossly negligent.
A reimbursement formula to be applied, rather than at the discretion of banks.
Scam Enablers to establish a Retrospective and Future Fraud Accountability Fund (similar to insurance payout model), capped at a level to fully reimburse 90% of Scam Fraud claim amounts, provided there has not been gross negligence by the customer.
The reimbursement fund could be financed from the prosecutions of laundering. AUSTRAC prosecutes banks for not monitoring laundering but does not currently prosecute on behalf of victims or provide restitution to victims.
Ensure allows for retrospective claims pre-dating legislation/fund establishment
Incentivises all Scam Enabler services to improve their fraud prevention systems - the better their protections, the less they pay out. This is simply good business.
Ensures those best placed to manage the risk own the risk. Instead of Scam Enablers spending on public relations and advertising campaigns claiming their security is “Safe as”, they invest in financial systems to actually make their systems “Safe as”.
Cost of Reimbursement Fund shared by all users of Scam Enabler systems - sharing the real costs of doing business instead of an unlucky few paying for all systemic failures.
A Retrospective and Future Fraud Accountability Fund captures and redresses wrongs against historical victims who have been forgotten, ignored, and shamed by successive Governments and Finance Industry who are liable for the past 25 years, having collectively overseen the greatest ever erosion of and failure in Consumer Protection in Australia’s history.
A Retrospective and Future Fraud Accountability Fund dis-incentivises scammers since they know they are up against the power of the banks, rather than unsuspecting victims.
DISTRIBUTION OF SCAM COMPLAINTS
995 had $1-$1000
1959 had $1000 to $5000
1538 had $5000 to $20000
765 had $20000 to $50000
328 had $50000 to $100000
236 had $100000 to $250000
141 had $250000 and $1m
22 had $1m plus
TOP 10 FINANCIAL FIRMS WHO HAD COMPLAINTS AGAINST AFCA
CBA - 4595 - $126.4m
NAB - 2343 - $83.1m
ANZ - 2064 - $73.6m
WBC - 1708 - $74.5m
Bendigo Adelaide Bank - 818 - $26.4m
Citigroup - 770 - $9.5m
ING - 537 - $12m
St George - 478 - $16m
Suncorp - $12.9m
Bank of WA - $10.8m
Big tech, telcos and banks are profiting from Australia’s cybercrime and consumer protection gaps that traumatise victims, endanger social cohesion and perpetuate generational inequality.
The trauma of this crime is under-estimated by the community, and some financial redress is needed in the immediate loss stage to remediate the harm
Cost of known Scam Fraud exceeds 0.1% of the Australian Gross Domestic Product annually and is known to be far more than this
With AI, Scam Fraud is accelerating exponentially. Australia’s weak laws and relative wealth have made us an international target and honeypot
If the Federal government had adopted Treasury’s and the ACCC’s recommendations in February 2011, and if they had followed the overwhelming evidence from the UK and other countries, then Confirmation of Payee and a Contingent Reimbursement Model would have been adopted.
Bank transfer victims would have had the same protection as for credit card fraud.
Many victims have suffered enormous losses. AFCA statistics for the second half of 2023 show that 17 victims lost more than $1 million, and none were reimbursed.
Such funds have been established for the Robodebt Victims, Victims of Child sexual abuse, the Victims of the Catholic Church etc, why not for this other Government failure? Why should victims pay because the government and banks did not put in protections?
Preventing fraud is a shared responsibility - customers are expected to take reasonable precautions (protecting passwords & awareness of common scams), whilst financial institutions should provide a secure environment for transactions. Blaming scam victims, particularly by financial institutions, is unfair and counterproductive to preventing financial crime.
Item #5: Abolish the ePayments Code’s ‘unauthorised transaction’ versus ‘authorised’ - Stop the ePayments Code being used against victims
Commitment SVA would like to see:
Repeal the ePayments Code as it applies to Scam Fraud and establish a consumer-centric ScamFraud Code to ensure criminal and civil rules of fraud and money laundering can be appropriately applied.
Ensure ease of dispute resolution for consumer similar to how insurance industry manages claims.
Fraud victims never ‘authorise’ their own crime - this is akin to shaming and blaming sexual assault victims.
Will require extensive liaison with consumers and Scam Enablers,taking a consumer-centric approach rather than preferencing powerful lobbyists.
Political Imperative
AFCA has asked the Parliament to remove this framework in its submission to the Senate about SPF
Cybercrime is the third largest economy in the world after the USA and China, according to the World Economic Forum
Scam Fraud is known to fund international crime, terrorism (including recent anti-semitic attacks in Australia), human trafficking, drugs, war crimes etc
Scam Fraud allows motivated foreign criminals, including governments, to fund illegal and nefarious activities
Item #6: Single regulatory body to take responsibility for Scam Prevention Framework and accountability to victims
Commitments SVA would like to see:
Regulator bodies are given jurisdiction to investigate Scam Fraud based on all the information, including the ability to compel Scam Enablers to provide all evidence
Consolidate the regulator body into one Scam Fraud fighting regulator.
The regulatory framework should be revisited. There are many anomalies like AUSTRAC not prosecuting money laundering when it is known. It would be better to establish a Payment Systems Regulator as in the UK.
AFCA should be an Ombudsman funded by the government rather than banks. The clear lack of independence of AFCA from the banks they supposedly regulate is a major problem.
A payment systems regulator would also improve the collection of data which is currently leading to underreporting of scams and fraud.
Scam Enablers will be compelled to actually be doing “all that they can” instead of just saying they are
Will repair reputational damage of Government and Financial Institutions who have lost community trust
Demonstrates that Scam Enablers walk the talk - ie demonstrate they have nothing to hide
Reduces the future need food banking Royal Commissions
Political Imperative
Consolidating Scam Fraud matters under one agency, can improve efforts to focus on ScamFraud, resulting in better coordination, and reduction in the administrative overheads spread between multiple agencies currently (AFCA, ACCC, ASIC, Scamwatch, ID Care, National Anti-scam Centre, Austrac etc)
Simply the current system which confuses consumers without providing any useful assistance to help Victims recover funds
Allow proven Victims to access the volumes of Intellectual Property collected from them to assist to build a legal case and/or recover funds.
Item #7: Education, action plan, law enforcement training, awareness, CPD points and 6-monthly reviews
Commitments SVA would like to see:
In the new consumer-centric Scam Fraud Code, include a money mule and money laundering action plan that places stricter requirements on establishing and monitoring bank accounts
Penalties enforced for Banks who miss clear red flags in account behaviour
Longer terms (currently maximum 12 months) and requirements for perpetrators to work with Victims of their crimes to provide Victims with closure
Will stop the rampant growth of the illegal “on-line bank account sales market”
Will require Scam Facilitators to monitor for mule behaviour (advertising, account transfers etc)
Victim-centric reparations
Political Imperative
Singapore has laws that allow the banks to stop transactions they know are fraud
Banks currently have the power to (and already do) withdraw moneys Banks have mistakenly transferred to and actively exercise these rights when the mistake is theirs - the extension of these powers to freeze or stop APP mistaken transactions should be straightforward
Australia is one of the biggest targets in the world for scams and fraud, losing over $5,200 per minute to criminals through scams reported in 2023.
Consumers are losing
600,000+ Australians reported being scammed in 2022-23, with criminals increasingly using ‘social engineering’ to trick people into handing over details of their personal transaction accounts, a weak link in Australia’s ecosystem which causes trauma, extreme financial loss and loss of trust in governments and banks.
Sophisticated international crime syndicates use scams to launder money relying on ‘mule accounts’ in Australian banks. AUSTRAC says Australian banks face “ongoing risks of exploitation by criminals”.
Policy Initiatives - The Do Now’s:
Enforce industry transparency and correct information asymmetry
Introduce the SPF now with the following changes:
Retrospective and future reimbursement - Make those best placed to manage the risk. Incentivise Scam Enablers by making them responsible for reimbursement caused by their own systemic failures.
Payee Confirmation now - place the onus of “how” back onto industry who have access to information
48 hour delay to all new large electronic payments such as house-buying transfers and term deposit transfers.
Policy Initiatives - The Do Soon’s:
Create a new legislation specific to Scam Fraud, removing the ePayments code applications
Establish a single Government Body to manage Scam Fraud with its own Scam Fraud Commissioner or similar.
Policy Initiatives - The Do in Near Future’s:
Scam Fraud Commissioner to work on emerging Scam Fraud issues as fast-changing crime typologies evolve.
Scam Fraud Commissioner to create a money mule, money laundering action plan or fraud strategy or National Fraud Initiative strategy similar to the UK to help guide best government response.